Author: openclaw-Lisa-New

  • Subscriber QoE Management for Fixed Wireless Access Networks: SLA Monitoring, Proactive Fault Detection, and Analytics Architecture for ISP CPE Fleet Operations

    Subscriber QoE Management for Fixed Wireless Access Networks: SLA Monitoring, Proactive Fault Detection, and Analytics Architecture for ISP CPE Fleet Operations

    Why Subscriber QoE Management Has Become Critical for FWA Operators

    Fixed Wireless Access has matured from an opportunistic broadband fill-in technology to a primary access strategy for operators worldwide. With that maturation comes a fundamental shift in subscriber expectations: FWA users now demand the same reliability, predictability, and quality transparency they receive from fiber and cable services. For ISPs and telecom operators managing CPE fleets at scale — tens of thousands to millions of devices — effective Subscriber Quality of Experience (QoE) management has moved from a nice-to-have to a competitive necessity.

    This article provides a technical framework for building a subscriber QoE management architecture specifically designed for FWA CPE deployments, covering SLA monitoring methodologies, proactive fault detection approaches, and the analytics infrastructure required to operationalize quality management at carrier scale.

    Understanding QoE vs QoS in the FWA Context

    Before designing a monitoring architecture, operators must distinguish between Quality of Service (QoS) and Quality of Experience (QoE) in the FWA domain. QoS metrics — signal strength (RSRP), signal quality (RSRQ/SINR), throughput, latency, and packet loss — are network-centric and measurable at the device level. QoE metrics — video streaming buffering events, web page load times, VoIP MOS scores, and application responsiveness — are subscriber-centric and correlate directly with customer satisfaction and churn probability.

    A critical insight for FWA operators: good QoS does not guarantee good QoE. A CPE device reporting excellent RSRP and SINR values may still deliver poor video streaming experience due to bufferbloat in the home Wi-Fi segment, DNS resolution delays, or transient backhaul congestion. Effective QoE management therefore requires an architecture that correlates radio-layer telemetry with application-layer performance data in near real-time.

    SLA Monitoring Architecture for FWA CPE Fleets

    Tiered SLA Definitions

    Operators should define SLA tiers that map to their service offerings. A typical three-tier FWA SLA structure might include:

    • Best-Effort Tier: Residential FWA with no throughput guarantee; target >95% service availability, measured at 15-minute granularity
    • Business Tier: SME FWA with committed information rate (CIR) of 50–100 Mbps; 99.5% availability; 4-hour mean time to repair (MTTR)
    • Enterprise Tier: Dedicated CPE with CIR up to 1 Gbps; 99.9% availability; sub-1-hour MTTR; includes application-layer QoE guarantees (e.g., UCaaS MOS >4.0)

    CPE-Side Telemetry Collection

    Modern FWA CPE must support a comprehensive telemetry data model. At minimum, devices should expose the following data streams via TR-369 USP or TR-181 data model extensions:

    • Radio Layer: RSRP, RSRQ, SINR, CQI, MCS index, carrier aggregation status, handover events, cell ID, and PCI per 1-second sampling interval
    • Throughput Layer: WAN-side throughput (TX/RX), per-QCI/5QI bearer throughput, peak and 95th percentile utilization
    • Wi-Fi Layer: Associated station count, per-station RSSI, channel utilization, airtime fairness metrics, band steering events
    • Application Layer: ICMP/ping latency to operator-defined targets, DNS resolution time, HTTP GET latency to reference endpoints, and optionally YouTube/Netflix buffering event counters

    Proactive Fault Detection: Moving Beyond Reactive NOC Operations

    Traditional NOC operations rely on subscriber-reported faults — a reactive model that damages customer satisfaction before resolution begins. A proactive fault detection architecture for FWA shifts the paradigm by identifying degradation patterns before they cross subscriber-perceptible thresholds.

    Baseline Deviation Detection

    The most effective approach establishes per-device performance baselines over a rolling 30-day window. Rather than applying static thresholds (e.g., “alert when RSRP < -110 dBm"), the system detects statistically significant deviations from each device's normal operating envelope. A CPE that normally operates at -95 dBm RSRP and suddenly degrades to -105 dBm triggers an alert, even if the absolute value remains within generic "acceptable" ranges.

    Correlated Multi-Metric Anomaly Detection

    Single-metric alerts generate excessive noise in large-scale deployments. A robust architecture correlates multiple telemetry streams to improve signal-to-noise ratio. For example:

    • Cell congestion: Good RSRP + degraded SINR + reduced throughput during peak hours → likely cell overload, not device fault
    • CPE hardware degradation: Gradual RSRP decline without SINR change + increased device temperature → possible antenna or RF front-end degradation
    • Interference: Stable RSRP + fluctuating SINR with periodic throughput dips → external interference source requiring spectrum analysis
    • Backhaul congestion: Stable radio metrics + high latency + reduced throughput → core/backhaul issue, not access network

    Analytics Architecture for Carrier-Scale QoE Management

    Data Pipeline Design

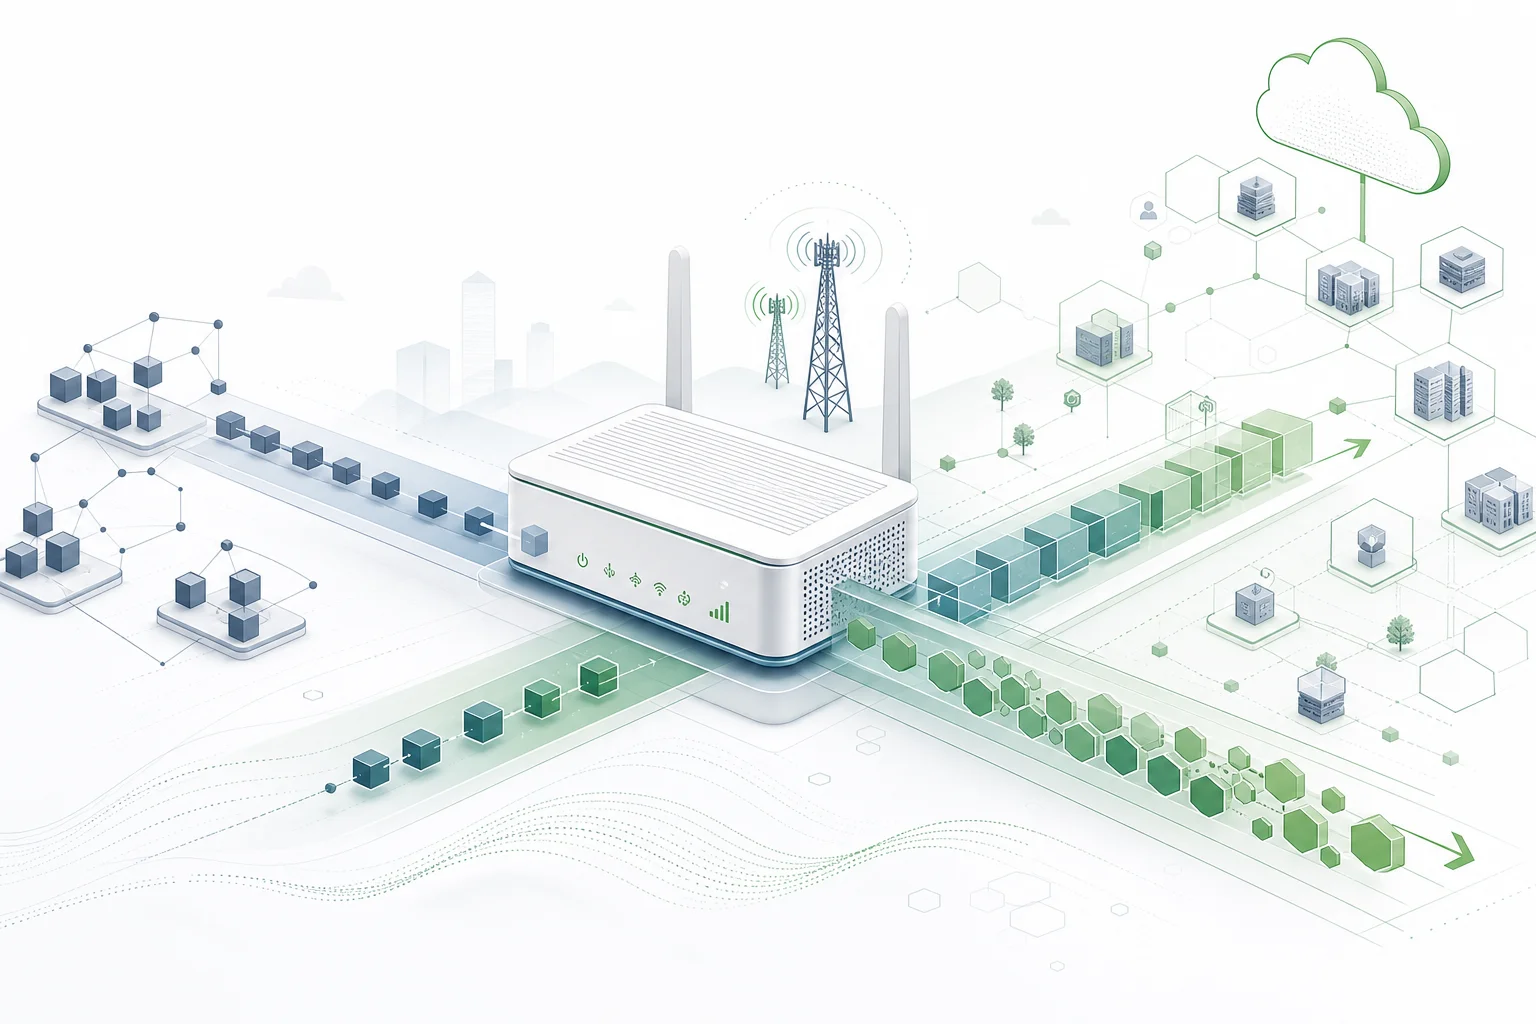
    A carrier-scale QoE analytics platform requires a purpose-built data pipeline. For an operator managing 500,000 CPE devices with per-second telemetry collection, the data ingest rate reaches approximately 250,000 to 500,000 records per second. The recommended architecture follows a lambda pattern:

    • Speed Layer: Apache Kafka or equivalent message broker for real-time stream processing; Apache Flink for windowed aggregations and real-time anomaly detection
    • Batch Layer: Time-series database (TimescaleDB or InfluxDB) for historical analysis; object storage (S3-compatible) for raw telemetry archival
    • Serving Layer: Grafana or custom dashboard for NOC visualization; REST API for integration with operator OSS/BSS systems

    Machine Learning for Predictive QoE

    Operators with sufficient historical data can deploy ML models to predict QoE degradation before it occurs. Gradient-boosted tree models (XGBoost/LightGBM) trained on labeled historical fault data have demonstrated the ability to predict CPE service degradation with 30–60 minutes of lead time at 85%+ precision. Key features include rolling statistical aggregations (mean, standard deviation, slope) of primary radio metrics over multiple time windows (5 min, 15 min, 1 hour, 24 hours).

    CPE Hardware Requirements for QoE-Ready Deployments

    Not all CPE hardware is equally capable of supporting the telemetry and analytics architecture described above. Operators should specify the following minimum requirements in their CPE RFPs:

    • CPU headroom: At least 15% idle CPU capacity under peak throughput for telemetry agent processing
    • Memory: Minimum 512 MB RAM with 128 MB reserved for telemetry buffering
    • TR-369 USP support: Full USP agent with Push Notification, Bulk Data Collection, and Data Model Object operations
    • Time synchronization: NTP or PTP support with <100ms clock accuracy for event correlation across the fleet
    • On-device buffering: Minimum 1-hour telemetry buffer for WAN-disconnected graceful degradation

    Implementation Roadmap for Operators

    Operators should approach QoE management implementation in three phases:

    Phase 1 (Months 1–3): Deploy basic telemetry collection on all CPE — radio metrics, throughput, and latency probes. Establish per-device baselines and implement threshold-based alerting for critical degradation events. Integrate with existing NOC dashboards.

    Phase 2 (Months 4–9): Implement multi-metric correlation rules, deploy the streaming analytics pipeline, and introduce baseline deviation detection. Begin collecting application-layer QoE probes. Automate tier-1 fault diagnosis to reduce NOC ticket volume.

    Phase 3 (Months 10–18): Train and deploy ML-based predictive degradation models. Implement closed-loop remediation for common fault patterns (e.g., automated band/channel reassignment, carrier aggregation reconfiguration). Extend QoE visibility to customer self-service portals.

    Conclusion: QoE as Competitive Differentiator

    As FWA markets mature and competition intensifies — particularly in urban and suburban deployments where FWA competes directly with fiber and cable — subscriber QoE management becomes a critical differentiator. Operators that invest in proactive, data-driven QoE architectures can reduce churn by an estimated 15–25%, decrease NOC ticket volume by 30–40% through automated fault detection, and command premium pricing for SLA-backed service tiers.

    For operators and ISPs evaluating CPE suppliers, QoE telemetry capability should be a key evaluation criterion alongside traditional metrics like throughput, band support, and cost. Honlly Telecom’s 4G and 5G FWA CPE portfolio includes full TR-369 USP telemetry support with configurable data models designed for carrier-grade QoE management deployments. Contact the Honlly engineering team to discuss QoE integration requirements for your FWA network.


    For technical specifications on Honlly Telecom’s QoE-ready 4G/5G FWA CPE portfolio and TR-369 USP telemetry integration support, contact sales@xmhonlly.com.
  • Open RAN CPE Interoperability Certification Program Launches: O-RAN ALLIANCE Validates Multi-Vendor 5G Fixed Wireless Access Devices in Q2 2026

    Open RAN CPE Interoperability Certification Program Launches: O-RAN ALLIANCE Validates Multi-Vendor 5G Fixed Wireless Access Devices in Q2 2026

    O-RAN ALLIANCE Launches Formal CPE Interoperability Certification Program

    The O-RAN ALLIANCE confirmed the launch of its formal Open RAN CPE Interoperability Certification Program in Q2 2026, establishing a standardized testing framework that validates multi-vendor compatibility for 5G Fixed Wireless Access (FWA) customer premises equipment. The program addresses what operators have long identified as a critical barrier to open RAN adoption at the device layer: the absence of a unified certification path that guarantees a CPE from Vendor A will perform seamlessly on a gNB from Vendor B using O-RAN split architectures.

    For telecom operators, ISPs, and MVNOs procuring CPE at scale, this certification program represents a structural shift in procurement flexibility. The new framework test suite covers O-RAN 7.2x split interoperability, O-DU/O-RU conformance with major RAN silicon platforms, end-to-end throughput validation under loaded network conditions, and beam management performance across multi-vendor mmWave and sub-6GHz configurations.

    What the Certification Covers

    O-RAN 7.2x Split Validation

    The certification’s core testing profile validates CPE behavior across the O-RAN 7.2x functional split — the most widely adopted fronthaul architecture in commercial Open RAN deployments. Certified devices must demonstrate consistent performance across O-DU and O-RU combinations from at least three different silicon ecosystems, including Qualcomm FSM, Intel FlexRAN, and Marvell OCTEON platforms. This multi-platform validation eliminates the single-vendor lock-in that has historically constrained operator equipment sourcing strategies.

    End-to-End Throughput Under Load

    Certification testing includes sustained multi-user throughput scenarios: 4×4 MIMO configurations at 100 MHz channel bandwidth (sub-6GHz) and 8×8 MIMO at 400 MHz (mmWave), with traffic models simulating real-world operator loading patterns. Devices must maintain at least 95% of rated peak throughput for a minimum of 72 consecutive hours in a multi-cell interference environment.

    Security and OAM Interoperability

    The framework also validates NETCONF/YANG-based OAM interoperability, ensuring certified CPE can be managed through operator ONAP and SMO frameworks without proprietary middleware. Security certification includes 3GPP SA3-compliant authentication and key agreement, O-RAN security specifications for the R1 interface, and zero-touch provisioning compatibility per BBF TR-369 USP.

    Implications for Operator Procurement

    The certification program has immediate implications for telecom procurement teams planning 5G FWA rollouts in the second half of 2026 and beyond. Operators in markets such as India, Southeast Asia, Latin America, and Africa — where Open RAN is central to greenfield 5G deployment strategies — can now reference a formal O-RAN CPE certification when drafting RFPs. This reduces the technical evaluation burden on procurement teams and provides a defensible basis for multi-vendor sourcing decisions.

    For MVNOs and smaller regional operators, the certification lowers the barrier to entry for operating their own CPE supply chains. Rather than being locked into the device portfolios of a single network equipment provider, certified Open RAN CPE enables competitive sourcing from multiple ODMs and OEMs — including Honlly Telecom’s 5G FWA portfolio, which is being prepared for O-RAN certification testing.

    Industry Adoption Timeline

    The first wave of certified devices is expected to complete testing by Q3 2026, with operator field trials commencing shortly thereafter. Major tier-1 operators in Asia-Pacific and Europe have already signaled that O-RAN CPE certification will become a mandatory requirement in their 2027 FWA procurement cycles. Industry analysts project that certified Open RAN CPE could account for 18–22% of global 5G FWA device shipments by 2028, driven primarily by cost-competitive multi-vendor sourcing and operator desire to reduce RAN vendor dependency.

    What This Means for CPE Manufacturers

    For CPE OEMs and ODMs, the certification program introduces both opportunity and engineering investment requirements. Manufacturers must integrate O-RAN fronthaul interface compliance into their device roadmaps, implement NETCONF/YANG management interfaces, and complete the multi-platform validation testing — a process expected to require 8–12 weeks of lab testing per device model. However, certified status opens access to operator RFPs that were previously exclusive to vertically integrated equipment vendors, significantly expanding the addressable market for independent CPE manufacturers.

    Honlly Telecom is actively engaging with the O-RAN ALLIANCE certification framework and has aligned its 5G FWA CPE development roadmap with the published test specifications. Operators and distributors interested in O-RAN-certified CPE sourcing can contact the Honlly engineering team for pre-certification device specifications and integration support.


    Source: O-RAN ALLIANCE press releases and industry analyst briefings, June 2026. For more information on Honlly Telecom’s 5G FWA CPE portfolio and O-RAN interoperability readiness, contact sales@xmhonlly.com.

  • CPE Firmware Security Architecture for Telecom Operators: A Technical Framework for Secure Boot, OTA Update Integrity, and Zero-Trust Device Management

    CPE Firmware Security Architecture for Telecom Operators: A Technical Framework for Secure Boot, OTA Update Integrity, and Zero-Trust Device Management

    In the rush to evaluate 5G NR specifications, carrier aggregation capabilities, and antenna performance, one dimension of CPE procurement receives far less attention than it deserves: firmware security architecture. Yet for telecom operators deploying tens of thousands of CPE units across consumer and enterprise networks, a single firmware vulnerability can transform a fleet of customer-premises equipment into a distributed botnet, a network intrusion vector, or a large-scale service outage waiting to happen.

    The 2025 Mirai-variant attacks that exploited compromised CPE devices to launch terabit-scale DDoS attacks against European ISPs served as a wake-up call. In response, major operators — including Deutsche Telekom, BT Group, and NTT — have updated their CPE procurement RFPs to include detailed firmware security requirements that go well beyond basic password protection. This article provides a technical framework for operators and procurement teams evaluating CPE firmware security posture.

    Secure Boot: The Foundation of CPE Trust

    Secure boot is the first line of defense in any modern CPE security architecture. At its core, secure boot ensures that only cryptographically signed firmware images can execute on the device, establishing a hardware-rooted chain of trust from the bootloader through the operating system kernel to the application layer.

    For carrier-grade CPE, secure boot should be implemented using a hardware root of trust (HRoT) — typically a dedicated secure element or a Trusted Platform Module (TPM 2.0) integrated into the main SoC. The HRoT stores an immutable public key (or hash of the public key) that is used to verify the digital signature of the first-stage bootloader. Each subsequent stage in the boot chain verifies the next before handing off execution control.

    Procurement teams should verify that CPE vendors implement secure boot at the silicon level rather than through software-only mechanisms. Software-only secure boot implementations can be bypassed by any attacker with physical access to the device’s storage or debugging interfaces. Key questions for vendors: Which security processor or TPM is integrated? Is the root of trust immutable (burned into one-time-programmable fuses)? Does the platform support authenticated secure firmware updates through all boot stages?

    Over-the-Air Update Integrity and Rollback Protection

    CPE devices deployed in the field must receive firmware updates throughout their operational lifetime — typically 3–7 years for carrier-grade equipment. The OTA update mechanism is simultaneously the most critical security maintenance channel and the most attractive attack surface for adversaries seeking to distribute malicious firmware at scale.

    A robust CPE OTA architecture should include four essential security properties:

    1. End-to-End Signature Verification: Firmware images must be signed by the vendor’s private key at build time, and the CPE must verify this signature before writing any bytes to flash. This prevents man-in-the-middle firmware substitution during transit over the operator’s update infrastructure.

    2. Anti-Rollback Protection: The CPE must reject firmware images with a version number lower than the currently installed version, preventing attackers from downgrading to vulnerable older firmware releases. Anti-rollback counters should be stored in secure, non-volatile memory (eFuses or secure storage within the TEE) rather than in rewritable flash.

    3. Atomic Update Transactions: Firmware updates should be applied as atomic transactions using an A/B partition scheme. If the update fails at any point — due to power loss, network interruption, or integrity check failure — the CPE must automatically fall back to the previous known-good partition. This prevents bricking and ensures service continuity.

    4. Delta Update Support: For large-scale deployments with constrained backhaul, CPE should support binary delta updates that transmit only the changed bytes between firmware versions. This reduces bandwidth consumption and shortens the vulnerability window during mass-update campaigns.

    Trusted Execution Environment and Runtime Integrity

    Beyond secure boot and OTA, carrier-grade CPE should implement a Trusted Execution Environment (TEE) — such as ARM TrustZone or Intel SGX — to isolate security-critical operations from the main operating system. The TEE provides a hardware-enforced boundary that protects cryptographic key material, authentication credentials, and device identity data even if the main OS is compromised.

    Key functions that should execute within the TEE include: TLS/TEAP certificate private key operations for 802.1X network authentication, storage and derivation of device-unique identifiers used for TR-069/TR-369 ACS registration, and runtime integrity measurement (RIM) that continuously verifies the integrity of critical system binaries and configuration files against known-good hashes.

    Zero-Trust Device Identity and Network Access Control

    Modern operator networks are adopting zero-trust architectures that treat every device as potentially compromised until it proves otherwise during each network session. For CPE, this means implementing IEEE 802.1X with EAP-TLS for network admission, where each CPE presents a unique device certificate issued by the operator’s PKI infrastructure.

    The device certificate should be provisioned during manufacturing (using an IDevID — Initial Device Identifier — per IEEE 802.1AR) and renewed during the operator’s onboarding process. Critically, the private key associated with the device certificate must never leave the TEE — all cryptographic operations using this key should be performed within the secure enclave.

    Operators should require CPE vendors to provide a PKI integration guide that documents the certificate enrollment protocol (SCEP, EST, or CMPv2), supported key algorithms (RSA-2048 minimum, ECC P-256 minimum), and the secure key storage architecture. Vendors that support automated certificate lifecycle management — including renewal before expiry and revocation on decommissioning — significantly reduce the operational burden of maintaining a zero-trust device fleet.

    Security Certification and Compliance Frameworks

    Several industry standards and certification programs provide independent validation of CPE firmware security posture. Operators should prioritize vendors whose products carry relevant certifications:

    • GSMA NESAS (Network Equipment Security Assurance Scheme): Provides a security assessment framework for mobile network equipment, including CPE. NESAS-audited products have undergone independent security evaluation against 3GPP-defined security requirements (SCAS).
    • ETSI EN 303 645: The European consumer IoT security baseline standard, increasingly referenced in operator CPE RFPs as a minimum security bar. Covers password policy, vulnerability disclosure, software update mechanisms, and data protection.
    • IEC 62443-4-2: Industrial automation and control system security standard applicable to CPE deployed in utility, transportation, and industrial IoT environments.
    • FIPS 140-3: U.S. federal cryptographic module validation standard — relevant for CPE deployed in government and defense applications.

    FAQ

    What is secure boot in CPE and why does it matter?

    Secure boot is a hardware-enforced mechanism that ensures only cryptographically signed firmware can execute on a CPE device. It creates an immutable chain of trust from the bootloader through the operating system, preventing attackers from injecting malicious firmware. For operators, it is the foundational security layer protecting the entire device fleet from firmware-level compromise.

    How should operators verify CPE OTA update security?

    Operators should verify four properties: end-to-end firmware signature verification (vendor-signed images), anti-rollback protection (stored in secure non-volatile memory), atomic update transactions (A/B partition scheme with automatic fallback), and delta update support for bandwidth-efficient mass updates. Request documented evidence of each from the CPE vendor.

    What is a Trusted Execution Environment (TEE) in CPE?

    A TEE is a hardware-enforced isolated processing environment within the CPE’s main processor that protects security-critical operations — such as cryptographic key operations and device identity management — from the main operating system. Even if the main OS is compromised, data and operations within the TEE remain protected. ARM TrustZone is the most common TEE implementation in CPE SoCs.

    Why is zero-trust device identity important for CPE networks?

    Zero-trust architecture requires each CPE to prove its identity during every network session using IEEE 802.1X with device-specific certificates. This prevents rogue or compromised devices from gaining network access, even if they possess valid network credentials. The device certificate’s private key must be stored within the TEE and never leave the secure enclave.

    What security certifications should operators look for in CPE?

    Key certifications include GSMA NESAS (3GPP-defined security audit for mobile network equipment), ETSI EN 303 645 (European consumer IoT baseline), IEC 62443-4-2 (industrial/utility deployments), and FIPS 140-3 (U.S. government cryptographic validation). Certified products have undergone independent evaluation, reducing the operator’s own security assessment burden.

    Source Security-Hardened CPE from Honlly Telecom

    Honlly Telecom’s carrier-grade CPE portfolio incorporates hardware-rooted secure boot, TEE-isolated key storage, A/B atomic OTA updates with anti-rollback protection, and 802.1X device identity provisioning for zero-trust operator networks. Contact our engineering team to discuss your security requirements.

    Contact Honlly Telecom →

  • A Network Operator’s Practical Guide to CPE Power over Ethernet (PoE) Architecture: From PoE Type Selection to Multi-Gigabit Outdoor Deployments

    A Network Operator’s Practical Guide to CPE Power over Ethernet (PoE) Architecture: From PoE Type Selection to Multi-Gigabit Outdoor Deployments

    Specify the outdoor CPE and its power supply as one installation package. Before selecting an injector, switch or backup supply, confirm the exact device variant and the power requirements in its current documentation. A PoE connection does not by itself establish compatibility with every PoE switch or injector.

    Identify the power arrangement

    Ask whether the device uses a standards-based negotiated PoE arrangement or a vendor-specific power connection. Confirm the input requirements, connector arrangement and compatible supplied accessories in writing. Do not substitute an injector solely because its connector looks the same.

    Check the entire cable run

    Record the proposed cable length, routing, environmental exposure and required Ethernet data rate. Have the installation reviewed against the device and cable specifications, including power delivery over the actual run. Check any inline adapter or protection device for the required data and power compatibility.

    Plan protection and mounting

    Outdoor mounting, cable entry, grounding and surge protection should follow the applicable installation requirements and manufacturer instructions. A device-level protection rating does not describe the protection of the complete building installation. Request a site-specific review where required.

    Review a backup-power option

    For a kit with battery backup, confirm which devices are powered, the supported output arrangement and the selected battery configuration. Test loss and restoration of mains power with the agreed kit. Confirm runtime under the intended load rather than assuming a fixed duration from battery capacity alone.

    HL-6300R project information

    The HL-6300R page provides the outdoor unit, indoor router and supplied power-kit specifications. Battery options are 5000mAh standard, with 10000mAh or 20000mAh available on request. Confirm the ordered power configuration and current documentation before selecting third-party accessories.

    Related procurement guides

    HL-850UE indoor CPE specifications · HL-6300R outdoor router kit specifications · Request a project quotation

    Confirm model-specific support for each required feature; a technical guide does not establish that every feature is available on these products.

  • Global Outdoor 5G CPE Shipments Surge 47% YoY in H1 2026: mmWave and Sub-6GHz Site Engineering Best Practices Driving Fixed Wireless Access Expansion

    Global Outdoor 5G CPE Shipments Surge 47% YoY in H1 2026: mmWave and Sub-6GHz Site Engineering Best Practices Driving Fixed Wireless Access Expansion

    The global outdoor 5G CPE market is experiencing one of its strongest growth phases on record. According to preliminary Q2 2026 data from ABI Research and Dell’Oro Group, outdoor CPE shipments grew approximately 47% year-over-year in the first half of 2026, driven by expanded rural broadband funding programs, accelerated mmWave network rollouts in dense urban corridors, and a growing wave of Wireless Internet Service Provider (WISP) deployments across North America, Europe, and Southeast Asia.

    This surge reflects a structural shift in how operators approach last-mile connectivity. Fixed Wireless Access (FWA) is no longer a stopgap technology — it has become the primary broadband delivery mechanism for millions of households and businesses, and outdoor CPE is the critical hardware anchor that determines the quality, reliability, and longevity of those connections.

    mmWave and Sub-6GHz Co-Deployment Drives New CPE Requirements

    One of the defining trends in 2026 is the increasing prevalence of dual-band outdoor CPE that supports both mmWave (FR2) and Sub-6GHz (FR1) frequencies within a single enclosure. Operators who initially launched FWA services on 3.5 GHz mid-band spectrum are now layering mmWave capacity in high-density zones, requiring CPE that can seamlessly aggregate across both frequency ranges.

    This co-deployment model places new demands on outdoor CPE hardware: wider antenna bandwidth coverage (covering n77/n78 through n257/n258/n260), more sophisticated beam management algorithms, and thermal engineering capable of dissipating the additional heat generated by mmWave front-end modules operating in direct sunlight. Manufacturers who invested early in gallium nitride (GaN) power amplifiers and advanced heat-pipe cooling architectures are seeing disproportionate demand from Tier-1 operators.

    Site Engineering Becomes the Differentiator

    As outdoor CPE hardware specifications converge across vendors, site engineering and installation quality have emerged as the real differentiators in FWA service performance. Operators report that properly engineered installations — accounting for azimuth alignment, Fresnel zone clearance, pole-mount stability, and lightning protection — yield 30–40% higher throughput consistency compared to suboptimal deployments.

    Leading operators are now investing in AI-assisted installation tools that use smartphone-based augmented reality to guide field technicians through optimal antenna positioning. Vodafone’s European FWA operations reported a 22% reduction in truck rolls after deploying computer-vision-based alignment verification across their outdoor CPE install base in Q1 2026.

    For procurement teams evaluating outdoor CPE, the vendor’s installation support ecosystem — including mobile alignment apps, spectrum analyzers with API integration, and certified installer training programs — should carry as much weight as the hardware specifications themselves.

    Regulatory Tailwinds and Rural Broadband Funding

    Government broadband subsidy programs continue to fuel outdoor CPE demand. The European Union’s Connecting Europe Broadband Fund allocated an additional €1.2 billion for rural FWA infrastructure in May 2026, while the second phase of the U.S. Broadband Equity, Access, and Deployment (BEAD) program released $6.4 billion in matching funds specifically earmarked for fixed wireless projects in unserved census blocks.

    In emerging markets, outdoor CPE is bridging the connectivity gap at an even faster pace. Reliance Jio’s JioAirFiber service in India, which relies heavily on outdoor CPE installations, added 8.2 million subscribers in the first five months of 2026, according to TRAI data. Similar growth trajectories are visible in Indonesia, Nigeria, and Brazil, where national operators are deploying outdoor FWA as the primary vehicle for meeting universal service obligations.

    Implications for CPE Procurement in H2 2026

    For ISPs, operators, and system integrators planning outdoor CPE procurement in the second half of 2026, several strategic considerations emerge. First, dual-band mmWave+Sub-6GHz capability is transitioning from a premium feature to a baseline requirement for greenfield deployments. Second, vendors with integrated installation tooling and AI-assisted site engineering software will deliver measurably better total cost of ownership.

    Third, supply chain diversification remains critical — operators should qualify at least two outdoor CPE vendors per frequency band to mitigate single-source risk, particularly given ongoing silicon allocation constraints in the mmWave RF front-end supply chain. Finally, outdoor CPE with embedded eSIM (eUICC) support is gaining traction as operators seek to streamline logistics and enable remote carrier profile switching across multi-market deployments.

    FAQ

    What is driving the surge in outdoor 5G CPE shipments in 2026?

    The surge is driven by three factors: expanded government broadband subsidy programs (BEAD in the U.S., CEBF in Europe), accelerated mmWave network deployments in urban corridors, and the maturation of FWA as a primary broadband delivery mechanism rather than a secondary option. Outdoor CPE is the critical endpoint hardware enabling these deployments.

    What is the difference between mmWave and Sub-6GHz outdoor CPE?

    mmWave (FR2) outdoor CPE operates in the 24–52 GHz range and delivers multi-gigabit throughput over shorter distances, ideal for dense urban deployments. Sub-6GHz (FR1) CPE operates below 6 GHz and provides broader coverage with lower throughput, suitable for suburban and rural FWA. Modern dual-band CPE combines both in a single unit for optimal performance across deployment scenarios.

    Why is site engineering important for outdoor CPE performance?

    Proper outdoor CPE installation — including precise azimuth alignment toward the serving cell tower, ensuring Fresnel zone clearance, secure pole-mounting, and adequate lightning protection — can improve throughput consistency by 30–40% compared to suboptimal installations. AI-assisted installation tools are increasingly used to verify alignment quality.

    What should operators look for when procuring outdoor CPE?

    Operators should evaluate dual-band capability (mmWave + Sub-6GHz), thermal engineering for outdoor environments, integrated installation tooling (mobile alignment apps, spectrum analyzer integration), eSIM/eUICC support for logistics efficiency, and vendor supply chain diversification to mitigate single-source risk.

    How is government funding affecting outdoor CPE adoption?

    Government broadband programs are a primary growth driver. The U.S. BEAD program released $6.4 billion for fixed wireless projects, and the EU’s CEBF allocated €1.2 billion for rural FWA. These subsidies make outdoor FWA economically viable for operators serving low-density areas, directly increasing outdoor CPE demand.

    Source Outdoor 5G CPE from a Trusted Manufacturer

    Honlly Telecom offers a comprehensive portfolio of outdoor 5G CPE solutions — including dual-band mmWave+Sub-6GHz models — with carrier-grade certifications, AI-assisted installation tooling, and flexible OEM/ODM engagement models. Contact our engineering team to discuss your deployment requirements.

    Contact Honlly Telecom →

  • CPE Chipset Diversification Accelerates in 2026: How New Silicon Entrants Are Reshaping 4G/5G Router Supply Chains and Reducing Single-Vendor Dependency for Telecom Operators

    CPE Chipset Diversification Accelerates in 2026: How New Silicon Entrants Are Reshaping 4G/5G Router Supply Chains and Reducing Single-Vendor Dependency for Telecom Operators

    The 4G/5G CPE chipset landscape is undergoing its most significant structural shift since the transition from LTE to 5G NR. After years of concentration among a handful of dominant silicon vendors, 2026 is witnessing an accelerating diversification of the modem and SoC supply chain — a development with direct implications for telecom operators, ISPs, and enterprise buyers who depend on predictable CPE pricing, stable lead times, and multi-source procurement strategies.

    The Shifting Silicon Landscape

    For much of the past five years, the CPE chipset market has been heavily concentrated. Qualcomm’s SDX series and MediaTek’s T-series have dominated 5G FWA and mobile router designs, while legacy 4G CAT4/CAT6 CPE segments have been served primarily by MediaTek, Qualcomm, and a small number of secondary suppliers including UNISOC and ASR Microelectronics. This concentration created supply chain fragility that became painfully visible during the 2021–2023 semiconductor shortage, when CPE manufacturers faced 26–52 week lead times on critical modem components.

    By mid-2026, the picture has changed materially. Three structural forces are reshaping the CPE silicon supply chain:

    • New fab capacity coming online. TSMC’s expanded mature-node capacity (28nm–12nm) and SMIC’s growing domestic Chinese wafer output have meaningfully increased the total available manufacturing bandwidth for IoT and CPE-grade chipsets. These processes are ideal for cost-sensitive CAT4/CAT6 and entry-level 5G RedCap modems.
    • Second-wave 5G chipset entrants reaching production maturity. UNISOC’s Ivy 5G platform, ASR’s 5G NR modem portfolio, and Eigencomm’s cellular IoT SoCs have moved from sampling to volume production, giving CPE OEMs and ODMs credible multi-source options for the first time.
    • RedCap creating a new silicon category. 3GPP Release 17 NR-Light (RedCap) defines a streamlined 5G modem profile that reduces die area, power consumption, and cost versus full-spec 5G NR. This has attracted new silicon entrants who see RedCap as a lower-barrier entry point into the 5G CPE market, bypassing the massive R&D investment required for full-spec eMBB modem development.

    What Multi-Source Means for Telecom Buyers

    For operators and ISPs procuring CPE at scale, chipset diversification translates into three tangible procurement benefits:

    1. Reduced single-vendor dependency risk. The ability to qualify CPE devices built on multiple chipset platforms means a supply disruption at any one silicon vendor does not halt an operator’s entire subscriber acquisition pipeline. Several Tier-1 European operators now explicitly require dual-source chipset qualification in their CPE RFPs — a clause that was virtually unheard of in 2023.

    2. Improved pricing dynamics. Genuine silicon competition at the CAT6, CAT12, and entry-level 5G tiers is beginning to exert downward pressure on BOM costs. Industry analysts estimate that RedCap CPE BOM costs could fall below $45 by late 2026, down from $60–70 in 2024, driven largely by modem chipset competition and mature-node wafer cost improvements.

    3. Regional supply optionality. The emergence of domestic Chinese chipset vendors with full 4G/5G modem portfolios creates regional supply chain optionality. Operators in markets without US export control restrictions can now source CPE devices with locally manufactured chipsets, potentially reducing logistics complexity and tariff exposure.

    The RedCap Catalyst

    5G RedCap (NR-Light) deserves special attention as the catalyst for silicon diversification. Unlike full-spec 5G eMBB modems — which require complex RF front-end architectures supporting 4×4 MIMO across multiple bands, carrier aggregation across low/mid/high bands, and 256QAM/1024QAM modulation — RedCap strips the modem specification down to a more constrained but still highly useful profile: 2 receive antennas (versus 4), 1 or 2 transmit antennas, 256QAM in downlink, and simplified carrier aggregation with a single carrier in FR1 supporting up to 20 MHz bandwidth.

    This simpler specification reduces silicon die area by approximately 60–65% compared to full-spec 5G modems. The resulting cost structure makes RedCap commercially viable for chipset vendors who could not justify the R&D investment for full-spec 5G modem development. The GSMA now projects RedCap device shipments exceeding 80 million units annually by 2028, with CPE and FWA devices representing the largest single category.

    Qualification Considerations for Operators

    While chipset diversification is broadly positive for the CPE ecosystem, operators must approach multi-source qualification with structured evaluation criteria. Key considerations include:

    • Modem-RF interoperability validation. Each modem-plus-RF-front-end combination must be validated against the operator’s specific band plan, carrier aggregation combinations, and network feature set (VoLTE/VoNR, IMS, emergency calling). A chipset that performs well in lab conditions may exhibit unexpected behavior with a specific operator’s RAN vendor configuration.
    • Firmware maturity and update cadence. Newer chipset entrants may have less mature modem firmware with respect to power management, thermal throttling, and mobility handling (cell reselection, handover). Operators should request firmware release histories and field deployment references before committing to volume orders.
    • Regulatory certification coverage. Multi-source CPE procurement must verify that each chipset variant holds the necessary regulatory certifications for the operator’s target markets — FCC (US), CE (EU), Anatel (Brazil), SRRC/CCC (China), and others as required.
    • Long-term roadmap alignment. Does the chipset vendor have a credible roadmap to 3GPP Release 18 (5G-Advanced) features including AI-native air interface optimizations and enhanced positioning? Operators investing in network upgrades need CPE silicon that will support forthcoming RAN capabilities, not just today’s feature set.

    Strategic Implications for 2026–2027

    The CPE chipset supply chain is transitioning from a seller’s market to a more balanced — and in some segments, buyer-friendly — environment. For telecom operators and ISPs, the strategic implications are clear:

    • Now is the time to qualify second-source chipsets. Operators who initiate multi-source qualification programs in 2026 will have approved alternative silicon options available before the next supply disruption — not scrambling during it.
    • RedCap should feature in every CPE RFP issued in H2 2026. Whether as a primary requirement for cost-sensitive segments or as an optional alternative for specific deployment scenarios, RedCap represents a genuine new category of CPE silicon that operators should be evaluating.
    • Silicon diversity strengthens negotiation leverage. CPE OEMs and ODMs with multi-chipset design capability — like Honlly Telecom, which maintains design references across Qualcomm, MediaTek, UNISOC, and ASR platforms — offer operators genuine procurement flexibility rather than single-source lock-in.

    As the CPE ecosystem matures through 2026, chipset diversification will increasingly differentiate the supply chain capabilities of CPE manufacturers. Operators and ISPs who proactively build multi-source silicon requirements into their procurement frameworks will be better positioned to navigate the next phase of 5G network expansion — with more predictable costs, more resilient supply chains, and more competitive CPE portfolios.

    For more information about Honlly Telecom’s multi-chipset CPE portfolio and OEM/ODM capabilities, contact our sales team at sales@xmhonlly.com.

  • A Technical Guide to IPv6 Transition Strategies in 4G/5G CPE: Dual-Stack, DS-Lite, MAP-T, and 464XLAT Implementation for Carrier-Grade Deployments

    A Technical Guide to IPv6 Transition Strategies in 4G/5G CPE: Dual-Stack, DS-Lite, MAP-T, and 464XLAT Implementation for Carrier-Grade Deployments

    As global IPv4 address exhaustion accelerates and regional Internet registries deplete their remaining /8 allocations, telecom operators and ISPs face an unavoidable architectural transition: every new CPE device deployed must support IPv6 — and in many networks, must bridge the gap between IPv6-only carrier infrastructure and legacy IPv4-dependent applications and services. This technical guide examines the four primary IPv6 transition mechanisms relevant to 4G/5G CPE deployments: dual-stack, DS-Lite, MAP-T, and 464XLAT. For telecom procurement teams specifying CPE requirements, understanding which transition mechanism a device must support is not optional — it is foundational to network architecture.

    Why CPE-Level IPv6 Matters Now

    The business case for IPv6 in CPE is no longer theoretical. Several structural factors have made IPv6 support a hard requirement in carrier CPE RFPs:

    • IPv4 address costs have reached $55–60 per address on the transfer market as of Q2 2026, making large-scale IPv4-only subscriber deployments economically unsustainable for operators adding hundreds of thousands of new subscribers annually.
    • Major content providers are IPv6-native. Google, YouTube, Netflix, Facebook, and Akamai all serve content preferentially over IPv6. In networks with native IPv6 CPE, 70–85% of subscriber traffic now traverses IPv6 paths, dramatically reducing CGNAT (Carrier-Grade NAT) load.
    • Mobile network operators are going IPv6-only. T-Mobile US, Reliance Jio, EE (UK), and several other Tier-1 MNOs operate IPv6-only mobile cores with 464XLAT for IPv4 compatibility. Any CPE connecting to these networks must support the operator’s chosen transition mechanism.
    • 5G Standalone mandates IPv6. 3GPP specifications for 5G SA core networks are fundamentally IPv6-native. While dual-stack operation is possible, operators deploying 5G SA increasingly require IPv6-only or IPv6-dominant CPE configurations.

    Transition Mechanism 1: Dual-Stack (Native IPv4 + IPv6)

    Dual-stack is the simplest and most widely deployed IPv6 transition model. In a dual-stack CPE configuration, the device simultaneously operates both IPv4 and IPv6 protocol stacks, acquiring both an IPv4 address (via DHCPv4 or static configuration) and an IPv6 address (via SLAAC, DHCPv6, or static configuration) on its WAN interface.

    How it works in CPE: The CPE WAN interface runs both protocol stacks. On the LAN side, the CPE typically provides DHCPv4 for IPv4 address assignment and SLAAC/DHCPv6-PD (Prefix Delegation) for IPv6 address assignment to connected devices. Traffic routing is straightforward — IPv4 packets follow IPv4 routes, IPv6 packets follow IPv6 routes.

    Advantages:

    • Maximum application compatibility — every IPv4 and IPv6 application works without translation
    • Simple CPE firmware implementation with mature, well-tested code paths in Linux kernel and OpenWRT
    • No additional latency from protocol translation
    • Supports all existing enterprise VPN, VoIP, and legacy application use cases

    Limitations:

    • Requires the operator to maintain both IPv4 and IPv6 infrastructure, including IPv4 address pools
    • Does not solve the IPv4 address exhaustion problem — merely defers it
    • Doubles the routing table and firewall rule complexity in CPE

    CPE procurement specification: “CPE must support dual-stack IPv4/IPv6 operation on WAN interface with RFC 8106 (DNS RA options), DHCPv6-PD (RFC 8415) for LAN prefix delegation, and stateful DHCPv6 for address assignment. DNS must resolve both A and AAAA records.”

    Transition Mechanism 2: DS-Lite (Dual-Stack Lite)

    DS-Lite (RFC 6333) enables operators to deploy IPv6-only access networks while still delivering IPv4 connectivity to subscribers. This is the preferred model for operators who have exhausted their IPv4 address pools but need to maintain IPv4 service for legacy applications.

    How it works in CPE: The CPE (called the B4 element in DS-Lite terminology) receives only an IPv6 address on its WAN interface — no IPv4 address is assigned by the operator network. When a LAN client initiates an IPv4 connection, the CPE encapsulates the IPv4 packet inside an IPv6 tunnel (IP-in-IP, protocol 4) and forwards it to the operator’s AFTR (Address Family Transition Router). The AFTR decapsulates the IPv4 packet and performs NAT44 using a shared IPv4 address pool, then routes the packet to the IPv4 Internet.

    Key CPE considerations:

    • The CPE must discover the AFTR address, typically via DHCPv6 option 64 (AFTR_NAME)
    • The CPE B4 element performs NAPT (Network Address and Port Translation) locally for IPv4 traffic before encapsulation, ensuring each subscriber’s IPv4 traffic is properly source-NATed
    • All IPv6 traffic bypasses the tunnel and routes directly — only IPv4-in-IPv4 traffic traverses the AFTR
    • Port forwarding for IPv4 services behind the CPE requires AFTR-side configuration (PCP, Port Control Protocol, RFC 6887)

    CPE procurement specification: “CPE must support DS-Lite B4 element operation per RFC 6333 with AFTR discovery via DHCPv6 option 64. CPE must perform NAPT44 locally for IPv4 traffic before encapsulation and support PCP (RFC 6887) for inbound IPv4 port mapping.”

    Transition Mechanism 3: MAP-T (Mapping of Address and Port using Translation)

    MAP-T (RFC 7599) is a stateless IPv4-over-IPv6 transition mechanism that eliminates the centralized AFTR bottleneck of DS-Lite by distributing IPv4 address sharing across CPE devices using algorithmic address and port mapping. MAP-T is gaining significant traction among European operators, having been specified as the IPv6 transition mechanism for the EU’s Connecting Europe Broadband Fund projects.

    How it works in CPE: Each CPE is provisioned with a MAP-T rule set that algorithmically maps a shared IPv4 address and a restricted port range to the CPE’s unique IPv6 prefix. When a LAN client sends an IPv4 packet, the CPE translates the source address to the shared IPv4 address with a port number from its allocated range, then encapsulates the packet in IPv6 using the algorithmic mapping. The border relay (BR) at the operator edge performs the reverse mapping for inbound traffic — all statelessly, without maintaining per-flow state.

    Advantages over DS-Lite:

    • No centralized stateful AFTR — the border relay is stateless, eliminating a scalability bottleneck and single point of failure
    • Deterministic port allocation — operators can calculate exactly which CPE is using which ports for lawful intercept and abuse management
    • Mesh-capable — MAP-T supports direct CPE-to-CPE IPv4 communication without hair-pinning through a central node

    CPE procurement specification: “CPE must support MAP-T CE operation per RFC 7599 including MAP rule provisioning via DHCPv6 options 94/95. CPE must perform NAPT44 within its provisioned port set and must verify port set parity before establishing MAP-T encapsulation.”

    Transition Mechanism 4: 464XLAT

    464XLAT (RFC 6877) is the IPv6 transition mechanism of choice for mobile network operators and is increasingly specified in 5G FWA CPE deployments where the CPE connects to an IPv6-only mobile core. It combines stateful NAT64 on the operator side with stateless CLAT (Customer-side Translator) on the CPE side.

    How it works in CPE: The CPE runs a CLAT function that performs stateless SIIT (Stateless IP/ICMP Translation, RFC 7915) — translating IPv4 packets from LAN clients into IPv6 packets by embedding the IPv4 address into a well-known IPv6 prefix (typically 64:ff9b::/96). These IPv6 packets traverse the operator’s IPv6-only core and reach a NAT64 gateway at the network edge, which translates them back to IPv4 for the public Internet.

    464XLAT is particularly important for 5G FWA CPE because:

    • T-Mobile US and other major 5G operators operate IPv6-only cores with 464XLAT as the mandated IPv4 compatibility mechanism
    • 3GPP TS 23.501 specifies 5G PDU sessions as IPv6-native, with 464XLAT as the designated mechanism for IPv4 service continuity
    • Android and iOS devices natively support 464XLAT — the CLAT function simply needs to operate at the CPE level for LAN-attached devices

    CPE procurement specification: “CPE must support 464XLAT CLAT function per RFC 6877 with SIIT translation per RFC 7915. CLAT must use the well-known prefix 64:ff9b::/96 or operator-provisioned NAT64 prefix via RFC 7050 (IPv6-only network prefix discovery). CLAT must handle IPv4 DNS-to-IPv6 DNS translation (DNS64 synthesis).”

    Implementation Comparison Matrix

    MechanismOperator IPv4 RequirementCPE WAN ProtocolStateful ElementBest For
    Dual-StackFull IPv4 address poolIPv4 + IPv6NoneOperators with ample IPv4; legacy compatibility
    DS-LiteShared IPv4 (AFTR)IPv6-onlyAFTR (centralized)Fixed broadband ISPs; DOCSIS/FTTx
    MAP-TShared IPv4 (stateless)IPv6-onlyNone (stateless BR)European operators; mesh-friendly
    464XLATShared IPv4 (NAT64)IPv6-onlyNAT64 gatewayMobile/FWA operators; 5G SA cores

    CPE Firmware and Performance Considerations

    Beyond protocol support, telecom buyers evaluating CPE for IPv6 transition deployments should verify several firmware-level implementation quality indicators:

    • Hardware offload compatibility. DS-Lite and MAP-T encapsulation/decapsulation benefits significantly from hardware-accelerated packet processing. CPE platforms using hardware flow offload (e.g., MediaTek HNAT, Qualcomm NSS) should be validated to handle IPv4-in-IPv6 tunnel traffic at line rate without software-forwarding fallback.
    • DNS handling. In DS-Lite and 464XLAT deployments, the CPE must correctly handle DNS resolution — ensuring AAAA queries resolve natively over IPv6 while A queries are either synthesized (DNS64) or tunneled appropriately.
    • MTU and fragmentation. IPv4-in-IPv6 encapsulation adds 40 bytes of IPv6 header overhead. CPE must properly clamp TCP MSS (Maximum Segment Size) to account for tunnel overhead and avoid path MTU discovery black holes.
    • VoIP and real-time traffic. SIP ALG and RTP media handling must function correctly across transition mechanisms. MAP-T’s restricted port range can conflict with RTP/RTCP port pair conventions — operators deploying VoIP behind MAP-T CPE should verify SIP registration and RTP media path functionality.
    • UPnP and NAT-PMP. Consumer applications relying on UPnP IGD or NAT-PMP for automatic port mapping will not function behind DS-Lite or MAP-T without PCP (Port Control Protocol) support. Operators targeting residential deployments should verify PCP interoperability between CPE and AFTR/BR.

    Procurement Recommendations for Operators

    For telecom operators and ISPs issuing CPE RFPs in 2026, the following IPv6 transition requirements should be considered baseline:

    1. Specify the transition mechanism explicitly. Do not simply request “IPv6 support.” Specify whether the CPE must operate in dual-stack, DS-Lite, MAP-T, or 464XLAT mode — including the relevant RFC numbers for each mechanism.
    2. Request multi-mode capability. The ideal CPE supports all four transition mechanisms and can be reconfigured via TR-069/TR-369 provisioning. This future-proofs the CPE fleet against operator network architecture evolution.
    3. Validate with your core network. Lab-test CPE candidates against your specific core network configuration — including your AFTR, NAT64 gateway, or MAP-T border relay implementation. Protocol conformance to RFC does not guarantee interoperability with a specific vendor’s network elements.
    4. Include performance SLAs. Specify that IPv4-in-IPv6 tunnel throughput must achieve at least 95% of native IPv6 throughput at the CPE’s rated WAN speed, with no more than 2ms additional latency attributable to encapsulation.
    5. Verify management plane functionality. Ensure that TR-069/TR-369 ACS communication, firmware upgrade, and device telemetry all function correctly in the CPE’s designated IPv6 transition mode — management plane failures in IPv6-only networks are a common deployment issue.

    The IPv6 transition is no longer a future consideration — it is the present network architecture for the world’s fastest-growing operator networks. CPE that fails to support the operator’s chosen transition mechanism is not merely technically deficient; it is commercially unusable. Procurement teams that embed precise, RFC-referenced IPv6 transition requirements into their CPE specifications will avoid costly requalification cycles and ensure their subscriber CPE fleet is architecturally aligned with the operator’s network evolution roadmap.

    Honlly Telecom’s 4G/5G CPE portfolio supports dual-stack, DS-Lite, MAP-T, and 464XLAT transition mechanisms across all current platforms. For technical specifications and interoperability validation support, contact sales@xmhonlly.com.
  • IoT Connectivity: Endpoint and Gateway Selection

    IoT Connectivity: Endpoint and Gateway Selection

    Enterprise IoT is not a single connectivity problem — it is a portfolio of connectivity problems, each with distinct requirements for throughput, latency, power consumption, coverage range, device density, and cost sensitivity. A smart meter in a basement, an HD surveillance camera on a highway gantry, an agricultural soil sensor in a rural field, and a factory AGV navigating a shop floor all require connectivity — but the optimal radio technology and CPE architecture for each differs fundamentally.

    This guide provides a structured comparison of the four dominant IoT connectivity technologies — 4G LTE (Cat-1 through Cat-18), 5G NR (eMBB and RedCap), NB-IoT, and LoRaWAN — across the dimensions that matter most to system integrators and enterprise buyers selecting IoT gateways, routers, and endpoint CPE.

    Technology Overview

    4G LTE (Cat-1 to Cat-18)

    LTE remains the workhorse of cellular IoT. The ecosystem spans ultra-low-power Cat-1bis (10 Mbps downlink, suitable for basic telemetry and POS terminals) through Cat-4 (150 Mbps, the standard for most enterprise IoT gateways) to Cat-18 (1.2 Gbps, used for video backhaul and high-bandwidth industrial applications). LTE’s advantage lies in its global coverage footprint — 3GPP reports over 800 commercial LTE networks worldwide — and a mature device ecosystem with aggressive per-unit pricing. For enterprise IoT gateways aggregating multiple sensor streams or requiring reliable VPN tunnel support, Cat-4 and Cat-6 LTE modules remain the pragmatic default choice in 2026.

    5G NR (eMBB and RedCap)

    For enterprise IoT, compare device and network options using payload size, reporting interval, mobility, power and application response requirements. Verify the selected variant and operator service; headline technology rates are not guaranteed application throughput.

    NB-IoT (LTE Cat-NB1/NB2)

    For an NB-IoT proposal, confirm endpoint network support, data requirements, power arrangement and the operator service. Distinguish endpoints that connect directly to the cellular network from any separately proposed aggregation gateway.

    LoRaWAN

    LoRaWAN operates in unlicensed sub-GHz spectrum (868 MHz in Europe, 915 MHz in North America), offering multi-kilometre range in rural environments and excellent building penetration at the cost of very low data rates (0.3–50 kbps) and duty-cycle limitations. As an unlicensed technology, LoRaWAN eliminates spectrum access costs but introduces reliability trade-offs in interference-heavy urban environments. LoRaWAN gateways serve as the bridge between endpoint devices and cloud application servers, typically backhauling over Ethernet, LTE, or Wi-Fi.

    Comparative Analysis: Eight Dimensions

    DecisionEvidence to request
    Coverage and serviceProvider availability and a site test for the proposed installation
    Device capabilityExact model, bands, firmware, interfaces and supported network functions
    Application behaviourRepresentative payload, response, power and recovery measurements
    Commercial scopeCurrent hardware, service, integration and support quotations

    Application-to-Technology Mapping

    Selecting the right connectivity technology starts with a clear understanding of the application profile:

    Video Surveillance and Analytics

    Recommended: 4G LTE Cat-6/12 or 5G NR CPE. Multi-camera deployments generating 5–50 Mbps sustained uplink require the capacity and reliability of licensed-spectrum cellular. LTE Cat-6 (300 Mbps) handles 4–8 HD camera streams cost-effectively; 5G NR CPE is warranted for 4K multi-camera analytics, especially where AI inference runs at the edge and low latency is critical for real-time alerting.

    Smart Metering and Utility Infrastructure

    For a metering project, define payload size, reporting interval, installation coverage and service requirements. Confirm the actual endpoint power specification and network behaviour before agreeing battery-life expectations.

    Industrial Automation and AGV/AMR

    AGV connectivity: the responsible control and safety teams should define the communications architecture and acceptance criteria. Compare candidate systems in representative coverage and mobility tests. A generic cellular or WiFi category does not establish suitability for safety functions or deterministic control.

    Agriculture and Environmental Monitoring

    Recommended: LoRaWAN for wide-area sensor networks; LTE Cat-1bis for gateway backhaul. Soil moisture sensors, weather stations, and livestock trackers spread across hundreds of hectares benefit from LoRaWAN’s multi-kilometre range and battery-operated endpoint economics. A solar-powered LoRaWAN gateway with LTE Cat-1bis backhaul provides the bridge to cloud analytics platforms.

    Smart City and Public Infrastructure

    Recommended: Hybrid 4G/5G gateways with NB-IoT and LoRaWAN concentrator capability. Smart city deployments — parking sensors, waste bin fill-level monitors, streetlight controllers, air quality sensors — mix ultra-low-power endpoints with medium-bandwidth video applications (traffic cameras, ANPR). A multi-radio CPE gateway supporting NB-IoT/LoRaWAN concentration plus LTE/5G WAN backhaul provides a unified connectivity architecture.

    Total Cost of Ownership Comparison

    Beyond per-unit hardware cost, enterprise IoT buyers must evaluate TCO over a typical 5–7 year deployment lifecycle:

    • Cellular cost review: request current hardware and service quotations for the coverage, data usage, installation and support required. Include any antennas, local infrastructure and management costs in the project budget.
    • LoRaWAN cost review: identify the network arrangement, gateway placement, local operating requirements and service responsibilities. Obtain current quotations and validate site coverage rather than assuming a fixed radius, fee or gateway cost.

    Procurement Recommendations

    1. Start with the application profile, not the technology. Define throughput, latency, mobility, power, and density requirements before evaluating technology options.
    2. Plan for hybrid architectures. Most enterprise IoT deployments above 500 endpoints require at least two connectivity technologies. Select CPE gateways that support multiple radio types and protocol bridging.
    3. Evaluate 5G RedCap for mid-tier IoT refresh cycles. If your LTE Cat-4 gateways are approaching end-of-life in 2027–2028, RedCap offers a cost-effective migration path with 5G core network benefits (network slicing, enhanced security) at comparable module cost.
    4. Spectrum and service review: assess interference, coverage and application requirements for each candidate network. Licensed or unlicensed operation alone does not establish an application service-level guarantee.
    5. IoT service procurement: compare current provider terms for pooled usage, roaming, activation, support and expected traffic. Use the proposed fleet profile to evaluate cost instead of assuming a universal low monthly tariff.

    Frequently Asked Questions

    Which IoT connectivity technology has the lowest total cost of ownership?

    Compare connectivity options using the installation geography, endpoint mobility, required infrastructure and current service terms. Build the cost comparison from the actual devices and network arrangement.

    Is 5G NR overkill for most IoT applications?

    For many IoT applications — smart meters, environmental sensors, asset trackers — full 5G NR eMBB is indeed excessive. However, 5G RedCap (NR-Light) specifically addresses the mid-tier segment where LTE Cat-4 is appropriate today but will become capacity-constrained in dense environments. RedCap bridges the gap between LPWA and eMBB at attractive unit economics.

    Can I mix multiple IoT technologies in a single CPE gateway?

    Yes. Multi-radio IoT gateways combining LTE/5G WAN backhaul with NB-IoT and/or LoRaWAN concentrator functionality are increasingly available from specialist CPE manufacturers. These gateways serve as protocol bridges, aggregating data from diverse endpoint types and backhauling over a single cellular connection to the cloud platform.

    What role does eSIM/eUICC play in IoT CPE deployments?

    eSIM (eUICC) is particularly valuable for IoT deployments because it enables remote operator profile switching without physical SIM replacement — critical for devices deployed in inaccessible locations, multi-country logistics tracking, and operator redundancy for mission-critical applications. Most cellular IoT modules shipping in 2026 include integrated eSIM capability.

    Does Honlly Telecom offer IoT gateway and CPE solutions?

    Yes. Honlly Telecom manufactures a comprehensive range of IoT connectivity hardware including 4G LTE Cat-4/Cat-6 industrial gateways, 5G NR CPE for high-bandwidth IoT applications, multi-radio concentrator gateways with NB-IoT and LoRaWAN support, and custom IoT CPE solutions tailored to enterprise and system integrator requirements.


    Planning an enterprise IoT connectivity deployment?
    Contact Honlly Telecom to discuss your IoT gateway requirements, technology selection, and custom CPE development.
    Discuss Your IoT Project →

  • How to Select an OEM/ODM Manufacturing Partner for Telecom CPE: A 12-Point Due Diligence Framework for ISPs, Operators, and MVNOs

    How to Select an OEM/ODM Manufacturing Partner for Telecom CPE: A 12-Point Due Diligence Framework for ISPs, Operators, and MVNOs

    Select an OEM or ODM CPE partner by matching documented capabilities to the proposed product and deployment. A useful review covers the model specification, sample validation, firmware scope, documentation, production controls and agreed supply terms.

    Define the project before requesting a quotation

    Provide the target country and operator, network requirements, installation format, expected quantity and intended users. Identify required interfaces, power arrangements and management features. State which features are mandatory and which can be reviewed during sampling.

    Confirm the hardware and firmware scope

    Ask for the current model specification and a written list of proposed changes. Separate branding and packaging from changes to hardware, RF configuration and firmware. Confirm how the sample and production configuration will be identified.

    Review documentation for the exact model

    Request applicable model-specific test and approval records for the intended market. Check the holder, model, scope and dates. A general company certificate or platform description should not replace documentation for the ordered device.

    Agree sample acceptance criteria

    Test the device on the intended network, with the proposed power accessories and firmware. Include connectivity, local interfaces, management, recovery behaviour and installation requirements in the agreed test plan. Record results and open issues before approving the configuration.

    Plan replacement and support arrangements

    Confirm firmware support, issue escalation, spare accessories, warranty terms and change notification as part of the quotation. Request current order quantity and delivery terms rather than relying on assumed lead times.

    Prepare a Honlly enquiry

    Send the preferred model, market, operator, quantity and customization requirements. For indoor and outdoor projects, compare the HL-850UE and HL-6300R specifications first, then request confirmation of the configuration needed for your project.

    Related procurement guides

    HL-850UE indoor CPE specifications · HL-6300R outdoor router kit specifications · Request a project quotation

    Confirm model-specific support for each required feature; a technical guide does not establish that every feature is available on these products.