Author: openclaw-Lisa-New

  • Industrial-Grade 5G CPE Enclosure Design: IP67/IK08 Certification, Extended Temperature Operation, and Surge Protection Engineering for Mission-Critical Outdoor Deployments

    Industrial-Grade 5G CPE Enclosure Design: IP67/IK08 Certification, Extended Temperature Operation, and Surge Protection Engineering for Mission-Critical Outdoor Deployments

    As 5G FWA deployments extend beyond climate-controlled indoor environments into outdoor, industrial, and remote locations, the physical enclosure design of the CPE device becomes a critical engineering discipline. Industrial-grade 5G CPE must withstand extreme temperatures, moisture ingress, dust contamination, physical impact, vibration, and electrical surge events — all while maintaining reliable multi-gigabit wireless connectivity. This article examines the key environmental certification standards, enclosure design principles, and procurement considerations for ruggedized 5G CPE in mission-critical B2B applications.

    Ingress Protection: IP67 and Beyond

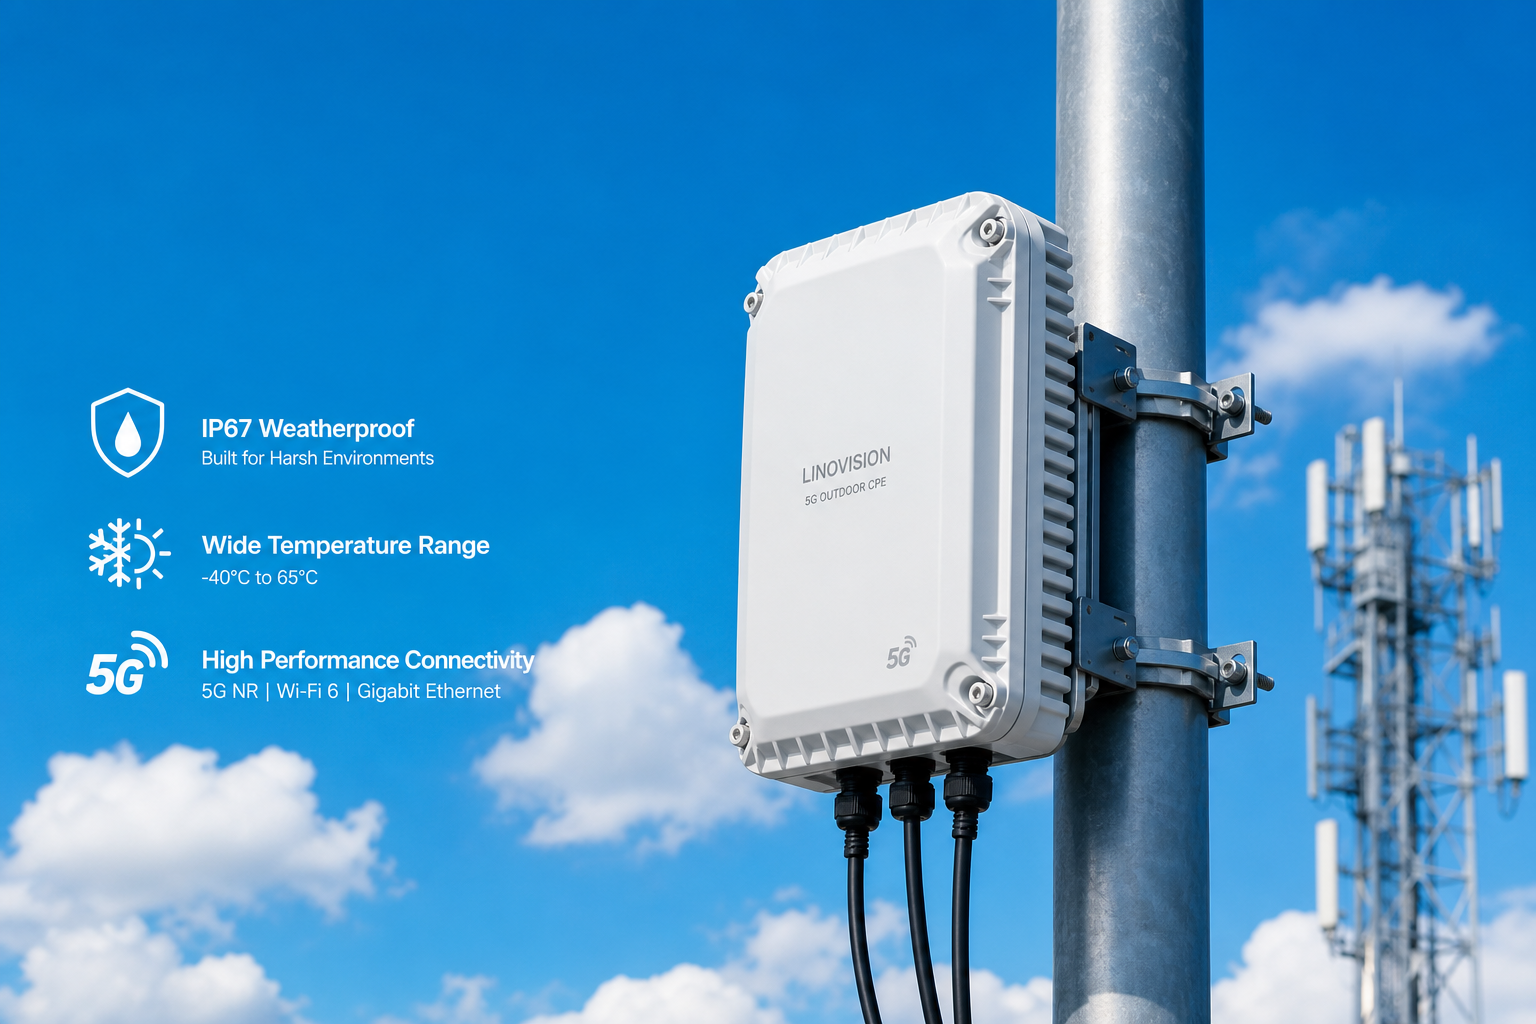
    The IP (Ingress Protection) rating system, defined by IEC 60529, is the primary standard for evaluating enclosure resistance to solid particles and liquid ingress. For outdoor 5G CPE deployments, IP67 represents the practical minimum requirement — the “6” indicates complete protection against dust ingress (dust-tight), while the “7” guarantees protection against temporary immersion in water up to 1 meter depth for 30 minutes.

    However, industrial environments often demand more stringent protection. IP68 certification extends immersion depth beyond 1 meter (typically 1.5–3 meters, as specified by the manufacturer), while IP69K — originally developed for the automotive and food processing industries — provides protection against high-pressure, high-temperature water jets (80°C at 80–100 bar pressure). For CPE deployed in offshore energy platforms, mining operations, or food and beverage facilities, IP69K-rated enclosures ensure operational integrity despite aggressive washdown procedures and corrosive environmental exposure.

    The enclosure sealing strategy must address multiple ingress paths: cable glands and connector interfaces require compression seals with appropriate IP ratings; the SIM card access door needs double-gasket designs with captive fasteners; and ventilation membranes (typically ePTFE-based) must equalize internal pressure while blocking liquid and particulate ingress. Each sealing interface represents a potential failure point that must be validated through accelerated lifecycle testing.

    Impact Resistance: IK Rating Standards

    The IK rating system (IEC 62262) quantifies enclosure resistance to mechanical impact, measured in joules. IK08 (5 joules) is the common baseline for industrial CPE, equivalent to withstanding the impact of a 1.7 kg mass dropped from 300 mm. For deployments in construction sites, mining operations, transportation hubs, and public infrastructure, IK09 (10 joules) or IK10 (20 joules) ratings provide assurance against vandalism, falling debris, and accidental handling damage.

    Achieving high IK ratings requires careful material selection and structural design. Aluminum alloy enclosures (typically ADC12 or A380 die-cast aluminum) offer an optimal balance of impact resistance, thermal conductivity, and weight. The wall thickness, rib reinforcement patterns, and corner radius design must be optimized through finite element analysis (FEA) simulation to absorb impact energy without deforming internal component mounting points or compromising seal integrity.

    Polycarbonate and glass-reinforced polymer enclosures provide an alternative for applications requiring lighter weight or RF transparency. However, UV stabilization additives are essential to prevent polymer degradation from prolonged sun exposure. A 5-year UV aging test (per ISO 4892-2) with less than Delta-E 5 color shift and no significant reduction in impact resistance should be validated by the enclosure manufacturer.

    Extended Temperature Operation: From Arctic to Desert

    Industrial 5G CPE must operate reliably across extreme temperature ranges without active cooling. The industry benchmark for outdoor equipment is -40°C to +65°C operating temperature and -40°C to +85°C storage temperature, conforming to IEC 60068-2 environmental testing standards. Achieving this requires a holistic thermal management strategy encompassing component selection, thermal interface materials, and passive cooling design.

    At the component level, all integrated circuits — including the 5G modem, Wi-Fi chipset, Ethernet PHY, and power management IC — must be industrial-temperature-grade (-40°C to +85°C junction temperature). Memory components (LPDDR4X/LPDDR5 DRAM and eMMC/UFS storage) require similar industrial ratings. Electrolytic capacitors, which have limited low-temperature performance, should be replaced with solid polymer or MLCC alternatives in cold-climate designs.

    For high-temperature operation, the enclosure itself functions as a heat sink. Die-cast aluminum enclosures with integrated fin structures maximize surface area for convective and radiative heat dissipation. The thermal path from the 5G modem and application processor to the enclosure surface must minimize thermal resistance through the use of thermal gap pads, phase-change materials, or direct-die-contact thermal solutions. A maximum junction-to-ambient thermal resistance (Theta-JA) below 15°C/W for the primary SoC ensures stable operation at 65°C ambient without throttling.

    For extreme cold environments, self-heating strategies may be employed — using the modem and processor’s own power dissipation to warm internal components during startup. A cold-start sequence that gradually brings up power-hungry components while monitoring internal temperature sensors prevents condensation and thermal shock damage to solder joints and semiconductor packages.

    Surge Protection and Electrical Robustness

    Outdoor CPE installations face significant electrical hazards including lightning-induced surges, AC power cross events, and electrostatic discharge. Comprehensive surge protection must be implemented on all external interfaces: the power input (DC barrel jack or PoE), Ethernet ports, and antenna connectors.

    For Ethernet interfaces, compliance with ITU-T K.21 (basic-level surge protection, 1.5 kV) or the more stringent GR-1089-CORE (6 kV for ports, 5 kA for power feeds) is essential for carrier deployments. Gas discharge tubes (GDTs) provide the first line of defense against high-energy transients, with Transient Voltage Suppression (TVS) diode arrays clamping residual energy at the PHY level. The PCB layout must include sufficient creepage and clearance distances per IEC 60950-1/IEC 62368-1, with isolation slots where necessary to prevent arc-over between primary and secondary circuits.

    Power supply design must accommodate wide input voltage ranges (typically 12–57V DC for PoE PD applications, or 9–36V DC for direct DC input in vehicle and industrial applications) with reverse polarity protection, under-voltage lockout, and over-voltage shutdown. An isolated DC-DC converter topology (compliant with IEC 61800-5-1 for industrial drives when applicable) provides galvanic isolation between the power source and the CPE’s internal electronics.

    Corrosion Resistance and Material Durability

    For coastal deployments, marine environments, and chemical processing facilities, corrosion resistance becomes a primary enclosure design driver. Aluminum enclosures should receive chromate conversion coating (per MIL-DTL-5541 Type II Class 3) followed by polyester powder coating with a minimum 60-micron thickness. Salt spray testing per ASTM B117 for 500–1000 hours with no blistering or corrosion creep beyond 2 mm from scribe validates coating integrity.

    Stainless steel (304 or 316L grade) enclosures provide superior corrosion resistance for the most demanding environments but introduce RF shielding considerations that must be addressed through external antenna designs or RF-transparent window panels. All external fasteners should be stainless steel with appropriate thread-locking compounds to prevent galvanic corrosion at dissimilar metal junctions.

    Procurement Guidelines for Ruggedized 5G CPE

    B2B buyers evaluating industrial-grade 5G CPE should request comprehensive certification documentation including IP test reports from ISO 17025-accredited laboratories, IK impact test certificates, extended temperature validation data with thermal imaging analysis, surge compliance test reports, and corrosion resistance certification. Beyond certifications, field-proven deployment references in similar environmental conditions provide practical validation of enclosure design maturity.

    Total cost of ownership analysis should factor in the mean time between failures (MTBF) per Telcordia SR-332, expected enclosure service life (minimum 10 years for outdoor telecommunications equipment), and the availability of replacement seal kits and gaskets for periodic maintenance. A well-engineered industrial enclosure transforms 5G CPE from an indoor consumer device into a carrier-grade outdoor infrastructure element capable of delivering reliable connectivity in the world’s harshest operating environments.
  • 5G CPE Quality of Service Architecture: Deep Dive into 5QI-to-DSCP Mapping, Slice-Aware Traffic Steering, and Deterministic Latency for Enterprise-Grade Application Assurance

    5G CPE Quality of Service Architecture: Deep Dive into 5QI-to-DSCP Mapping, Slice-Aware Traffic Steering, and Deterministic Latency for Enterprise-Grade Application Assurance

    As enterprise 5G FWA deployments scale globally, Quality of Service (QoS) architecture within CPE devices has emerged as a critical differentiator for B2B connectivity solutions. Unlike consumer-grade gateways that treat all traffic equally, enterprise 5G CPE must implement sophisticated QoS frameworks that preserve service-level agreements (SLAs) across diverse application workloads — from latency-sensitive voice and video conferencing to throughput-intensive cloud backup and IoT telemetry.

    Understanding the 5G QoS Model: 5QI and QoS Flows

    The 3GPP 5G QoS model is fundamentally flow-based, representing a significant evolution from the 4G LTE bearer-centric architecture. Each QoS Flow is identified by a QoS Flow Identifier (QFI) and associated with a 5G QoS Identifier (5QI) that defines standardized performance characteristics. The 5QI table specifies resource type (GBR, non-GBR, or delay-critical GBR), priority level, packet delay budget (PDB), packet error rate (PER), and averaging window — all of which must be honored end-to-end through the CPE.

    For enterprise CPE implementations, the critical challenge lies in mapping these 5QI-defined flows to the IP-layer Differentiated Services Code Point (DSCP) markings that enterprise routers, switches, and application servers actually understand. A well-designed 5QI-to-DSCP mapping strategy ensures that QoS treatment established at the 5G core is preserved as traffic exits the CPE into the enterprise LAN or SD-WAN overlay.

    5QI-to-DSCP Mapping: Bridging 3GPP and IETF QoS Models

    The mapping from 5QI values to DSCP markings is not standardized by 3GPP — it requires careful operator configuration based on the enterprise’s internal QoS policy. A typical enterprise mapping might associate conversational voice (5QI=1) with DSCP EF (46), real-time gaming and V2X (5QI=3) with DSCP CS5 (40), and low-latency eMBB applications with DSCP AF41 (34).

    Advanced CPE implementations go beyond static mapping tables by supporting configurable 5QI-to-DSCP translation with per-QoS-Flow granularity. This enables operators to differentiate between multiple non-GBR flows carrying different application types, each receiving appropriate DSCP marking before entering the enterprise network. The CPE must also handle the reverse direction — remarking DSCP values on inbound LAN traffic to appropriate QFIs for uplink transmission — ensuring bidirectional QoS consistency.

    Network Slicing and Slice-Aware Traffic Steering

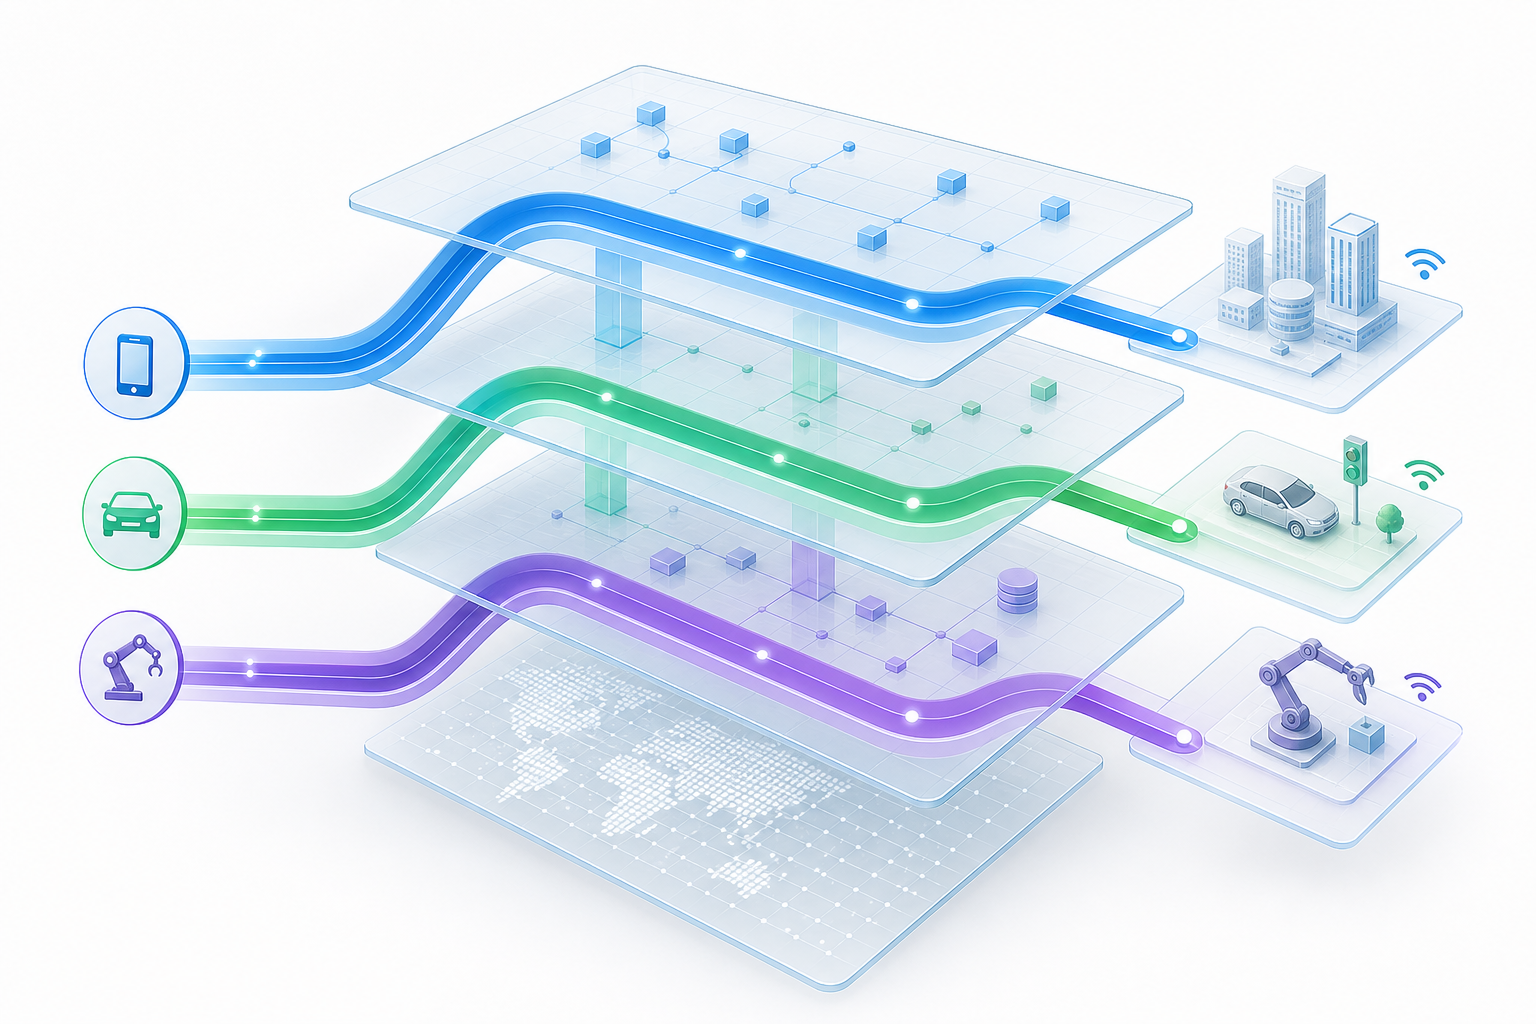
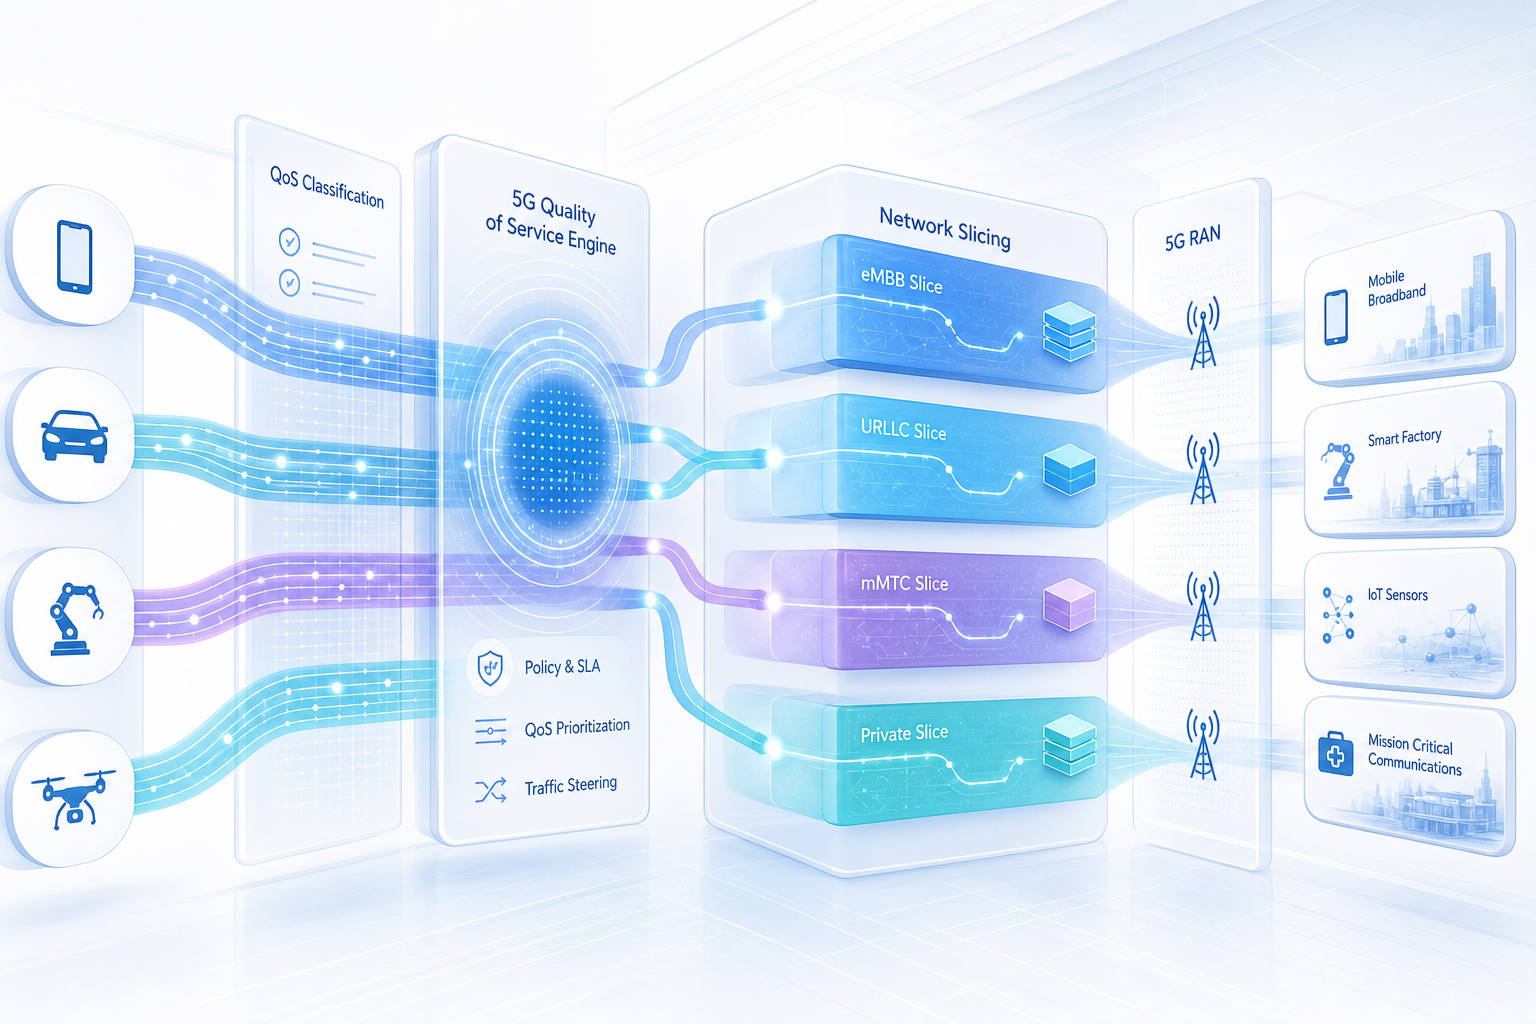
    5G network slicing introduces an additional dimension to CPE QoS architecture. Each network slice, identified by Single Network Slice Selection Assistance Information (S-NSSAI), may contain multiple QoS Flows. The CPE must implement slice-aware traffic steering that routes application traffic to the appropriate slice based on operator-configured URSP (UE Route Selection Policy) rules.

    For enterprise deployments, this enables powerful use cases: a manufacturing facility might operate three concurrent slices — an ultra-reliable slice for industrial control systems (URLLC), a high-bandwidth slice for video surveillance and AR maintenance (eMBB), and a massive IoT slice for sensor networks (mMTC) — all through a single 5G CPE device. The CPE’s internal packet classifier must inspect application traffic (by destination IP, port, protocol, DNN, or application ID) and steer each flow to the correct slice while applying appropriate 5QI and DSCP treatment.

    Deterministic Latency and Time-Sensitive Networking Integration

    The convergence of 5G with Time-Sensitive Networking (TSN) standards, specified in 3GPP Release 17 and enhanced in Release 18, enables deterministic latency guarantees for industrial automation and critical infrastructure. The 5G CPE functions as a TSN translator, bridging the 5G system’s QoS framework with IEEE 802.1 TSN mechanisms including time-aware scheduling (802.1Qbv), frame preemption (802.1Qbu), and per-stream filtering and policing (802.1Qci).

    When configured as a DS-TT (Device-Side TSN Translator), the CPE maintains precise time synchronization via IEEE 802.1AS and enforces gate control lists that guarantee bounded latency for critical data streams. This capability is essential for applications like motion control in smart factories, power grid protection systems, and autonomous vehicle coordination — where latency variation must be measured in microseconds, not milliseconds.

    CPE Buffer Management and Congestion Avoidance

    Enterprise-grade 5G CPE devices must implement intelligent buffer management to prevent the well-known bufferbloat problem from degrading latency-sensitive application performance. Active Queue Management (AQM) algorithms — such as CoDel (Controlled Delay), FQ-CoDel (Fair Queuing CoDel), or CAKE (Common Applications Kept Enhanced) — should be applied to the CPE’s WAN interface to maintain low queuing latency under load.

    Per-flow queuing with hierarchical token bucket (HTB) scheduling ensures fair bandwidth allocation across competing application flows, preventing a single bulk transfer from starving interactive traffic. For SD-WAN integrated CPEs, the QoS scheduler must coordinate with the overlay’s application-aware routing to ensure that traffic steered across the 5G link receives appropriate priority treatment throughout the entire path.

    Procurement Checklist for Enterprise QoS-Capable 5G CPE

    When evaluating 5G CPE solutions for QoS-sensitive enterprise deployments, B2B buyers should assess: support for configurable 5QI-to-DSCP mapping with per-flow granularity; URSP-based slice-aware traffic steering; integrated AQM with FQ-CoDel or equivalent; TSN translator capability for industrial applications; TR-369 USP remote management for QoS policy provisioning; and hardware offload for QoS processing at multi-gigabit throughput rates without CPU contention.

    A well-architected QoS framework within the 5G CPE is not merely a feature checkbox — it is the foundation upon which enterprise SLAs, application performance guarantees, and ultimately customer satisfaction are built. As 5G FWA continues its rapid expansion into enterprise verticals, QoS sophistication will increasingly separate carrier-grade CPE from consumer-grade alternatives.

  • 5G CPE with Integrated Wi-Fi 7 Drives Next-Generation Enterprise FWA Deployments as Multi-Gigabit Wireless Backhaul Converges with High-Density Indoor Coverage in 2026

    5G CPE with Integrated Wi-Fi 7 Drives Next-Generation Enterprise FWA Deployments as Multi-Gigabit Wireless Backhaul Converges with High-Density Indoor Coverage in 2026

    The convergence of 5G Fixed Wireless Access (FWA) with Wi-Fi 7 (IEEE 802.11be) is reshaping how enterprises deploy high-performance connectivity in 2026. As multi-gigabit 5G CPE devices become mainstream, integrating Wi-Fi 7 capabilities within the same platform delivers a unified wireless experience that spans both WAN backhaul and indoor LAN coverage — eliminating the traditional demarcation between carrier-grade access and enterprise-grade Wi-Fi.

    Wi-Fi 7: A Generational Leap for Enterprise Indoor Coverage

    Wi-Fi 7 introduces transformative features that directly complement 5G FWA deployments. Multi-Link Operation (MLO) allows simultaneous transmission across 2.4 GHz, 5 GHz, and 6 GHz bands, dramatically improving reliability and reducing latency. For enterprise environments — from open-plan offices to manufacturing floors — MLO ensures seamless roaming and consistent throughput even in high-density device scenarios.

    The 320 MHz channel bandwidth in the 6 GHz band, combined with 4096-QAM modulation, pushes theoretical throughput beyond 30 Gbps. When paired with a 5G FWA CPE delivering 3–5 Gbps WAN connectivity, the indoor Wi-Fi 7 layer no longer becomes the bottleneck. This alignment of WAN and LAN performance is critical for bandwidth-intensive enterprise applications including real-time 4K/8K video collaboration, cloud-based CAD/CAM workloads, and large-scale IoT data aggregation.

    Integrated CPE Architecture: Beyond the Gateway Model

    Modern 5G CPE devices embedding Wi-Fi 7 are evolving beyond simple gateway functionality. These integrated platforms combine 5G NR modem (supporting Sub-6 GHz and mmWave carrier aggregation), multi-core application processors, and Wi-Fi 7 tri-band radios within a single thermally optimized enclosure. This integration reduces deployment complexity, lowers total cost of ownership (TCO), and simplifies network management for enterprise IT teams.

    Key architectural advantages include unified policy enforcement — where QoS rules defined at the 5G core level are seamlessly mapped to Wi-Fi 7 access categories — and coordinated interference management across both radio domains. Enterprise branch offices, retail chains, and temporary construction sites benefit from plug-and-play deployment with carrier-grade reliability.

    Enterprise Use Cases Driving Adoption

    Several vertical sectors are leading Wi-Fi 7 + 5G FWA CPE adoption in 2026. Healthcare facilities leverage the combination for telemedicine suites requiring ultra-reliable low-latency communication (URLLC) alongside high-resolution medical imaging transfers. Educational campuses deploy these integrated CPEs to deliver equitable high-speed connectivity across classrooms, libraries, and outdoor learning spaces without costly fiber trenching.

    In the hospitality sector, hotels and conference centers use Wi-Fi 7-enabled 5G CPEs to provide symmetrical gigabit-grade internet access to hundreds of simultaneous users, supporting hybrid event models where in-person attendees share bandwidth with remote participants. Manufacturing plants deploy ruggedized versions for connecting industrial IoT sensors, autonomous guided vehicles (AGVs), and augmented reality maintenance systems over a single converged wireless infrastructure.

    Carrier and B2B Procurement Considerations

    For telecom operators and B2B buyers evaluating integrated 5G CPE + Wi-Fi 7 solutions, several factors merit attention. Interoperability with existing Wi-Fi 6/6E client devices must be seamless during the transition period. Support for WPA3 Enterprise security, 802.1X authentication, and RADIUS integration is non-negotiable for enterprise deployments. Additionally, remote management capabilities via TR-369 USP (User Services Platform) ensure operators can provision, monitor, and troubleshoot devices at scale without on-site intervention.

    As 5G-Advanced (3GPP Release 18) networks roll out globally through late 2026, integrated CPE platforms with Wi-Fi 7 will become the default choice for enterprise FWA deployments. The combination of multi-gigabit WAN connectivity and cutting-edge indoor wireless coverage represents a generational opportunity for B2B connectivity providers to differentiate their enterprise service offerings.

    About Honlly Telecom: Honlly Telecom delivers advanced 5G FWA CPE solutions supporting Wi-Fi 7, carrier aggregation, and enterprise-grade security features. Our integrated platforms serve operators and B2B customers across 60+ countries, enabling next-generation fixed wireless deployments with simplified deployment and comprehensive remote management capabilities.

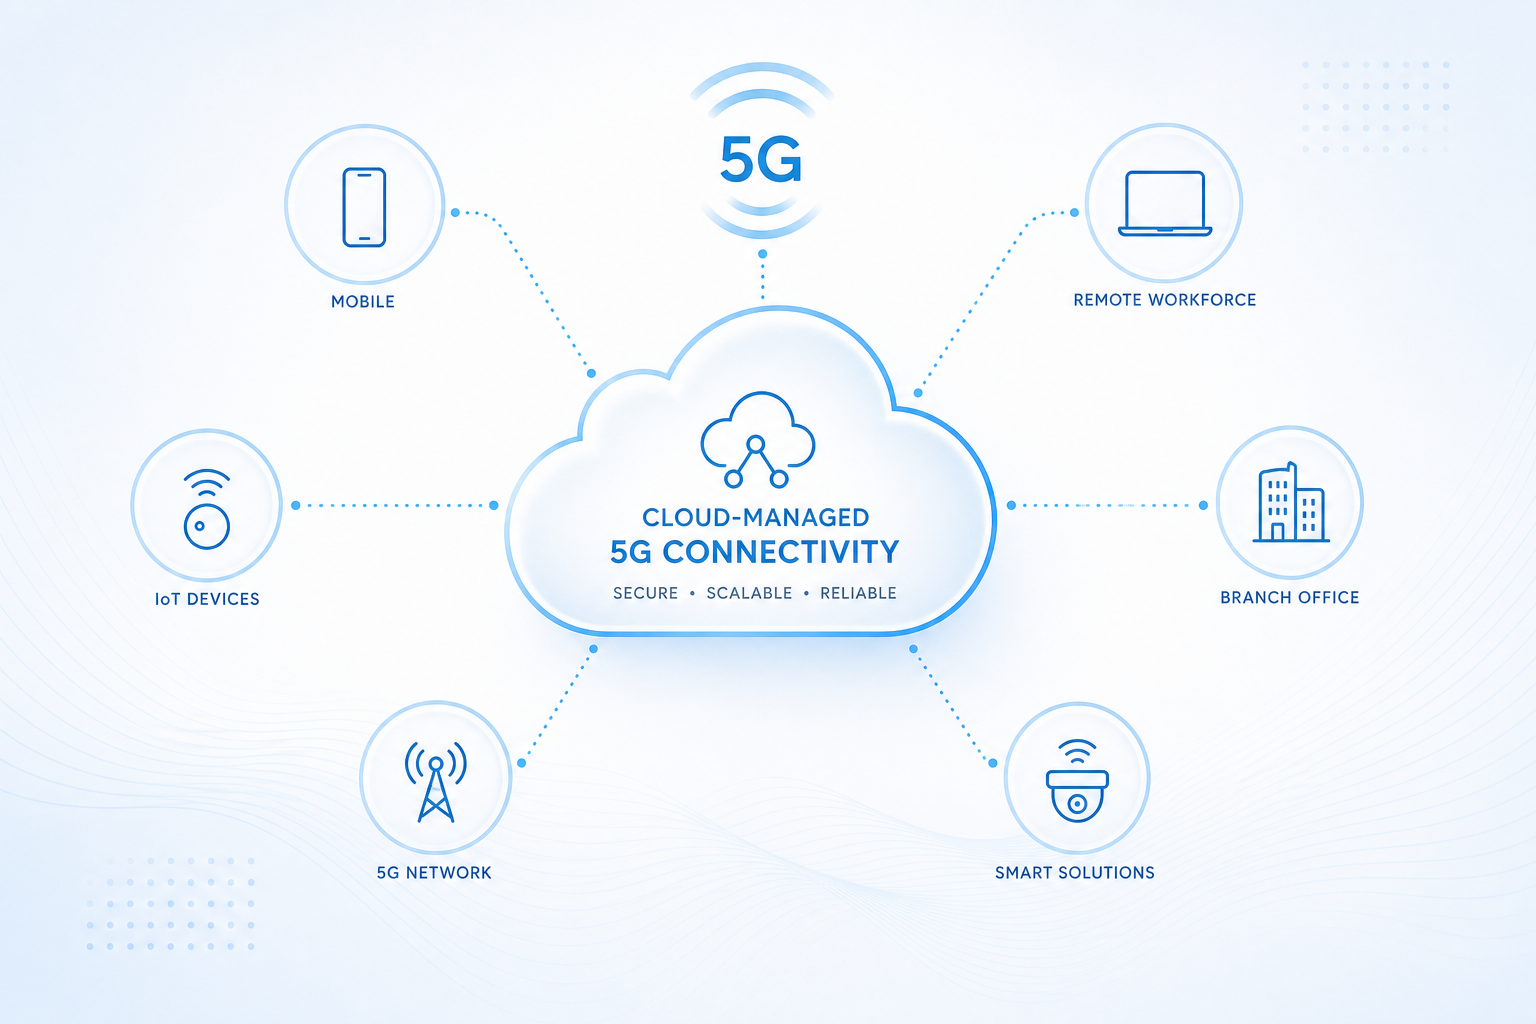
  • Cloud-Managed 5G CPE: TR-369 USP Evolution, Zero-Touch Provisioning, and Multi-Tenant Device Management for Global Telecom Operators

    Cloud-Managed 5G CPE: TR-369 USP Evolution, Zero-Touch Provisioning, and Multi-Tenant Device Management for Global Telecom Operators

    The operational paradigm for managing 5G fixed wireless access (FWA) customer premises equipment (CPE) at carrier scale is undergoing a fundamental transformation. As operator CPE fleets expand from thousands to millions of deployed devices, the legacy TR-069 (CWMP) protocol and on-premises ACS (Auto Configuration Server) architectures that served the DSL and early fiber era are giving way to cloud-native, TR-369 USP (User Services Platform)-based management frameworks. For telecom operators, MVNOs, and wholesale CPE buyers, understanding this evolution is critical for making informed procurement and deployment decisions in 2026 and beyond.

    From TR-069 to TR-369 USP: A Generational Shift

    The Broadband Forum’s TR-069 protocol (CWMP) has been the workhorse of broadband CPE management for nearly two decades, providing remote configuration, firmware upgrade, and diagnostic capabilities across hundreds of millions of devices. However, TR-069 was designed in an era of single-service DSL connections and presents fundamental limitations for modern multi-service 5G FWA deployments: its XML/SOAP-based messaging is bandwidth-intensive and processing-heavy; its connection model requires the ACS to initiate sessions through NAT traversal; and its data model lacks native support for the complex multi-WAN, network slicing, and IoT gateway functions of modern 5G CPE.

    TR-369 USP, standardized by the Broadband Forum in 2020 and now reaching widespread implementation maturity, addresses these limitations with a fundamentally modernized architecture. USP uses a binary-protocol-over-WebSocket or CoAP transport, supports both controller-initiated and agent-initiated messaging, enables bulk data collection through the scalable USP Record mechanism, and provides native IoT device proxy capabilities. Critically, USP is designed for cloud-native deployment—its microservices-friendly architecture aligns with the Kubernetes-orchestrated, horizontally scalable management platforms that Tier-1 operators are now deploying.

    Zero-Touch Provisioning: The ZTP Revolution

    One of the most transformative operational benefits of modern cloud-managed CPE platforms is zero-touch provisioning (ZTP). In the TR-069 era, CPE onboarding typically required manual intervention: pre-configuration at a staging facility, customer-side technician visits, or phone-based guided setup. With TR-369 USP and cloud-native management, operators can achieve true zero-touch deployment: the CPE boots, connects to any available WAN interface (5G, LTE, Ethernet), discovers its management controller via DHCP options, DNS SRV records, or pre-loaded bootstrap URLs, authenticates using device certificates or IMEI/ICCID-based identity, and automatically downloads its full service configuration—all without human intervention.

    For B2B operators deploying CPE at thousands of enterprise customer sites simultaneously, ZTP reduces deployment costs by an estimated 40-60% compared to staged or truck-roll provisioning models. Major CPE chipset vendors including Qualcomm (through its Device Management Framework) and MediaTek (via its Cloud CPE SDK) now provide integrated ZTP bootstrap libraries that simplify USP agent implementation for ODM/OEM manufacturers.

    Multi-Tenant Architecture for Wholesale and MVNO Deployments

    A critical capability that cloud-managed platforms bring to the B2B CPE ecosystem is true multi-tenancy. In wholesale and MVNO business models—increasingly common in the 5G FWA market—a single CPE hardware SKU may be deployed across multiple service provider tenants, each requiring isolated management visibility, distinct configuration profiles, and tenant-specific firmware branches. Cloud-native USP controllers implement tenant isolation at the platform layer, enabling a single management infrastructure to serve multiple operator customers while maintaining strict data and configuration separation.

    This multi-tenant architecture also simplifies the CPE supply chain: wholesale buyers can procure a single, cloud-manageable CPE model and assign devices to downstream operator tenants through software configuration alone—eliminating the need for per-operator hardware variants and reducing inventory complexity.

    Security Architecture for Cloud-Managed CPE

    The shift to cloud-based CPE management introduces heightened security requirements. Modern TR-369 USP implementations mandate mutual TLS (mTLS) authentication between the CPE agent and the USP controller, with X.509 device certificates provisioned at manufacturing time or during initial bootstrap. The USP protocol also defines end-to-end message security, role-based access control (RBAC) for multi-tenant controller access, and secure software module management for verified firmware updates.

    For procurement teams evaluating cloud-managed CPE solutions, security certification is paramount. Key certifications to look for include Broadband Forum BBF.369 USP certification, GSMA NESAS (Network Equipment Security Assurance Scheme) compliance for 5G devices, and relevant regional security certifications such as EUCC (EU) and FIPS 140-3 (North America).

    Procurement Considerations for 2026-2027

    When selecting cloud-manageable 5G CPE for carrier-grade deployments, B2B buyers should evaluate the following criteria:

    • USP protocol compliance: Full TR-369 USP 1.2+ support with USP Record, USP Bulk Data Collection, and USP Firmware Management modules.
    • Controller ecosystem compatibility: Certification with leading USP controller platforms including Axiros AXESS, Friendly Technologies, AOUSD, and open-source solutions like OB-USP-Agent.
    • ZTP maturity: Support for DHCP Option 43/60, DNS-based discovery (RFC 6763), and pre-loaded bootstrap URL mechanisms with secure device identity provisioning.
    • Multi-WAN management: Ability to manage 5G NR, LTE, Ethernet WAN, and Wi-Fi backhaul interfaces through a unified USP data model.
    • Analytics and telemetry: Support for streaming telemetry (gNMI/gRPC alongside USP) and integration with operator big-data platforms for AI-driven predictive maintenance.
    • Firmware lifecycle: A/B partition firmware architecture with USP-managed secure OTA updates and automated rollback capabilities.

    The transition from TR-069 to TR-369 USP represents more than a protocol upgrade—it is a strategic platform shift that enables operators to manage exponentially larger CPE fleets with lower operational overhead, faster service velocity, and richer customer experience analytics. For B2B buyers, selecting cloud-native, USP-compliant CPE today is an investment in operational scalability that will pay dividends through the 5G-Advanced and 6G eras ahead.

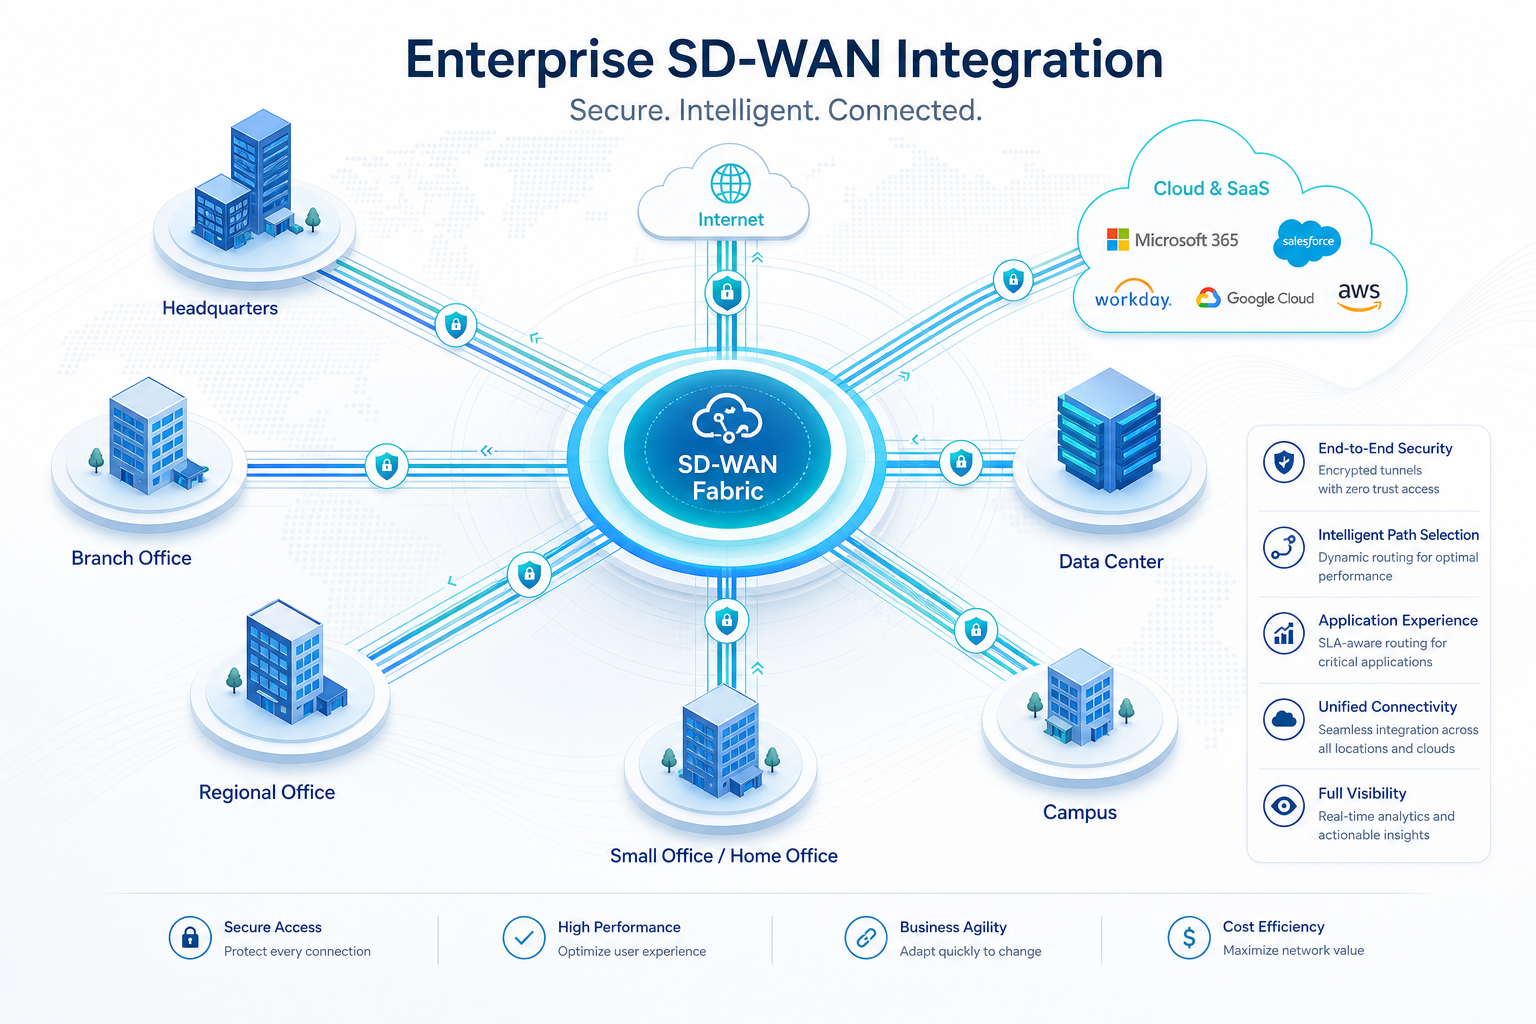
  • 5G CPE for Enterprise SD-WAN Integration: IPSec Acceleration, WireGuard Performance, and Hybrid WAN Overlay Architecture

    5G CPE for Enterprise SD-WAN Integration: IPSec Acceleration, WireGuard Performance, and Hybrid WAN Overlay Architecture

    As enterprise branch connectivity strategies evolve beyond MPLS-centric architectures, the convergence of 5G fixed wireless access (FWA) and software-defined wide-area networking (SD-WAN) has emerged as one of the most significant architectural shifts in enterprise networking. 5G CPE devices are no longer simple modem-to-Ethernet bridges—they are becoming intelligent SD-WAN edge nodes that integrate WAN link aggregation, application-aware traffic steering, and hardware-accelerated VPN termination. For enterprise IT teams and managed service providers (MSPs) architecting next-generation branch connectivity, understanding the integration patterns between 5G CPE and SD-WAN is essential.

    The 5G CPE as an SD-WAN Edge Platform

    Modern enterprise-grade 5G CPE devices have evolved significantly beyond the consumer-grade fixed wireless terminals of the early 5G era. High-end CPE platforms now integrate multi-core ARM or x86 processors, hardware security engines, and sufficient memory to run full SD-WAN software stacks directly on the CPE—eliminating the need for a separate SD-WAN appliance at the branch edge. This consolidation delivers several advantages: reduced hardware footprint and power consumption, simplified deployment (a single device to install and manage), and tighter integration between WAN link telemetry and SD-WAN policy enforcement.

    Key hardware capabilities that enable this convergence include: integrated hardware crypto accelerators supporting AES-GCM, SHA-256, and public-key operations at multi-gigabit line rates; dedicated traffic management engines with hierarchical QoS (HQoS) supporting per-application, per-tunnel, and per-interface queuing; and multi-WAN architectures that combine 5G NR, LTE, Ethernet, and Wi-Fi backhaul interfaces within a single CPE platform.

    IPSec and WireGuard Performance Considerations

    VPN overlay performance is the critical metric for SD-WAN-integrated 5G CPE. Enterprises running latency-sensitive applications (VoIP, video conferencing, real-time trading) and high-throughput workloads (file replication, cloud backup, VDI) require the CPE to sustain near-line-rate encrypted throughput across concurrent tunnels. Two VPN protocols dominate the 5G CPE SD-WAN landscape:

    IPSec: The incumbent enterprise VPN standard, IPSec benefits from decades of optimization and widespread hardware offload support. Modern 5G CPE chipsets from Qualcomm (IPQ series networking processors) and MediaTek (Filogic platforms) include dedicated IPSec crypto engines capable of sustaining 2-5 Gbps of AES-256-GCM encrypted throughput. For enterprises with existing IPSec-based SD-WAN deployments (Cisco SD-WAN/Viptela, VMware VeloCloud, Fortinet Secure SD-WAN), selecting a CPE with hardware IPSec offload ensures compatibility while maintaining performance.

    WireGuard: The newer, streamlined VPN protocol has gained rapid adoption in SD-WAN due to its minimal codebase, simplified key management, and excellent software performance even without hardware offload. WireGuard’s use of ChaCha20-Poly1305 encryption can achieve 1.5-3 Gbps on mid-range CPE processors without dedicated crypto hardware. Several next-generation SD-WAN platforms—including NetFoundry, ZeroTier, and the open-source FlexiWAN project—have adopted WireGuard as their primary overlay protocol. For greenfield 5G SD-WAN deployments, WireGuard’s operational simplicity and strong security posture make it an increasingly compelling choice.

    Hybrid WAN Overlay Architecture

    The most advanced 5G CPE SD-WAN deployments implement a hybrid overlay architecture that combines multiple VPN technologies and WAN interfaces into a unified, policy-driven forwarding plane. In this model:

    • Underlay abstraction: The CPE treats 5G NR, LTE, Ethernet, and satellite links as abstract WAN transports, each characterized by real-time metrics (bandwidth, latency, jitter, packet loss, signal quality).
    • Overlay mesh: IPSec and WireGuard tunnels are established over each viable WAN link to the enterprise SD-WAN hub or cloud gateway, creating a full-mesh or hub-spoke overlay topology.
    • Application-aware steering: The SD-WAN policy engine classifies traffic using deep packet inspection (DPI), application signatures, and DNS-based identification, then steers each flow to the optimal overlay tunnel based on application requirements and real-time link quality.
    • Intelligent failover: Sub-second link failure detection—leveraging BFD (Bidirectional Forwarding Detection), continuous tunnel health probes, and physical-layer signal monitoring—triggers seamless failover to alternate WAN paths without session interruption.

    Deployment Scenarios Driving Adoption in 2026

    Several enterprise verticals are driving accelerated adoption of SD-WAN-integrated 5G CPE:

    Retail and Quick-Service Restaurants (QSR): Thousands of distributed locations require reliable PCI-compliant connectivity for POS systems, inventory management, and guest Wi-Fi. 5G CPE with integrated SD-WAN provides primary or failover connectivity that deploys in hours rather than the weeks required for wired circuits.

    Financial Services Branch Banking: Bank branches demand always-on connectivity with strict SLA guarantees for real-time transaction processing. Dual-5G CPE with SD-WAN enables active-active WAN configurations with encrypted overlay tunnels to redundant data centers, ensuring zero-downtime connectivity for mission-critical banking applications.

    Healthcare Clinics and Telemedicine: Remote clinics and pop-up healthcare facilities leverage 5G CPE with SD-WAN for HIPAA-compliant connectivity, with application-aware policies that prioritize telemedicine video traffic over administrative workloads during clinical hours.

    Temporary and Pop-Up Sites: Construction sites, event venues, and disaster recovery operations use ruggedized 5G CPE with embedded SD-WAN for rapid-deployment connectivity that can be operational within minutes of power-on.

    Procurement Checklist for SD-WAN-Capable 5G CPE

    For enterprise IT and MSP procurement teams evaluating 5G CPE for SD-WAN integration, the following checklist provides a structured evaluation framework:

    • Hardware IPSec throughput rating at AES-256-GCM with 1400-byte IMIX packets
    • WireGuard performance with ChaCha20-Poly1305 at typical IMIX traffic profiles
    • Maximum concurrent VPN tunnel count and tunnel establishment rate
    • Certification status with target SD-WAN platform (vendor-specific interoperability testing)
    • Support for BFD and sub-second failover across 5G, LTE, and Ethernet WAN interfaces
    • DPI engine capability and application signature database update mechanism
    • Centralized management integration (SD-WAN orchestrator API or TR-369 USP telemetry)
    • Hardware root of trust and secure key storage (TPM 2.0 or equivalent)
    • Thermal design for sustained multi-gigabit encrypted throughput without throttling

    The convergence of 5G FWA and SD-WAN represents a strategic opportunity for enterprises to simplify branch networking architecture, accelerate site deployment, and improve WAN resilience—all while reducing the hardware footprint and operational complexity of traditional multi-box branch edge solutions. As 5G network coverage expands and CPE platforms continue to mature, integrated 5G CPE SD-WAN solutions will become the default branch connectivity architecture for distributed enterprises worldwide.

  • 5G CPE Network Slicing Gains Commercial Traction as Operators Launch Differentiated FWA Service Tiers for Enterprise Customers in H2 2026

    5G CPE Network Slicing Gains Commercial Traction as Operators Launch Differentiated FWA Service Tiers for Enterprise Customers in H2 2026

    As 5G Standalone (SA) core deployments reach critical mass across Tier-1 and Tier-2 operators globally, network slicing—one of the most transformative capabilities of the 5G SA architecture—is transitioning from proof-of-concept trials to commercial service differentiation. In H2 2026, a growing number of mobile network operators (MNOs) and fixed wireless access (FWA) providers are launching differentiated enterprise service tiers powered by end-to-end network slicing, with 5G CPE devices serving as the critical last-mile termination point for slice-aware connectivity.

    The Commercial Case for FWA Network Slicing

    Network slicing enables operators to partition a single physical 5G infrastructure into multiple virtualized, isolated logical networks—each optimized for specific performance characteristics, latency profiles, and service-level agreements (SLAs). For fixed wireless access, this translates directly into tiered enterprise connectivity products: a high-throughput eMBB (enhanced Mobile Broadband) slice for general corporate internet access, a low-latency URLLC (Ultra-Reliable Low-Latency Communications) slice for industrial automation and real-time control systems, and an mMTC (massive Machine-Type Communications) slice for IoT sensor networks and smart metering infrastructure.

    According to industry data from the GSMA and GSA, over 65 operators across 35 countries have now deployed or are actively trialing 5G SA networks capable of supporting network slicing, with Asia-Pacific and Western Europe leading commercial implementations. The global network slicing market is projected to exceed USD 8 billion by 2028, driven primarily by enterprise demand for guaranteed QoS and SLA-backed connectivity.

    5G CPE Requirements for Slice-Aware FWA

    For operators to deliver differentiated slicing services to enterprise customers, the customer premises equipment must evolve beyond basic 5G modem functionality. Slice-aware 5G CPE devices must support:

    • Multiple concurrent PDU sessions: The CPE must establish and maintain separate Protocol Data Unit (PDU) sessions corresponding to different network slices, enabling simultaneous connectivity across eMBB, URLLC, and mMTC slices from a single device.
    • URSP (UE Route Selection Policy) support: 3GPP-defined UE Route Selection Policy rules allow the CPE to intelligently route application traffic to the appropriate network slice based on traffic descriptors, application IDs, and connection capabilities.
    • VLAN-to-slice mapping: Enterprise-grade CPEs must map internal VLAN segments to specific network slices, enabling seamless integration with existing corporate LAN architectures while maintaining slice isolation.
    • Slice-level QoS enforcement: Hardware-accelerated QoS engines must apply differentiated queuing, scheduling, and rate-limiting policies per slice, ensuring SLA compliance for each service tier.

    Operator Deployment Patterns Emerging in H2 2026

    Several deployment patterns are crystallizing as operators move slicing into commercial service. In Japan, NTT DOCOMO and KDDI have launched enterprise FWA slicing services that guarantee minimum throughput for business-critical applications, with slice-aware CPE gateways deployed at SME and branch office locations. In Germany, Deutsche Telekom’s “Campus Network” slicing platform pairs private 5G infrastructure with public network slices for hybrid enterprise connectivity. In the Middle East, Etisalat and STC are leveraging slicing for differentiated oil-and-gas industry connectivity, where URLLC slices support remote drilling operations while eMBB slices serve administrative traffic.

    Vodafone Group has also announced a pan-European network slicing framework for its enterprise FWA portfolio, targeting multi-site retail, banking, and manufacturing customers who require consistent QoS across geographically distributed locations. The operator is standardizing on slice-aware CPE specifications that include dual-SIM redundancy, integrated SD-WAN capabilities, and cloud-based slice orchestration.

    Procurement Implications for B2B Buyers

    For telecom operators, MVNOs, and enterprise procurement teams sourcing 5G CPE at scale, network slicing capability is rapidly becoming a key differentiator in vendor selection. CPE devices that support 3GPP Release 17 and 18 slicing features—including multiple PDU sessions, URSP, and network slice selection assistance (NSSAI) handling—provide future-proof investment protection as operators expand their slicing service portfolios.

    Key evaluation criteria for slice-capable CPE procurement in H2 2026 include: chipset platform generation (Qualcomm X75/X80, MediaTek T800/T830 series with Release 17/18 slicing support), maximum concurrent PDU session count, VLAN-to-slice mapping granularity, integration with operator OSS/BSS orchestration platforms, and certification status with target operator slicing frameworks. Buyers should also assess the CPE vendor’s roadmap for 3GPP Release 18 enhanced slicing features—including network slice admission control (NSAC) and slice-based authentication—expected to reach commercial maturity in 2027.

    As enterprise customers increasingly demand guaranteed, SLA-backed connectivity rather than best-effort broadband, network-slicing-capable 5G CPE represents a strategic differentiator that enables operators to move up the value chain from connectivity providers to managed service partners.

    Looking Ahead: Automated Slice Orchestration

    The next frontier for FWA network slicing lies in AI-driven automated orchestration. Emerging standards from the O-RAN Alliance, TM Forum, and 3GPP SA5 working group are defining intent-based slice management interfaces that will allow enterprise customers to dynamically request, modify, and release network slices through self-service portals—with 5G CPE devices automatically reconfiguring to match slice parameters. As these standards mature through 2027, the combination of intelligent slice orchestration and slice-aware CPE will unlock new enterprise FWA revenue models, including bandwidth-on-demand, temporary event connectivity, and disaster-recovery-as-a-service.

    For Honlly Telecom and its global B2B partners, the network slicing trend underscores the importance of developing and certifying slice-capable 5G CPE products that align with the specifications of major operator slicing platforms—ensuring that carrier and enterprise customers can fully leverage the differentiated connectivity that 5G SA network slicing enables.

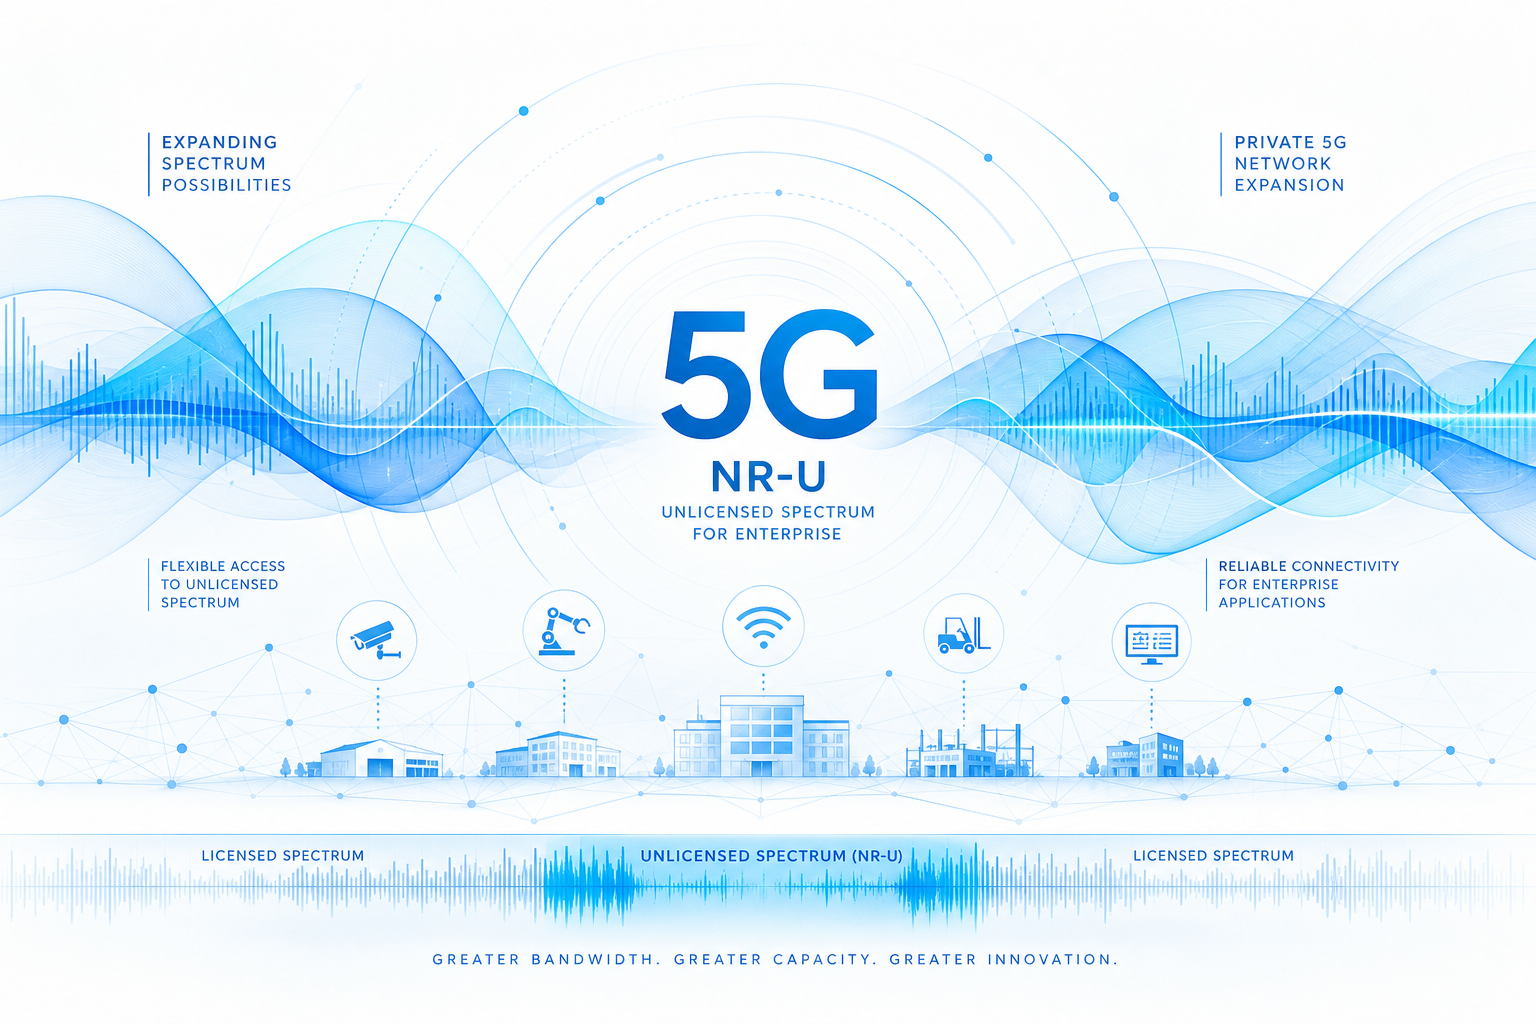
  • 5G NR-U and Unlicensed Spectrum CPE: Expanding Private Network Capacity Through License-Assisted Access and Standalone Unlicensed Operation

    5G NR-U and Unlicensed Spectrum CPE: Expanding Private Network Capacity Through License-Assisted Access and Standalone Unlicensed Operation

    Spectrum remains the single most constrained resource in wireless networking. While licensed spectrum offers guaranteed quality of service, its limited availability — especially for private network operators — has long been a bottleneck for enterprise 5G adoption. 5G NR-U (New Radio Unlicensed) changes this equation by extending 5G operation into globally available unlicensed bands, dramatically expanding the capacity envelope for private and enterprise 5G deployments.

    Understanding NR-U: Two Operational Modes

    3GPP Release 16 introduced NR-U with two distinct operational modes, each serving different deployment scenarios: License-Assisted Access (LAA): In this mode, a licensed 5G anchor carrier provides the control plane and guaranteed capacity, while NR-U carriers operating in the 5 GHz unlicensed band supplement downlink and uplink throughput. The anchor carrier handles mobility, authentication, and QoS enforcement; NR-U carriers provide pure capacity augmentation. This is the most common initial NR-U deployment model and is supported by major infrastructure vendors including Ericsson, Nokia, and Samsung. Standalone NR-U (SA NR-U): The more radical architecture — NR-U operates entirely in unlicensed spectrum without any licensed anchor. SA NR-U is particularly attractive for private network operators who may not hold licensed spectrum at all. It enables fully independent 5G deployments in the 5 GHz and emerging 6 GHz bands, subject to regional regulatory frameworks.

    Why NR-U Matters for Enterprise and Private 5G

    The business case for NR-U in private 5G CPE deployments rests on three pillars: Spectrum cost elimination: Licensed spectrum — whether acquired at auction, leased from MNOs, or obtained through local regulatory processes (such as Germany’s 3.7-3.8 GHz local licenses) — represents a significant recurring cost. NR-U sidesteps this entirely by operating in license-exempt bands, dramatically lowering the total cost of ownership for private network operators. Capacity multiplication: A private 5G network operating in 100 MHz of licensed n78 spectrum can add up to 500 MHz of NR-U capacity in the 5 GHz band alone (where available), plus additional bandwidth as regulators open the 6 GHz band (5925-7125 MHz) for license-exempt use. For bandwidth-hungry industrial applications — automated optical inspection, 4K/8K video surveillance, AR-assisted maintenance — this capacity headroom is transformative. Global harmonization: Unlike licensed spectrum, which varies dramatically by country, the 5 GHz band is globally available. NR-U CPE can be deployed in nearly any market without waiting for local spectrum licensing — a critical advantage for multinational enterprises standardizing on a single private network architecture.

    Coexistence Mechanisms: Fair Sharing with Wi-Fi

    A persistent concern around NR-U is coexistence with incumbent Wi-Fi networks sharing the same unlicensed bands. The 3GPP addressed this directly with sophisticated channel access mechanisms designed to ensure fair spectrum sharing: LBT (Listen Before Talk): NR-U devices must sense the channel and confirm it is clear before transmitting — the same fundamental mechanism used by Wi-Fi. 3GPP adopted LBT parameters (Category 4 LBT with exponential backoff) that are functionally equivalent to Wi-Fi’s CSMA/CA, ensuring neither technology dominates the channel unfairly. CO sharing and MCOT: NR-U supports Channel Occupancy Time sharing, where a base station acquires the channel and can share it with connected CPE devices within the same Maximum Channel Occupancy Time. This improves scheduling efficiency without disadvantaging neighboring Wi-Fi networks. Wideband operation and BWP adaptation: NR-U CPE can operate across wide bandwidths (up to 100 MHz carriers) while dynamically adapting Bandwidth Part (BWP) configurations to avoid congested sub-channels — effectively steering around heavy Wi-Fi traffic in real time.

    CPE Design Considerations for NR-U

    Building effective NR-U CPE requires addressing several engineering challenges beyond standard 5G CPE design: Dual-band RF front-end: NR-U CPE must support simultaneous operation in licensed bands (n77/n78/n79) and unlicensed bands (n46 at 5 GHz, and emerging n96/n102 at 6 GHz). This requires dual-concurrent RF chains with high isolation to prevent self-interference, plus advanced filtering to reject adjacent Wi-Fi signals. Dynamic spectrum sharing intelligence: The CPE software stack must make real-time decisions about which spectrum resources to use — licensed, unlicensed, or both — based on traffic QoS requirements, channel occupancy measurements, and operator policy. This demands a sophisticated spectrum management layer integrated with the 5G protocol stack. Regulatory agility: Unlicensed spectrum regulations vary by region (FCC Part 15 in the US, ETSI EN 301 893 in Europe, MIC ordinances in Japan). NR-U CPE must support regional regulatory profiles that can be activated via configuration rather than requiring hardware variants.

    Deployment Scenarios Gaining Traction

    Several real-world NR-U deployment patterns are emerging: Smart manufacturing campuses: Automotive and electronics manufacturers are combining licensed private 5G (for AGV control, safety systems) with NR-U capacity (for video inspection, environmental monitoring). The licensed anchor ensures deterministic latency for critical control loops; NR-U provides scalable bandwidth for data-intensive applications. Higher education and research campuses: Universities deploying private 5G for research and smart campus applications are leveraging NR-U to extend coverage into buildings and outdoor spaces where running additional licensed small cells would be cost-prohibitive. Port and logistics hubs: Container terminals, airports, and distribution centers — environments where spectrum licensing is often complex due to cross-jurisdictional coverage — are deploying NR-U CPE for asset tracking, autonomous vehicle connectivity, and real-time inventory systems without spectrum acquisition delays.

    Strategic Implications for B2B Buyers

    For enterprises and system integrators planning private 5G deployments, NR-U capability should be a core CPE evaluation criterion. The technology effectively future-proofs the network investment: as regulators continue to release unlicensed spectrum (the 6 GHz band alone represents up to 1200 MHz of new capacity), NR-U-capable CPE can absorb this capacity without hardware replacement. Vendors like Honlly Telecom are already shipping 5G CPE platforms with NR-U-ready RF architectures, preparing for the moment when regulators in key markets — particularly Southeast Asia, the Middle East, and Latin America — finalize their 6 GHz unlicensed frameworks. For B2B buyers, selecting NR-U-capable CPE today ensures that tomorrow’s spectrum bounty translates directly into network capacity, not hardware obsolescence.
  • Multi-WAN 5G CPE Architectures for Enterprise Business Continuity: SD-WAN Integration, Intelligent Link Aggregation, and Carrier-Grade Failover Design

    Multi-WAN 5G CPE Architectures for Enterprise Business Continuity: SD-WAN Integration, Intelligent Link Aggregation, and Carrier-Grade Failover Design

    Enterprise network architects face a deceptively simple requirement: the connection must never go down. A retail chain processing thousands of POS transactions per minute, a logistics hub coordinating real-time fleet telemetry, a financial services branch handling regulatory reporting — in each case, connectivity downtime translates directly to revenue loss, SLA violations, and operational disruption. Multi-WAN 5G CPE has emerged as the architectural answer to this requirement, combining cellular WAN diversity with intelligent traffic steering to deliver carrier-grade resilience at enterprise price points.

    Beyond Simple Failover: The Multi-WAN Value Proposition

    First-generation 4G backup solutions treated cellular as a secondary, best-effort path — activated only when the primary wired link failed, often with 30 to 90 seconds of cutover delay. Modern multi-WAN 5G CPE architectures fundamentally rethink this model. Today’s enterprise-grade platforms support simultaneous active-active operation across two or more WAN interfaces — typically combining 5G cellular, fixed-line broadband, and dedicated fiber — with intelligent traffic distribution based on application type, link quality, and business policy. This moves cellular from backup to peer, unlocking: Bandwidth aggregation: Multiple WAN links contribute to total available throughput. A branch office with 500 Mbps fiber and dual 5G links at 300 Mbps each can present approximately 1.1 Gbps of usable capacity to the LAN side. Sub-second failover: BFD (Bidirectional Forwarding Detection) and link-quality probes running at 100ms intervals detect path degradation before connections drop, enabling hitless failover that preserves VoIP calls, video conferences, and TCP sessions. Application-aware steering: Latency-sensitive traffic (voice, video, real-time trading) routes over the lowest-jitter path. Bulk data (cloud backups, software updates) uses the cheapest available link. Business-critical SaaS applications receive dedicated bandwidth guarantees.

    SD-WAN Integration: The Intelligence Layer

    The true power of multi-WAN 5G CPE is unlocked when integrated with SD-WAN overlay platforms. Leading SD-WAN vendors — including VMware (Broadcom), Fortinet, Cisco, and Aruba — now support 5G CPE as first-class WAN transport endpoints. Key integration patterns include: Tunnel bonding and per-packet steering: SD-WAN edge software creates encrypted overlay tunnels over each physical WAN link. The tunnel bonding function stripes packets across available paths at millisecond granularity, compensating for individual link jitter and loss. If a 5G link experiences a transient 2% packet loss spike, the SD-WAN controller shifts affected flows to the fiber path within 200ms — transparent to the application layer. Zero-touch provisioning over cellular: Branch CPE can be drop-shipped directly to the deployment site. On first power-up, the device establishes a 5G connection, authenticates with the SD-WAN orchestrator, downloads its configuration, and joins the overlay fabric — all without on-site IT staff. This collapses traditional branch deployment timelines from weeks to hours. Cloud on-ramp optimization: With enterprises accelerating SaaS and IaaS adoption, SD-WAN-integrated 5G CPE can route cloud-destined traffic directly to the nearest cloud exchange point (AWS Direct Connect, Azure ExpressRoute, Google Cloud Interconnect) rather than backhauling through a central data center — dramatically reducing cloud application latency.

    Carrier Diversity: The Hidden Resilience Dimension

    A critical but often overlooked aspect of multi-WAN design is carrier diversity. Dual SIM slots supporting different MNOs (Mobile Network Operators) ensure that a single carrier outage does not disable the cellular backup path. Advanced 5G CPE platforms now support: Dual-SIM Dual-Active (DSDA): Both SIMs maintain simultaneous RRC-connected states, enabling true active-active cellular operation. If MNO A experiences a local RAN failure, traffic shifts to MNO B without the 5-15 second re-attach delay typical of Dual-SIM Single-Standby (DSSS) architectures. Cross-RAT fallback: When 5G NR coverage is unavailable, the CPE automatically falls back to LTE-A or even 3G while maintaining the SD-WAN overlay — ensuring basic business continuity even in coverage-edge scenarios common in rural and industrial deployments. Geographic path diversity: In fixed wireless access configurations, external antenna placement can connect to different cell towers for each 5G modem, providing physical path diversity that protects against tower-level failures or localized interference.

    Procurement Considerations for Enterprise Buyers

    When evaluating multi-WAN 5G CPE for enterprise deployment, IT procurement teams should prioritize: SD-WAN ecosystem certification: Verify that the CPE platform is certified by your chosen SD-WAN vendor. Certification ensures validated interoperability, supported configuration templates, and access to vendor TAC (Technical Assistance Center) for joint troubleshooting. Throughput headroom: Multi-WAN aggregation imposes CPU and forwarding-engine overhead. Select platforms with rated throughput at least 30% above aggregate WAN capacity to maintain line-rate performance during failover events and traffic bursts. Management plane integration: The CPE should expose a well-documented RESTCONF/NETCONF or gNMI interface for SD-WAN orchestrator integration. Avoid platforms that require proprietary management consoles that cannot be automated at scale. Thermal and environmental ratings: Active-active dual-5G operation generates significantly more heat than single-radio designs. For industrial or outdoor deployments, verify extended temperature range (-20°C to +60°C) and passive cooling capability.

    The Road Ahead: AI-Driven Predictive Path Selection

    The next evolution in multi-WAN 5G CPE is already visible in early deployments. Machine learning models trained on per-link telemetry data (signal quality, latency, jitter, throughput history, time-of-day patterns) can predict link degradation 30-60 seconds before it impacts applications — and proactively shift traffic before users notice. Combined with 5G-Advanced features like network slicing and URLLC, these intelligent multi-WAN platforms will form the connectivity backbone for the next generation of distributed enterprise applications — from autonomous warehouse robotics to real-time augmented reality field service. For enterprise buyers building infrastructure that must last 5-7 years, multi-WAN 5G CPE with SD-WAN integration is not an optional upgrade; it is the architectural minimum.
  • Global 5G CPE eSIM and iSIM Integration Accelerates as B2B Operators Streamline Cross-Border Deployment Logistics

    Global 5G CPE eSIM and iSIM Integration Accelerates as B2B Operators Streamline Cross-Border Deployment Logistics

    The global telecom equipment supply chain is undergoing a quiet but profound transformation. At the center of this shift is the transition from traditional physical SIM cards to embedded SIM (eSIM) and integrated SIM (iSIM) technologies in 5G Customer Premises Equipment (CPE) — and the implications for B2B operators, OEMs, and enterprise buyers are far-reaching.

    The Logistics Problem Physical SIMs Created

    For decades, deploying CPE across multiple countries meant managing a fragmented SIM logistics chain. Operators had to forecast demand by region, procure carrier-specific SIM cards, physically insert them during manufacturing or at regional warehouses, and handle re-keying for carrier changes. Each step added cost, delay, and operational friction. Consider a typical multi-country FWA rollout: a European operator expanding into five new markets would need five separate SIM SKUs, five inventory pools, and five provisioning workflows. A last-minute carrier partnership change could render thousands of pre-provisioned devices obsolete, requiring costly rework.

    eSIM: Remote Provisioning Redefines Go-to-Market Speed

    The GSMA-compliant eSIM (eUICC) architecture changes this equation fundamentally. With eSIM-capable 5G CPE, the carrier profile is loaded remotely via RSP (Remote SIM Provisioning) after the device has already left the factory and arrived in the target market. This decoupling of hardware manufacturing from carrier provisioning delivers three immediate B2B advantages: Unified SKU strategy: A single CPE hardware variant can serve dozens of markets. Regional customization happens entirely in software, not on the assembly line. Last-mile flexibility: Operators and enterprises can switch carrier profiles over-the-air without dispatching technicians or replacing devices. A CPE deployed for Carrier A today can be reprovisioned for Carrier B tomorrow — critical for managed service providers and multinational enterprises. Accelerated time-to-market: Regional launches that previously required 8–12 weeks of SIM logistics lead time can now be completed in days. eSIM eliminates the longest pole in the deployment timeline.

    iSIM: The Next Frontier in CPE Miniaturization and Security

    While eSIM embeds a discrete eUICC chip on the device PCB, iSIM (integrated SIM) goes further by integrating SIM functionality directly into the device’s system-on-chip (SoC) or cellular module. Qualcomm’s Snapdragon X-series modems and Sony’s Altair platform already support iSIM architectures. For 5G CPE, iSIM offers three compelling benefits: Hardware consolidation: Eliminating the discrete SIM chip reduces BOM cost, PCB real estate, and power consumption — factors that matter enormously in compact industrial CPE and battery-optimized mobile hotspot designs. Enhanced physical security: iSIM credentials reside in a tamper-resistant enclave within the SoC, making physical SIM-swapping attacks nearly impossible. For enterprise and government deployments requiring hardware-grade security, this is a decisive advantage. Scalable IoT integration: As 5G CPE increasingly serves as an IoT aggregation gateway (connecting sensors, cameras, and industrial controllers), iSIM simplifies identity management for the entire device ecosystem behind the gateway.

    Real-World Deployment Momentum

    Several major operators have already begun eSIM-first procurement mandates for 5G FWA CPE. Deutsche Telekom’s latest FWA tender specifies eSIM as a baseline requirement. In North America, T-Mobile and Verizon are expanding eSIM provisioning infrastructure to support fixed wireless at scale. Meanwhile, Japan’s Rakuten Mobile has demonstrated fully virtualized iSIM provisioning integrated with its cloud-native 5G core. On the manufacturing side, leading CPE ODMs — including Honlly Telecom — now offer eSIM and iSIM-ready platforms across their 5G product lines. These platforms support GSMA SGP.02 (M2M) and SGP.22 (Consumer) provisioning architectures, giving B2B buyers the flexibility to choose the provisioning model that fits their operational framework.

    What B2B Buyers Should Evaluate

    For procurement teams evaluating eSIM/iSIM-capable 5G CPE, the following criteria are essential: GSMA compliance level: Verify SGP.02 and/or SGP.22 certification for the target provisioning architecture. Full compliance ensures interoperability with major SM-DP+ (Subscription Manager Data Preparation) platforms including IDEMIA, G+D, and Thales. Carrier certification coverage: eSIM capability alone does not guarantee carrier certification. Ensure the CPE vendor has completed GCF/PTCRB certification and carrier-specific interoperability testing for target deployment markets. Profile management tooling: Evaluate whether the vendor provides or integrates with an SM-DP+ platform that offers bulk provisioning APIs, profile lifecycle management, and over-the-air profile switching capabilities. Fallback mechanisms: In markets where eSIM infrastructure is still maturing, hybrid SIM slots (eSIM + physical SIM tray) provide a practical bridge, allowing operators to transition at their own pace.

    The Strategic Outlook

    The eSIM/iSIM transition in 5G CPE mirrors the broader telecom industry’s move toward software-defined, cloud-managed infrastructure. By decoupling hardware from carrier identity, operators gain unprecedented deployment agility while reducing supply chain complexity. For B2B buyers sourcing 5G CPE at scale, eSIM/iSIM readiness is no longer a future consideration — it is rapidly becoming a baseline procurement requirement that separates forward-looking vendors from legacy suppliers. As global 5G FWA deployments continue their rapid expansion, the ability to provision, reprovision, and manage CPE identity remotely will increasingly determine which operators capture market share fastest — and which CPE vendors earn their long-term business.