Author: openclaw-Lisa-New

  • 5G FWA CPE vs Fiber: A Comprehensive TCO Analysis for Operators Deploying Last-Mile Broadband in 2026

    5G FWA CPE vs Fiber: A Comprehensive TCO Analysis for Operators Deploying Last-Mile Broadband in 2026

    For telecom operators and ISPs planning greenfield broadband deployments, the perennial question has shifted from “fiber or wireless?” to “fiber and wireless — but in what mix?” As 5G FWA matures into a carrier-grade last-mile technology capable of delivering 500 Mbps to 1 Gbps with sub-20ms latency, the total cost of ownership (TCO) comparison against fiber-to-the-home (FTTH) demands rigorous reexamination. This analysis provides B2B buyers with a comprehensive TCO framework for 2026 deployment planning.

    The TCO Equation: Breaking Down Cost Components

    A meaningful TCO comparison between 5G FWA CPE and FTTH must account for the full deployment lifecycle — from civil engineering to ongoing operations — over a standard 5-year and 10-year horizon. The components differ fundamentally:

    FTTH Cost Structure

    • Civil Works (40-55% of TCO): Trenching, duct laying, pole attachments, and right-of-way permits dominate fiber economics. Urban trenching costs range from $80-250 per meter in developed markets; rural builds can exceed $300/meter due to longer distances and challenging terrain.
    • Active Equipment (15-20%): OLTs, ONTs/ONUs, optical splitters, and aggregation switches represent a moderate but non-trivial cost. GPON ONT units average $45-80; XGS-PON ONTs range $90-150.
    • Operations (20-25%): Fiber maintenance, fault localization (OTDR truck rolls), and physical repair account for significant ongoing costs, particularly in areas with construction activity or severe weather.
    • Customer Acquisition (8-12%): On-site installation with skilled technicians, typically 2-4 hours per premises.

    5G FWA CPE Cost Structure

    • CPE Hardware (30-40% of TCO): The CPE unit itself is the single largest cost center. Indoor 5G FWA CPE ranges $150-350; outdoor CPE with high-gain antennas ranges $250-600. However, per-unit costs continue declining at approximately 12-15% annually as chipset volumes scale.
    • Spectrum (15-20%): Unlike fiber, 5G FWA requires licensed spectrum — either acquired at auction or through leasing arrangements. Mid-band spectrum (3.5 GHz) provides the optimal balance of coverage and capacity for FWA applications.
    • Network Infrastructure (15-20%): gNodeB deployment costs are significantly lower than FTTH civil works. A single macro cell site ($40,000-80,000) can serve 500-2,000 premises depending on density and spectrum bandwidth.
    • Customer Installation (5-10%): Self-install indoor CPE eliminates truck rolls. Even outdoor CPE installations average under 1 hour — versus 2-4 hours for fiber ONT installation.
    • Operations (8-12%): Remote management via TR-369 USP dramatically reduces operational costs versus physical fiber maintenance.

    5-Year TCO Comparison Per Premises

    Cost CategoryFTTH (Urban)FTTH (Rural)5G FWA (Urban)5G FWA (Rural)
    Civil/Deployment$450-900$1,200-2,500$80-180$200-500
    Active Equipment$120-200$150-250$220-450$300-600
    Installation$120-200$200-350$0-80$50-150
    5-Year Operations$200-350$350-550$80-150$120-200
    Total 5-Year TCO$890-1,650$1,900-3,650$380-860$670-1,450

    Note: All figures in USD per premises. 5G FWA costs amortize the gNodeB capital expenditure across the served subscriber base. Spectrum costs excluded from per-premises calculation as they are typically incurred at the network level.

    Where 5G FWA Wins on TCO

    Low-Density and Rural Deployments: In areas with fewer than 50 premises per square kilometer, 5G FWA delivers 40-65% TCO savings over FTTH. The fixed cost of fiber trenching becomes prohibitive when premises are widely dispersed; a single 5G macro site can cover 5-15 km radius — equivalent to laying hundreds of kilometers of fiber.

    Rapid Time-to-Market: A 5G FWA cell site can be deployed and serving customers within 4-8 weeks, versus 12-36 months for a typical FTTH build-out. For operators facing competitive pressure or government broadband mandates with tight deadlines, the speed advantage translates directly to earlier revenue realization and lower working capital requirements.

    MDUs and Difficult Premises: Multi-dwelling units with legacy internal wiring, historic buildings with trenching restrictions, and premises separated by waterways or highways create disproportionate costs for FTTH. 5G FWA sidesteps these physical barriers entirely — a single outdoor CPE on a balcony or exterior wall can serve the entire premises.

    Where Fiber Retains the Advantage

    Ultra-High-Density Urban: In dense urban corridors (>500 premises/km²), fiber’s per-premises civil cost drops below $300, making the 10-year TCO competitive or superior to 5G FWA. Additionally, fiber’s virtually unlimited capacity (10G XGS-PON today, 25G/50G-PON on the horizon) future-proofs the investment.

    SLA-Dependent Enterprise: Enterprises requiring guaranteed symmetrical throughput, sub-millisecond jitter, or 99.999% uptime continue to prefer dedicated fiber. While 5G FWA with network slicing can approach these metrics, fiber’s deterministic physical layer provides an inherent advantage for the most demanding applications like high-frequency trading or real-time industrial control.

    Spectrum-Constrained Markets: In countries where mid-band spectrum is scarce or prohibitively expensive, the spectrum cost component can erode 5G FWA’s TCO advantage. Operators in these markets may find FTTH more economically predictable over 10+ year horizons.

    Strategic Recommendation for Operators

    The data supports a hybrid deployment strategy: use 5G FWA as the primary access technology for suburban, rural, and difficult-to-serve premises while continuing FTTH build-out in high-density urban corridors where fiber economics remain compelling. This approach optimizes both capital efficiency and coverage velocity.

    For operators evaluating this strategy, the critical procurement decision is CPE selection. Look for outdoor 5G FWA CPE with high-gain beamforming antennas (8-12 dBi), 4×4 MIMO on n77/n78 bands, carrier aggregation (n78+n78 or n78+n79), and TR-369 USP remote management. These specifications directly determine the viable coverage radius and, consequently, the number of premises served per cell site — the single largest lever on per-subscriber TCO.

    As 5G-Advanced (3GPP Release 18) features like enhanced MIMO, AI-native beam management, and integrated sensing enter the commercial mainstream through 2027, the TCO gap between FWA and FTTH will widen further — particularly in the suburban and exurban segments that represent the largest addressable market for broadband expansion.
  • Zero Trust Security Architecture for 5G FWA CPE: Implementing SASE, Micro-Segmentation, and Hardware-Rooted Encryption for Enterprise Branch Networks in 2026

    Zero Trust Security Architecture for 5G FWA CPE: Implementing SASE, Micro-Segmentation, and Hardware-Rooted Encryption for Enterprise Branch Networks in 2026

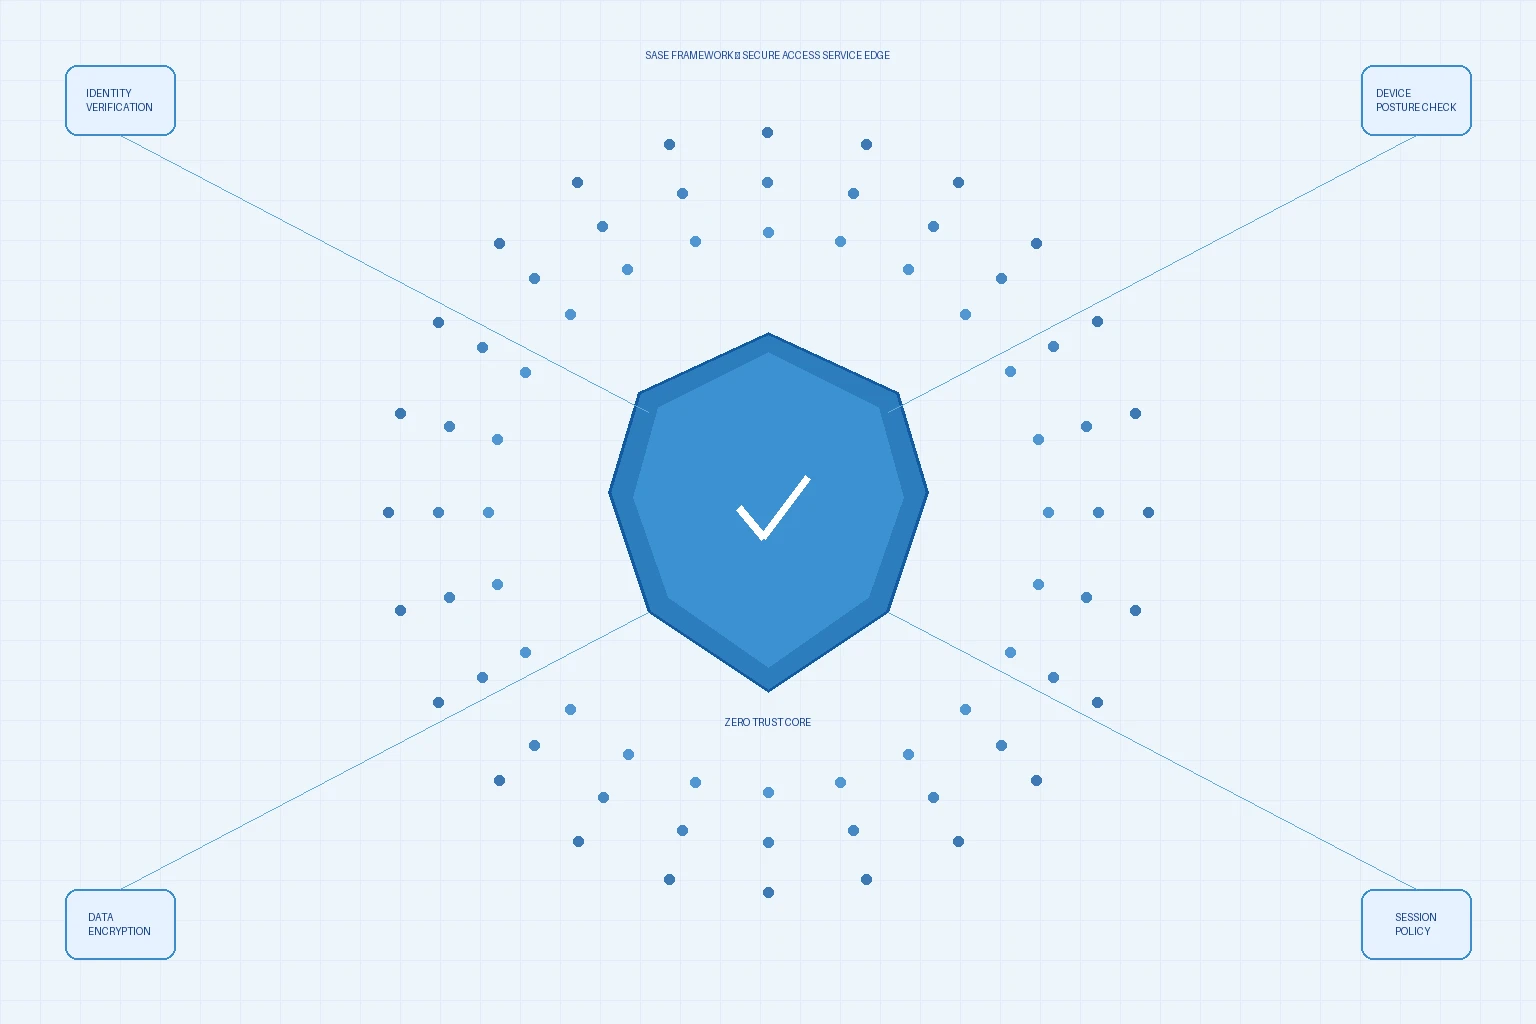
    As enterprise branch networks increasingly rely on 5G Fixed Wireless Access (FWA) as primary WAN connectivity, the traditional perimeter-based security model has become obsolete. In 2026, forward-thinking ISPs, MSPs, and enterprise IT buyers are adopting Zero Trust Architecture (ZTA) integrated directly into 5G CPE platforms, eliminating the security gap between the WAN edge and the LAN fabric.

    This technical guide examines how SASE (Secure Access Service Edge), micro-segmentation, and hardware-rooted encryption are being embedded into carrier-grade 5G CPE — and what B2B procurement teams should validate when specifying secure FWA gateways.

    Why Perimeter Security Fails for 5G Branch Networks

    Traditional branch security architectures place a firewall/VPN appliance behind the CPE, creating a trusted LAN zone behind the WAN demarcation point. This model has critical weaknesses in 5G FWA deployments:

    • Split-tunnel vulnerabilities — Direct internet breakout from the CPE for cloud/SaaS traffic bypasses the branch firewall entirely
    • Lateral movement risk — Once an attacker compromises a single LAN device, the flat branch network offers no internal barriers
    • IoT device exposure — Branch IoT endpoints (printers, cameras, sensors) lack endpoint security agents and become entry vectors
    • CPE-as-attack-surface — The CPE itself runs a Linux/OpenWrt-based OS with an attack surface that perimeter models ignore
    • Multi-tenant isolation gaps — In multi-dwelling units (MDUs) or shared office spaces, VLAN isolation alone is insufficient

    Zero Trust Principles Applied to 5G CPE

    A Zero Trust 5G CPE implements the core ZTA principles at the network edge:

    1. Never Trust, Always Verify — At the CPE Level

    Every packet entering the CPE — whether from the WAN (5G interface) or LAN (Ethernet/Wi-Fi clients) — undergoes identity-based policy enforcement. The CPE maintains a dynamic policy decision point (PDP) that evaluates every flow against real-time attributes: user identity (802.1X/RADIUS), device posture (MAC address + certificate fingerprint), application signature (DPI/L7 classification), and time-of-day policy. Flows that fail any check are dropped before they traverse the CPE.

    2. Micro-Segmentation Within the CPE

    Rather than bridging all LAN ports and Wi-Fi SSIDs into a single broadcast domain, a Zero Trust CPE implements per-port and per-SSID policy zones. Each zone has its own security policy, routing table, and firewall ruleset — enforced in hardware by the CPE’s embedded switch ASIC or NPU (Network Processing Unit). This means:

    • A compromised IoT camera on LAN port 3 cannot reach the POS terminal on LAN port 1
    • The guest Wi-Fi SSID is fully isolated from the corporate SSID, even at Layer 2
    • Branch employee laptops can only communicate with specific cloud applications, not with each other

    3. SASE Integration: CPE as the SD-WAN + SSE Convergence Point

    The CPE serves as the physical enforcement point for SASE policies. It establishes encrypted tunnels (IPsec, WireGuard, or GRE) to the SASE provider’s Points of Presence (PoPs) while simultaneously applying SSE (Security Service Edge) functions locally:

    • SWG (Secure Web Gateway) — Local URL filtering and content inspection cache, with full inspection offloaded to cloud SWG for unknown URLs
    • CASB (Cloud Access Security Broker) — API-based shadow IT discovery with inline policy enforcement for sanctioned SaaS applications
    • ZTNA (Zero Trust Network Access) — Per-application tunnels with continuous session validation, replacing always-on VPN connections
    • FWaaS (Firewall-as-a-Service) — L7 application-aware firewalling with threat intelligence feed integration (STIX/TAXII)

    Hardware Security: Root of Trust and Secure Boot

    Software-based security is only as strong as the hardware it runs on. Enterprise-grade Zero Trust CPE must implement a hardware root of trust (HRoT) chain:

    Security LayerImplementationPurpose
    Secure BootU-Boot/ARM Trusted Firmware with fused root key (eFuse/OTP)Verify bootloader and kernel integrity before execution
    TPM 2.0Discrete or firmware TPM (Infineon OPTIGA, STSAFE)Secure key storage, measured boot, remote attestation
    Hardware Crypto EngineDedicated crypto accelerator (ARM CryptoCell, CE engine)Line-rate IPsec/TLS encryption without CPU bottleneck
    Secure EnclaveARM TrustZone / Qualcomm TEE execution environmentIsolated execution of security-critical functions
    Physical Tamper DetectionPCB-level tamper switches + chassis intrusion sensorsDetect and respond to physical access attempts

    Procurement Checklist: 12 Questions for Zero Trust CPE Vendors

    When evaluating 5G CPE for Zero Trust branch deployments, B2B buyers should verify:

    1. Does the CPE support TLS 1.3 with mutual authentication for all management interfaces (TR-069/TR-369, Web UI, SSH)?
    2. Is secure boot with hardware-fused root key implemented and verifiable via attestation report?
    3. Can the CPE enforce per-port and per-SSID micro-segmentation in hardware, not software bridging?
    4. Does it support multiple simultaneous IPsec/WireGuard tunnels to different SASE PoPs with per-tunnel QoS?
    5. Is there a TPM 2.0 module for key storage and measured boot with remote attestation (PCR quoting)?
    6. Does the CPE support 802.1X supplicant and authenticator roles simultaneously?
    7. Can it integrate with major SASE platforms via API (Zscaler, Netskope, Palo Alto Prisma, Cato Networks)?
    8. Is FIPS 140-3 or Common Criteria EAL4+ certification available for the cryptographic module?
    9. Does the firmware update mechanism (FOTA) require signed delta packages with rollback protection?
    10. Can the CPE run a local DNS firewall with RPZ (Response Policy Zones) and DoH/DoT support?
    11. Is there hardware-accelerated DPI for L7 application identification without impacting throughput?
    12. Does the vendor provide SBOM (Software Bill of Materials) and vulnerability disclosure program?

    Honlly’s Zero Trust CPE Architecture

    Honlly Telecom’s 5G CPE platforms incorporate defense-in-depth security designed for enterprise Zero Trust deployments:

    • Qualcomm X75/X80 with integrated Secure Processing Unit (SPU) — Hardware-isolated TEE for key management, cryptographic operations, and secure boot verification
    • Infineon OPTIGA TPM 2.0 — Discrete TPM with ECC P-256/P-384 support for device identity, remote attestation, and sealed key storage
    • OpenWrt-based OS with kernel hardening — SELinux enforcing mode, KASLR, stack canaries, read-only rootfs overlay, and signed immutable firmware updates
    • Multi-tunnel SASE integration — Pre-validated with Zscaler, Palo Alto Prisma Access, and Cato Networks via IPsec and GRE with BGP dynamic routing
    • Hardware micro-segmentation — Integrated L2/L3 switch with per-port ACLs, private VLANs, and port isolation enforced in silicon
    • Zero-touch provisioning with SZTP (RFC 8572) — Secure bootstrap with IDevID certificate for automated onboarding without manual configuration

    Frequently Asked Questions

    Q: Can a Zero Trust CPE replace my branch firewall entirely?
    A: For many branch deployments, yes. A fully-featured Zero Trust CPE with integrated NGFW, SWG, and ZTNA capabilities can serve as the single branch security appliance. However, large branches with complex security requirements (DLP, sandboxing, full TLS decryption) may still benefit from a dedicated next-gen firewall alongside the CPE. The CPE serves as the policy enforcement point closest to the WAN, with the option to offload intensive inspection to cloud SSE.

    Q: What’s the throughput impact of enabling Zero Trust features?
    A: This is the critical question. Software-based security features can reduce throughput by 50-70%. Honlly’s CPE uses the Qualcomm NPU (Network Processing Unit) for hardware-accelerated IPsec, L4 stateful firewall, and DPI — maintaining line-rate throughput (2.5 Gbps+) even with all security features enabled. Always ask for throughput figures with security features turned on, not just baseline routing throughput.

    Q: How do I manage Zero Trust policies across hundreds of CPEs?
    A: Policy management should be centralized via ACS (TR-369 USP or TR-069) with integration to your SASE management console. Honlly’s CPE supports bulk policy push via the ACS northbound REST API, with per-device policy overrides for exception cases. SASE policies are pulled from the cloud SSE platform, ensuring consistent policy across the entire fleet.

    Evaluate Honlly’s Zero Trust 5G CPE for your enterprise FWA deployment. Request a security architecture review and CPE evaluation kit with pre-configured ZTNA, SASE integration, and hardware security documentation.

  • 5G Outdoor CPE Thermal Engineering: Advanced Heat Dissipation Design, IP68 Enclosure Cooling, and Environmental Hardening for Carrier-Grade Deployments

    5G Outdoor CPE Thermal Engineering: Advanced Heat Dissipation Design, IP68 Enclosure Cooling, and Environmental Hardening for Carrier-Grade Deployments

    Outdoor 5G CPE deployments in extreme environments — desert solar farms, tropical telecom towers, arctic mining operations, and dense urban rooftops — face a fundamental engineering challenge: managing heat dissipation while maintaining IP68 environmental sealing. Poor thermal design is the leading cause of premature CPE failure in carrier-grade outdoor deployments, directly impacting SLA compliance, truck-roll costs, and total cost of ownership.

    This technical guide examines the thermal engineering principles, materials science, and design methodologies that distinguish carrier-grade outdoor CPE from consumer-grade devices — and what ISP/operator procurement teams should require in thermal specifications.

    The Thermal Challenge: Why Outdoor CPE Runs Hotter Than You Think

    Outdoor 5G CPE operates in fundamentally different thermal conditions than indoor equipment. Key heat sources and environmental stressors include:

    • Solar radiation load — Direct sunlight on the enclosure can add 15-25°C to internal ambient temperature. A CPE mounted on a Middle Eastern rooftop can experience an external surface temperature exceeding 85°C.
    • 5G modem power dissipation — Qualcomm X75 and X80 modems dissipate 3-7W under full load (4CC CA with 256QAM), concentrated in a small SoC die area (~80mm²). This creates a high heat flux density that must be efficiently spread and dissipated.
    • Power amplifier (PA) heat — The 5G NR FR1 PA chain adds 2-4W of additional heat, particularly at higher bands (n77/n78/n79 at 3.5-4.9 GHz) where PA efficiency drops.
    • Enclosure sealing penalty — IP68-rated enclosures (fully dust-tight, submersible) eliminate convective airflow between the interior and exterior. All heat must be conducted through the enclosure walls — a much less efficient thermal path than forced-air convection.
    • SoC throttling cascade — When junction temperature (Tj) exceeds the rated maximum (typically 95-105°C for modem SoCs), the chipset initiates thermal throttling, reducing throughput and potentially dropping carrier aggregation combinations — directly degrading user experience.

    Thermal Design Architecture: The Complete Heat Path

    Effective thermal management in outdoor CPE requires a system-level approach addressing every element in the heat path from chip junction to ambient air:

    1. Die-Level: Thermal Interface Material (TIM)

    The first and most critical thermal interface is between the modem SoC/PMIC dies and the internal heat spreader. High-performance TIMs for outdoor CPE must balance thermal conductivity with mechanical compliance:

    • Gap filler pads (silicon-based, 3-8 W/m·K) — Good for production consistency, moderate performance
    • Phase-change materials (PCM) (5-12 W/m·K) — Solid at room temperature, liquefy at operating temperature to fill micro-gaps. Superior wetting but requires containment
    • Thermal grease/paste (6-15 W/m·K) — Highest performance but risk of pump-out and dry-out over thermal cycling; requires validated long-term reliability data
    • Graphite pads (5-15 W/m·K in-plane) — Excellent for spreading heat laterally from small die to larger heat spreader area

    2. Board-Level: Heat Spreading and PCB Design

    The PCB itself is a critical thermal management element. Key design considerations:

    • Thermal vias — Dense arrays of plated through-holes (typically 0.3mm diameter, 0.8mm pitch) under the modem SoC BGA pads, filled and capped with copper, conduct heat from the top-layer pads to internal copper planes
    • Heavy copper layers — 2oz-4oz copper on internal ground/power planes acts as an in-plane heat spreader, reducing thermal resistance from the chip area to the board edges
    • Metal-core PCB (MCPCB) — For the RF PA section, aluminum or copper base MCPCB provides direct thermal path from PA transistors to enclosure baseplate
    • Component placement optimization — High-power components (modem, PA, PMIC) are placed with thermal separation; temperature-sensitive components (TCXO, GNSS LNA) are placed away from heat sources in cooler board zones

    3. Enclosure-Level: Conduction and Natural Convection

    The enclosure is the final thermal interface to the environment. Carrier-grade outdoor CPE enclosures use several complementary strategies:

    TechniqueThermal BenefitImplementation
    Die-cast aluminum enclosureHigh thermal conductivity (ADC12: ~96 W/m·K)One-piece die-cast housing with integrated fin geometry
    External cooling fins2-4x increase in effective surface area for natural convectionVertical fin orientation, optimized fin spacing (8-15mm) and height (20-40mm)
    Internal heat spreader plateEfficient conduction from PCB hot spots to enclosure wallsAluminum or copper plate with milled bosses contacting TIM above hot components
    Solar-reflective coatingReduces solar absorption by 30-50%White or light-colored powder coat with high solar reflectance (TSR ≥ 0.70)
    Radiation-enhanced surfaceImproves radiative heat transfer to skyAnodized or painted surface with high emissivity (ε ≥ 0.85)

    Environmental Hardening: Beyond Temperature

    Thermal management cannot be designed in isolation. It must coexist with other environmental hardening requirements:

    IP68 Sealing vs. Thermal Venting Trade-Off

    True IP68 (submersion-rated) enclosures cannot have ventilation openings — eliminating the most effective cooling mechanism. Some designs use Gore-Tex breathable membranes that allow pressure equalization while blocking liquid water ingress, enabling IP67/IP68 ratings with some vapor transmission. However, these do not provide meaningful convective cooling. The engineering trade-off is: accept higher internal operating temperatures in exchange for full environmental sealing, or use an IP67-rated design with drainage paths and conformal coating on internal PCBs.

    Condensation Management

    Outdoor enclosures experience daily thermal cycling (day/night temperature swings of 20-40°C), which creates internal condensation risk. Effective strategies include:

    • Internal desiccant packs (silica gel or molecular sieve) with sufficient capacity for the enclosure internal volume
    • Conformal coating (acrylic, silicone, or parylene) on all PCBs to protect against moisture-induced leakage currents and dendritic growth
    • Drainage paths and weeping holes (for IP67 designs) positioned at the lowest point with bug screens
    • Anti-condensation heaters that activate below dew point — typically a small resistive heater (5-10W) controlled by a humidity sensor

    Validation and Testing Standards

    B2B buyers should require thermal validation reports from CPE vendors. Key industry standards include:

    • IEC 60068-2-1/2/14/30/78 — Environmental testing: cold, dry heat, temperature cycling, damp heat, thermal shock
    • ETSI EN 300 019-1-4 Class 4.1/4.1E — Weather-protected and non-weather-protected outdoor locations
    • GR-487-CORE — Telcordia generic requirements for outdoor electronics enclosures (US market)
    • MIL-STD-810H Method 501.7/502.7 — High and low temperature operational testing with solar radiation profiles

    Honlly Telecom subjects all outdoor CPE designs to accelerated life testing (ALT) with 1,000-hour thermal cycling (-40°C to +85°C), 85°C/85% RH damp heat soak, and solar radiation simulation (1,120 W/m² per IEC 60068-2-5). Thermal imaging during full-load operation verifies that all SoC junction temperatures remain below 95°C with 15°C design margin at maximum rated ambient temperature.

    Frequently Asked Questions

    Q: What is the typical operating temperature range for carrier-grade outdoor CPE?
    A: Industrial-grade outdoor CPE should support -40°C to +60°C ambient air temperature with full performance (no thermal throttling). Extended-temperature variants (-40°C to +70°C) are available for extreme environments. Always confirm whether the specified range is ambient air temperature or internal enclosure temperature — the difference can be 15-25°C.

    Q: Does fanless design mean no thermal management?
    A: Absolutely not. Fanless design requires more sophisticated passive thermal management than active cooling. Fanless outdoor CPE relies on larger heat spreaders, optimized enclosure fin geometry, and premium TIMs to achieve equivalent thermal performance. Fanless is preferred for outdoor deployments because fans are a major failure point (dust ingress, bearing wear, power consumption).

    Q: How can I verify a vendor’s thermal claims?
    A: Request thermal simulation reports (ANSYS Icepak or FloTHERM models) showing junction temperatures for all major components at max rated ambient. Request thermal camera images from physical testing at full load. Ask for ALT (Accelerated Life Test) reports with pre/post thermal performance comparison. Honlly provides full thermal validation documentation as part of the CPE qualification package.

    Specify thermal-hardened outdoor 5G CPE for your next deployment. Contact Honlly Telecom’s hardware engineering team for thermal design documentation, ALT reports, and outdoor CPE evaluation samples with environmental testing data.

  • 5G Network Slicing for Enterprise FWA Enters Commercial Phase as Operators Launch Dedicated Slice-as-a-Service Offerings in 2026

    5G Network Slicing for Enterprise FWA Enters Commercial Phase as Operators Launch Dedicated Slice-as-a-Service Offerings in 2026

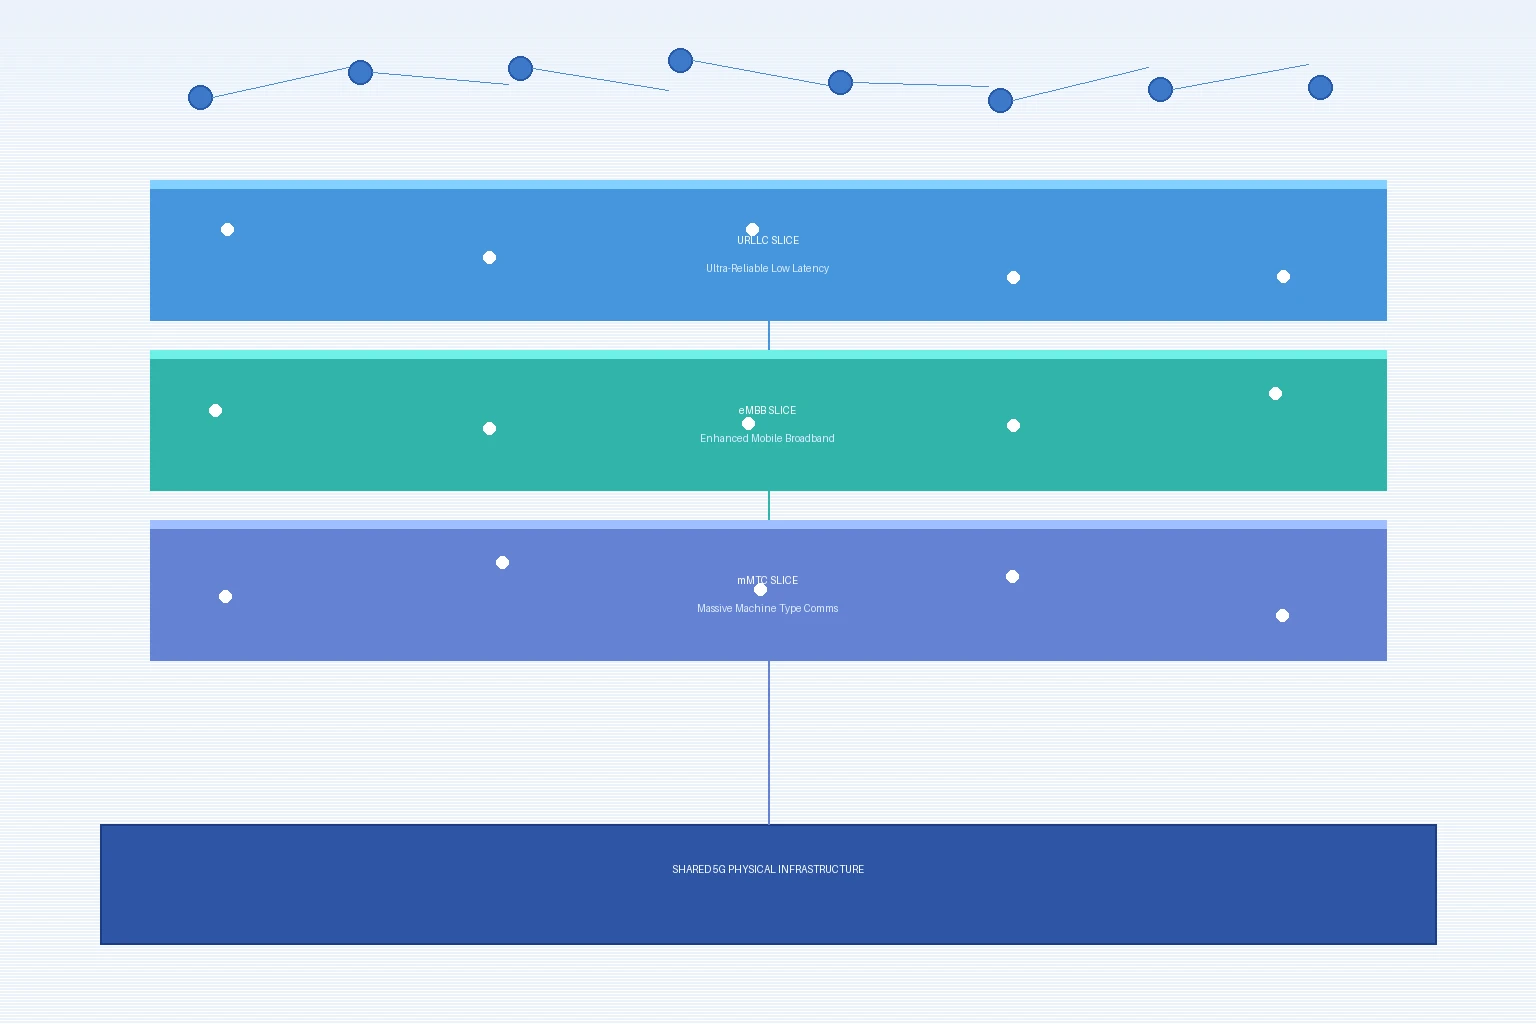
    The telecom industry is witnessing a paradigm shift as 5G network slicing transitions from lab trials and proof-of-concept demonstrations to live commercial deployments. In 2026, multiple Tier-1 and Tier-2 operators across Asia-Pacific, Europe, and the Middle East have launched dedicated enterprise slice-as-a-service offerings, enabling B2B customers to procure guaranteed QoS, latency, and throughput on shared 5G infrastructure.

    For ISP procurement teams, MVNO technical buyers, and enterprise FWA decision-makers, understanding the commercial readiness of network slicing is no longer optional — it directly impacts CPE specification requirements, SLA definitions, and total cost of ownership calculations for upcoming FWA deployments.

    What Is Changing in 2026?

    The 3GPP-defined network slicing framework (standardized from Release 15 through Release 18) has reached a maturity point where end-to-end slicing — from 5G core through RAN to CPE — is now commercially viable. Key developments include:

    • Standalone (SA) 5G core deployments have exceeded 60 commercial networks globally, providing the architectural foundation for slice orchestration
    • URSP (UE Route Selection Policy) support in CPE chipsets (Qualcomm X75/X80, MediaTek T800, UNISOC V510/V516) enables device-side slice selection and traffic routing
    • NSSAI (Network Slice Selection Assistance Information) integration in operator provisioning systems allows automated slice assignment per enterprise contract
    • Major NEPs (Ericsson, Nokia, Huawei) have deployed slice management functions (NSMF/NSSMF) with northbound APIs for BSS/OSS integration

    Commercial Slice Use Cases Driving CPE Demand

    Operators are packaging network slices into distinct enterprise product categories, each with specific CPE requirements:

    1. URLLC Slice for Industrial Automation

    Targeting manufacturing, mining, and port logistics, these slices deliver sub-5ms latency with 99.999% reliability. CPE requirements include dual-module redundancy, IEEE 802.1 TSN (Time-Sensitive Networking) bridging, and support for 5G-LAN type services. Honlly’s URLLC-ready CPE platforms integrate hardware timestamping and PRTC (Primary Reference Time Clock) synchronization for industrial protocol translation (PROFINET, EtherCAT, MODBUS TCP).

    2. eMBB Slice for Enterprise Branch and SD-WAN

    The most commercially mature slice category delivers guaranteed downlink throughput (typically 100-500 Mbps per slice) for enterprise branch offices, retail chains, and remote sites. CPE must support VLAN-to-slice mapping, application-aware traffic steering, and seamless integration with SD-WAN orchestration platforms (VMware VeloCloud, Fortinet, Cisco Catalyst).

    3. mMTC Slice for Massive IoT Backhaul

    Optimized for high-density sensor networks, smart metering, and environmental monitoring, mMTC slices prioritize connection density over per-device throughput. CPE serving as IoT gateways must support NB-IoT and LTE-M fallback aggregation, along with lightweight protocol translation (MQTT, CoAP, LwM2M) to cloud IoT platforms (AWS IoT Core, Azure IoT Hub).

    CPE Slicing Capabilities: What Buyers Must Verify

    Not all 5G CPE devices support network slicing equally. Procurement teams evaluating CPE for slice-enabled deployments should verify:

    CapabilityMinimum RequirementVerification Method
    URSP Support3GPP Rel-16 UE Route Selection PolicyCheck modem AT command interface / QMI for URSP rules
    Multiple PDU Sessions≥4 simultaneous PDU sessions on different slicesLab test with operator core simulator (Amarisoft, Keysight)
    S-NSSAI ConfigurationConfigurable S-NSSAI via TR-069/TR-369 ACS or local GUIVerify ACS parameter tree or Web UI slice settings page
    Slice-Aware QoSPer-slice 5QI-to-DSCP mapping, GBR/non-GBR handlingRFC 2544 throughput test per slice with iPerf3
    VLAN/Slice BindingIEEE 802.1Q VLAN trunking with slice-to-VLAN mappingVerify tagged traffic routing per VLAN to correct PDU session

    Operator Commercial Models and Pricing

    Operators are adopting varied commercial models for slice offerings. The shift toward slice-as-a-service introduces new pricing constructs that CPE procurement teams must factor into TCO models:

    • Per-slice subscription fee — Monthly recurring charge per activated slice (typically $50-$300/month for enterprise-grade URLLC slices)
    • QoS tier pricing — Premium surcharge for guaranteed bit rate (GBR) vs. non-GBR slices
    • Slice lifecycle management fee — Charge for slice creation, modification, and deletion via operator portal or API
    • SLA-backed throughput guarantee — Service credit mechanism if slice throughput drops below contracted level

    For ISPs and MVNOs, the ability to white-label slice offerings through CPE that supports multi-tenant slice isolation creates new revenue streams. A single CPE can serve multiple enterprise customers with dedicated slices, each with independent billing, QoS, and security policies.

    Honlly’s Slice-Ready CPE Portfolio

    Honlly Telecom’s 5G CPE platforms are designed for slice-enabled commercial deployments. Key features include:

    • Multi-PDU session support — Up to 8 simultaneous PDU sessions across different slices on Qualcomm X75-based platforms
    • URSP policy engine integration — Full support for network-provided and device-local URSP rules with fallback behavior
    • Slice-aware ACS management — TR-369 USP data model extensions for slice configuration, monitoring, and diagnostics
    • Hardware QoS offload — Dedicated NPU (Network Processing Unit) for per-slice traffic shaping, policing, and queue management at line rate
    • Operator certification — Pre-certified for network slicing interoperability with major 5G SA core vendors

    Frequently Asked Questions

    Q: Is network slicing available on 5G NSA (Non-Standalone) networks?
    A: No. Network slicing requires 5G SA (Standalone) architecture with a 5G core (5GC). NSA networks using EPC cannot support end-to-end slicing. Buyers should verify their target operator has deployed 5G SA before specifying slice-capable CPE.

    Q: How many slices can a single CPE support simultaneously?
    A: This depends on the modem chipset and software implementation. Entry-level platforms support 2-4 PDU sessions/slices, while premium platforms (Qualcomm X75/X80) support 8+. Honlly’s enterprise-grade CPE supports up to 8 simultaneous slices with hardware-accelerated QoS per slice.

    Q: What happens if the operator changes slice parameters mid-contract?
    A: 3GPP defines slice modification procedures where the network can update S-NSSAI parameters. CPE must support dynamic slice reconfiguration without requiring a device reboot. Honlly CPE implements graceful slice modification with sub-second failover to default slice if reconfiguration fails.

    Q: Can I mix and match CPE vendors across different slices on the same operator network?
    A: Yes — 3GPP network slicing is standardized and vendor-agnostic at the CPE-UE level. However, certain operator-specific slice management features (e.g., proprietary telemetry, slice-level FOTA) may require vendor-specific integration. Honlly’s open API architecture supports integration with all major operator NSSMF platforms.

    Ready to deploy slice-enabled 5G FWA CPE? Contact Honlly Telecom’s solutions engineering team for a technical consultation, CPE evaluation kit, and slice interoperability testing with your operator partner.

  • Wi-Fi 7 and 5G CPE Convergence: A Technical Architecture Guide for Enterprise LAN-WAN Integration with 802.11be MLO, 320 MHz Channels, and Multi-Gigabit Backhaul in 2026

    Wi-Fi 7 and 5G CPE Convergence: A Technical Architecture Guide for Enterprise LAN-WAN Integration with 802.11be MLO, 320 MHz Channels, and Multi-Gigabit Backhaul in 2026

    As enterprise networks evolve toward higher-density, lower-latency wireless architectures, the convergence of Wi-Fi 7 (IEEE 802.11be) and 5G FWA CPE represents one of the most consequential integration challenges — and opportunities — for B2B network infrastructure in 2026. Wi-Fi 7 access points are now shipping at scale from major vendors including Cisco, Aruba, and Huawei, with enterprise adoption accelerating through the second half of 2026. The question facing network architects and procurement teams is no longer whether to adopt Wi-Fi 7, but how to architect the 5G WAN edge to complement — rather than constrain — the 802.11be LAN environment.

    Wi-Fi 7: Beyond the Hype

    Wi-Fi 7 delivers several architectural improvements over Wi-Fi 6/6E that directly impact 5G CPE integration requirements:

    • 320 MHz Channel Bandwidth: Doubling the 160 MHz ceiling of Wi-Fi 6E, 320 MHz channels in the 6 GHz band require a backhaul connection capable of sustaining multi-gigabit throughput. A Wi-Fi 7 AP serving a dense enterprise floor can easily generate 8-10 Gbps of aggregate LAN traffic — well within 5G NR’s capability but only if the CPE WAN interface is engineered for end-to-end throughput, not just peak modem speed.
    • Multi-Link Operation (MLO): Wi-Fi 7’s signature feature enables simultaneous transmission across multiple frequency bands (2.4 GHz, 5 GHz, 6 GHz). MLO dramatically reduces latency and improves reliability, but it also multiplies the effective traffic load delivered to the CPE WAN port. A single MLO-capable client can generate 5+ Gbps of throughput — requiring careful CPE buffer management and QoS mapping between the Wi-Fi LAN and 5G WAN domains.
    • 4K QAM (4096-QAM): Wi-Fi 7’s higher modulation order achieves 20% greater spectral efficiency compared to Wi-Fi 6’s 1024-QAM. This translates to higher effective throughput at the same range, further raising the bar for CPE WAN interface provisioning.

    The 5G CPE as a Wi-Fi 7 Gateway: Architectural Models

    B2B deployments typically follow one of three integration architectures, each with distinct CPE requirements:

    Model A: Integrated 5G + Wi-Fi 7 CPE (All-in-One)

    For small-to-medium enterprise branches, retail locations, and remote offices, integrated CPE combining 5G NR modem, Wi-Fi 7 AP, and multi-gigabit Ethernet switching in a single device offers the simplest deployment model. Key technical requirements include a 2.5GbE or 10GbE WAN-to-LAN bridge to prevent the CPE’s internal switch fabric from becoming a throughput bottleneck, hardware-accelerated MLO support on the Wi-Fi 7 radio, and unified management plane for both cellular and Wi-Fi domains.

    Model B: 5G CPE as WAN Gateway + Dedicated Wi-Fi 7 APs

    Larger deployments typically separate the 5G WAN termination (CPE) from the Wi-Fi 7 LAN infrastructure for scalability and vendor flexibility. In this model, the 5G CPE functions as a pure WAN gateway, terminating the 5G NR connection and presenting a multi-gigabit Ethernet handoff to downstream Wi-Fi 7 AP controllers or switches. The CPE must support 10GbE SFP+ or 2.5GbE RJ45 WAN-side interfaces, hardware NAT/NAPT at line rate without degrading throughput, and standard routing protocols (BGP, OSPF) for integration with enterprise SD-WAN fabrics.

    Model C: Dual-WAN 5G CPE with Wi-Fi 7 AP Integration

    For business continuity and hybrid WAN scenarios, dual-5G-modem CPE configurations provide carrier diversity with automatic failover. Combined with Wi-Fi 7 MLO, this creates a resilient connectivity stack where both the WAN and LAN layers independently support multi-path operation. The CPE must coordinate failover events with the Wi-Fi 7 controller to prevent client re-association storms when WAN paths change.

    Throughput Engineering: Avoiding the Bottleneck

    The most common failure mode in Wi-Fi 7 + 5G CPE deployments is a throughput mismatch between the LAN and WAN domains. Consider a typical configuration: a Wi-Fi 7 AP with 320 MHz channel in 6 GHz delivering 8 Gbps aggregate throughput, connected to a 5G CPE with a baseband capable of 4 Gbps peak but an Ethernet interface limited to 1GbE. The result: the Wi-Fi 7 investment is wasted because the CPE’s physical interface becomes the bottleneck long before the 5G NR air interface reaches capacity.

    B2B buyers should verify end-to-end throughput across every link in the chain: 5G NR air interface → modem baseband → CPU/NPU forwarding engine → Ethernet PHY → Wi-Fi 7 AP → client device. Each hop must support at least the target service throughput, with headroom for MLO multiplication effects.

    Latency Coordination: 5G URLLC Meets Wi-Fi 7 MLO

    Latency-sensitive enterprise applications — including industrial automation, augmented reality, and real-time collaboration — benefit from coordinated low-latency behavior across both the 5G and Wi-Fi 7 domains. 5G URLLC features (mini-slot scheduling, configured grant transmission) can deliver sub-5ms one-way latency on the WAN side, while Wi-Fi 7 MLO with restricted target wake time (rTWT) can achieve sub-2ms latency on the LAN side. However, these mechanisms operate independently — the CPE must implement intelligent QoS mapping and traffic classification to preserve end-to-end latency guarantees across the WAN-LAN boundary.

    Security Considerations

    Wi-Fi 7 introduces WPA4 (based on WPA3 with enhanced 802.11be protections), which must interoperate with the 5G CPE’s security architecture. For enterprise deployments, this means consistent implementation of 802.1X authentication, RADIUS integration, and certificate-based device identity across both the Wi-Fi LAN and cellular WAN domains. The CPE should function as a policy enforcement point that applies consistent security rules regardless of whether traffic enters via 5G NR or local Wi-Fi 7 association.

    Procurement Checklist for B2B Buyers

    • Verify CPE WAN Ethernet interface supports at least 2.5GbE (preferably 10GbE SFP+) to avoid bottlenecking Wi-Fi 7’s 320 MHz channel throughput
    • Confirm hardware NAT/NP offload capable of line-rate forwarding at multi-gigabit speeds
    • Check for unified management API that exposes both 5G NR and Wi-Fi 7 telemetry to enterprise NMS platforms
    • Ensure MLO-aware QoS mapping between Wi-Fi 7 TID (Traffic Identifier) values and 5G 5QI (5G QoS Identifier) classes
    • Validate WPA4/WPA3-Enterprise interoperability with existing RADIUS/802.1X infrastructure

    At Honlly Telecom, our 5G FWA CPE platforms are engineered with Wi-Fi 7 convergence in mind — featuring 2.5GbE and 10GbE WAN interfaces, hardware-accelerated forwarding, and unified management APIs that bridge the cellular and Wi-Fi domains for enterprise deployers seeking to unlock the full potential of 802.11be without WAN-side compromise.

  • AI/ML-Driven 5G CPE Traffic Optimization: On-Device Intelligence for Predictive QoS, Autonomous Diagnostics, and Real-Time Application Classification in 2026 Enterprise FWA Deployments

    AI/ML-Driven 5G CPE Traffic Optimization: On-Device Intelligence for Predictive QoS, Autonomous Diagnostics, and Real-Time Application Classification in 2026 Enterprise FWA Deployments

    The integration of Artificial Intelligence and Machine Learning (AI/ML) into 5G CPE firmware represents one of the most transformative shifts in FWA device architecture since the transition from LTE to 5G NR. As enterprise networks grow more complex and application traffic becomes increasingly heterogeneous, static QoS configurations and threshold-based monitoring are proving insufficient. The 2026 generation of 5G CPE platforms is embedding AI/ML inference engines directly into the device — enabling real-time traffic classification, predictive bandwidth orchestration, and autonomous fault diagnostics that were previously possible only in cloud-based or core-network analytics systems.

    Why AI/ML Belongs at the CPE Edge

    The traditional model places network intelligence in the 5G core or cloud analytics platform, with CPE devices functioning as relatively passive WAN termination points. This architecture introduces inherent latency in the decision loop: traffic anomalies must traverse the WAN, be analyzed remotely, and trigger policy updates that propagate back to the device — often taking seconds or minutes. For latency-sensitive enterprise applications, this delay is unacceptable.

    Edge AI/ML in the CPE collapses this loop to microseconds. By running lightweight inference models directly on the CPE’s application processor or dedicated NPU (Neural Processing Unit), the device can classify application flows, detect anomalies, and adjust QoS parameters in real time — without depending on cloud connectivity. This is particularly critical for remote sites with intermittent or high-latency backhaul, where cloud-dependent analytics become unreliable precisely when they are most needed.

    Three Core AI/ML Workloads in 5G CPE

    1. Intelligent Traffic Classification and Dynamic QoS

    Traditional CPE QoS relies on static rules — mapping DSCP markings, 5QI values, or port numbers to priority queues. AI/ML-based classification goes further by inspecting traffic patterns in real time and identifying application types based on flow behavior rather than header markings alone. A properly trained model can distinguish between a Microsoft Teams video call (latency-sensitive, moderate bandwidth), a OneDrive file sync (bandwidth-intensive, latency-tolerant), and a SaaS application heartbeat (low volume, keep-alive priority) — even when all three traverse the same encrypted tunnel on the same port.

    This capability is especially valuable for SD-WAN-integrated CPE, where application-aware routing decisions depend on accurate real-time traffic identification. ML models trained on enterprise traffic datasets can achieve >95% application classification accuracy within the first 5-10 packets of a flow, enabling QoS decisions before the application session is fully established.

    2. Predictive Bandwidth Management

    Enterprise WAN traffic follows predictable temporal patterns: video conferencing peaks during business hours, cloud backups run overnight, software updates deploy on schedules. Predictive ML models — typically lightweight LSTM (Long Short-Term Memory) or Transformer-based architectures optimized for embedded deployment — can forecast bandwidth demand 15-60 minutes in advance with high accuracy.

    This foresight enables proactive resource allocation: the CPE can pre-negotiate additional 5G network slices during predicted peak periods, adjust buffer sizes to accommodate expected traffic bursts, or shift non-urgent traffic to off-peak windows. For operators offering tiered FWA services, predictive bandwidth management translates directly to improved SLA compliance and reduced customer churn.

    3. Autonomous Network Diagnostics and Self-Healing

    CPE faults — modem lock-ups, RF interference, SIM authentication failures, DHCP lease expirations — are a major operational cost for managed service providers. AI/ML-driven diagnostics continuously monitor device telemetry (signal strength, SNR, block error rate, temperature, memory utilization, process health) and detect anomaly patterns before they escalate into user-visible outages.

    Advanced implementations go beyond detection to autonomous remediation: when an ML model identifies a degrading RF condition, the CPE can proactively switch to a different 5G band, adjust antenna configuration, or trigger a controlled modem reset during a traffic lull — all without human intervention. Fleet operators deploying thousands of CPE units report 30-50% reductions in truck-roll incidents after implementing on-device ML diagnostics.

    Hardware Requirements for On-Device AI/ML

    Running ML inference at the CPE edge requires hardware considerations that go beyond traditional embedded router specifications:

    • NPU or AI Accelerator: Purpose-built neural processing units — such as those integrated into Qualcomm’s Networking Pro series, MediaTek’s Filogic platforms, or external accelerators like Hailo-8 — provide 2-26 TOPS of INT8 inference performance at sub-5W power envelopes. This is sufficient for running multiple concurrent traffic classification, bandwidth prediction, and anomaly detection models.
    • Memory Footprint: Quantized ML models for CPE applications typically require 50-200 MB of RAM — modest by smartphone standards but significant for embedded router platforms that traditionally ship with 256-512 MB. 2026 CPE designs targeting AI/ML workloads are now shipping with 1-2 GB of LPDDR4/LPDDR5 memory.
    • Model Update Pipeline: On-device models must be updatable via FOTA without service interruption. This requires A/B partitioning of the ML model storage, delta update support, and rollback mechanisms for model version regression.

    Privacy and Data Sovereignty Benefits

    An often-overlooked advantage of edge AI/ML in CPE is data sovereignty. Traffic classification and anomaly detection that run entirely on-device never export raw flow data to the cloud — addressing GDPR, CCPA, and sector-specific compliance requirements in industries like healthcare, finance, and government. The CPE can export anonymized, aggregated telemetry for fleet-level analytics while keeping sensitive per-flow data within the enterprise perimeter.

    The Road Ahead: Generative AI in CPE Management

    Looking beyond 2026, the next frontier is generative AI for CPE configuration and troubleshooting. Natural language interfaces that allow IT administrators to query device status (“Why is Branch 37 experiencing packet loss?”) and receive diagnostic summaries generated by small language models (SLMs) running locally on the CPE are already appearing in vendor roadmaps. This represents a fundamental shift from dashboard-driven management to conversational network operations — and the CPE, as the enterprise’s first touchpoint with the 5G network, is the natural platform for this intelligence.

    At Honlly Telecom, we are embedding AI/ML inference capabilities across our 2026 5G CPE lineup, with hardware-accelerated traffic classification, predictive bandwidth management, and autonomous diagnostics as standard features for enterprise-grade FWA deployments.

  • 5G RedCap (NR-Light) CPE Enters Commercial Mainstream as Operators and Enterprises Embrace Mid-Tier 5G for IoT, Smart Grid, and Retail Deployments in 2026

    5G RedCap (NR-Light) CPE Enters Commercial Mainstream as Operators and Enterprises Embrace Mid-Tier 5G for IoT, Smart Grid, and Retail Deployments in 2026

    The 5G device ecosystem is entering a pivotal diversification phase. While flagship 5G CPE platforms continue to push multi-gigabit performance boundaries for fixed wireless access (FWA) and enterprise branch connectivity, a parallel category is quietly gaining commercial momentum: 5G RedCap (NR-Light) CPE. Standardized in 3GPP Release 17 and enhanced in Release 18, RedCap defines a reduced-capability 5G NR device class that occupies the middle ground between ultra-high-performance eMBB devices and low-complexity NB-IoT/LTE-M endpoints — and it is reshaping how operators and enterprises think about 5G CPE procurement for mid-tier applications in 2026.

    What 5G RedCap Brings to CPE Design

    RedCap devices operate with a reduced bandwidth of 20 MHz in FR1 (sub-7 GHz) and support a single RX antenna branch (1RX) or dual-RX (2RX) configurations — compared to the 100 MHz bandwidth and 4×4 MIMO typical of full-spec eMBB CPE. This architectural simplification delivers three direct benefits for CPE integration: lower bill-of-materials cost (estimated 50-65% reduction vs. full 5G modems), reduced power consumption (targeting 1-3W typical operation), and smaller physical form factors suitable for embedded deployment in industrial gateways, smart meters, and compact enterprise access points.

    For B2B buyers, this is not about compromising on connectivity — it is about rightsizing the radio for the application. A connected sensor array monitoring warehouse temperature does not need 4×4 MIMO and 100 MHz carrier aggregation. A point-of-sale terminal in a retail chain does not benefit from 256QAM in the downlink. RedCap CPE delivers the reliability, low latency, and network slicing benefits of 5G NR at a cost and complexity profile aligned with these use cases.

    Commercial Deployment Landscape in 2026

    Multiple tier-1 operators have activated RedCap on their 5G SA networks during 2025-2026. China Mobile, Deutsche Telekom, and AT&T have all launched commercial RedCap services, with device certification programs now accepting RedCap CPE modules from Qualcomm (Snapdragon X35), MediaTek (T300), and UNISOC. The GSMA’s Q2 2026 device registry lists over 85 RedCap-capable CPE and module SKUs — up from just 12 in early 2025.

    Key deployment verticals driving demand include:

    • Industrial IoT Gateways: RedCap CPE serving as aggregation backhaul for Modbus, PROFINET, and OPC-UA sensor networks in factory environments, replacing legacy LTE Cat-4/Cat-6 gateways with 5G-native connectivity at comparable cost points.
    • Smart Grid and Utility Networks: Distribution automation, smart meter concentrators, and substation monitoring equipment benefit from 5G’s deterministic latency and network slicing without requiring full eMBB throughput.
    • Retail and POS Infrastructure: Multi-site retail chains deploying RedCap CPE for PCI-DSS compliant payment processing, inventory management, and digital signage backhaul — applications where 150-220 Mbps peak throughput is more than sufficient.
    • Smart City Sensor Networks: Traffic management cameras, environmental monitoring stations, and public safety infrastructure leveraging RedCap’s improved coverage characteristics compared to LTE-M.

    Technical Considerations for B2B Procurement

    Procurement teams evaluating RedCap CPE should focus on several technical parameters that differentiate device quality:

    SA Core Dependency: RedCap requires a 5G Standalone (SA) core network. Unlike NSA-mode eMBB CPE that can fall back to LTE EPC anchoring, RedCap devices operate natively on 5G SA. Buyers must verify operator SA coverage in target deployment regions before committing to RedCap CPE fleets. The good news: as of mid-2026, over 62% of global 5G operators have deployed SA cores, according to GSA data.

    Power Profile and PoE Integration: RedCap’s 1-3W power envelope makes Power over Ethernet (PoE) a natural fit. Many industrial RedCap CPE designs now support 802.3at (PoE+) or 802.3bt (PoE++) for single-cable deployment, eliminating the need for separate power infrastructure in factory and outdoor installations.

    Network Slicing Support: RedCap devices can participate in URLLC-like network slices for latency-sensitive applications. While RedCap itself does not deliver full URLLC latency (which requires 4Rx and wider bandwidths), it achieves sub-10ms one-way latency in optimized SA deployments — sufficient for most industrial monitoring and control applications.

    RedCap vs. LTE Cat-6: The Migration Equation

    Many enterprises currently run private LTE Cat-4 or Cat-6 networks for IoT backhaul. RedCap presents a compelling migration path: comparable hardware costs, 2-3x throughput improvement (150-220 Mbps vs. 50-150 Mbps), native 5G SA security architecture, and access to network slicing. For greenfield deployments, the TCO analysis increasingly favors RedCap over LTE — especially in regions where operators are beginning to refarm LTE spectrum toward 5G NR.

    Honlly’s RedCap CPE Roadmap

    At Honlly Telecom, we are integrating RedCap-capable modules into our mid-tier 5G CPE product line, targeting industrial IoT gateway and multi-site enterprise applications. Our RedCap CPE designs prioritize PoE power delivery, industrial temperature range operation (-40°C to +75°C), and compatibility with leading 5G SA core vendors including Ericsson, Nokia, and Huawei. For B2B buyers seeking to rightsize their 5G connectivity investment without sacrificing reliability or forward compatibility, RedCap CPE represents one of the most strategically important device categories to watch in the second half of 2026.

  • Cloud-Native TR-369 USP Device Management for Carrier-Grade 5G CPE: Migrating from TR-069

    Cloud-Native TR-369 USP Device Management for Carrier-Grade 5G CPE: Migrating from TR-069

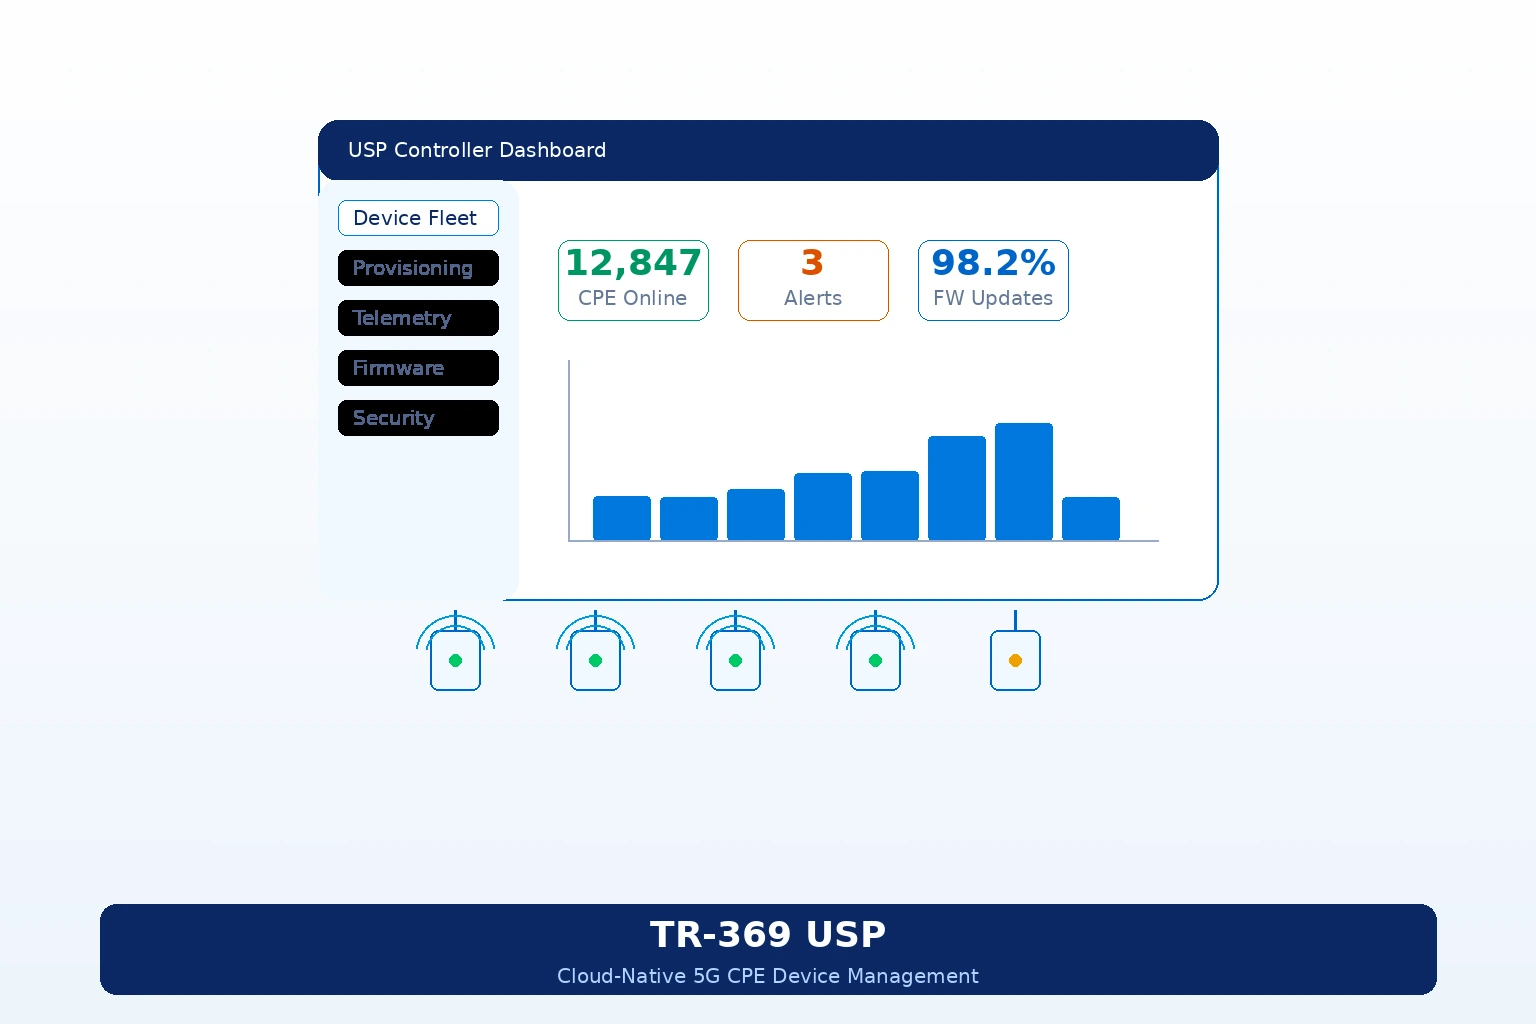
    For over 15 years, TR-069 (CPE WAN Management Protocol, or CWMP) has been the workhorse of broadband device management, enabling operators to remotely configure, monitor, and troubleshoot millions of CPE devices. But as 5G networks push toward cloud-native, microservices-based operations, TR-069’s SOAP/XML foundations and rigid client-server architecture are showing their age. The Broadband Forum’s TR-369 USP (User Services Platform) — commonly referred to as USP — is the designated successor, and operator migration timelines are accelerating through 2026.

    Why TR-069 Is Reaching Its Limits in the 5G Era

    TR-069 was designed in the DSL era and optimized for intermittent connectivity, low-bandwidth management traffic, and centralized ACS (Auto Configuration Server) architectures. In modern 5G FWA deployments, several limitations have become critical:

    • Connection-oriented polling: TR-069 relies on periodic CPE-initiated sessions (Periodic Inform) or ACS-triggered Connection Requests. In 5G networks with NAT44/NAT64/CGNAT traversal, Connection Requests frequently fail or require STUN-based workarounds that add latency.
    • SOAP/XML overhead: Each TR-069 transaction wraps parameter values in multiple layers of SOAP envelope, XML namespace declarations, and CWMP method framing. For bulk parameter queries across thousands of CPEs, this overhead is computationally expensive on both the ACS and CPE sides.
    • Limited concurrency model: TR-069 sessions are single-threaded per CPE. Simultaneous configuration changes, firmware downloads, and diagnostics require sequential session handling, creating bottlenecks in large-scale operations.
    • No native push-notification architecture: CPE-originated events (alarms, threshold breaches, connectivity changes) are batched into the next Periodic Inform interval rather than delivered in real time — a significant operational gap for carrier-grade 5G FWA.

    TR-369 USP: Architecture and Key Capabilities

    TR-369 USP fundamentally rearchitects the device-management paradigm around three principles: message-oriented communication, multi-protocol transport, and service-based abstraction.

    USP Message Architecture

    USP uses a compact, binary-encoded message format (Protocol Buffers, or protobuf) transported over WebSocket, MQTT, STOMP, or CoAP — a dramatic departure from TR-069’s HTTP/1.1 + SOAP/XML stack. Each USP message carries:

    • Header: Message ID, message type (Get, Set, Add, Delete, Operate, Notify), source/destination endpoint identifiers.
    • Body: A Request/Response or Notification payload, encoded in protobuf with strong typing and schema validation.
    • Record-level integrity: USP supports per-message digital signatures (using JWS) and TLS 1.3 mutual authentication, meeting carrier security requirements without the XML Signature overhead of TR-069.

    Multi-Protocol Transport and Always-On Connectivity

    Unlike TR-069’s session-based HTTP model, USP supports persistent connections via WebSocket, enabling:

    • Real-time push notifications: CPE events (link status changes, throughput threshold alarms, security incidents) are pushed to the controller in real time, enabling proactive network operations.
    • Bidirectional command flow: The controller can send configuration commands to the CPE at any time without waiting for a Connection Request cycle or Periodic Inform window.
    • MQTT integration: For operators with existing MQTT-based IoT or telemetry infrastructure, USP agents can connect directly to MQTT brokers, unifying CPE management with broader IoT device management under a single message bus.

    USP Data Model: TR-181 Device:2 and Service Objects

    USP reuses the TR-181 Device:2 data model (already familiar from TR-069) but extends it with service objects that map directly to 5G-specific management domains:

    • Device.WiFi.* objects for Wi-Fi 6/6E/7 radio, SSID, and band steering configuration.
    • Device.Cellular.* objects for 5G NR modem status, PLMN selection, band locking, carrier aggregation state, and signal quality metrics (RSRP, RSRQ, SINR per component carrier).
    • Device.Firewall.*, Device.Routing.*, Device.QoS.* for advanced networking configuration.
    • Device.BulkData.* for throughput and latency telemetry streaming (IPFIX-based).
    • Device.SoftwareModules.* for containerized firmware component management (DU, CU separation in multi-component CPE architectures).

    Migration Path: From TR-069 ACS to USP Controller

    Most operators cannot execute a “big-bang” replacement of their TR-069 infrastructure. The Broadband Forum anticipates a 3-5 year coexistence period during which CPE fleets will include a mix of TR-069-only, USP-only, and dual-stack devices. The recommended migration strategy includes:

    Phase 1: USP Controller Deployment with TR-069 Proxy (2026)

    Deploy a USP Controller that also implements a TR-069 southbound proxy (or integrates with the existing ACS via northbound APIs). This enables:

    • Unified operator dashboards that query and configure both TR-069 and USP CPE through a single interface.
    • Gradual CPE replacement or firmware upgrade without service disruption on legacy devices.
    • Parallel monitoring of Key Performance Indicators (KPIs) across protocol generations.

    Phase 2: Dual-Stack CPE with USP Preference (2026-2027)

    Procure or upgrade CPE firmware to support both TR-069 and USP agents simultaneously, with USP as the preferred management channel and TR-069 as fallback. New CPE should:

    • Register with both the legacy ACS and the new USP Controller on initial boot.
    • Accept configuration changes through either channel, with USP taking precedence when both attempt to modify the same parameter.
    • Report telemetry and events through USP while maintaining TR-069 Inform-based health checks for backward compatibility.

    Phase 3: TR-069 Decommissioning (2027-2028)

    Once the USP Controller demonstrates equivalent or superior operational KPIs (provisioning success rate, alarm delivery latency, bulk configuration throughput), operators can begin phasing out TR-069 ACS infrastructure. Legacy CPE that cannot be upgraded should be targeted for replacement as part of natural hardware refresh cycles (typically 3-5 years for FWA CPE).

    Operational Benefits of USP Migration

    Operators who have completed pilot USP deployments report significant operational improvements:

    • Provisioning time reduction: Bulk configuration of 10,000 CPEs completes in minutes rather than hours, thanks to USP’s concurrent message processing and protobuf’s compact encoding (typically 5-10x smaller than equivalent SOAP/XML payloads).
    • Real-time alarm response: CPE-originated alarms (5G signal degradation, WAN link failure, security intrusion detection) arrive at the NOC in under 5 seconds rather than the 5-15 minute Periodic Inform window, enabling faster mean-time-to-resolution (MTTR).
    • Firmware upgrade success rates: USP’s segmented file transfer with integrity verification and resume capability improves firmware upgrade success rates in lossy 5G environments compared to TR-069’s monolithic HTTP download model.
    • Cloud-native integration: USP Controller implementations built on Kubernetes and Kafka integrate natively with operator DevOps toolchains (CI/CD pipelines, Prometheus/Grafana monitoring, ELK logging), reducing operational overhead compared to monolithic ACS appliances.

    Selecting a USP Stack: Build vs. Buy

    Operators have several options for USP infrastructure:

    • Open-source USP Controller (OB-USP-Agent + OB-USP-Controller): The Broadband Forum’s reference implementations provide a solid starting point. Suitable for operators with in-house CPE management development teams who want full customization.
    • Commercial USP platforms: Vendors including Axiros, Friendly Technologies, Incognito, and AVSystem offer carrier-grade USP Controllers with TR-069 coexistence, multi-tenancy, and integration with existing OSS/BSS. Typically the faster path to production for operators without large in-house CPE management teams.
    • CPE vendor-managed USP: Some CPE manufacturers (including Honlly Telecom) provide USP agent firmware and can host managed USP Controller instances, offering a turnkey device management solution for smaller operators and MVNOs.

    USP Agent Requirements for 5G FWA CPE

    When evaluating and procuring 5G FWA CPE with USP support, operators should verify the following agent capabilities:

    • USP 1.3+ compliance with WebSocket and MQTT transport support.
    • TR-181 Device:2.16+ data model support including Cellular interface extensions for 5G NR (NRCell, NRCarrier, ENDC combination status).
    • TLS 1.3 with mutual authentication using device certificates (SMI or operator PKI issued).
    • Bulk data collection (BulkData object) with configurable reporting intervals for throughput, latency, and signal quality telemetry.
    • Firmware upgrade with USP segmented download and digital signature verification.
    • Concurrent session support for simultaneous configuration and monitoring operations.
    • TR-069 coexistence mode (dual-agent) for migration-phase deployments.

    Conclusion

    The migration from TR-069 to TR-369 USP is not merely a protocol upgrade — it is a fundamental shift toward cloud-native, event-driven device management that aligns 5G FWA CPE operations with modern carrier infrastructure. Operators who begin their USP migration in 2026 will be well-positioned to exploit real-time telemetry, automated service orchestration, and containerized firmware management as their 5G FWA subscriber bases scale through the end of the decade.

    For operators planning 5G FWA CPE deployments, specifying TR-369 USP support in procurement RFPs today ensures that device fleets deployed in 2026-2027 will support the management architecture carriers will operate through 2030 and beyond.


    Honlly Telecom’s 5G FWA CPE platforms support TR-369 USP with TR-069 coexistence. Contact our solutions team to discuss USP integration for your device fleet.

  • 5G-Advanced (3GPP Release 18) CPE Readiness: What Operators Need to Know for 2026-2027 Deployments

    5G-Advanced (3GPP Release 18) CPE Readiness: What Operators Need to Know for 2026-2027 Deployments

    The 3GPP Release 18 specification reached its functional freeze in mid-2025, marking the official arrival of 5G-Advanced — the evolutionary bridge between current 5G NR deployments and the future 6G ecosystem. For operators and enterprise buyers evaluating 5G CPE, FWA routers, and MiFi procurement strategies, understanding precisely which Release 18 capabilities will materialize in commercial CPE chipsets across 2026 and 2027 is now a critical planning exercise.

    What Is 5G-Advanced and Why Does It Matter for CPE?

    5G-Advanced — also branded as 5.5G by some vendors — introduces a suite of enhancements across three pillars: enhanced mobile broadband (eMBB+), massive IoT expansion, and AI/ML-native air interface optimization. Unlike the generational leap from 4G to 5G, Release 18 builds incrementally on the existing 5G NR foundation, which means backward-compatible CPE upgrades are feasible — but only if the underlying modem and RF front-end were designed with enough headroom.

    Key Release 18 features with direct CPE impact include:

    • MIMO Enhancement (FeMIMO): Support for up to 32-port base-station MIMO with improved CPE-side beam management, increasing cell-edge throughput for fixed wireless access deployments by an estimated 20-35% compared to Release 17 configurations.
    • AI/ML for NR Air Interface: Network-side AI-driven CSI (Channel State Information) compression and beam prediction reduce signaling overhead. CPE devices with compatible modem firmware can benefit from these optimizations without hardware changes — a significant procurement advantage.
    • NR Sidelink Evolution: Expanded sidelink relay capabilities enable CPE-to-CPE mesh topologies, particularly interesting for campus and industrial private network deployments where multiple CPE units can form resilient local backhaul.
    • Enhanced Positioning (cm-level): Carrier-phase positioning enables sub-meter accuracy, opening new enterprise use cases for location-aware CPE in logistics, manufacturing, and smart infrastructure.
    • Extended Reality (XR) Optimizations: QoS handling tuned for variable-bitrate XR traffic benefits CPE deployed in telemedicine, remote training, and industrial AR applications.

    CPE Chipset Roadmap: Who Is Supporting Release 18?

    The CPE silicon landscape for 5G-Advanced is coalescing around three major platforms:

    Qualcomm X80 / X85 Modem-RF Systems (announced 2025, sampling 2026): The X80 was the first modem announced with explicit Release 18 readiness, including 6x carrier aggregation across sub-6 GHz and mmWave, the dedicated AI tensor accelerator for CSI feedback optimization, and integrated NTN (non-terrestrial network) support for satellite-direct-to-device. The follow-on X85, expected in volume during H2 2026, extends carrier aggregation to 8x and adds Release 18 sidelink capabilities.

    MediaTek T830 Platform (sampling since late 2025): The T830 targets the mid-range FWA CPE market with Release 18 MIMO enhancement support and AI-driven power management. It supports 4x CA across sub-6 GHz bands and integrates Wi-Fi 7 (802.11be) for the LAN side, making it a strong candidate for carrier-branded home gateways.

    UNISOC V510 / upcoming V520 (2026): UNISOC is positioning the V510 as a cost-optimized Release 18 CPE platform for emerging markets, supporting 3x CA and basic FeMIMO, with the V520 adding sidelink relay capabilities expected in 2027.

    Which Operators Are Deploying 5G-Advanced CPE?

    Several tier-1 operators have already signaled 5G-Advanced CPE deployment timelines:

    • China Mobile began 5G-Advanced (5.5G) commercial trials in 2025 across 300+ cities, with FWA CPE rollouts targeting 2026 Q3-Q4. Procurement specifications already reference Release 18 MIMO and AI/ML CSI features.
    • Etisalat (e&) announced 5G-Advanced FWA services in the UAE starting mid-2026, with CPE RFPs requiring Release 18 carrier aggregation support.
    • European operators including Deutsche Telekom and Vodafone are testing Release 18 CPE in lab environments, with commercial deployment timelines clustered around late 2026 to early 2027.

    Procurement Guidance for B2B Buyers and Operators

    For operators, MVNOs, and enterprise buyers sourcing 5G CPE in 2026, the following recommendations apply:

    1. Verify modem silicon generation. Not all “5G CPE” available in 2026 includes Release 18 support. Request modem model numbers and cross-reference against the chipset vendor’s Release 18 feature matrix. Devices based on Qualcomm X75 or earlier, MediaTek T750 or earlier, or UNISOC V510 or earlier will not support key Release 18 enhancements.

    2. Plan for firmware-upgradable AI/ML features. Many Release 18 AI/ML air-interface optimizations are network-side or implementable via modem firmware updates. Ensure vendor roadmaps include at least one major firmware release targeting Release 18 feature activation during 2026-2027.

    3. Evaluate sidelink-enabled CPE for enterprise private networks. If your deployment includes campus or industrial sites, Release 18 sidelink relay capabilities can significantly reduce fiber backhaul dependency by enabling mesh topologies between CPE units. Factor this into total cost of ownership (TCO) calculations.

    4. Watch for NTN (satellite) integration. Release 18 expands NTN support to include IoT-NTN and NR-NTN enhancements. For operators serving rural or remote regions, CPE with integrated satellite fallback via NTN can dramatically reduce coverage-gap costs.

    5. Wi-Fi 7 bundling is becoming standard. Release 18-era CPE almost universally pairs 5G-Advanced WAN with Wi-Fi 7 LAN. Ensure your procurement specifications explicitly call for Wi-Fi 7 (802.11be) rather than Wi-Fi 6/6E to avoid stranded investment in soon-to-be-legacy LAN silicon.

    The 2026-2027 Transition Window

    The 2026-2027 period represents a critical procurement window. Operators who lock in multi-year CPE supply agreements based on Release 17 silicon risk a 12-18 month competitive disadvantage as 5G-Advanced networks come online. Conversely, early adopters of Release 18 CPE will be positioned to offer differentiated services — higher cell-edge throughput, location-aware enterprise applications, and satellite-integrated coverage — from day one of network activation.

    As a 5G CPE and MiFi manufacturer serving global operators, Honlly Telecom is actively aligning its product roadmap with 3GPP Release 18 timelines. For operators seeking Release 18-ready CPE solutions, early engagement with manufacturers who are tracking silicon availability and feature integration roadmaps is strongly recommended.


    This article is part of Honlly Telecom’s ongoing coverage of 5G standards evolution and its impact on B2B CPE procurement. For more information on 5G-Advanced-ready CPE solutions, contact our sales team.