Category: Blog

Technical guides and best practices

  • 5G Outdoor CPE Thermal Engineering: Advanced Heat Dissipation Design, IP68 Enclosure Cooling, and Environmental Hardening for Carrier-Grade Deployments

    5G Outdoor CPE Thermal Engineering: Advanced Heat Dissipation Design, IP68 Enclosure Cooling, and Environmental Hardening for Carrier-Grade Deployments

    Outdoor 5G CPE deployments in extreme environments — desert solar farms, tropical telecom towers, arctic mining operations, and dense urban rooftops — face a fundamental engineering challenge: managing heat dissipation while maintaining IP68 environmental sealing. Poor thermal design is the leading cause of premature CPE failure in carrier-grade outdoor deployments, directly impacting SLA compliance, truck-roll costs, and total cost of ownership.

    This technical guide examines the thermal engineering principles, materials science, and design methodologies that distinguish carrier-grade outdoor CPE from consumer-grade devices — and what ISP/operator procurement teams should require in thermal specifications.

    The Thermal Challenge: Why Outdoor CPE Runs Hotter Than You Think

    Outdoor 5G CPE operates in fundamentally different thermal conditions than indoor equipment. Key heat sources and environmental stressors include:

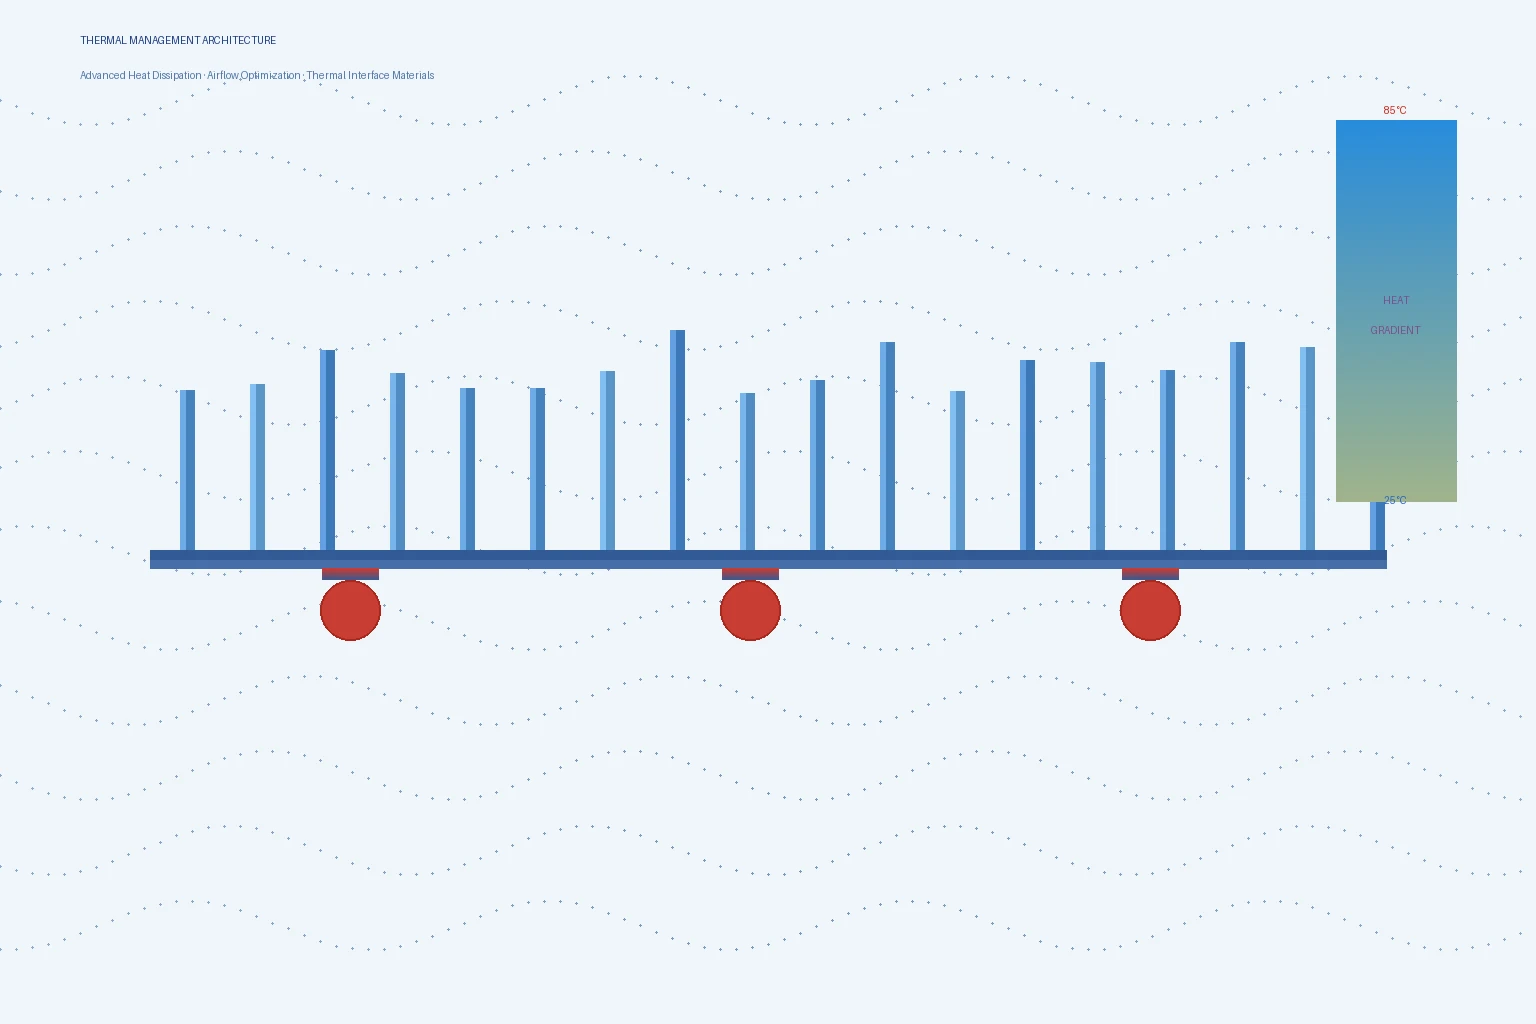
    • Solar radiation load — Direct sunlight on the enclosure can add 15-25°C to internal ambient temperature. A CPE mounted on a Middle Eastern rooftop can experience an external surface temperature exceeding 85°C.
    • 5G modem power dissipation — Qualcomm X75 and X80 modems dissipate 3-7W under full load (4CC CA with 256QAM), concentrated in a small SoC die area (~80mm²). This creates a high heat flux density that must be efficiently spread and dissipated.
    • Power amplifier (PA) heat — The 5G NR FR1 PA chain adds 2-4W of additional heat, particularly at higher bands (n77/n78/n79 at 3.5-4.9 GHz) where PA efficiency drops.
    • Enclosure sealing penalty — IP68-rated enclosures (fully dust-tight, submersible) eliminate convective airflow between the interior and exterior. All heat must be conducted through the enclosure walls — a much less efficient thermal path than forced-air convection.
    • SoC throttling cascade — When junction temperature (Tj) exceeds the rated maximum (typically 95-105°C for modem SoCs), the chipset initiates thermal throttling, reducing throughput and potentially dropping carrier aggregation combinations — directly degrading user experience.

    Thermal Design Architecture: The Complete Heat Path

    Effective thermal management in outdoor CPE requires a system-level approach addressing every element in the heat path from chip junction to ambient air:

    1. Die-Level: Thermal Interface Material (TIM)

    The first and most critical thermal interface is between the modem SoC/PMIC dies and the internal heat spreader. High-performance TIMs for outdoor CPE must balance thermal conductivity with mechanical compliance:

    • Gap filler pads (silicon-based, 3-8 W/m·K) — Good for production consistency, moderate performance
    • Phase-change materials (PCM) (5-12 W/m·K) — Solid at room temperature, liquefy at operating temperature to fill micro-gaps. Superior wetting but requires containment
    • Thermal grease/paste (6-15 W/m·K) — Highest performance but risk of pump-out and dry-out over thermal cycling; requires validated long-term reliability data
    • Graphite pads (5-15 W/m·K in-plane) — Excellent for spreading heat laterally from small die to larger heat spreader area

    2. Board-Level: Heat Spreading and PCB Design

    The PCB itself is a critical thermal management element. Key design considerations:

    • Thermal vias — Dense arrays of plated through-holes (typically 0.3mm diameter, 0.8mm pitch) under the modem SoC BGA pads, filled and capped with copper, conduct heat from the top-layer pads to internal copper planes
    • Heavy copper layers — 2oz-4oz copper on internal ground/power planes acts as an in-plane heat spreader, reducing thermal resistance from the chip area to the board edges
    • Metal-core PCB (MCPCB) — For the RF PA section, aluminum or copper base MCPCB provides direct thermal path from PA transistors to enclosure baseplate
    • Component placement optimization — High-power components (modem, PA, PMIC) are placed with thermal separation; temperature-sensitive components (TCXO, GNSS LNA) are placed away from heat sources in cooler board zones

    3. Enclosure-Level: Conduction and Natural Convection

    The enclosure is the final thermal interface to the environment. Carrier-grade outdoor CPE enclosures use several complementary strategies:

    TechniqueThermal BenefitImplementation
    Die-cast aluminum enclosureHigh thermal conductivity (ADC12: ~96 W/m·K)One-piece die-cast housing with integrated fin geometry
    External cooling fins2-4x increase in effective surface area for natural convectionVertical fin orientation, optimized fin spacing (8-15mm) and height (20-40mm)
    Internal heat spreader plateEfficient conduction from PCB hot spots to enclosure wallsAluminum or copper plate with milled bosses contacting TIM above hot components
    Solar-reflective coatingReduces solar absorption by 30-50%White or light-colored powder coat with high solar reflectance (TSR ≥ 0.70)
    Radiation-enhanced surfaceImproves radiative heat transfer to skyAnodized or painted surface with high emissivity (ε ≥ 0.85)

    Environmental Hardening: Beyond Temperature

    Thermal management cannot be designed in isolation. It must coexist with other environmental hardening requirements:

    IP68 Sealing vs. Thermal Venting Trade-Off

    True IP68 (submersion-rated) enclosures cannot have ventilation openings — eliminating the most effective cooling mechanism. Some designs use Gore-Tex breathable membranes that allow pressure equalization while blocking liquid water ingress, enabling IP67/IP68 ratings with some vapor transmission. However, these do not provide meaningful convective cooling. The engineering trade-off is: accept higher internal operating temperatures in exchange for full environmental sealing, or use an IP67-rated design with drainage paths and conformal coating on internal PCBs.

    Condensation Management

    Outdoor enclosures experience daily thermal cycling (day/night temperature swings of 20-40°C), which creates internal condensation risk. Effective strategies include:

    • Internal desiccant packs (silica gel or molecular sieve) with sufficient capacity for the enclosure internal volume
    • Conformal coating (acrylic, silicone, or parylene) on all PCBs to protect against moisture-induced leakage currents and dendritic growth
    • Drainage paths and weeping holes (for IP67 designs) positioned at the lowest point with bug screens
    • Anti-condensation heaters that activate below dew point — typically a small resistive heater (5-10W) controlled by a humidity sensor

    Validation and Testing Standards

    B2B buyers should require thermal validation reports from CPE vendors. Key industry standards include:

    • IEC 60068-2-1/2/14/30/78 — Environmental testing: cold, dry heat, temperature cycling, damp heat, thermal shock
    • ETSI EN 300 019-1-4 Class 4.1/4.1E — Weather-protected and non-weather-protected outdoor locations
    • GR-487-CORE — Telcordia generic requirements for outdoor electronics enclosures (US market)
    • MIL-STD-810H Method 501.7/502.7 — High and low temperature operational testing with solar radiation profiles

    Honlly Telecom subjects all outdoor CPE designs to accelerated life testing (ALT) with 1,000-hour thermal cycling (-40°C to +85°C), 85°C/85% RH damp heat soak, and solar radiation simulation (1,120 W/m² per IEC 60068-2-5). Thermal imaging during full-load operation verifies that all SoC junction temperatures remain below 95°C with 15°C design margin at maximum rated ambient temperature.

    Frequently Asked Questions

    Q: What is the typical operating temperature range for carrier-grade outdoor CPE?
    A: Industrial-grade outdoor CPE should support -40°C to +60°C ambient air temperature with full performance (no thermal throttling). Extended-temperature variants (-40°C to +70°C) are available for extreme environments. Always confirm whether the specified range is ambient air temperature or internal enclosure temperature — the difference can be 15-25°C.

    Q: Does fanless design mean no thermal management?
    A: Absolutely not. Fanless design requires more sophisticated passive thermal management than active cooling. Fanless outdoor CPE relies on larger heat spreaders, optimized enclosure fin geometry, and premium TIMs to achieve equivalent thermal performance. Fanless is preferred for outdoor deployments because fans are a major failure point (dust ingress, bearing wear, power consumption).

    Q: How can I verify a vendor’s thermal claims?
    A: Request thermal simulation reports (ANSYS Icepak or FloTHERM models) showing junction temperatures for all major components at max rated ambient. Request thermal camera images from physical testing at full load. Ask for ALT (Accelerated Life Test) reports with pre/post thermal performance comparison. Honlly provides full thermal validation documentation as part of the CPE qualification package.

    Specify thermal-hardened outdoor 5G CPE for your next deployment. Contact Honlly Telecom’s hardware engineering team for thermal design documentation, ALT reports, and outdoor CPE evaluation samples with environmental testing data.
  • Wi-Fi 7 and 5G CPE Convergence: A Technical Architecture Guide for Enterprise LAN-WAN Integration with 802.11be MLO, 320 MHz Channels, and Multi-Gigabit Backhaul in 2026

    Wi-Fi 7 and 5G CPE Convergence: A Technical Architecture Guide for Enterprise LAN-WAN Integration with 802.11be MLO, 320 MHz Channels, and Multi-Gigabit Backhaul in 2026

    As enterprise networks evolve toward higher-density, lower-latency wireless architectures, the convergence of Wi-Fi 7 (IEEE 802.11be) and 5G FWA CPE represents one of the most consequential integration challenges — and opportunities — for B2B network infrastructure in 2026. Wi-Fi 7 access points are now shipping at scale from major vendors including Cisco, Aruba, and Huawei, with enterprise adoption accelerating through the second half of 2026. The question facing network architects and procurement teams is no longer whether to adopt Wi-Fi 7, but how to architect the 5G WAN edge to complement — rather than constrain — the 802.11be LAN environment.

    Wi-Fi 7: Beyond the Hype

    Wi-Fi 7 delivers several architectural improvements over Wi-Fi 6/6E that directly impact 5G CPE integration requirements:

    • 320 MHz Channel Bandwidth: Doubling the 160 MHz ceiling of Wi-Fi 6E, 320 MHz channels in the 6 GHz band require a backhaul connection capable of sustaining multi-gigabit throughput. A Wi-Fi 7 AP serving a dense enterprise floor can easily generate 8-10 Gbps of aggregate LAN traffic — well within 5G NR’s capability but only if the CPE WAN interface is engineered for end-to-end throughput, not just peak modem speed.
    • Multi-Link Operation (MLO): Wi-Fi 7’s signature feature enables simultaneous transmission across multiple frequency bands (2.4 GHz, 5 GHz, 6 GHz). MLO dramatically reduces latency and improves reliability, but it also multiplies the effective traffic load delivered to the CPE WAN port. A single MLO-capable client can generate 5+ Gbps of throughput — requiring careful CPE buffer management and QoS mapping between the Wi-Fi LAN and 5G WAN domains.
    • 4K QAM (4096-QAM): Wi-Fi 7’s higher modulation order achieves 20% greater spectral efficiency compared to Wi-Fi 6’s 1024-QAM. This translates to higher effective throughput at the same range, further raising the bar for CPE WAN interface provisioning.

    The 5G CPE as a Wi-Fi 7 Gateway: Architectural Models

    B2B deployments typically follow one of three integration architectures, each with distinct CPE requirements:

    Model A: Integrated 5G + Wi-Fi 7 CPE (All-in-One)

    For small-to-medium enterprise branches, retail locations, and remote offices, integrated CPE combining 5G NR modem, Wi-Fi 7 AP, and multi-gigabit Ethernet switching in a single device offers the simplest deployment model. Key technical requirements include a 2.5GbE or 10GbE WAN-to-LAN bridge to prevent the CPE’s internal switch fabric from becoming a throughput bottleneck, hardware-accelerated MLO support on the Wi-Fi 7 radio, and unified management plane for both cellular and Wi-Fi domains.

    Model B: 5G CPE as WAN Gateway + Dedicated Wi-Fi 7 APs

    Larger deployments typically separate the 5G WAN termination (CPE) from the Wi-Fi 7 LAN infrastructure for scalability and vendor flexibility. In this model, the 5G CPE functions as a pure WAN gateway, terminating the 5G NR connection and presenting a multi-gigabit Ethernet handoff to downstream Wi-Fi 7 AP controllers or switches. The CPE must support 10GbE SFP+ or 2.5GbE RJ45 WAN-side interfaces, hardware NAT/NAPT at line rate without degrading throughput, and standard routing protocols (BGP, OSPF) for integration with enterprise SD-WAN fabrics.

    Model C: Dual-WAN 5G CPE with Wi-Fi 7 AP Integration

    For business continuity and hybrid WAN scenarios, dual-5G-modem CPE configurations provide carrier diversity with automatic failover. Combined with Wi-Fi 7 MLO, this creates a resilient connectivity stack where both the WAN and LAN layers independently support multi-path operation. The CPE must coordinate failover events with the Wi-Fi 7 controller to prevent client re-association storms when WAN paths change.

    Throughput Engineering: Avoiding the Bottleneck

    The most common failure mode in Wi-Fi 7 + 5G CPE deployments is a throughput mismatch between the LAN and WAN domains. Consider a typical configuration: a Wi-Fi 7 AP with 320 MHz channel in 6 GHz delivering 8 Gbps aggregate throughput, connected to a 5G CPE with a baseband capable of 4 Gbps peak but an Ethernet interface limited to 1GbE. The result: the Wi-Fi 7 investment is wasted because the CPE’s physical interface becomes the bottleneck long before the 5G NR air interface reaches capacity.

    B2B buyers should verify end-to-end throughput across every link in the chain: 5G NR air interface → modem baseband → CPU/NPU forwarding engine → Ethernet PHY → Wi-Fi 7 AP → client device. Each hop must support at least the target service throughput, with headroom for MLO multiplication effects.

    Latency Coordination: 5G URLLC Meets Wi-Fi 7 MLO

    Latency-sensitive enterprise applications — including industrial automation, augmented reality, and real-time collaboration — benefit from coordinated low-latency behavior across both the 5G and Wi-Fi 7 domains. 5G URLLC features (mini-slot scheduling, configured grant transmission) can deliver sub-5ms one-way latency on the WAN side, while Wi-Fi 7 MLO with restricted target wake time (rTWT) can achieve sub-2ms latency on the LAN side. However, these mechanisms operate independently — the CPE must implement intelligent QoS mapping and traffic classification to preserve end-to-end latency guarantees across the WAN-LAN boundary.

    Security Considerations

    Wi-Fi 7 introduces WPA4 (based on WPA3 with enhanced 802.11be protections), which must interoperate with the 5G CPE’s security architecture. For enterprise deployments, this means consistent implementation of 802.1X authentication, RADIUS integration, and certificate-based device identity across both the Wi-Fi LAN and cellular WAN domains. The CPE should function as a policy enforcement point that applies consistent security rules regardless of whether traffic enters via 5G NR or local Wi-Fi 7 association.

    Procurement Checklist for B2B Buyers

    • Verify CPE WAN Ethernet interface supports at least 2.5GbE (preferably 10GbE SFP+) to avoid bottlenecking Wi-Fi 7’s 320 MHz channel throughput
    • Confirm hardware NAT/NP offload capable of line-rate forwarding at multi-gigabit speeds
    • Check for unified management API that exposes both 5G NR and Wi-Fi 7 telemetry to enterprise NMS platforms
    • Ensure MLO-aware QoS mapping between Wi-Fi 7 TID (Traffic Identifier) values and 5G 5QI (5G QoS Identifier) classes
    • Validate WPA4/WPA3-Enterprise interoperability with existing RADIUS/802.1X infrastructure

    At Honlly Telecom, our 5G FWA CPE platforms are engineered with Wi-Fi 7 convergence in mind — featuring 2.5GbE and 10GbE WAN interfaces, hardware-accelerated forwarding, and unified management APIs that bridge the cellular and Wi-Fi domains for enterprise deployers seeking to unlock the full potential of 802.11be without WAN-side compromise.

  • AI/ML-Driven 5G CPE Traffic Optimization: On-Device Intelligence for Predictive QoS, Autonomous Diagnostics, and Real-Time Application Classification in 2026 Enterprise FWA Deployments

    AI/ML-Driven 5G CPE Traffic Optimization: On-Device Intelligence for Predictive QoS, Autonomous Diagnostics, and Real-Time Application Classification in 2026 Enterprise FWA Deployments

    The integration of Artificial Intelligence and Machine Learning (AI/ML) into 5G CPE firmware represents one of the most transformative shifts in FWA device architecture since the transition from LTE to 5G NR. As enterprise networks grow more complex and application traffic becomes increasingly heterogeneous, static QoS configurations and threshold-based monitoring are proving insufficient. The 2026 generation of 5G CPE platforms is embedding AI/ML inference engines directly into the device — enabling real-time traffic classification, predictive bandwidth orchestration, and autonomous fault diagnostics that were previously possible only in cloud-based or core-network analytics systems.

    Why AI/ML Belongs at the CPE Edge

    The traditional model places network intelligence in the 5G core or cloud analytics platform, with CPE devices functioning as relatively passive WAN termination points. This architecture introduces inherent latency in the decision loop: traffic anomalies must traverse the WAN, be analyzed remotely, and trigger policy updates that propagate back to the device — often taking seconds or minutes. For latency-sensitive enterprise applications, this delay is unacceptable.

    Edge AI/ML in the CPE collapses this loop to microseconds. By running lightweight inference models directly on the CPE’s application processor or dedicated NPU (Neural Processing Unit), the device can classify application flows, detect anomalies, and adjust QoS parameters in real time — without depending on cloud connectivity. This is particularly critical for remote sites with intermittent or high-latency backhaul, where cloud-dependent analytics become unreliable precisely when they are most needed.

    Three Core AI/ML Workloads in 5G CPE

    1. Intelligent Traffic Classification and Dynamic QoS

    Traditional CPE QoS relies on static rules — mapping DSCP markings, 5QI values, or port numbers to priority queues. AI/ML-based classification goes further by inspecting traffic patterns in real time and identifying application types based on flow behavior rather than header markings alone. A properly trained model can distinguish between a Microsoft Teams video call (latency-sensitive, moderate bandwidth), a OneDrive file sync (bandwidth-intensive, latency-tolerant), and a SaaS application heartbeat (low volume, keep-alive priority) — even when all three traverse the same encrypted tunnel on the same port.

    This capability is especially valuable for SD-WAN-integrated CPE, where application-aware routing decisions depend on accurate real-time traffic identification. ML models trained on enterprise traffic datasets can achieve >95% application classification accuracy within the first 5-10 packets of a flow, enabling QoS decisions before the application session is fully established.

    2. Predictive Bandwidth Management

    Enterprise WAN traffic follows predictable temporal patterns: video conferencing peaks during business hours, cloud backups run overnight, software updates deploy on schedules. Predictive ML models — typically lightweight LSTM (Long Short-Term Memory) or Transformer-based architectures optimized for embedded deployment — can forecast bandwidth demand 15-60 minutes in advance with high accuracy.

    This foresight enables proactive resource allocation: the CPE can pre-negotiate additional 5G network slices during predicted peak periods, adjust buffer sizes to accommodate expected traffic bursts, or shift non-urgent traffic to off-peak windows. For operators offering tiered FWA services, predictive bandwidth management translates directly to improved SLA compliance and reduced customer churn.

    3. Autonomous Network Diagnostics and Self-Healing

    CPE faults — modem lock-ups, RF interference, SIM authentication failures, DHCP lease expirations — are a major operational cost for managed service providers. AI/ML-driven diagnostics continuously monitor device telemetry (signal strength, SNR, block error rate, temperature, memory utilization, process health) and detect anomaly patterns before they escalate into user-visible outages.

    Advanced implementations go beyond detection to autonomous remediation: when an ML model identifies a degrading RF condition, the CPE can proactively switch to a different 5G band, adjust antenna configuration, or trigger a controlled modem reset during a traffic lull — all without human intervention. Fleet operators deploying thousands of CPE units report 30-50% reductions in truck-roll incidents after implementing on-device ML diagnostics.

    Hardware Requirements for On-Device AI/ML

    Running ML inference at the CPE edge requires hardware considerations that go beyond traditional embedded router specifications:

    • NPU or AI Accelerator: Purpose-built neural processing units — such as those integrated into Qualcomm’s Networking Pro series, MediaTek’s Filogic platforms, or external accelerators like Hailo-8 — provide 2-26 TOPS of INT8 inference performance at sub-5W power envelopes. This is sufficient for running multiple concurrent traffic classification, bandwidth prediction, and anomaly detection models.
    • Memory Footprint: Quantized ML models for CPE applications typically require 50-200 MB of RAM — modest by smartphone standards but significant for embedded router platforms that traditionally ship with 256-512 MB. 2026 CPE designs targeting AI/ML workloads are now shipping with 1-2 GB of LPDDR4/LPDDR5 memory.
    • Model Update Pipeline: On-device models must be updatable via FOTA without service interruption. This requires A/B partitioning of the ML model storage, delta update support, and rollback mechanisms for model version regression.

    Privacy and Data Sovereignty Benefits

    An often-overlooked advantage of edge AI/ML in CPE is data sovereignty. Traffic classification and anomaly detection that run entirely on-device never export raw flow data to the cloud — addressing GDPR, CCPA, and sector-specific compliance requirements in industries like healthcare, finance, and government. The CPE can export anonymized, aggregated telemetry for fleet-level analytics while keeping sensitive per-flow data within the enterprise perimeter.

    The Road Ahead: Generative AI in CPE Management

    Looking beyond 2026, the next frontier is generative AI for CPE configuration and troubleshooting. Natural language interfaces that allow IT administrators to query device status (“Why is Branch 37 experiencing packet loss?”) and receive diagnostic summaries generated by small language models (SLMs) running locally on the CPE are already appearing in vendor roadmaps. This represents a fundamental shift from dashboard-driven management to conversational network operations — and the CPE, as the enterprise’s first touchpoint with the 5G network, is the natural platform for this intelligence.

    At Honlly Telecom, we are embedding AI/ML inference capabilities across our 2026 5G CPE lineup, with hardware-accelerated traffic classification, predictive bandwidth management, and autonomous diagnostics as standard features for enterprise-grade FWA deployments.

  • Cloud-Native TR-369 USP Device Management for Carrier-Grade 5G CPE: Migrating from TR-069

    Cloud-Native TR-369 USP Device Management for Carrier-Grade 5G CPE: Migrating from TR-069

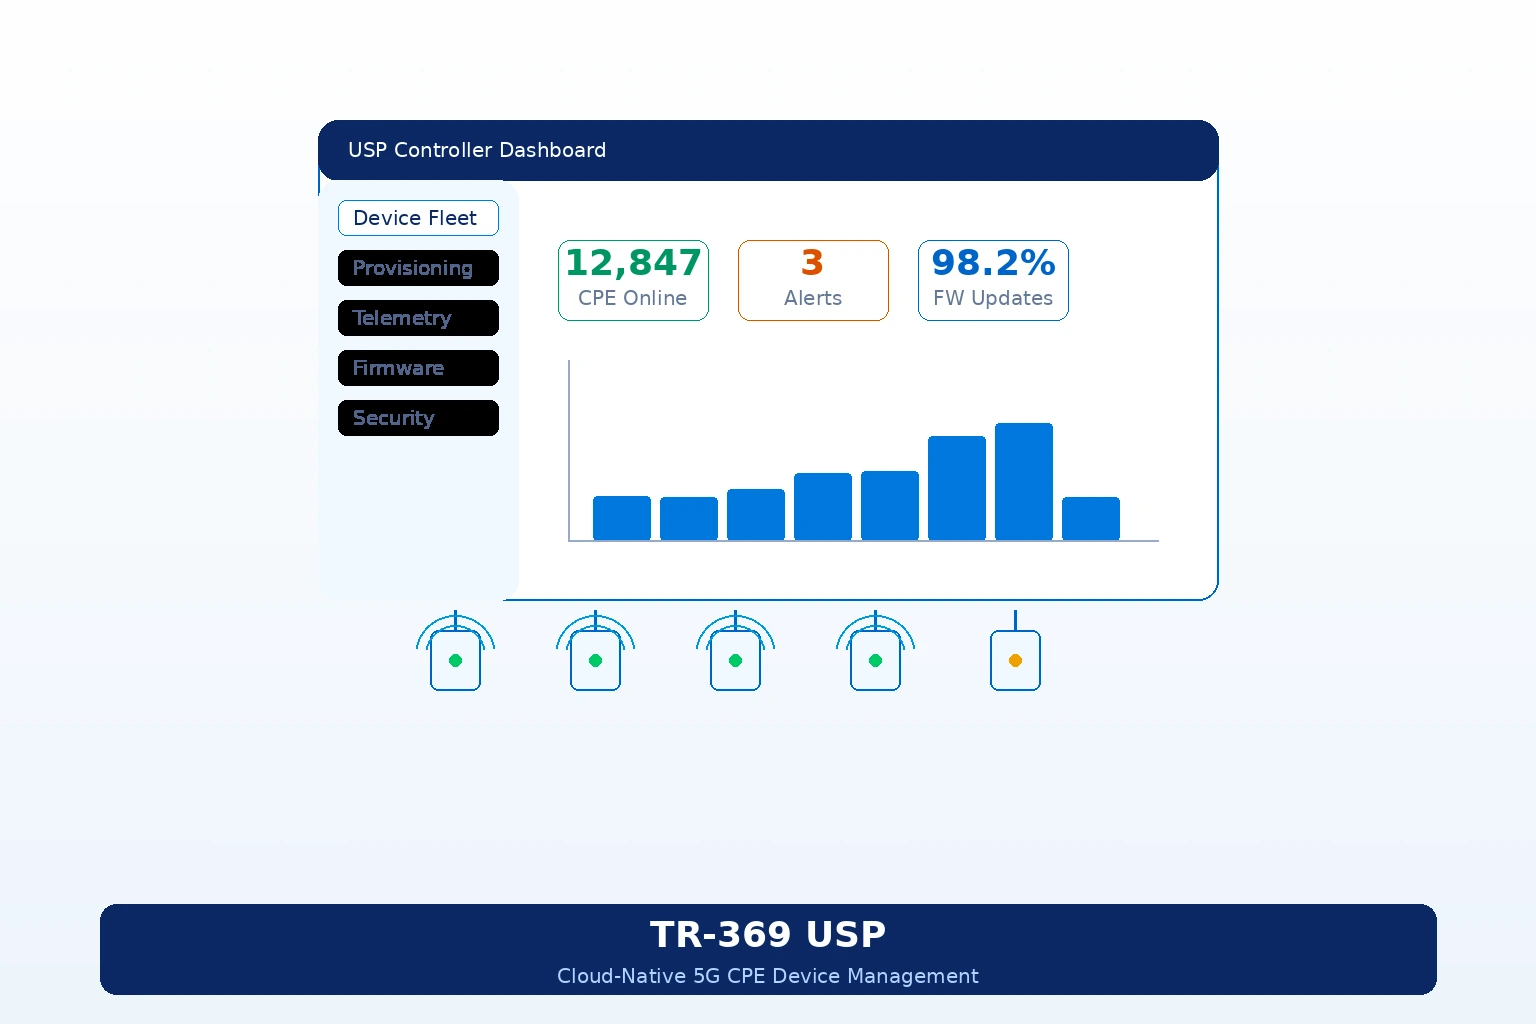
    For over 15 years, TR-069 (CPE WAN Management Protocol, or CWMP) has been the workhorse of broadband device management, enabling operators to remotely configure, monitor, and troubleshoot millions of CPE devices. But as 5G networks push toward cloud-native, microservices-based operations, TR-069’s SOAP/XML foundations and rigid client-server architecture are showing their age. The Broadband Forum’s TR-369 USP (User Services Platform) — commonly referred to as USP — is the designated successor, and operator migration timelines are accelerating through 2026.

    Why TR-069 Is Reaching Its Limits in the 5G Era

    TR-069 was designed in the DSL era and optimized for intermittent connectivity, low-bandwidth management traffic, and centralized ACS (Auto Configuration Server) architectures. In modern 5G FWA deployments, several limitations have become critical:

    • Connection-oriented polling: TR-069 relies on periodic CPE-initiated sessions (Periodic Inform) or ACS-triggered Connection Requests. In 5G networks with NAT44/NAT64/CGNAT traversal, Connection Requests frequently fail or require STUN-based workarounds that add latency.
    • SOAP/XML overhead: Each TR-069 transaction wraps parameter values in multiple layers of SOAP envelope, XML namespace declarations, and CWMP method framing. For bulk parameter queries across thousands of CPEs, this overhead is computationally expensive on both the ACS and CPE sides.
    • Limited concurrency model: TR-069 sessions are single-threaded per CPE. Simultaneous configuration changes, firmware downloads, and diagnostics require sequential session handling, creating bottlenecks in large-scale operations.
    • No native push-notification architecture: CPE-originated events (alarms, threshold breaches, connectivity changes) are batched into the next Periodic Inform interval rather than delivered in real time — a significant operational gap for carrier-grade 5G FWA.

    TR-369 USP: Architecture and Key Capabilities

    TR-369 USP fundamentally rearchitects the device-management paradigm around three principles: message-oriented communication, multi-protocol transport, and service-based abstraction.

    USP Message Architecture

    USP uses a compact, binary-encoded message format (Protocol Buffers, or protobuf) transported over WebSocket, MQTT, STOMP, or CoAP — a dramatic departure from TR-069’s HTTP/1.1 + SOAP/XML stack. Each USP message carries:

    • Header: Message ID, message type (Get, Set, Add, Delete, Operate, Notify), source/destination endpoint identifiers.
    • Body: A Request/Response or Notification payload, encoded in protobuf with strong typing and schema validation.
    • Record-level integrity: USP supports per-message digital signatures (using JWS) and TLS 1.3 mutual authentication, meeting carrier security requirements without the XML Signature overhead of TR-069.

    Multi-Protocol Transport and Always-On Connectivity

    Unlike TR-069’s session-based HTTP model, USP supports persistent connections via WebSocket, enabling:

    • Real-time push notifications: CPE events (link status changes, throughput threshold alarms, security incidents) are pushed to the controller in real time, enabling proactive network operations.
    • Bidirectional command flow: The controller can send configuration commands to the CPE at any time without waiting for a Connection Request cycle or Periodic Inform window.
    • MQTT integration: For operators with existing MQTT-based IoT or telemetry infrastructure, USP agents can connect directly to MQTT brokers, unifying CPE management with broader IoT device management under a single message bus.

    USP Data Model: TR-181 Device:2 and Service Objects

    USP reuses the TR-181 Device:2 data model (already familiar from TR-069) but extends it with service objects that map directly to 5G-specific management domains:

    • Device.WiFi.* objects for Wi-Fi 6/6E/7 radio, SSID, and band steering configuration.
    • Device.Cellular.* objects for 5G NR modem status, PLMN selection, band locking, carrier aggregation state, and signal quality metrics (RSRP, RSRQ, SINR per component carrier).
    • Device.Firewall.*, Device.Routing.*, Device.QoS.* for advanced networking configuration.
    • Device.BulkData.* for throughput and latency telemetry streaming (IPFIX-based).
    • Device.SoftwareModules.* for containerized firmware component management (DU, CU separation in multi-component CPE architectures).

    Migration Path: From TR-069 ACS to USP Controller

    Most operators cannot execute a “big-bang” replacement of their TR-069 infrastructure. The Broadband Forum anticipates a 3-5 year coexistence period during which CPE fleets will include a mix of TR-069-only, USP-only, and dual-stack devices. The recommended migration strategy includes:

    Phase 1: USP Controller Deployment with TR-069 Proxy (2026)

    Deploy a USP Controller that also implements a TR-069 southbound proxy (or integrates with the existing ACS via northbound APIs). This enables:

    • Unified operator dashboards that query and configure both TR-069 and USP CPE through a single interface.
    • Gradual CPE replacement or firmware upgrade without service disruption on legacy devices.
    • Parallel monitoring of Key Performance Indicators (KPIs) across protocol generations.

    Phase 2: Dual-Stack CPE with USP Preference (2026-2027)

    Procure or upgrade CPE firmware to support both TR-069 and USP agents simultaneously, with USP as the preferred management channel and TR-069 as fallback. New CPE should:

    • Register with both the legacy ACS and the new USP Controller on initial boot.
    • Accept configuration changes through either channel, with USP taking precedence when both attempt to modify the same parameter.
    • Report telemetry and events through USP while maintaining TR-069 Inform-based health checks for backward compatibility.

    Phase 3: TR-069 Decommissioning (2027-2028)

    Once the USP Controller demonstrates equivalent or superior operational KPIs (provisioning success rate, alarm delivery latency, bulk configuration throughput), operators can begin phasing out TR-069 ACS infrastructure. Legacy CPE that cannot be upgraded should be targeted for replacement as part of natural hardware refresh cycles (typically 3-5 years for FWA CPE).

    Operational Benefits of USP Migration

    Operators who have completed pilot USP deployments report significant operational improvements:

    • Provisioning time reduction: Bulk configuration of 10,000 CPEs completes in minutes rather than hours, thanks to USP’s concurrent message processing and protobuf’s compact encoding (typically 5-10x smaller than equivalent SOAP/XML payloads).
    • Real-time alarm response: CPE-originated alarms (5G signal degradation, WAN link failure, security intrusion detection) arrive at the NOC in under 5 seconds rather than the 5-15 minute Periodic Inform window, enabling faster mean-time-to-resolution (MTTR).
    • Firmware upgrade success rates: USP’s segmented file transfer with integrity verification and resume capability improves firmware upgrade success rates in lossy 5G environments compared to TR-069’s monolithic HTTP download model.
    • Cloud-native integration: USP Controller implementations built on Kubernetes and Kafka integrate natively with operator DevOps toolchains (CI/CD pipelines, Prometheus/Grafana monitoring, ELK logging), reducing operational overhead compared to monolithic ACS appliances.

    Selecting a USP Stack: Build vs. Buy

    Operators have several options for USP infrastructure:

    • Open-source USP Controller (OB-USP-Agent + OB-USP-Controller): The Broadband Forum’s reference implementations provide a solid starting point. Suitable for operators with in-house CPE management development teams who want full customization.
    • Commercial USP platforms: Vendors including Axiros, Friendly Technologies, Incognito, and AVSystem offer carrier-grade USP Controllers with TR-069 coexistence, multi-tenancy, and integration with existing OSS/BSS. Typically the faster path to production for operators without large in-house CPE management teams.
    • CPE vendor-managed USP: Some CPE manufacturers (including Honlly Telecom) provide USP agent firmware and can host managed USP Controller instances, offering a turnkey device management solution for smaller operators and MVNOs.

    USP Agent Requirements for 5G FWA CPE

    When evaluating and procuring 5G FWA CPE with USP support, operators should verify the following agent capabilities:

    • USP 1.3+ compliance with WebSocket and MQTT transport support.
    • TR-181 Device:2.16+ data model support including Cellular interface extensions for 5G NR (NRCell, NRCarrier, ENDC combination status).
    • TLS 1.3 with mutual authentication using device certificates (SMI or operator PKI issued).
    • Bulk data collection (BulkData object) with configurable reporting intervals for throughput, latency, and signal quality telemetry.
    • Firmware upgrade with USP segmented download and digital signature verification.
    • Concurrent session support for simultaneous configuration and monitoring operations.
    • TR-069 coexistence mode (dual-agent) for migration-phase deployments.

    Conclusion

    The migration from TR-069 to TR-369 USP is not merely a protocol upgrade — it is a fundamental shift toward cloud-native, event-driven device management that aligns 5G FWA CPE operations with modern carrier infrastructure. Operators who begin their USP migration in 2026 will be well-positioned to exploit real-time telemetry, automated service orchestration, and containerized firmware management as their 5G FWA subscriber bases scale through the end of the decade.

    For operators planning 5G FWA CPE deployments, specifying TR-369 USP support in procurement RFPs today ensures that device fleets deployed in 2026-2027 will support the management architecture carriers will operate through 2030 and beyond.


    Honlly Telecom’s 5G FWA CPE platforms support TR-369 USP with TR-069 coexistence. Contact our solutions team to discuss USP integration for your device fleet.

  • eSIM Integration in 5G FWA CPE: A Technical Guide for Operators Deploying Remote SIM Provisioning

    eSIM Integration in 5G FWA CPE: A Technical Guide for Operators Deploying Remote SIM Provisioning

    The GSMA estimates that by 2027, over 4 billion eSIM-capable devices will be in circulation globally. While smartphones have dominated early eSIM adoption, the fixed wireless access (FWA) CPE segment is emerging as one of the most compelling use cases for embedded SIM technology. For operators and MVNOs deploying 5G FWA at scale, eSIM integration transforms device logistics, reduces churn, and enables new service models that physical SIM cards cannot support.

    Why eSIM Matters for 5G FWA CPE

    Traditional physical SIM deployment in FWA CPE creates multiple operational friction points:

    • Logistics overhead: Physical SIM cards must be manufactured, inventoried, shipped, inserted, and activated — a process that adds days or weeks to subscriber onboarding.
    • SIM swap complexity: When a subscriber changes operators or plans, a physical SIM replacement requires either a truck roll or customer self-service, introducing service disruption and cost.
    • Single-IMSI limitation: A physical SIM typically carries one profile, locking the CPE to a single operator unless multi-IMSI applets are pre-provisioned — which adds cost and complexity.
    • Device return and refurbishment: Recovered CPE units often have outdated or operator-locked SIMs, complicating refurbishment and redeployment workflows.

    eSIM (embedded UICC, or eUICC) addresses all of these challenges through remote SIM provisioning (RSP), enabling operators to download, activate, switch, and delete SIM profiles over the air — without any physical intervention on the CPE.

    GSMA eSIM Architecture for Consumer and M2M Devices

    The GSMA defines two primary eSIM architectures, each relevant to different FWA CPE deployment scenarios:

    Consumer Architecture (GSMA SGP.22)

    The SGP.22 (RSP Technical Specification v3.x) consumer architecture is increasingly the preferred model for FWA CPE because it empowers the end-user — or in B2B contexts, the enterprise IT administrator — to manage profiles. Key components include:

    • LPA (Local Profile Assistant): A software component running on the CPE that manages profile download, enabling, disabling, and deletion. The LPA interfaces with the SM-DP+ (Subscription Manager Data Preparation) server via HTTPS.
    • SM-DP+: The operator-side server that securely packages and delivers profiles to the eUICC.
    • SM-DS (Discovery Server): Optional push-notification infrastructure that alerts the LPA when a new profile is available for download.
    • eUICC (embedded UICC): The hardware secure element (typically a MFF2 or WLCSP soldered chip) that stores multiple operator profiles.

    In a typical FWA deployment flow: the operator provisions a profile on the SM-DP+, sends an activation code (or SM-DS event) to the CPE, the LPA downloads and installs the profile, and the eUICC switches to the new profile — all within seconds and without physical interaction.

    M2M Architecture (GSMA SGP.02)

    The older SGP.02 M2M architecture uses a push model where the operator’s SM-SR (Subscription Manager Secure Routing) server directly controls profile operations on the eUICC. While less flexible than SGP.22, SGP.02 remains relevant for managed-service FWA deployments where the operator wants complete control over profile lifecycle without any LPA dependency on the CPE.

    eSIM Hardware Integration in 5G FWA CPE

    Integrating eSIM into a 5G CPE design involves several hardware and firmware considerations:

    eUICC Form Factors

    • MFF2 (QFN-8): The most common eUICC package for CPE, measuring 5x6mm. Widely available from Infineon, STMicroelectronics, and Thales, with GSMA SAS-UP certification. Compatible with standard SMD assembly processes.
    • WLCSP (Wafer-Level Chip-Scale Package): Smaller footprint (approximately 2.5×2.5mm), suitable for compact CPE such as MiFi hotspots. Higher integration complexity but better thermal characteristics.
    • iSIM (Integrated SIM): The next evolution where eUICC functionality is integrated directly into the modem SoC die (e.g., Qualcomm’s Snapdragon X80 with integrated iSIM support on select SKUs). iSIM eliminates the discrete eUICC component entirely, reducing BOM cost and board area.

    Profile Storage and Multi-IMSI

    Modern eUICCs for 5G CPE typically support 2-5 simultaneously stored profiles, with one active at a time. For operators offering multi-country or multi-network FWA services, this enables:

    • Home + Roaming profiles: A primary profile for the home network and a secondary profile for partner-network roaming, with automatic switching based on PLMN availability.
    • Failover profiles: A backup profile from a different MNO that activates automatically if the primary network experiences an outage, enabling carrier-grade FWA resilience.
    • Test-to-production migration: Pre-loaded test profiles that can be remotely replaced with production profiles after device installation and network verification.

    RSP Integration Architecture for Carrier-Grade CPE

    At the CPE firmware level, eSIM integration requires:

    1. LPA implementation: An SGP.22-compliant LPA daemon that handles profile download (ES9+, ES11 interfaces), profile management (ES10x interfaces), and SM-DS event listening. For Linux-based CPE (OpenWrt, RDK-B, prplOS), LPAd open-source implementations are viable starting points but require security hardening for carrier deployment.
    2. Modem-eUICC interface: The ISO 7816 interface between the modem baseband processor and the eUICC, with support for the increased APDU throughput required by 5G NR authentication procedures.
    3. TR-069 / TR-369 remote management integration: Operators managing large CPE fleets need to trigger profile operations through their existing device management platforms. This requires extending the TR-069/TR-369 data model with eSIM-specific parameters and RPCs for profile download, activation, and status reporting.
    4. Secure boot and TEE integration: The LPA and eUICC communication path must be protected against tampering. A Trusted Execution Environment (TEE) is strongly recommended for storing LPA credentials and protecting the eUICC-ISD-R communication channel.

    Operator Benefits: Operational and Commercial

    Reduced subscriber acquisition cost: Zero-touch provisioning eliminates physical SIM logistics. CPE can be drop-shipped directly from the manufacturer (or distributor) to the end user, with profile download triggered on first power-on — reducing time-to-service from days to minutes.

    Churn reduction via multi-profile stickiness: A CPE with multiple eSIM profiles creates a switching-cost barrier. Even if a subscriber considers changing their primary operator, the convenience of managing all profiles on one device — and the perceived complexity of re-provisioning — reduces churn rates.

    New wholesale and MVNO models: eSIM enables dynamic wholesale: an infrastructure operator can pre-integrate profiles from multiple retail MVNO partners, allowing enterprise customers to select (and switch between) service providers through a self-service portal — without any CPE hardware change.

    Refurbishment and circular economy: When a CPE is returned, the operator can remotely delete all profiles and provision a new one for the next subscriber in minutes, dramatically reducing device turnaround time and enabling CPE-as-a-Service rental models.

    Current Challenges and Mitigations

    Despite its advantages, eSIM deployment in 5G FWA CPE faces several real-world challenges:

    • SM-DP+ interoperability: Not all SM-DP+ implementations handle FWA CPE profile downloads identically. Operators should validate profile download success rates across their SM-DP+ vendor and target CPE models during lab testing, not after field deployment.
    • Regulatory variance: Some markets (e.g., India, certain Middle Eastern countries) have regulatory restrictions on remote SIM provisioning or eSIM profile switching that differ from GSMA norms. Local legal review is essential before launching eSIM-based FWA services.
    • LPA maturity on embedded Linux: LPAd implementations for OpenWrt and similar CPE operating systems are less mature than their Android counterparts. Operators should budget for LPA integration and testing effort when evaluating eSIM-capable CPE.
    • Legacy OSS/BSS integration: Existing operational support systems designed for physical SIM lifecycle management may require adaptation to handle eSIM profile inventory, activation codes, and state transitions.

    Recommendations for Operators

    For operators planning 5G FWA CPE deployments in 2026-2027:

    1. Specify eSIM readiness in procurement RFPs: Require SGP.22 consumer architecture compliance as a minimum, with iSIM readiness as a forward-looking preference. Include LPA integration with TR-369 USP as a firmware requirement.
    2. Select an SM-DP+ provider early: Entrust, Thales, G+D, Idemia, and Workz all offer SM-DP+ platforms. Early engagement ensures profile packaging compatibility with your chosen CPE vendor’s LPA implementation.
    3. Run multi-vendor interoperability testing: Test profile download, activation, switching, and deletion across all CPE models, SM-DP+ platforms, and network configurations in your deployment plan.
    4. Plan for iSIM migration: If your CPE roadmap extends into 2027-2028, engage with modem vendors (Qualcomm, MediaTek) on iSIM-integrated SoC availability to further reduce BOM and simplify supply chain.

    As eSIM and iSIM technology mature, the business case for operators to transition from physical SIM to embedded SIM in 5G FWA CPE becomes increasingly compelling. Early adopters who build eSIM RSP infrastructure today will be positioned to capture the operational and commercial advantages that remote provisioning delivers at scale.


    Honlly Telecom offers 5G FWA CPE with eSIM-ready hardware platforms. Contact our engineering team to discuss eSIM integration requirements for your deployment.

  • IPv6 Transition Strategies for 5G FWA CPE: Dual-Stack, 464XLAT, and What B2B Buyers Need to Know in 2026

    IPv6 Transition Strategies for 5G FWA CPE: Dual-Stack, 464XLAT, and What B2B Buyers Need to Know in 2026

    The IPv4 address space is effectively exhausted. All five RIRs (Regional Internet Registries) have reached their final /8 allocations, and the secondary IPv4 transfer market now prices individual addresses at $40–55 USD. For 5G Fixed Wireless Access (FWA) operators deploying CPE at scale — tens of thousands to millions of units — the economics of IPv4 scarcity directly impact CAPEX and network architecture decisions. IPv6 transition is no longer optional: it is a procurement-critical requirement for FWA CPE in 2026.

    This guide examines the IPv6 transition mechanisms relevant to 5G FWA CPE, their architectural trade-offs, and what B2B buyers must evaluate when selecting gateway equipment for large-scale deployments.

    Why IPv6 Matters for 5G FWA Specifically

    5G FWA networks have characteristics that make IPv6 transition both more urgent and more complex than traditional broadband:

    • Scale: FWA operators routinely deploy 100,000+ CPE units. At $45/IPv4 address, a public IPv4 address per CPE adds $4.5 million to the address budget alone — before considering NAT gateway infrastructure.
    • 3GPP Standards: 5G core networks are natively IPv6. The 5G user plane function (UPF) supports IPv6 PDU sessions as a baseline requirement, and many 5G SA deployments are IPv6-only at the transport layer.
    • Enterprise Services: FWA is increasingly sold as a primary business-grade connection, not just residential broadband. Enterprise customers expect public IP addresses, static addressing, and end-to-end transparency — requirements that CGNAT struggles to meet.
    • IoT and Slicing: Network slicing in 5G SA can assign dedicated IPv6 prefixes per slice, enabling clean address separation for different enterprise services without overlapping RFC 1918 space.

    IPv6 Transition Mechanisms for CPE

    1. Dual-Stack (Native IPv4 + Native IPv6)

    Dual-stack is the simplest transition model: the CPE receives both an IPv4 address (public or CGNAT) and an IPv6 prefix, typically via DHCPv6 Prefix Delegation. All endpoints on the LAN get both IPv4 and IPv6 addresses, and the CPE routes traffic accordingly.

    Advantages: Maximum compatibility. All applications, legacy and modern, work without translation overhead. No DNS64/NAT64 infrastructure required.

    Disadvantages: Does not solve IPv4 exhaustion — each CPE still consumes at least one IPv4 address (even if CGNAT). Doubles the routing table and firewall rule complexity on the CPE. Not a long-term scaling solution for operators targeting millions of subscribers.

    CPE requirements: Dual-stack IP stack, DHCPv6-PD client, IPv6 router advertisement daemon, dual-stack DNS proxy, and dual-stack firewall with stateful inspection for both protocols.

    2. 464XLAT (IPv4-as-a-Service over IPv6-Only Access)

    464XLAT is the transition mechanism deployed at scale by T-Mobile US, Reliance Jio, and several other major mobile/FWA operators. It enables IPv4 application connectivity over an IPv6-only network by combining two components:

    • CLAT (Customer-side translator): Runs on the CPE. Translates IPv4 packets from LAN devices into IPv6 packets using Stateless IP/ICMP Translation (SIIT, RFC 7915). The CLAT synthesizes IPv6 addresses for IPv4 destinations using the operator’s NAT64 prefix (typically a /96 Well-Known Prefix 64:ff9b::/96 or an operator-specific prefix).
    • PLAT (Provider-side translator): Runs in the operator’s core network. A stateful NAT64 gateway that translates the IPv6-encapsulated packets back to IPv4 for communication with the IPv4 internet.

    How it works for the end user: The CPE receives only an IPv6 address/prefix from the network. LAN devices get IPv6 addresses normally. When an IPv4-only application (e.g., a legacy IP camera, older IoT sensor, or IPv4-only enterprise VPN client) attempts to send an IPv4 packet, the CLAT on the CPE translates it to IPv6 on the fly. The PLAT in the core network handles the IPv6-to-IPv4 translation at the internet edge.

    Advantages: No IPv4 addresses needed on the CPE or access network. Proven at massive scale (hundreds of millions of devices on T-Mobile’s network). Transparent to IPv4 applications.

    Disadvantages: Adds translation overhead. Breaks applications that embed IPv4 literals in payloads (FTP, SIP, some gaming protocols). Requires operator-side NAT64/PLAT infrastructure. Debugging can be complex due to address translation layers.

    CPE requirements: CLAT daemon (typically clatd on Linux-based CPE, or vendor-proprietary implementation), DNS64 support (synthesizes AAAA records for IPv4-only destinations), and awareness of the operator’s NAT64 prefix (learned via RFC 7050 or DHCPv6 option).

    3. MAP-T (Mapping of Address and Port with Translation)

    MAP-T (RFC 7599) is a stateless IPv4-over-IPv6 transition mechanism that avoids the stateful NAT64 infrastructure required by 464XLAT. Instead, it uses algorithmic mapping: each CPE is assigned a specific IPv4 address (or shared address) and a set of TCP/UDP port ranges, algorithmically embedded into an IPv6 prefix.

    Advantages: Stateless core — no carrier-grade NAT64 state tables to maintain. Deterministic port mapping simplifies troubleshooting and lawful intercept compliance. Full IPv4 transparency without NAT44 on the CPE.

    Disadvantages: Requires each CPE to have a share of IPv4 address space (even if port-restricted). More complex provisioning. Less widely deployed than 464XLAT. Port range restrictions can limit concurrent connections for heavy-use subscribers.

    4. IPv6-Only with DNS64/NAT64 (No CLAT on CPE)

    In this model, the CPE is purely IPv6 — no IPv4 stack at all on the WAN or LAN side. IPv4 connectivity is provided entirely by the operator’s DNS64/NAT64 infrastructure. IPv4-addressed destinations are reached by synthesizing AAAA records through DNS64, and traffic is translated by the operator’s NAT64 gateway.

    This is the most aggressive transition model and is suitable for greenfield deployments where all endpoint devices and applications are IPv6-capable. It is not yet practical for most B2B FWA deployments due to legacy application dependencies.

    CPE Procurement Checklist for IPv6 Transition

    When evaluating FWA CPE for IPv6-ready deployments, B2B buyers should verify the following capabilities:

    Capability Why It Matters
    DHCPv6 Prefix Delegation (IA_PD)Required for the CPE to receive an IPv6 prefix from the operator and delegate subnets to LAN devices
    CLAT Support (RFC 6877)Essential if the operator runs an IPv6-only access network with 464XLAT
    DNS64 Awareness (RFC 7050)CPE must discover the NAT64 prefix and use it for IPv4-embedded IPv6 address synthesis
    IPv6 Firewall with Stateful InspectionMust provide equivalent security to IPv4 firewall, including DDoS protection and access control
    Dual-Stack or IPv6-Only WAN OptionFlexibility to deploy in dual-stack today and migrate to IPv6-only/464XLAT in the future
    MAP-T Support (RFC 7599)Required if the operator uses MAP-T rather than 464XLAT for stateless IPv4aaS
    TR-069 / TR-369 IPv6 ManagementRemote management must work over IPv6 transport; CPE must be reachable via IPv6 ACS

    Regional IPv6 Deployment Trends for FWA

    Asia-Pacific: India leads globally with over 75% IPv6 adoption, driven by Reliance Jio’s IPv6-only mobile and FWA network. Japan and South Korea report 45–55% IPv6 usage. APAC FWA buyers should prioritize 464XLAT-ready CPE.

    North America: T-Mobile US operates one of the world’s largest 464XLAT deployments for its FWA service, with over 5 million FWA subscribers. The US federal government’s IPv6 mandate (OMB M-21-07) requires all federal agencies to operate at least 80% IPv6-only by 2025, accelerating enterprise IPv6 demand.

    Europe: RIPE NCC’s IPv6 adoption rate sits at approximately 35–40%, with strong operator support from Deutsche Telekom, BT, and Orange. European operators tend to prefer dual-stack with gradual migration to MAP-T rather than aggressive 464XLAT.

    Middle East & Africa: IPv6 adoption remains below 10% in most markets. FWA operators in these regions have a unique opportunity to deploy greenfield IPv6-only networks and leapfrog the IPv4 exhaustion problem entirely — if they select the right CPE.

    Latin America: Brazil and Mexico lead with 35–45% IPv6 adoption. Several Brazilian ISPs use MAP-T for FWA IPv4 address sharing, making MAP-T CPE support a procurement requirement in that market.

    Business Case: IPv6-Native CPE Reduces TCO

    A TCO analysis for a hypothetical operator deploying 200,000 FWA CPE units illustrates the economic case:

    • Dual-stack with CGNAT: ~$2M for CGNAT infrastructure + $500K/year for IPv4 address leasing (10,000 public addresses at $50 each, with CGNAT sharing ratio of 20:1). CPE cost: baseline. Total 5-year TCO: ~$4.5M.
    • 464XLAT IPv6-only: $1.2M for NAT64/PLAT infrastructure + $0 for IPv4 addresses. CPE cost: +$3–5/unit for CLAT-capable firmware. Total 5-year TCO: ~$2.2M — roughly 50% savings.

    For operators deploying at scale, the savings from IPv6-native CPE architectures are compelling and rapidly recover any incremental CPE hardware cost.

    Frequently Asked Questions

    Can IPv6-only CPE support IPv4-only enterprise VPN clients?

    It depends on the VPN protocol. IPsec IKEv2 with IPv6 transport works natively. SSL/TLS-based VPNs (OpenVPN, WireGuard) also work when the VPN endpoint is reachable over IPv6. However, legacy IPsec clients that rely on IPv4 transport may require 464XLAT or dual-stack fallback.

    What happens to IPv4-only IoT devices on an IPv6-only FWA network?

    The CLAT on the CPE handles IPv4-to-IPv6 translation for LAN-originated IPv4 traffic. IPv4-only IoT devices on the LAN will function normally, as the CPE presents a standard IPv4 DHCP server and gateway address to the LAN, while translating traffic to IPv6 on the WAN side.

    Is 464XLAT compatible with all 5G FWA bands?

    Yes. 464XLAT operates at the IP layer and is independent of the radio access technology. It works identically over 5G NR, 4G LTE, and even Wi-Fi backhaul.

    Does IPv6 impact CPE throughput performance?

    Negligible impact. The CLAT translation overhead is typically under 1% of CPU utilization on modern CPE SoCs. In some cases, IPv6-only paths can actually improve throughput by eliminating CGNAT processing latency in the core network.

    Evaluating IPv6-ready FWA CPE for your network deployment? Contact Honlly Telecom to discuss your IPv6 transition strategy with our solutions architects.

  • Open RAN and Multi-Vendor CPE Interoperability: A Procurement Guide for Operators Deploying O-RAN Compliant FWA Gateways in 2026

    Open RAN and Multi-Vendor CPE Interoperability: A Procurement Guide for Operators Deploying O-RAN Compliant FWA Gateways in 2026

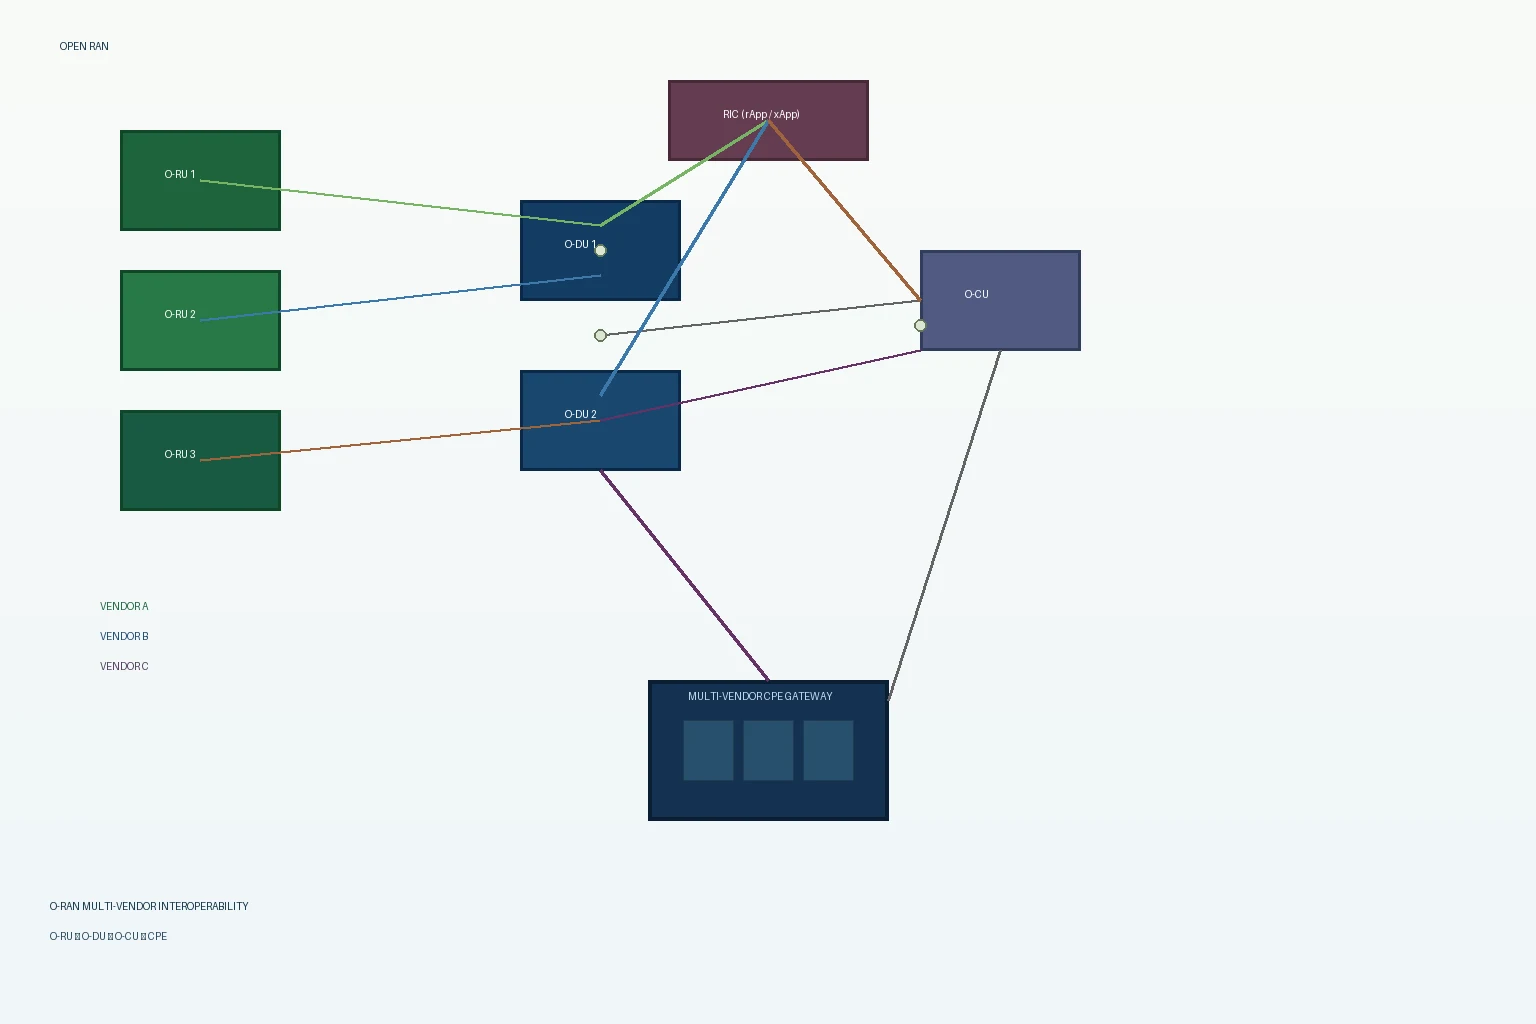
    Open RAN (O-RAN) represents the most significant architectural shift in radio access networks since the transition from 2G to 3G. By disaggregating the RAN into standardized, interoperable components — radio units (O-RU), distributed units (O-DU), and centralized units (O-CU) — Open RAN enables operators to mix and match equipment from multiple vendors rather than being locked into a single supplier’s end-to-end stack.

    For Fixed Wireless Access (FWA) operators, this architectural openness extends to Customer Premises Equipment. As O-RAN deployments scale globally — with over 45 commercial O-RAN networks now in operation and cumulative investments exceeding $15 billion — CPE interoperability has become a critical procurement consideration. This guide examines the standards, testing frameworks, and strategic considerations for B2B buyers evaluating O-RAN compliant FWA gateways.

    The O-RAN Alliance and CPE Relevance

    The O-RAN Alliance, founded in 2018 by AT&T, China Mobile, Deutsche Telekom, NTT DOCOMO, and Orange, now includes over 300 member organizations. While O-RAN specifications primarily focus on the RAN infrastructure (O-RU, O-DU, O-CU, RIC), several working groups produce specifications that directly impact CPE design and interoperability:

    • WG4 (Open Fronthaul): Defines the interface between O-RU and O-DU. While CPE does not connect at this interface, fronthaul architecture choices (split 7.2x vs split 8) affect CPE-visible parameters like timing alignment and beamforming coordination.
    • WG7 (White-box Hardware): Publishes reference designs for white-box hardware, including indoor and outdoor radio units. Some WG7 design principles — particularly around thermal management, power efficiency, and modular architecture — influence CPE hardware design.
    • WG8 (Stack Reference Design): Defines reference software stacks for O-DU and O-CU. CPE protocol stacks must interoperate with multi-vendor implementations of these reference designs.
    • WG11 (Security): Defines security requirements for O-RAN components, including zero-trust principles that extend logically to CPE authentication and secure boot.

    How Open RAN Changes CPE Interoperability Requirements

    In a traditional single-vendor RAN, the CPE is typically validated against one implementation of the 3GPP protocol stack — the RAN vendor’s proprietary implementation. Interoperability testing is simplified because both the network side and the CPE side are developed, tested, and optimized together.

    In an O-RAN environment, the CPE may need to interoperate with:

    • O-RUs from Vendor A (e.g., NEC, Fujitsu, Comba)
    • O-DUs from Vendor B (e.g., Mavenir, Parallel Wireless, Rakuten Symphony)
    • O-CUs from Vendor C (e.g., Nokia, Ericsson, Samsung — all of which now offer O-RAN compliant CU software)
    • RIC (RAN Intelligent Controller) from Vendor D
    • Core network from Vendor E

    This multi-vendor environment introduces interoperability challenges that single-vendor RANs avoid. CPE must be validated against a matrix of possible RAN component combinations, not just one stack.

    Key CPE Capabilities for O-RAN Environments

    1. 3GPP Standards Compliance — Beyond the Minimum

    While all 5G CPE must comply with 3GPP Release 15+ UE specifications, O-RAN environments demand stricter adherence. Single-vendor RANs may tolerate minor deviations from the standard because the vendor controls both sides of the air interface. In multi-vendor O-RAN, every deviation is a potential interoperability failure point.

    B2B buyers should verify that CPE has been tested against ATIS or ETSI-defined 3GPP conformance test suites — specifically TS 38.521 (UE RF conformance), TS 38.523 (UE protocol conformance), and TS 38.533 (UE RRM conformance).

    2. Beam Management and Mobility in Multi-Vendor Deployments

    Beam management procedures — including initial beam acquisition, beam failure detection, and beam failure recovery — must work correctly across O-RUs from different vendors. In a single-vendor deployment, the gNB and CPE may use vendor-optimized beam codebooks that implicitly share assumptions. In O-RAN, the CPE must handle standard-compliant beam management with O-RUs that may implement different beam-sweeping patterns and SSB configurations.

    3. RAN Slicing Awareness

    O-RAN’s RIC enables dynamic RAN slicing — allocating different radio resources to different network slices serving different enterprise customers or service types. CPE that is slice-aware can request and utilize dedicated RAN slices for specific traffic types (e.g., a dedicated slice for industrial automation vs. best-effort internet).

    CPE should support NSSAI (Network Slice Selection Assistance Information) signaling in RRC and NAS layers, enabling the device to request specific slices and accept slice-specific PDU sessions.

    4. O-RAN Security Requirements

    O-RAN WG11 defines security requirements including mutual TLS (mTLS) for all O-RAN interfaces, secure boot with hardware root of trust, and continuous integrity monitoring. CPE deployed in O-RAN environments should provide equivalent security capabilities: hardware-backed secure boot, TPM-backed key storage, signed firmware updates, and certificate-based device authentication on the network.

    Multi-Vendor Interoperability Testing Frameworks

    Several industry initiatives provide interoperability testing infrastructure for O-RAN components, including CPE:

    • O-RAN Alliance OTIC (Open Testing and Integration Centers): Currently 15 OTICs operate globally, including facilities in Berlin, Tokyo, Beijing, Bangalore, and the United States. OTICs provide conformance, interoperability, and end-to-end testing for O-RAN equipment.
    • Telecom Infra Project (TIP) Community Labs: TIP operates testing facilities focused on open and disaggregated network equipment, with specific test cases for CPE interoperability.
    • NTIA/ITS O-RAN Test Lab (US): Funded by the US NTIA’s $1.5 billion Public Wireless Supply Chain Innovation Fund, this facility provides independent O-RAN testing for equipment vendors seeking US market access.

    B2B buyers should request OTIC or equivalent test reports demonstrating CPE interoperability with their specific O-RAN component mix before committing to volume procurement.

    Procurement Strategies for O-RAN FWA CPE

    Strategy 1: Pre-Validated Bundles

    Several system integrators (including Rakuten Symphony, Mavenir, and NEC) now offer pre-validated O-RAN bundles that include specific CPE models tested against their RAN stack. This approach reduces integration risk but may limit CPE vendor choice to the integrator’s validated list.

    Strategy 2: Independent Validation + Multi-Source

    Operators with in-house integration capabilities can independently validate CPE from multiple vendors against their specific O-RAN configuration. This approach maximizes supply chain diversity and competitive pricing but requires significant testing investment.

    Strategy 3: O-RAN Badge Certification

    The O-RAN Alliance is developing a formal certification and badging program (expected to launch fully in late 2026) that will provide standardized interoperability certification for O-RAN equipment, including CPE. Operators may choose to require O-RAN Badge certification as a procurement prerequisite once the program matures.

    Global O-RAN FWA Deployment Landscape

    Japan: Rakuten Mobile operates the world’s largest commercial O-RAN network, serving over 6 million subscribers with a fully virtualized, O-RAN compliant RAN. NTT DOCOMO’s OREC (O-RAN Enterprise Consortium) initiative extends O-RAN to enterprise 5G, including FWA use cases.

    United States: DISH Wireless (now EchoStar) built the world’s first greenfield O-RAN 5G network, with O-RAN compliant infrastructure from multiple vendors. The US government’s rip-and-replace program for Huawei equipment is accelerating O-RAN adoption among rural carriers, many of whom use FWA as a primary service offering.

    Europe: Vodafone has committed to O-RAN across 2,500 sites in the UK, with plans for 30% of its European RAN to be O-RAN compliant by 2030. Deutsche Telekom’s “O-RAN Town” initiative in Neubrandenburg, Germany, is the operator’s flagship multi-vendor O-RAN deployment.

    India: Reliance Jio and Bharti Airtel are both deploying O-RAN elements in their 5G networks. Jio’s in-house 5G RAN stack is claimed to be O-RAN compliant, creating a significant market for O-RAN interoperable CPE.

    Cost and Timeline Considerations

    O-RAN FWA CPE currently carries a cost premium of approximately 10–20% compared to traditional single-vendor-validated CPE, driven by more rigorous testing requirements and additional features like slice awareness and enhanced security. However, this premium is expected to decline as O-RAN deployments scale and testing processes become more automated.

    Operators planning O-RAN FWA deployments in 2026–2027 should budget for a 3–6 month CPE validation cycle, including lab conformance testing, field trials in representative deployment environments, and interoperability testing with each component vendor in their RAN stack.

    Frequently Asked Questions

    Does O-RAN require special CPE, or can standard 5G CPE work?

    Standard 3GPP-compliant 5G CPE should technically work with O-RAN networks, as the air interface is still 3GPP NR. However, to fully leverage O-RAN capabilities — RAN slicing, multi-vendor beam management optimization, and O-RAN security features — purpose-built O-RAN aware CPE is recommended.

    How do I verify CPE interoperability with my O-RAN stack?

    Request OTIC (Open Testing and Integration Center) test reports or equivalent third-party validation. For large deployments, conduct your own interoperability testing with a representative sample of your specific O-RU/O-DU/O-CU combination.

    Will O-RAN CPE cost more than traditional CPE?

    Currently, yes — expect a 10–20% premium. However, this is partially offset by supply chain competition benefits. As O-RAN adoption scales, the premium should compress to 5–10% by 2028.

    Is O-RAN likely to become mandatory for FWA CPE?

    No global mandate exists, but in markets with strong O-RAN policy support (US, UK, Japan, India), O-RAN compliance may become a de facto procurement requirement, particularly for government-funded rural broadband programs.

    Planning an O-RAN FWA deployment and need interoperable CPE? Contact Honlly Telecom to discuss our O-RAN validated CPE portfolio and integration support services.

  • 5G CPE Antenna Design and RF Optimization: MIMO Beamforming, External Antenna Ports, and Signal Engineering for Challenging Enterprise Deployments

    5G CPE Antenna Design and RF Optimization: MIMO Beamforming, External Antenna Ports, and Signal Engineering for Challenging Enterprise Deployments

    In the 5G CPE procurement process, antenna performance is often treated as an afterthought — a spec-sheet footnote overshadowed by throughput numbers, chipset brands, and software features. Yet antenna design and RF front-end engineering are arguably the single most important determinants of real-world CPE performance, particularly in the challenging deployment environments that define enterprise B2B use cases. A CPE with a best-in-class modem chipset paired with a poorly designed antenna system will consistently underperform a mid-range chipset with optimized RF engineering.

    Why Antenna Design Matters More Than You Think

    5G New Radio (NR) operates across a dramatically wider frequency range than any previous cellular generation — from 600 MHz (n71) to 47 GHz (n262 mmWave) and everything in between. Each frequency band presents fundamentally different propagation characteristics, antenna element requirements, and beamforming strategies. A CPE antenna system must simultaneously handle:

    • Sub-1 GHz (FR1 low band): Excellent propagation through walls and obstacles, but requires larger antenna elements for efficient radiation. Critical for rural and suburban coverage where cell sites are distant.
    • 1–6 GHz (FR1 mid band, including C-band n77/n78/n79): The “goldilocks” spectrum for 5G FWA — good capacity and reasonable propagation. Requires precisely tuned antenna elements with wide instantaneous bandwidth (up to 100 MHz per carrier for 5G NR).
    • 24–47 GHz (FR2 mmWave): Massive capacity but extremely limited range and near-zero penetration through solid objects. Requires phased array antenna modules with dozens of individual elements and active beam-steering integrated circuits.

    A CPE that excels on n78 C-band but underperforms on n71 low-band will fail at rural enterprise deployments. Conversely, a CPE without mmWave support may be inadequate for dense urban environments where carriers are densifying with mmWave small cells.

    MIMO and Beamforming: The Multiplier Effect

    Modern 5G CPE devices typically implement 4×4 MIMO (Multiple Input, Multiple Output) on sub-6 GHz bands — meaning four receive antennas and four transmit antennas operating simultaneously. This configuration can theoretically double spectral efficiency compared to 2×2 MIMO, but only if the antenna elements are sufficiently de-correlated. Achieving low correlation between four antenna elements in the confined space of a desktop CPE enclosure is a significant RF engineering challenge.

    Key design considerations for 4×4 MIMO in CPE:

    • Antenna element spacing: Minimum spacing of λ/2 (half-wavelength) between elements for adequate decorrelation. At 3.5 GHz (n78), λ/2 ≈ 43 mm — which begins to constrain the industrial design of compact CPE enclosures.
    • Polarization diversity: Alternating between vertical and horizontal polarization, or using ±45° slant polarization, reduces correlation without increasing physical separation — effectively fitting more antennas into less space.
    • Pattern diversity: Designing antenna elements with intentionally different radiation patterns (e.g., one broadside-facing element and one end-fire element) provides decorrelation through angular diversity rather than spatial separation.
    • Mutual coupling compensation: When antenna elements are in close proximity, they couple electromagnetically — energy from one element induces currents in adjacent elements. Sophisticated matching networks and digital pre-distortion algorithms can compensate for mutual coupling effects, recovering the MIMO performance that would otherwise be lost.

    For mmWave CPE, the challenge scales dramatically: phased array modules may contain 16, 32, or even 64 individual antenna elements per polarization, each with its own phase shifter and amplitude control. The antenna module becomes a complex, multi-layer PCB with integrated beamforming ICs — essentially a small radar system repurposed for communications.

    External Antenna Ports: The Deployment Flexibility Multiplier

    While integrated antennas work well for many deployment scenarios — particularly window-mounted CPE with clear line-of-sight to the serving cell — enterprise deployments frequently encounter challenging RF environments:

    • CPE installed in basements, equipment rooms, or metal-clad buildings where internal antennas receive severely attenuated signals.
    • Deployments in rural areas where the serving cell is 10+ km away and high-gain directional external antennas are necessary for a stable connection.
    • Industrial environments with high electromagnetic interference from machinery, motors, and power equipment — where external antennas can be positioned away from noise sources.

    Enterprise-grade 5G CPE should provide TS-9 or SMA external antenna ports with the following capabilities:

    • Per-port configurability: The ability to assign specific antenna ports to specific frequency bands, enabling mixed configurations — for example, using integrated antennas for n78 mid-band while connecting high-gain directional external antennas for distant n71 low-band cell sites.
    • Automatic antenna detection: The CPE should automatically sense when an external antenna is connected to a port and switch the RF path accordingly, without requiring manual configuration.
    • External antenna vendor ecosystem: Published RF specifications (impedance, supported frequency ranges, maximum gain) that enable third-party antenna vendors to design compatible products, expanding deployment options for system integrators.

    Signal Quality Metrics That Actually Matter

    When evaluating CPE antenna performance, buyers should look beyond the marketing-friendly “antenna gain” number (typically quoted in dBi at a single frequency) and focus on metrics that predict real-world performance:

    • Total Radiated Power (TRP): Measures the total power actually radiated by the CPE in all directions — a more meaningful metric than conducted transmit power, as it accounts for antenna efficiency.
    • Total Isotropic Sensitivity (TIS): The reciprocal metric for receiver performance — the minimum signal level at which the CPE can maintain a connection, integrated over all spatial directions.
    • Envelope Correlation Coefficient (ECC): Quantifies the independence of MIMO antenna elements. ECC < 0.3 is generally considered acceptable for 4×4 MIMO; ECC < 0.1 is excellent.
    • Antenna efficiency: The ratio of radiated power to input power, expressed as a percentage or in dB. Even a 1 dB efficiency loss translates directly to reduced coverage range and lower throughput at the cell edge.
    • In-band VSWR (Voltage Standing Wave Ratio): Measures impedance matching across the operating frequency band. Poor VSWR means reflected power that never reaches the antenna, wasted as heat in the transmitter.

    Real-World RF Engineering Tradeoffs

    CPE antenna design is an exercise in managing competing constraints. Industrial design wants a sleek, compact enclosure; RF engineering needs physical volume for antenna separation. Marketing wants to quote the highest possible antenna gain; real-world deployments need wide beamwidth for consistent coverage regardless of device orientation. Cost optimization pushes for integrated antennas only; deployment flexibility demands external ports.

    The best 5G CPE designs navigate these tradeoffs thoughtfully, optimizing for real-world performance rather than spec-sheet hero numbers. For B2B buyers, the practical advice is simple: evaluate CPE antenna performance in your actual deployment environment, with your actual carrier network, during your actual usage patterns. A CPE that delivers 2 Gbps in a lab on a test network is less valuable than one that delivers a consistent 500 Mbps in a basement equipment room at a real customer site.

    Antenna engineering may not be glamorous, but in the physics of radio communications, it is everything. Choose accordingly.


    Honlly Telecom’s 5G CPE products feature precision-engineered multi-band antenna systems with 4×4 MIMO, external antenna port options, and carrier-optimized RF front-end designs. Contact our engineering team for detailed RF performance data and deployment consultation.

  • Multi-WAN 5G CPE for Business Continuity: SD-WAN Integration, Link Aggregation, and Intelligent Failover for Enterprise Branch Networks

    Multi-WAN 5G CPE for Business Continuity: SD-WAN Integration, Link Aggregation, and Intelligent Failover for Enterprise Branch Networks

    Business continuity demands that enterprise branch networks stay online — no exceptions. A single hour of downtime at a retail location, logistics hub, or financial services branch can cost tens of thousands of dollars in lost transactions, missed shipments, and reputational damage. Multi-WAN 5G CPE devices that natively integrate SD-WAN intelligence, link aggregation, and automatic failover are rapidly becoming the gold standard for enterprise branch connectivity — and for good reason.

    The Multi-WAN Imperative

    Single-link branch connectivity is a single point of failure. Fixed-line broadband, fiber, or MPLS circuits can go down due to construction damage, equipment failures, carrier outages, or natural events — and restoration times often stretch into days. A 2025 Uptime Institute survey found that 38% of enterprise network outages lasted more than four hours, and 11% exceeded 24 hours. For distributed enterprises, the financial exposure is unacceptable.

    Multi-WAN 5G CPE addresses this by combining at least two — and often three or four — WAN interfaces in a single device:

    • Primary WAN: 5G NR (sub-6 GHz or mmWave) providing multi-gigabit throughput as the active primary link, with the flexibility to operate in both SA and NSA modes depending on carrier network maturity.
    • Secondary WAN: Gigabit Ethernet WAN port for wired broadband, fiber ONT, or legacy MPLS circuit termination.
    • Tertiary WAN: Built-in LTE Cat 20 modem or secondary 5G radio on a different carrier for true carrier-diverse cellular failover.
    • Optional quaternary: Wi-Fi WAN (client mode) for temporary tethering to a nearby hotspot or mesh node in extreme scenarios.

    The value is not just in having multiple pipes — it is in how intelligently they are managed.

    SD-WAN Integration: Beyond Simple Failover

    First-generation multi-WAN routers used crude mechanisms: ping a gateway IP, and if three pings fail, switch to the backup link. This “dead-or-alive” model is inadequate for modern enterprise applications. Real-time voice and video traffic degrades long before a link is declared dead. Financial transaction applications require sub-second failover to avoid timeout errors. Cloud application performance varies by link quality, not just link availability.

    Modern 5G CPE with embedded SD-WAN brings application-aware path selection to the branch edge:

    • Per-application steering: Route Microsoft 365 and Salesforce traffic over the 5G link with the lowest latency, while sending bulk backup traffic over the wired broadband link — all dynamically adjusted based on real-time link quality measurements.
    • Forward error correction (FEC): Duplicate critical packets across two WAN links simultaneously, reconstructing clean streams at the destination even if one link experiences 30–40% packet loss — essential for VoIP and video conferencing over less reliable connections.
    • Sub-second failover with session persistence: When a primary link degrades or fails, active TCP sessions are migrated to the secondary link without dropping. Users on a video call won’t even notice the transition.
    • Dynamic path conditioning: Continuous measurement of jitter, latency, and packet loss on each WAN link, with the SD-WAN engine selecting the optimal path per packet in real time.
    • SaaS acceleration: Local DNS-based steering that routes Office 365, Google Workspace, and Salesforce traffic through the fastest available path, bypassing congested transit links.

    Link Aggregation: More Than the Sum of Parts

    Advanced 5G CPE platforms now support true link aggregation — bonding multiple WAN connections into a single logical tunnel with combined throughput. Unlike simple load balancing (which distributes flows across links), link aggregation combines the bandwidth of multiple links for a single flow:

    • 5G + wired broadband: A branch requiring 1.5 Gbps sustained throughput for real-time video analytics can combine a 900 Mbps 5G link with a 600 Mbps fiber circuit to achieve the required capacity, with the aggregation tunnel running to a cloud-based gateway or SD-WAN hub.
    • Dual 5G carrier aggregation: Two 5G modems on different carriers (e.g., carrier A on n78, carrier B on n41) bonded together through a cloud aggregation gateway, providing carrier-level redundancy plus combined throughput.
    • MPTCP (Multipath TCP): Standards-based multipath transport that splits a single TCP connection across multiple WAN interfaces, compatible with existing server infrastructure without requiring proprietary tunnel protocols.

    Intelligent Failover Architecture: A Technical Deep Dive

    Enterprise-grade multi-WAN CPE implements a multi-layer failover detection system that operates far beyond simple ping-based link monitoring:

    Layer 1 — Physical link detection: The CPE continuously monitors the physical layer status of each WAN interface — Ethernet link state, cellular modem registration status, signal quality indicators (RSRP, SINR, RSRQ for 5G NR). Physical link loss triggers an immediate (sub-50ms) failover decision, as there is no point waiting for higher-layer protocols to time out.

    Layer 2 — Carrier network reachability: Even with a registered modem, the carrier’s packet gateway may be unreachable. The CPE probes the carrier’s PDN gateway and DNS servers at configurable intervals (typically 500ms–2s). Consecutive failures trigger failover before TCP connections begin timing out.

    Layer 3 — End-to-end application reachability: The SD-WAN engine probes actual application endpoints — Salesforce login page, Microsoft 365 front-door IPs, corporate data center gateways — measuring not just reachability but also response time. Degraded performance (e.g., latency exceeding a configured threshold) triggers a proactive failover even if the link is technically “up.”

    Layer 4 — Synthetic transaction monitoring: Advanced implementations perform lightweight synthetic transactions — a DNS lookup followed by a TCP connect and TLS handshake — against critical application endpoints every few seconds. This catches subtle failures like DNS misconfigurations or TLS certificate issues that simpler probes would miss.

    Deployment Best Practices

    For enterprise network architects deploying multi-WAN 5G CPE at scale, several best practices emerge from real-world deployments:

    1. Carrier diversity is non-negotiable: A primary and backup link from the same carrier share fate during carrier-wide outages. Use different carriers for cellular links, and ideally a wired broadband link from a different physical infrastructure provider.
    2. Test failover under load: Failover that works perfectly in a lab with 5 Mbps of test traffic may fail in production with 500 Mbps of real user traffic. Conduct regular chaos engineering exercises — deliberately failing primary links during business hours — to validate failover behavior under real-world conditions.
    3. Monitor the secondary link actively: A backup link that has been silently failing for weeks is worse than no backup at all. The CPE should continuously validate secondary link health by sending synthetic traffic through it, not just waiting for a failover event to discover a problem.
    4. Align QoS policies with link capacity: When failing over from a 2 Gbps 5G primary to a 300 Mbps LTE backup, QoS policies must automatically adjust to prevent non-critical traffic from starving business-critical applications of bandwidth on the constrained link.
    5. Plan for asymmetric routing: In link aggregation scenarios, upstream and downstream traffic may take different paths. Ensure that stateful firewalls and security appliances are configured to handle asymmetric flows without dropping legitimate traffic.

    The Business Case

    For a typical enterprise with 50 branch locations, the math is straightforward: the incremental cost of multi-WAN 5G CPE over single-link routers is roughly $8,000–$15,000 across the fleet. A single 4-hour outage at one branch location can cost $5,000–$50,000 in direct losses alone, not including brand damage and customer churn. The ROI on multi-WAN resilience is measured in weeks, not months.

    Multi-WAN 5G CPE with embedded SD-WAN intelligence represents the convergence of connectivity, resilience, and application performance optimization into a single branch-edge platform. For enterprises that cannot afford downtime — which is to say, all of them — it is no longer optional. It is infrastructure.


    Honlly Telecom’s enterprise 5G CPE portfolio includes multi-WAN models with embedded SD-WAN, carrier-diverse dual-SIM support, and sub-second intelligent failover — designed for mission-critical branch connectivity. Explore our product line or contact our solutions engineering team for a customized deployment plan.