Author: openclaw-Lisa-New

  • A Technical Buyer’s Guide to 5G CPE Zero-Trust Security Architecture: Hardware Root of Trust, Secure Boot, and End-to-End Encryption for Enterprise FWA Deployments

    A Technical Buyer’s Guide to 5G CPE Zero-Trust Security Architecture: Hardware Root of Trust, Secure Boot, and End-to-End Encryption for Enterprise FWA Deployments

    As enterprise 5G fixed wireless access deployments scale from proof-of-concept trials to production networks carrying sensitive corporate, financial, and operational traffic, the security architecture of CPE devices has emerged as a boardroom-level concern. The traditional perimeter-based security model—where CPE was treated as a trusted endpoint inside the corporate firewall—is fundamentally incompatible with the distributed, multi-site, cloud-first enterprise architectures dominating 2026. For technical buyers evaluating 5G CPE for enterprise and industrial deployments, zero-trust security principles must now inform procurement specifications as rigorously as throughput, latency, and radio performance parameters.

    The CPE Attack Surface: Why 5G FWA Demands Zero-Trust

    5G CPE occupies a uniquely exposed position in the enterprise network topology. Unlike a core router locked in a climate-controlled data center with physical access controls and 24/7 security monitoring, CPE is frequently deployed in branch offices, retail locations, construction trailers, and outdoor enclosures—environments where physical tampering, unauthorized access, and network-based attacks are realistic threat vectors. Compromised CPE provides an attacker with a persistent foothold inside the enterprise WAN, with the ability to intercept, modify, or exfiltrate traffic across every connected LAN segment.

    The 3GPP 5G security architecture (TS 33.501) provides robust air interface protection through 5G AKA mutual authentication, SUCI-based subscriber identity privacy, and 256-bit encryption on the radio link. However, these protections terminate at the CPE’s modem interface. Post-modem—within the CPE’s application processor, operating system, LAN interfaces, and management plane—enterprise security depends entirely on the CPE’s embedded security architecture, which varies dramatically across vendors and price points.

    Hardware Root of Trust: The Foundational Layer

    Zero-trust CPE security begins at the silicon level. A hardware root of trust (HRoT) provides an immutable, cryptographically verifiable foundation that ensures the CPE boots only authentic, vendor-signed firmware and that device identity keys cannot be extracted or cloned even with physical access to the device.

    Secure Boot Chain: The CPE’s boot ROM, signed by the SoC vendor’s root key, cryptographically verifies the first-stage bootloader. Each subsequent stage—U-Boot or LK bootloader, Linux kernel, root filesystem—is verified against signed hashes before execution. Any modification to the boot chain, whether through firmware tampering, JTAG/SWD debug interface exploitation, or storage replacement, causes boot failure and, ideally, tamper-evident logging to a secure element. Enterprise procurement specifications should mandate secure boot with hardware-backed key storage (e.g., TPM 2.0 or platform-integrated secure enclave) and configurable security policy for boot verification failure behavior.

    Trusted Platform Module (TPM) Integration: A discrete or firmware TPM 2.0 implementation enables secure storage of device identity keys, measured boot attestation, and sealed storage that binds encryption keys to specific platform configuration register (PCR) values. For enterprise zero-trust architectures, TPM-backed device attestation allows the network’s policy enforcement point to cryptographically verify that the CPE is running authorized firmware and configuration before granting network access—a foundational zero-trust principle.

    Secure Element and SIM/eUICC Integration

    The CPE’s UICC or eUICC provides a tamper-resistant secure element for 5G network authentication, but its security capabilities can and should be leveraged for CPE device identity beyond the 3GPP authentication framework. The GSMA’s IoT SAFE (IoT SIM Applet For Secure End-to-End) initiative standardizes the use of the SIM/eSIM as a hardware security module for device-level TLS client certificates, credential storage, and cryptographic operations.

    CPE implementing IoT SAFE can use the carrier-provisioned eUICC as the hardware root for mutually authenticated TLS connections to enterprise zero-trust policy engines, cloud management platforms, and ZTNA (Zero Trust Network Access) brokers. This eliminates the need for separate hardware security modules and leverages the existing mobile operator security infrastructure—including secure OTA provisioning and key rotation—for enterprise CPE identity management.

    End-to-End Encryption and Traffic Isolation

    Zero-trust architecture mandates that no traffic is trusted based on network location alone. For 5G CPE deployed at the enterprise edge, this translates to mandatory encryption across the CPE’s entire data path:

    IPsec and WireGuard Tunnel Termination: Enterprise CPE must support hardware-accelerated IPsec (IKEv2 with strong cipher suites) and WireGuard for tunnel termination to enterprise VPN concentrators or cloud security gateways. AES-256-GCM and ChaCha20-Poly1305 cipher support with hardware crypto acceleration is essential for maintaining multi-gigabit throughput with encryption overhead. CPE should support per-VLAN tunnel mapping, enabling different traffic classes (corporate data, guest Wi-Fi, IoT telemetry) to be encrypted and routed through separate security domains.

    Micro-Segmentation at the CPE Edge: Advanced enterprise CPE implements 802.1Q VLAN trunking with per-VLAN security policies, enabling micro-segmentation between corporate workstations, payment systems, building management IoT, and guest networks directly at the branch edge. Combined with dynamic policy enforcement from a cloud-based zero-trust policy engine, this architecture ensures that a compromised IoT sensor cannot pivot to attack the payment processing VLAN—even when both connect through the same 5G CPE.

    MACsec and 802.1X for LAN-Side Security: For deployments where the CPE’s LAN ports connect to managed switches or other infrastructure devices, MACsec (IEEE 802.1AE) at line rate and 802.1X supplicant functionality on the CPE’s LAN interfaces provide link-layer encryption and port-based authentication that extend the zero-trust boundary one hop deeper into the enterprise network.

    Management Plane Security: The Overlooked Vector

    CPE management interfaces—TR-069/TR-369 (USP), SNMP, SSH, RESTCONF, and vendor-specific cloud management APIs—represent a high-value attack surface. Zero-trust CPE security architecture must protect these interfaces with the same rigor applied to the data plane:

    Mutual TLS for Management Protocols: All CPE management protocols must use mutually authenticated TLS 1.3 with client certificate authentication. The CPE must authenticate the management server (preventing man-in-the-middle attacks), and the management server must authenticate the CPE (preventing rogue device registration). Certificate enrollment should use EST (RFC 7030) or SCEP with hardware-backed key generation in the TPM or secure element.

    Role-Based Access Control and Audit Logging: CPE must implement granular RBAC distinguishing between firmware update, configuration change, monitoring-only, and diagnostic roles. All administrative actions must generate syslog or structured audit events with immutable timestamps, forwarded to a centralized SIEM. Local admin credentials must be salted and hashed with modern algorithms (bcrypt, Argon2id), never stored in plaintext or reversible formats.

    Secure OTA Firmware Updates: Over-the-air firmware updates are the most security-critical operation in the CPE lifecycle. Updates must be signed with vendor private keys, verified by the CPE before installation, and delivered over mutually authenticated TLS. The update mechanism must support A/B partition schemes with automatic rollback on verification failure, and update metadata (version, hash, signature, target hardware revision) must be independently verifiable by enterprise security teams.

    Building the Procurement Specification

    For technical buyers drafting 5G CPE procurement specifications in 2026, the following zero-trust security requirements should be considered mandatory for enterprise-grade deployments:

    • Hardware root of trust with immutable boot ROM and secure boot chain verification
    • TPM 2.0 or equivalent secure enclave for key storage and device attestation
    • GSMA IoT SAFE or equivalent SIM-based credential storage for device identity
    • Hardware-accelerated IPsec (AES-256-GCM) and WireGuard with per-VLAN tunnel mapping
    • Mutual TLS 1.3 for all management interfaces with hardware-backed client certificates
    • Signed, verified OTA firmware updates with A/B dual-bank fallback
    • Granular RBAC with immutable audit logging to external SIEM
    • 802.1X supplicant and MACsec support for LAN-side zero-trust extension
    • FIPS 140-3 or Common Criteria EAL4+ certification for cryptographic modules

    The enterprise 5G FWA security landscape in 2026 demands that CPE be treated not as a simple modem-and-router appliance, but as a security-enforcement point at the distributed enterprise edge. Organizations that apply zero-trust principles to CPE procurement will build 5G FWA networks that are scalable, defensible, and audit-ready—while those that treat CPE security as an afterthought will embed technical debt that becomes exponentially more expensive to remediate as deployments scale.
  • A Technical Buyer’s Guide to 5G CPE IPv6 Transition: Dual-Stack Architecture, IPv6-Only Deployment Strategies, and Carrier-Grade NAT64/DNS64 Design

    A Technical Buyer’s Guide to 5G CPE IPv6 Transition: Dual-Stack Architecture, IPv6-Only Deployment Strategies, and Carrier-Grade NAT64/DNS64 Design

    As global IPv4 address exhaustion enters its terminal phase—with RIPE NCC, APNIC, and ARIN all operating from final /8 allocations and IPv4 transfer market prices exceeding USD 55 per address—the transition to IPv6 in 5G fixed wireless access deployments has moved from a future-proofing exercise to an operational imperative. For technical buyers evaluating 5G CPE for carrier and enterprise deployments in 2026, understanding IPv6 transition architecture is no longer optional: it directly impacts address scalability, application performance, NAT traversal overhead, and total cost of ownership across the CPE lifecycle.

    The IPv4 Exhaustion Landscape and 5G FWA Implications

    5G FWA networks introduce a unique scaling challenge for IPv4. Unlike traditional mobile broadband where NAT44 and CGNAT at the mobile core suffice for smartphone traffic, FWA CPE serves entire LANs—often with dozens to hundreds of connected devices per premises—each expecting routable or at least well-NATed IP connectivity. CGNAT at the 5G core introduces stateful translation overhead that scales linearly with concurrent sessions, creating throughput bottlenecks, increased latency, and application compatibility issues for protocols that embed IP addresses in payloads (SIP, FTP, IPsec, gaming protocols).

    The 3GPP 5G architecture mandates IPv6 support in the 5G core (5GC), and all major 5G standalone (SA) deployments globally operate with IPv6-native user plane functions (UPF). However, the last-mile CPE—where enterprise LANs meet the 5G WAN—remains the critical decision point where IPv6 transition strategy is implemented or broken.

    Dual-Stack Architecture: The Pragmatic Baseline

    Dual-stack remains the most widely deployed IPv6 transition mechanism in 5G CPE, and for good reason: it provides simultaneous IPv4 and IPv6 connectivity without requiring either protocol to tunnel through the other. In a dual-stack 5G FWA deployment, the 5GC assigns both an IPv4 address (typically RFC 1918 private address behind CGNAT) and an IPv6 global unicast address (GUA) prefix to the CPE WAN interface. The CPE then distributes IPv4 via NAT44 on the LAN side and IPv6 via prefix delegation (DHCPv6-PD) or SLAAC.

    Key design considerations for dual-stack CPE:

    DHCPv6 Prefix Delegation: The CPE must request an IPv6 prefix from the 5GC via DHCPv6-PD, with typical prefix lengths ranging from /56 to /64 depending on operator policy. Enterprise-grade CPE should support configurable prefix delegation hint sizes and sub-delegation to downstream routers for multi-subnet deployments.

    DNS64/NAT64 Integration: Even in dual-stack deployments, the 5GC may implement DNS64/NAT64 for IPv6-only transport, requiring the CPE to correctly handle synthesized AAAA records (RFC 7050) and ensure applications that use literal IPv4 addresses are properly translated through the NAT64 gateway’s well-known prefix (64:ff9b::/96).

    Happy Eyeballs v2 (RFC 8305): CPE should not interfere with client-side Happy Eyeballs algorithm operation, ensuring that dual-stack endpoints can rapidly prefer IPv6 when available while falling back to IPv4 seamlessly. Enterprise deployments should validate CPE firmware does not introduce DNS filtering or connection tracking that biases protocol selection.

    IPv6-Only Deployments: The End-State Architecture

    Forward-looking operators and large enterprises are increasingly targeting IPv6-only CPE deployments, eliminating IPv4 from the access network entirely. In this model, the CPE receives only an IPv6 GUA on its WAN interface, and IPv4 connectivity for legacy applications is provided through NAT64 translation at the 5GC UPF or through a CLAT (Customer-side Translator) function integrated into the CPE itself.

    464XLAT (RFC 6877): This architecture combines a CLAT function in the CPE that performs stateless IPv4-to-IPv6 translation (SIIT) with a PLAT (Provider-side Translator) in the operator network that performs stateful NAT64. The CPE’s CLAT function intercepts IPv4 traffic from LAN devices, encapsulates it in IPv6 packets addressed to the PLAT’s NAT64 prefix, and the PLAT completes the translation to public IPv4. This architecture is particularly suited to mobile network operators with large-scale CGNAT infrastructure already in place.

    MAP-T and MAP-E (RFC 7597, 7599): Mapping of Address and Port (MAP) technologies provide deterministic, stateless IPv4-over-IPv6 translation that eliminates the stateful NAT bottleneck at the operator core. MAP-T (Translation mode) and MAP-E (Encapsulation mode) are gaining traction in Asian operator deployments where CGNAT capacity planning has become a significant operational concern. CPE supporting MAP must implement Border Relay (BR) client functionality with configurable mapping rules, port-set allocation, and correct handling of ICMP/PMTUD in the translated path.

    Enterprise Considerations: Beyond Protocol Support

    IPsec and VPN Compatibility: Enterprise CPE commonly terminate IPsec tunnels to headquarters or cloud VPN concentrators. IPv6 transition mechanisms must be validated for IPsec interoperability: IKEv2’s support for IPv6 transport and IPv6-embedded IPsec Security Associations must be confirmed across CPE firmware versions. ESP encapsulation in MAP-E, in particular, can introduce MTU issues requiring careful PMTUD or MSS clamping configuration.

    SD-WAN Integration: Many enterprise 5G FWA deployments position the CPE as a WAN edge device within a broader SD-WAN fabric. The CPE’s IPv6 transition mechanism must be compatible with SD-WAN overlay protocols (VXLAN, GRE, IPsec) that may themselves operate over IPv4 or IPv6 underlay networks. Dual-stack CPE provides the greatest SD-WAN deployment flexibility, while 464XLAT and MAP-T/E architectures may require overlay-to-underlay address family translation in the SD-WAN edge.

    Application Performance Monitoring: IPv6 transition adds protocol translation hops that can complicate performance monitoring and root-cause analysis. Enterprise-grade CPE should expose per-protocol (IPv4/IPv6) throughput, latency, and session count metrics via SNMP, NETCONF/YANG, or RESTCONF APIs, enabling network operations teams to separately monitor native and translated traffic paths.

    Evolving Standards and the Road Ahead

    The IETF v6ops working group continues to refine IPv6 transition operational guidance, with RFC 9099 (Operational Security Considerations for IPv6 Networks) and RFC 9386 (IPv6 Deployment Status) providing updated recommendations relevant to CPE design. The Broadband Forum’s TR-124 issue 8 introduces IPv6 transition requirements for 5G residential gateways, specifying mandatory CLAT and 464XLAT support alongside dual-stack and IPv6-only operational modes.

    For technical buyers, the key takeaway is clear: 5G CPE procurement specifications must explicitly define IPv6 transition architecture requirements, including preferred mechanism (dual-stack, 464XLAT, MAP-T/E), required prefix delegation behavior, DNS64/NAT64 handling, and VPN/SD-WAN compatibility. CPE that ships with only IPv4 CGNAT support in 2026 is already technically obsolete for any operator or enterprise with a five-year deployment horizon.

  • A Technical Buyer’s Guide to 5G CPE Thermal Management: Passive Cooling, Industrial-Grade Enclosures, and Outdoor Deployment Reliability

    A Technical Buyer’s Guide to 5G CPE Thermal Management: Passive Cooling, Industrial-Grade Enclosures, and Outdoor Deployment Reliability

    Thermal management is one of the most overlooked yet critical design disciplines in 5G CPE engineering. While buyers and operators focus on throughput, band support, and MIMO configuration, the thermal envelope directly determines a device’s sustained performance, outdoor survivability, and total cost of ownership across a multi-year deployment lifecycle. A CPE that throttles under load or fails prematurely due to heat stress undermines the entire FWA business case.

    This guide provides a structured framework for technical buyers, procurement managers, and operator engineering teams evaluating 5G CPE thermal design — from passive cooling strategies to industrial-grade enclosure certification.

    Why Thermal Design Matters for 5G CPE

    5G CPE devices operate under fundamentally different thermal constraints than their 4G predecessors. Several factors contribute to increased heat generation:

    Higher Power Amplifier Output. 5G NR, particularly in n77/n78 (3.5 GHz) and n258/n257 (mmWave) bands, requires power amplifiers operating at higher output levels to maintain link budget. Each dB of PA output translates to additional milliwatts of dissipated heat.

    Multi-Band Carrier Aggregation. Modern CPE devices simultaneously operate across multiple frequency bands — sub-6 GHz for coverage and mmWave or mid-band for capacity. Each active RF chain contributes to the total thermal load.

    Integrated Wi-Fi 6/6E/7 AP. CPE serving as a combined 5G modem and Wi-Fi access point runs two high-performance radios in a single enclosure, essentially doubling the thermal challenge.

    Edge Compute Workloads. As CPE devices incorporate AI/ML inference for intelligent traffic steering, predictive maintenance, and local analytics, the SoC runs sustained compute workloads that compound RF-induced heat generation.

    The result: a 5G CPE can generate 12–25W of thermal dissipation load in sustained operation, compared to 5–10W for a typical 4G CPE. Without adequate thermal management, device temperature can exceed safe operating limits within 15–30 minutes of sustained full-load operation.

    Passive Cooling: The First Line of Defense

    For most CPE form factors — particularly indoor desktop and wall-mounted units — passive cooling is the preferred thermal management strategy. It eliminates fan-related failure modes, acoustic noise, and dust ingress, all of which are unacceptable in residential and quiet office environments.

    Heat Sink Design

    Effective passive cooling starts with the heat sink. Key design parameters include:

    Material Selection: Die-cast aluminum is the industry standard, balancing thermal conductivity (~120–170 W/m·K for common alloys), weight, and manufacturing cost. Premium designs may specify copper inserts for hotspot mitigation at the modem/SoC interface. – Fin Geometry: Fin height, pitch, and orientation must be optimized for the device’s mounting orientation. Wall-mounted CPE benefits from vertically oriented fins that enhance natural convection. Desktop CPE with horizontal orientation requires forced airflow paths or chimney-effect enclosures. – Surface Area: As a rule of thumb, passive cooling requires approximately 30–50 cm² of effective surface area per watt of dissipated heat for a 40°C ambient-to-junction temperature delta. A 20W CPE thus needs 600–1,000 cm² of effective heat sink surface area.

    Thermal Interface Materials (TIM)

    The gap between the modem/SoC die and the heat sink is a critical thermal bottleneck. High-performance thermal pads or phase-change materials with conductivity above 5 W/m·K are recommended. Gap filler pads must account for component height variance across the PCB — a 0.2mm tolerance stack can increase thermal resistance by 30% if uncompensated.

    Enclosure as Heat Sink

    Advanced passive designs use the entire CPE enclosure as a thermal dissipation surface. Magnesium-alloy or aluminum chassis bonded to internal heat spreaders distribute heat across the full device surface, eliminating hotspots while maximizing radiative and convective cooling. This approach is particularly effective for slim, wall-mounted indoor CPE where aesthetic constraints limit visible heat sink protrusions.

    Outdoor CPE: The Industrial-Grade Challenge

    Outdoor CPE — deployed on rooftops, poles, or building exteriors — faces thermal conditions that passive cooling alone cannot always handle. These devices must operate reliably across an ambient temperature range of -40°C to +55°C, with direct solar radiation adding 15–25°C of effective thermal load during peak sun exposure.

    IP-Rated Enclosures with Thermal Management

    The ingress protection (IP) rating fundamentally constrains thermal design. An IP67 or IP68 enclosure is sealed against dust and water — which also means zero natural airflow. Every watt of heat must be conducted through the enclosure walls. This creates a design tension between environmental sealing and thermal dissipation that requires careful engineering:

    Dual-Chamber Architecture: Some outdoor CPE designs separate the sealed electronics chamber from a vented heat exchanger chamber with Gore-Tex membranes that allow pressure equalization and limited vapor transmission without compromising IP rating. – Die-Cast Enclosure with Integrated Fins: The enclosure itself becomes the primary heat sink. Thick-walled die-cast aluminum bodies with external fins maximize surface area while maintaining structural integrity and IP compliance. – Solar Radiation Mitigation: Light-colored or reflective enclosure finishes reduce solar absorption. A white or light-gray powder-coated surface can reduce solar gain by 40–60% compared to dark-colored or bare metal enclosures.

    Sun Shield and Mounting Considerations

    Outdoor CPE mounting accessories contribute significantly to thermal performance:

    – A sun shield or visor above the CPE enclosure blocks direct solar radiation during peak hours, reducing internal temperature rise by 10–15°C. – Pole-mount brackets should include a thermal standoff gap (minimum 10mm) between the enclosure and the mounting surface to maintain convection airflow on all sides. – Orientation matters: vertical mounting with fins aligned to the prevailing wind direction improves cooling by up to 25% compared to horizontal orientations.

    Active Cooling: When Fans Are Necessary

    In extreme thermal environments — high ambient temperature combined with sustained full-load operation — passive cooling may be insufficient. Active fan-based cooling introduces moving parts but can dramatically increase heat dissipation capacity.

    Fan Selection and Reliability

    For CPE applications, fan selection criteria differ from consumer electronics:

    MTBF (Mean Time Between Failures): Industrial-grade fans rated for 70,000–100,000 hours at 40°C are minimum requirements for operator-grade outdoor CPE. Consumer-grade fans (30,000–50,000 hours) are unacceptable for multi-year outdoor deployments. – Dual-Ball vs. Sleeve Bearings: Dual-ball bearing fans maintain performance across wide temperature ranges and tolerate mounting in any orientation. Sleeve-bearing fans degrade rapidly when mounted vertically and are not recommended for outdoor CPE. – Fan Speed Control: PWM-controlled, temperature-regulated fan curves balance cooling with acoustic noise and power consumption. A smart fan controller can reduce fan duty cycle below 20% during idle/low-load conditions, extending fan life and reducing dust accumulation.

    Hybrid Passive-Active Designs

    The optimal approach for demanding outdoor deployments is a hybrid design: passive cooling handles normal operation, and a temperature-controlled fan activates only when the internal junction temperature exceeds a threshold (typically 65–70°C). This minimizes fan runtime — often to less than 5% of total operating hours in temperate climates — while providing thermal headroom for extreme conditions.

    Thermal Testing and Validation Standards

    Technical buyers should verify that CPE vendors have subjected their designs to rigorous thermal validation:

    IEC 60068-2 Environmental Testing: Thermal cycling (-40°C to +85°C, minimum 100 cycles), damp heat (85°C/85% RH, 1,000 hours), and thermal shock testing. – Soak Testing: Sustained operation at maximum ambient temperature (typically +55°C) with full RF and compute load for a minimum of 72 continuous hours with zero throttling events. – Solar Load Simulation: IEC 60068-2-5 procedures for solar radiation testing, simulating 1,120 W/m² irradiance.

    Evaluation Checklist for Buyers

    When assessing 5G CPE thermal design, request the following from vendors:

    1. Thermal simulation reports showing junction temperatures for CPU, modem, PA, and Wi-Fi chipset under worst-case conditions (max ambient + full load).
    2. Throttling policy documentation: At what temperature does the device begin reducing TX power, MIMO layers, or carrier aggregation? What is the recovery behavior?
    3. Enclosure material and finish specifications, including solar absorptivity index for outdoor models.
    4. IP rating certification from an accredited test laboratory — not self-declared.
    5. Fan MTBF certification and fan replacement procedures if active cooling is used.
    6. Field failure data from comparable deployments in similar climate zones.

    The Bottom Line

    Thermal management is not a secondary concern — it is a first-order determinant of CPE reliability and operator satisfaction. A device that handles heat well will deliver consistent throughput, survive harsh outdoor environments, and minimize field replacement costs over a 5–7 year deployment lifetime. At Honlly Telecom, our 5G CPE designs incorporate industrial-grade passive cooling architectures, IP67-rated enclosures, and hybrid thermal solutions validated to the most demanding operator specifications. Contact our engineering team to discuss thermal requirements for your next FWA deployment.

  • A Technical Buyer’s Guide to 5G CPE Carrier Aggregation and Spectrum Sharing: Multi-Band Optimization, DSS Strategies, and Throughput Maximization for Operator Deployments

    A Technical Buyer’s Guide to 5G CPE Carrier Aggregation and Spectrum Sharing: Multi-Band Optimization, DSS Strategies, and Throughput Maximization for Operator Deployments

    Carrier aggregation (CA) is the engine that transforms 5G from a single-band connectivity solution into a multi-gigabit wireless broadband platform. For operators deploying Fixed Wireless Access at scale, the CPE’s CA capabilities directly determine peak and average throughput, cell-edge performance, and the efficient utilization of fragmented spectrum assets. This guide provides a structured evaluation framework for technical buyers assessing 5G CPE carrier aggregation architecture, Dynamic Spectrum Sharing (DSS) integration, and real-world throughput optimization strategies.

    The Carrier Aggregation Landscape in 5G NR

    5G NR carrier aggregation differs fundamentally from LTE CA in both scale and flexibility. Release 15 introduced a baseline of up to 16 component carriers (CCs) with a maximum aggregated bandwidth of approximately 1 GHz in Frequency Range 2 (FR2, mmWave). Release 16 and 17 expanded intra-band and inter-band CA combinations, while Release 18 (5G-Advanced) introduces enhanced cross-carrier scheduling and AI-assisted carrier selection.

    Current CA Configurations Relevant to FWA CPE

    For sub-6 GHz FWA deployments, the most commercially relevant CA configurations include:

    | Configuration | Component Carriers | Aggregate BW | Peak DL Throughput (4×4 MIMO) | |—————|——————-|————-|——————————-| | n77 + n78 Intra-band | 2–4 CCs | 200–400 MHz | 3.4–6.8 Gbps | | n77 + n78 + n79 | 3–6 CCs | 300–600 MHz | 5.1–10.2 Gbps | | n1 + n3 + n78 | 3 CCs | 110–190 MHz | 1.9–3.2 Gbps | | n28 + n78 (Low+Mid) | 2 CCs | 130–170 MHz | 2.2–2.9 Gbps | | n258 + n257 (mmWave) | 4–8 CCs | 400–800 MHz | 6.8–13.6 Gbps |

    The practical throughput numbers depend on modulation order (256QAM vs. 64QAM), MIMO layers, and coding rate. Buyers should request vendor-validated throughput figures at specific signal conditions rather than relying on theoretical peak rates.

    Inter-Band vs. Intra-Band CA: Architecture Trade-offs

    Intra-Band Contiguous CA

    When an operator holds contiguous spectrum within a single band (e.g., 100 MHz + 60 MHz within n78), intra-band contiguous CA is the simplest configuration. A single RF chain and power amplifier can cover the entire bandwidth, minimizing component count, cost, and power consumption. CPE supporting intra-band contiguous CA typically achieves the highest power efficiency and lowest cost-per-Mbps.

    Intra-Band Non-Contiguous CA

    Non-contiguous intra-band CA addresses the common scenario where an operator’s spectrum within a band is fragmented — for example, 80 MHz + 40 MHz separated by a 20 MHz gap held by another operator. This requires a wider RF front-end or dual receive paths within the same band, increasing component complexity but enabling aggregation of otherwise stranded spectrum assets.

    Inter-Band CA

    Inter-band CA combines carriers across different frequency bands — most commonly low-band (n28, 700 MHz for coverage) with mid-band (n78, 3.5 GHz for capacity). This configuration requires multiple RF chains, separate antennas or a wideband antenna array, and more sophisticated baseband processing for cross-band scheduling. The value is significant: low-band carriers provide reliable control-plane coverage and uplink performance, while mid-band carriers deliver downlink throughput.

    For FWA CPE deployed in suburban and rural environments, inter-band CA combining sub-1 GHz coverage bands with 3.5 GHz capacity bands is often the most impactful configuration for balancing reach and speed.

    Dynamic Spectrum Sharing (DSS)

    DSS enables operators to simultaneously operate LTE and 5G NR in the same frequency band by dynamically allocating resource blocks between the two technologies on a millisecond timescale. For CPE buyers, DSS support is particularly relevant in markets where operators are refarming 4G spectrum for 5G rather than deploying on greenfield spectrum.

    How DSS Affects CPE Design

    From the CPE perspective, DSS is largely transparent at the physical layer — the device receives scheduling grants and demodulates the allocated resource blocks regardless of whether adjacent blocks carry LTE or NR traffic. However, two CPE features significantly impact DSS performance:

    1. DSS-Aware Rate Matching: The CPE modem must correctly interpret LTE Cell-Specific Reference Signal (CRS) rate matching patterns from the gNB to avoid demodulation errors on resource elements shared with LTE. CPE chipsets with DSS-optimized baseband processing achieve 5–15% higher throughput in DSS scenarios compared to basic implementations.

    2. MBSFN Subframe Awareness: In DSS deployments where LTE uses MBSFN subframes to free resources for NR, the CPE must handle the dynamic subframe configuration changes without connection drops. Field testing has shown that some early 5G CPE implementations experience intermittent connectivity in aggressive DSS configurations — buyers should verify DSS interoperability with their specific operator’s LTE/NR resource allocation scheme.

    CA Combination Validation: What Buyers Must Verify

    Not all CA combinations listed in modem datasheets are commercially viable. 3GPP specifications define hundreds of possible CA combinations, but practical implementation is constrained by:

    RF Front-End Complexity. Each additional CC adds filters, LNAs, and switching networks. A CPE supporting 6-way CA may require 12+ discrete RF filters, each adding insertion loss, cost, and PCB area. The gap between “chipset-capable” and “product-implemented” CA combinations can be significant.

    Coexistence and Desense. Multiple simultaneously active receivers operating across wide frequency separations (e.g., n28 at 700 MHz and n78 at 3.5 GHz) risk self-interference from harmonics, intermodulation products, and local oscillator leakage. Effective RF shielding, PCB isolation, and filtering are essential but add cost and physical volume.

    Antenna Isolation. Multiple antenna elements supporting different bands require sufficient isolation to avoid coupling. For FWA CPE with integrated antennas, achieving >15 dB of inter-band isolation in a compact form factor is a significant RF engineering challenge.

    Power and Thermal Budget. Each additional active receive path adds 0.5–2W to the power budget. CPE designs that claim extensive CA support on paper may throttle CA combinations under thermal load. Buyers should request sustained throughput data (not peak burst rates) at maximum ambient temperature.

    Buyer Verification Protocol

    When evaluating a CPE’s CA claims, request:

    1. A complete CA combination list with per-combination validated throughput (not chipset theoretical maximums).
    2. Sustained throughput stability data — 24-hour throughput logs at maximum CA configuration, with zero throttling events.
    3. Band-specific RSSI-to-throughput mapping showing performance degradation curves as signal strength decreases.
    4. DSS interoperability test reports with the target operator’s specific NR/LTE resource allocation configuration.
    5. Thermal performance at maximum CA configuration — junction temperatures and any throttling triggers.

    CA and Spectrum Strategy: Aligning CPE with Operator Roadmaps

    Operators should evaluate CPE CA capabilities against their mid-term spectrum strategy (3–5 year horizon), not just the current spectrum portfolio. Key considerations:

    Refarming Timelines

    If an operator plans to refarm 3G (2100 MHz) or 4G (1800 MHz, 2600 MHz) spectrum for 5G NR within the CPE deployment lifecycle, the device must support those band additions. CPE with software-defined radio (SDR) architectures offer future-proofing advantages — new bands can be added via firmware update rather than hardware replacement.

    5G-Advanced CA Enhancements

    Release 18 introduces several CA-related enhancements that will arrive in CPE chipsets from late 2026:

    Cross-Carrier Scheduling with Single DCI: Reducing control channel overhead by scheduling multiple carriers with a single downlink control information message. – AI/ML-Based Carrier Selection: Network-side AI models predict optimal carrier combinations per-UE based on load, interference, and mobility patterns. – Supplementary Uplink (SUL) Enhancements: Aggregating low-band uplink with mid-band downlink to improve uplink coverage in time-division duplex (TDD) deployments, critical for video conferencing and cloud upload use cases.

    Buyers procuring CPE for 2027–2028 deployments should prioritize Release 18-capable platforms to capture these efficiency gains.

    Cost vs. CA Capability: Finding the Right Tier

    Not every FWA deployment requires maximum CA. Segmenting CPE specifications by use case optimizes procurement cost:

    | Deployment Tier | Recommended CA | Target Throughput | Typical Cost Delta | |—————-|—————-|——————-|——————-| | Entry / Rural | 2× CA (Low+Mid) | 100–300 Mbps | Baseline | | Standard Suburban | 3–4× CA (Mid-band) | 500 Mbps–1 Gbps | +15–25% | | Premium Urban | 4–6× CA (Mid+mmWave) | 1–3 Gbps | +35–60% | | Enterprise / SMB | 6–8× CA (Full FR1+FR2) | 3–10 Gbps | +60–120% |

    The cost deltas include RF front-end, antenna, thermal, and baseband processing overhead. For operators serving diverse geographic markets, a tiered CPE portfolio — rather than a single “maximum CA” SKU — typically delivers the best ROI.

    Practical Throughput Expectations

    Buyers should calibrate expectations around real-world throughput. In field conditions, even well-designed CA implementations deliver 50–70% of theoretical peak rates due to:

    – Signal-to-Noise Ratio (SNR) degradation at cell edge – Network loading (shared spectrum among multiple UEs) – Backhaul constraints at the gNB – Transport-layer overhead (UDP/TCP headers, retransmissions) – Wi-Fi bridging losses for CPE operating as an AP

    A CPE rated for 5 Gbps peak CA throughput should be expected to deliver 2–3.5 Gbps in typical suburban deployment conditions and 1–2 Gbps at the cell edge. These are still transformative speeds for FWA — enabling multi-user 4K streaming, cloud gaming, and business-grade VPN performance — but realistic expectations prevent deployment disappointments.

    Conclusion

    Carrier aggregation is the defining performance feature of 5G FWA CPE. The difference between a well-executed CA architecture and a checklist-driven implementation can be a 2× gap in real-world throughput, coverage, and operator satisfaction. Technical buyers should move beyond counting component carriers and rigorously evaluate sustained performance, thermal behavior, DSS interoperability, and alignment with operator spectrum roadmaps.

    At Honlly Telecom, our 5G CPE portfolio spans entry-level 2× CA devices to premium 8× CA multi-gigabit platforms, all validated through extensive field testing with Tier-1 operators across Asia, Europe, and the Middle East. Contact our product team for detailed CA combination lists, throughput validation reports, and deployment case studies tailored to your spectrum environment.

  • 5G-Advanced CPE Commercialization Accelerates: 3GPP Release 18 Features Drive Next-Generation FWA Performance in H2 2026

    5G-Advanced CPE Commercialization Accelerates: 3GPP Release 18 Features Drive Next-Generation FWA Performance in H2 2026

    The 5G ecosystem is entering a new phase. As operators worldwide transition from early 5G Non-Standalone (NSA) deployments toward full 5G Standalone (SA) architectures, the 3GPP Release 18 specification — the first release under the 5G-Advanced banner — is driving a new wave of CPE innovation. In the second half of 2026, chipset vendors, CPE manufacturers, and Tier-1 operators are aligning around Release 18 features that promise meaningful improvements in spectral efficiency, uplink performance, energy consumption, and network intelligence for Fixed Wireless Access (FWA) deployments.

    Why 5G-Advanced Matters for CPE

    5G-Advanced represents more than an incremental upgrade. It introduces foundational enhancements that directly impact CPE design and end-user experience:

    Enhanced MIMO and Beamforming. Release 18 refines Multi-User MIMO (MU-MIMO) with support for up to 32 layers and introduces enhanced Channel State Information (CSI) feedback mechanisms. For CPE devices, this translates to more consistent throughput at cell edges — historically a pain point for FWA subscribers in suburban and rural deployments. Beam management enhancements reduce handover latency and improve reliability for fixed-wireless subscribers, even in non-line-of-sight conditions.

    AI/ML-Native Air Interface. One of Release 18’s most significant contributions is the standardization of AI/ML-based channel estimation, beam prediction, and positioning. CPE devices equipped with Release 18-compliant modems can leverage network-side AI models for real-time link adaptation, reducing the overhead of traditional pilot-based estimation and freeing up spectral resources for user data.

    Extended Reality (XR) and Deterministic Networking. Release 18 introduces QoS enhancements tailored for XR and cloud gaming traffic. For CPE vendors targeting the premium home broadband segment, support for bounded latency and jitter guarantees becomes a competitive differentiator — especially as operators bundle FWA with IPTV, cloud gaming, and VR content services.

    NR Sidelink Evolution. While traditionally associated with V2X and direct device-to-device communication, sidelink enhancements in Release 18 open new use cases for CPE mesh networking in multi-dwelling units (MDUs) and enterprise campuses. A primary CPE unit can relay connectivity to secondary nodes over sidelink, extending coverage without additional backhaul.

    Chipset Roadmap: Qualcomm, MediaTek, and UNISOC

    The semiconductor pipeline reflects the urgency of 5G-Advanced commercialization:

    Qualcomm has announced its Snapdragon X80 5G Modem-RF system with integrated Release 18 support, featuring a dedicated AI tensor accelerator for on-device channel optimization and a 6x carrier aggregation capability targeting peak downlink speeds exceeding 10 Gbps. – MediaTek is positioning its T800-series modem for the FWA CPE segment, emphasizing power efficiency and integrated NTN (Non-Terrestrial Network) support for hybrid satellite-terrestrial CPE designs. – UNISOC is targeting the value-tier CPE market with Release 18-ready platforms optimized for sub-6 GHz spectrum, addressing price-sensitive operators in emerging markets.

    CPE manufacturers now face a strategic choice: adopt Release 18 silicon early to capture premium operator RFPs, or optimize cost with Release 17 platforms for the volume segment. The window for Release 18 CPE design wins is opening in Q3 2026, with commercial shipment volumes expected by Q1–Q2 2027.

    Operator Deployment Momentum

    Several Tier-1 operators have signaled their 5G-Advanced FWA intentions:

    China Mobile began 5G-Advanced trials in select urban districts in June 2026, targeting a 40% improvement in FWA cell capacity through Release 18 MU-MIMO and AI-based scheduling. – T-Mobile US expanded its 5G FWA subscriber base past 7 million in Q2 2026 and has indicated that Release 18-capable CPE will be part of its 2027 device portfolio refresh. – Etisalat (e&) in the UAE announced a 5G-Advanced FWA showcase at GITEX 2026, demonstrating multi-gigabit throughput over mmWave with Release 18 carrier aggregation. – European operators, including Deutsche Telekom and Vodafone, are conducting lab trials of AI-enhanced beamforming for FWA, with field trials expected before year-end.

    CPE Design Implications

    For CPE OEMs and ODMs, Release 18 introduces specific hardware and firmware considerations:

    1. Modem Upgrades: The AI/ML Processing Unit on Release 18 modems requires additional memory bandwidth and thermal headroom. CPE thermal designs must account for sustained AI inference workloads alongside high-throughput data processing.

    2. Antenna Architecture: Enhanced MIMO with 32-layer support may push CPE antenna configurations beyond the current 4×4 MIMO standard toward 8×8 for premium CPE models — particularly for mmWave and upper mid-band deployments.

    3. Software Complexity: AI/ML model lifecycle management, OTA model updates, and interoperability with multi-vendor gNB implementations add significant software validation overhead. CPE vendors with strong software integration capabilities will have an advantage.

    4. Power Budget: Deterministic networking and XR optimizations may increase sustained power draw. Energy-efficient designs — including advanced sleep modes defined in Release 18 — will be critical for operator acceptance in markets with strict energy regulations.

    What This Means for Buyers and Operators

    For operators evaluating CPE procurement through 2027, the 5G-Advanced transition presents both opportunity and risk. Early adopters of Release 18 CPE can differentiate on network performance and future-proof their FWA subscriber base. However, premium pricing for first-generation Release 18 silicon may challenge ROI models in price-sensitive segments.

    For enterprise and wholesale buyers, the key takeaway is that 5G-Advanced CPE is not a “wait-and-see” technology. Devices arriving in H2 2026 are built on mature Release 18 specifications with multi-year operator roadmaps behind them. Procurement teams should begin evaluating Release 18 CPE specifications now — particularly around AI/ML feature sets, MIMO configuration, and power efficiency — to align with operator network upgrade timelines.

    The 5G-Advanced era is not a distant horizon. It is shipping in silicon today, and the CPE products built on that silicon will define the FWA competitive landscape for the next three years.

    For more information about Honlly Telecom’s 5G CPE product roadmap and 5G-Advanced-ready devices, contact our sales team or visit our product catalog.

  • A Technical Buyer’s Guide to 5G NR RedCap CPE: Optimized Device Design for Mid-Tier IoT, Industrial Sensors, and Massive-Scale Deployments

    A Technical Buyer’s Guide to 5G NR RedCap CPE: Optimized Device Design for Mid-Tier IoT, Industrial Sensors, and Massive-Scale Deployments

    As 5G networks mature beyond flagship smartphones and high-performance FWA, the ecosystem is turning its attention to a vast middle ground of use cases that require more than LTE-M or NB-IoT can deliver, yet do not justify the cost and complexity of full-specification 5G NR devices. Enter 5G NR RedCap (Reduced Capability), standardized in 3GPP Release 17 and enhanced in Release 18, which defines a device class optimized for mid-tier IoT, industrial wireless sensors, surveillance cameras, and wearable ecosystems. This guide provides technical buyers with a detailed framework for evaluating RedCap CPE and terminal solutions.

    What 5G NR RedCap Actually Reduces—and What It Preserves

    RedCap is not simply “5G-lite.” It is a carefully engineered device simplification that targets a specific performance envelope while preserving core 5G NR capabilities that differentiate it from LTE-based IoT technologies. The key reductions relative to full-spec NR devices (FR1) include:

    • Reduced Bandwidth: Maximum 20 MHz in FR1 (vs. 100 MHz for full NR), with mandatory support for 5 MHz and optional 10 MHz configurations. This simplification reduces RF front-end complexity, ADC/DAC requirements, and baseband processing demands significantly.
    • Reduced Antenna Configuration: 1 Rx or 2 Rx branches (vs. mandatory 4 Rx for full NR FR1). For many industrial sensor and wearable applications, 1 Rx is sufficient, though 2 Rx is recommended for FWA-type RedCap CPE to support basic receive diversity.
    • Half-Duplex FDD Support: Optional half-duplex FDD operation, eliminating the need for duplex filters and further reducing component count and cost for devices that can tolerate non-simultaneous transmission and reception.
    • Relaxed Processing Timeline: Extended processing timelines that reduce baseband computational requirements, enabling lower-cost modem silicon without compromising reliability.

    Critically, RedCap preserves: 5G NR waveform and numerology (OFDM with flexible subcarrier spacing); network slicing support (URSP); 5G core network integration; 5G security architecture (SUPI concealment, 5G-AKA, EAP-AKA’); and positioning enhancements. These retained capabilities mean RedCap devices are first-class citizens on the 5G network, not a separate IoT overlay.

    RedCap vs. eRedCap: The Release 18 Expansion

    3GPP Release 18 introduced “eRedCap” (enhanced RedCap), which further narrows the device complexity gap toward LTE Cat-1/Cat-4 territory while remaining within the 5G NR framework. eRedCap targets peak data rates of approximately 10 Mbps—similar to LTE Cat-1 bis but with 5G-native network integration benefits.

    Key eRedCap features include: mandatory 5 MHz bandwidth support (10 MHz maximum, 5 MHz minimum for FR1); further reduced peak data rates through transport block size limitations and relaxed MIMO layer counts; and optional support for device-specific bandwidth part (BWP) configurations that allow the network to schedule RedCap devices within a narrower portion of the carrier bandwidth while full NR devices use the entire carrier.

    For CPE and terminal buyers, the RedCap/eRedCap continuum creates a device hierarchy that maps cleanly to specific use cases: standard RedCap for fixed wireless sensors, industrial cameras, and gateways requiring 50–150 Mbps; eRedCap for wearable devices, asset trackers, and environmental sensors needing 5–10 Mbps with minimal power consumption and lowest possible BOM cost.

    RedCap CPE Architecture: System Design Considerations

    Designing a RedCap CPE or terminal requires a fundamentally different approach than downsizing a full-spec 5G CPE. The optimizations are architectural, not merely subtractive:

    Modem Selection: The Qualcomm Snapdragon X35 5G Modem-RF system, announced in early 2023 and now shipping in volume, was purpose-built for RedCap rather than derived from a full NR platform. Competing solutions from MediaTek (T300 series) and UNISOC are also reaching production maturity. Purpose-built RedCap modems offer 40–60% lower power consumption and 30–50% smaller PCB footprint compared to full NR modems configured in reduced mode.

    RF Front-End Simplification: The 20 MHz bandwidth limit means the RF front-end can use narrower-band LNAs and PAs with relaxed linearity requirements, surface acoustic wave (SAW) filters instead of bulk acoustic wave (BAW) filters in many bands, and simplified antenna switch modules. This contributes to a BOM cost reduction of approximately 35–50% compared to full-spec 5G CPE RF front-ends.

    Power Architecture: RedCap devices targeting battery-powered or energy-harvesting operation can leverage 3GPP Release 17 power-saving enhancements including: extended Discontinuous Reception (eDRX) with significantly longer sleep cycles than LTE-M; Radio Resource Management (RRM) relaxation for stationary devices to reduce measurement overhead; and Paging Early Indication (PEI) to skip unnecessary PDCCH monitoring.

    Thermal Design: Lower baseband processing complexity and reduced RF power translate to approximately 50–70% lower thermal output compared to full NR CPE, enabling fanless, sealed industrial enclosures suitable for harsh outdoor and factory-floor environments where active cooling is prohibited.

    Use Case Deep Dive: Industrial Wireless Sensor Networks

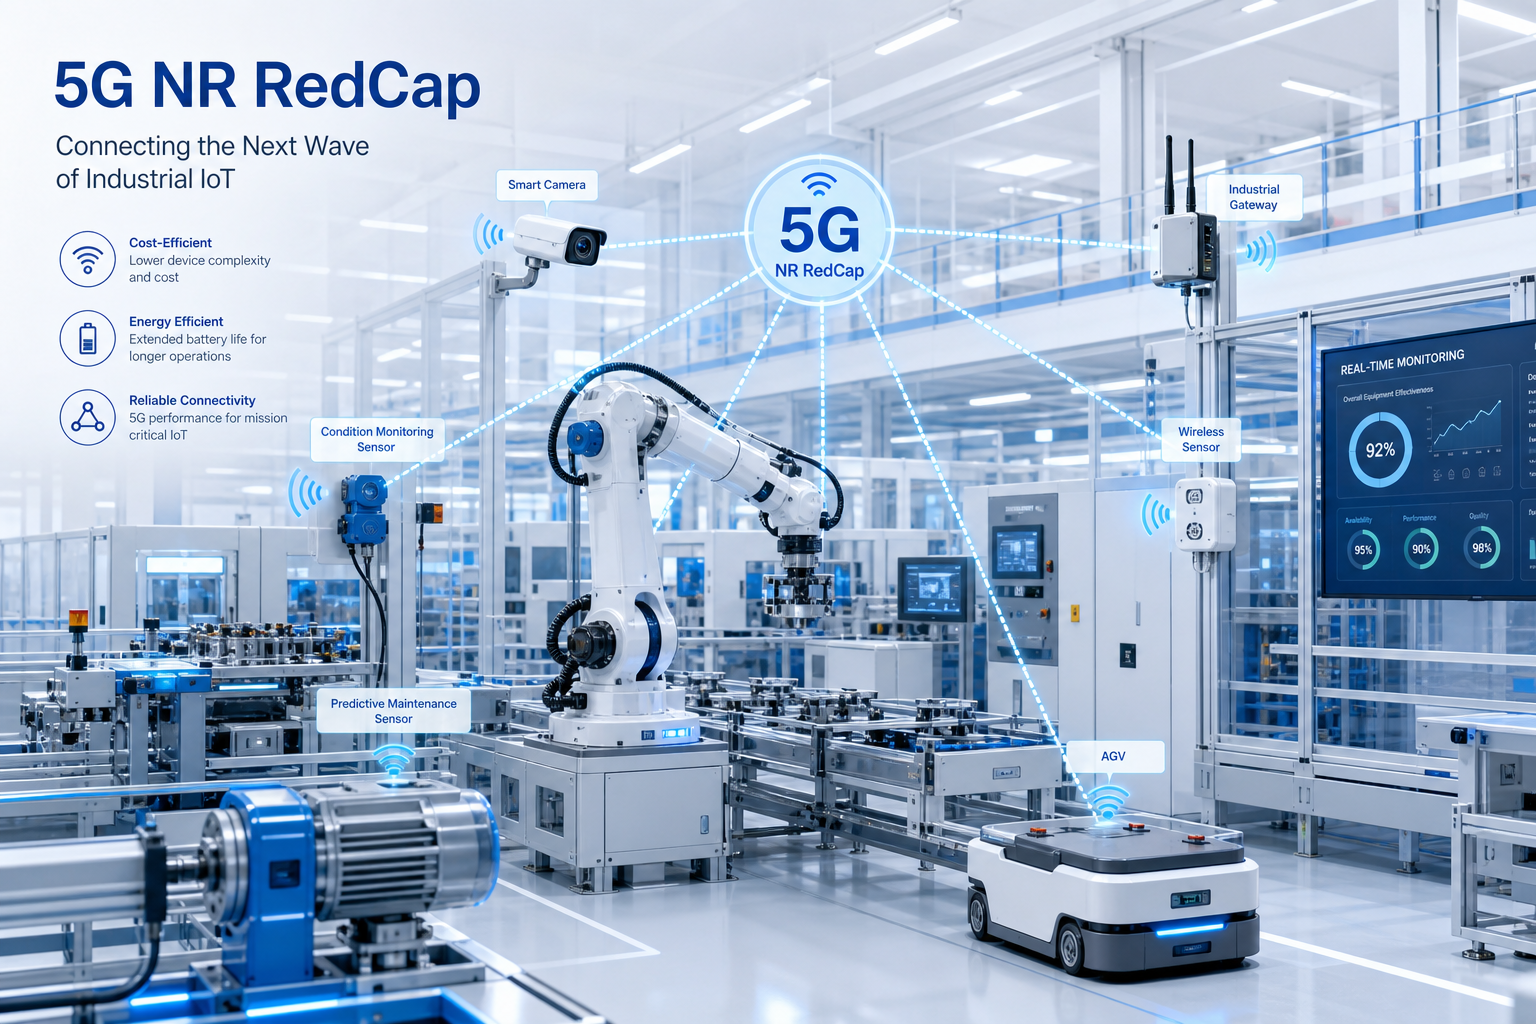
    One of the most compelling RedCap CPE applications is as an aggregation gateway for industrial wireless sensor networks in smart manufacturing environments. In this architecture, a RedCap CPE serves as the 5G backhaul endpoint for an on-premise sensor mesh (e.g., IO-Link Wireless, WirelessHART, or proprietary ISM-band sensor protocols), providing a managed bridge between the factory sensor layer and the 5G core network.

    The RedCap CPE in this role requires: industrial protocol conversion capability (Modbus TCP, PROFINET, EtherNet/IP to 5G data plane); deterministic latency guarantees via 5G network slicing and TSN (Time-Sensitive Networking) integration; ruggedized IP65 or higher enclosure with M12 connectors for industrial power and Ethernet; and support for IEEE 802.1CB Frame Replication and Elimination for Reliability (FRER) for ultra-reliable low-latency applications.

    The economic case is compelling: a RedCap-based sensor gateway at approximately 40% of the cost of a full-spec 5G industrial CPE, with sufficient throughput for aggregating hundreds of sensor streams at typical industrial data rates of 1–10 Mbps total backhaul traffic.

    Procurement Considerations for RedCap CPE

    Technical buyers evaluating RedCap 5G CPE should address the following decision points:

    • Band Support: Confirm RedCap band support aligns with deployment regions. While full NR devices support dozens of bands, RedCap devices typically support a targeted subset (Bands n1, n3, n5, n7, n8, n28, n38, n40, n41, n77, n78, n79). Verify specific band combinations with carrier aggregation support if required for throughput targets.
    • Rx Diversity: For fixed wireless sensor gateways with challenging RF environments (basements, metal enclosures, factory floors), specify minimum 2 Rx for basic receive diversity. Single Rx configurations are acceptable for outdoor pole-mounted units with line-of-sight to the cell site.
    • Network Slicing: URSP (UE Route Selection Policy) support is mandatory for industrial RedCap CPE to ensure traffic separation between critical control plane data and bulk telemetry. Verify the modem and device firmware support URSP rules with at least 8 concurrent PDU session support.
    • Positioning: For asset tracking and logistics applications, verify support for 5G NR positioning methods (DL-TDOA, UL-TDOA, Multi-RTT) available in Release 17/18, with sub-meter accuracy targets for indoor deployments.
    • Certification Roadmap: RedCap device certification through GCF/PTCRB is still maturing. Confirm that target operator(s) have completed RedCap network feature verification and that the device vendor has a clear certification timeline with committed conformance test coverage.
    • eRedCap Migration Path: For deployments planning volume scaling over 3–5 years, evaluate whether the CPE platform supports a pin-compatible upgrade to eRedCap modems as the technology matures and use cases evolve toward lower data rates and power consumption profiles.

    Market Outlook and Ecosystem Maturity

    The RedCap ecosystem is crossing the chasm from early-adopter trials to commercial scale in H2 2026. Operator support has expanded rapidly: China Mobile, China Telecom, and China Unicom have all completed RedCap commercial network verification and launched RedCap-specific data plans; AT&T and T-Mobile US are conducting enterprise trials with industrial and logistics customers; and major European operators including Deutsche Telekom, Vodafone, and BT/EE have activated RedCap on a portion of their 5G SA networks.

    ABI Research forecasts that RedCap/eRedCap device shipments will reach 85 million units annually by 2028, with industrial IoT and fixed wireless sensor gateways representing the largest single segment at approximately 40% of volume. The CPE and terminal segment within RedCap is projected to grow from approximately 1.2 million units in 2026 to over 8 million units by 2029.

    For procurement organizations planning mid-tier IoT and industrial connectivity strategies, 2026 H2 represents the inflection point where RedCap CPE transitions from technology evaluation to deployment-ready procurement. The devices shipping today are purpose-built, carrier-certified, and economically viable—the key remaining question is ecosystem scale, not technical readiness.

  • A Technical Buyer’s Guide to 5G CPE eSIM and Multi-IMSI Architecture: Remote SIM Provisioning, Profile Management, and Operator Flexibility

    A Technical Buyer’s Guide to 5G CPE eSIM and Multi-IMSI Architecture: Remote SIM Provisioning, Profile Management, and Operator Flexibility

    As 5G FWA deployments scale across multiple operators and geographies, the SIM architecture embedded within CPE devices has evolved from a simple authentication token into a strategic enabler of deployment flexibility, operational efficiency, and long-term lifecycle management. This technical buyer’s guide examines the eSIM and Multi-IMSI architectures now being integrated into enterprise-grade 5G CPE platforms, providing procurement teams with the technical framework needed to evaluate solutions for multi-operator, multi-region, and future-proof FWA deployments.

    The Evolution from Physical SIM to eSIM in CPE

    Traditional 5G CPE devices relied on removable UICC (Universal Integrated Circuit Card) formats—typically 2FF (Mini-SIM) or 4FF (Nano-SIM) physical cards. While functional, this approach introduced significant operational friction: truck rolls for SIM swaps during operator changes, physical SIM inventory management across distribution channels, vulnerability to theft and tampering, and limited ability to dynamically re-provision connectivity profiles in response to network conditions or commercial agreements.

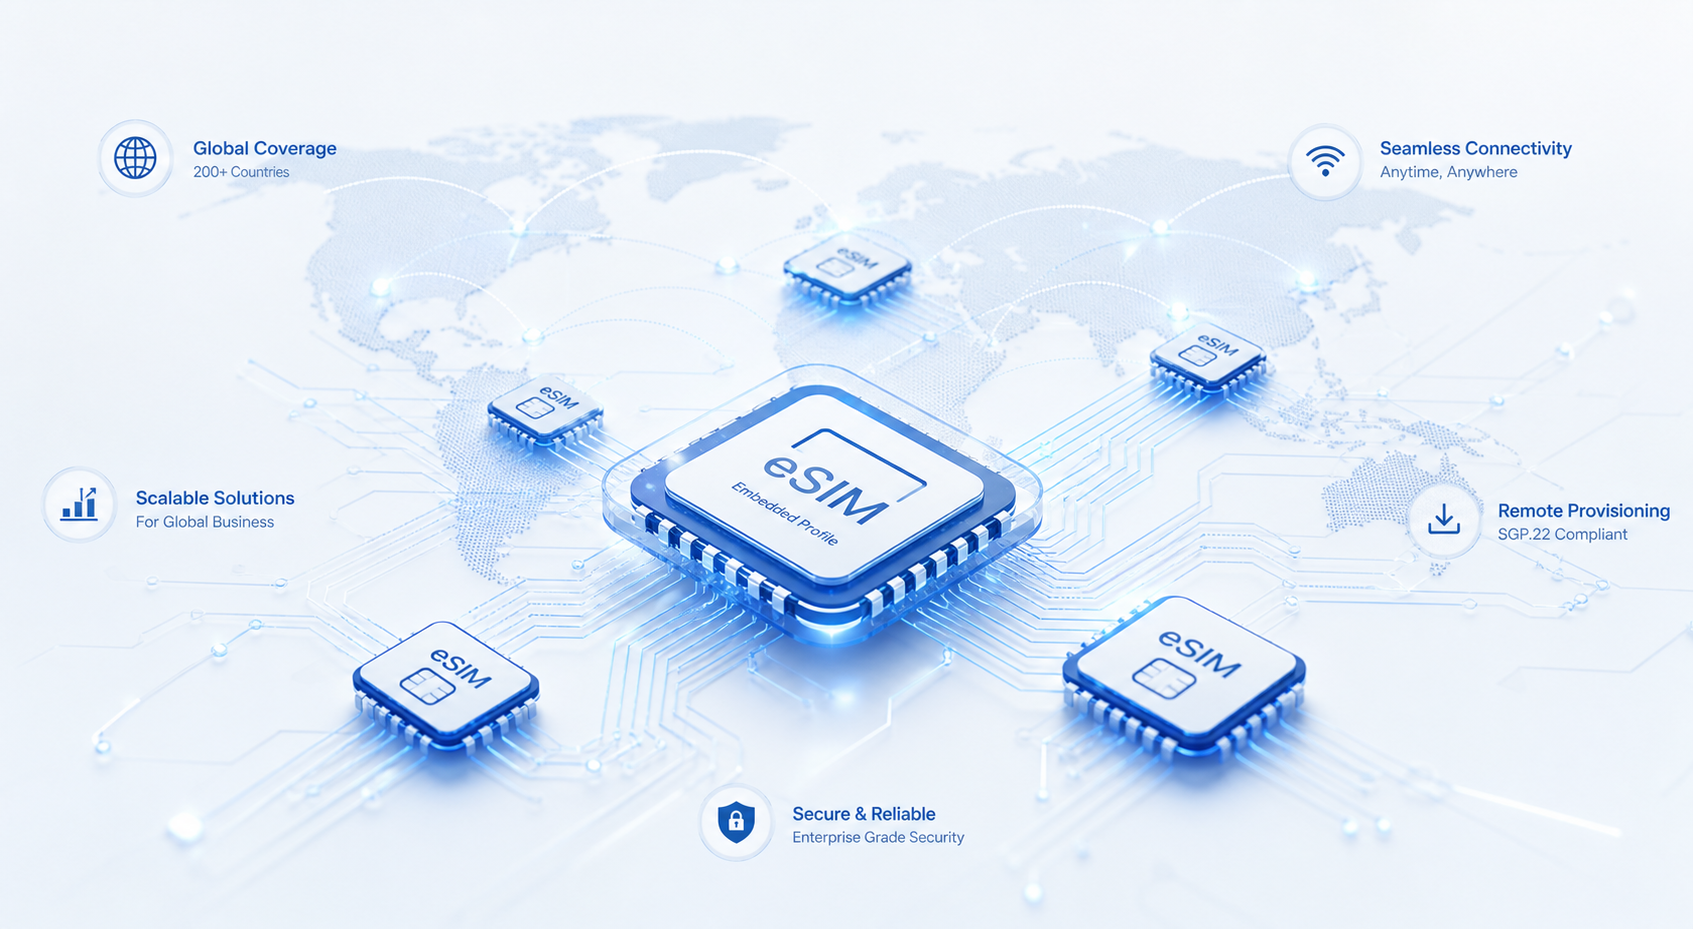
    The GSMA’s eSIM specifications—particularly GSMA SGP.02 (M2M) and SGP.22 (Consumer) architectures—have matured to address these pain points for CPE deployments. An eSIM (embedded UICC or eUICC) is a soldered, non-removable SIM chip that supports remote SIM provisioning (RSP), enabling operators to download, enable, disable, and delete operator profiles over-the-air without physical access to the device.

    The SGP.22 Consumer architecture, originally designed for smartphones and wearables, has proven particularly suitable for 5G CPE. It supports a “pull” model where the device initiates profile download via an SM-DP+ (Subscription Manager – Data Preparation+) server, activated through a QR code or activation code delivered via the operator’s mobile app or web portal. This consumer-friendly activation flow is increasingly adopted for residential FWA CPE, enabling self-install and zero-touch provisioning.

    For enterprise and industrial CPE deployments, the SGP.02 M2M architecture offers a “push” model where profiles are provisioned remotely by the operator via an SM-DP (Subscription Manager – Data Preparation) server, with minimal end-user interaction. This architecture supports bulk provisioning, scheduled profile switching, and integration with operator OSS/BSS systems—critical capabilities for deployments with thousands of distributed CPE endpoints.

    Multi-IMSI Architecture: Operational Flexibility for Roaming and Multi-Operator Deployments

    While eSIM enables remote profile management, Multi-IMSI (Multiple International Mobile Subscriber Identity) architecture extends the concept by allowing a single device to hold multiple active operator profiles simultaneously, with intelligent switching logic that selects the optimal profile based on configurable policies.

    A Multi-IMSI 5G CPE typically integrates a eUICC with support for multiple IMSI/applet combinations, managed through a SIM applet framework running on the UICC’s Java Card platform. The device maintains several operator profiles—each containing its own IMSI, authentication keys (Ki), OPC, and network parameters—with an applet that monitors network availability and switches active profiles based on rules such as:

    • Geographic Location: Automatically select the home network profile when on the home PLMN, switch to a roaming partner profile when abroad to achieve local-rate data pricing
    • Network Quality: Switch to an alternate operator profile if the primary network’s signal quality or throughput falls below defined thresholds
    • Time-Based Scheduling: Use a specific operator profile during business hours for guaranteed SLA performance, switch to a lower-cost profile outside peak hours
    • Application-Based Steering: Route critical enterprise traffic through one operator while offloading bulk data to another

    This Multi-IMSI capability is particularly valuable for: cross-border deployments where a single CPE model must operate across multiple countries; maritime and logistics applications where vessels and containers traverse multiple territorial waters; and enterprise branch offices requiring redundant WAN connectivity with automatic failover between operators.

    GSMA eSIM Compliance and Certification Considerations

    Procurement teams evaluating eSIM-enabled 5G CPE should verify compliance with the relevant GSMA specifications based on deployment use case:

    • SGP.02 v4.2: M2M eSIM architecture with push-based provisioning; required for enterprise/industrial CPE managed through operator OSS/BSS platforms
    • SGP.22 v3.0: Consumer eSIM architecture with pull-based provisioning; suitable for residential and SOHO CPE with end-user self-activation
    • SGP.32 v1.0: IoT eSIM specification; increasingly relevant for massive IoT deployments with constrained devices and LPWA connectivity

    GSMA SAS (Security Accreditation Scheme) certification for the eUICC manufacturer and SM-DP+ provider is essential. SAS-UP (UICC Production) certifies the secure manufacturing and personalization process for eUICCs, while SAS-SM (Subscription Management) certifies the security of the RSP platform infrastructure. Devices integrating non-certified eSIM components face interoperability risks and potential operator rejection during certification.

    Security Architecture: Mutual Authentication and Profile Isolation

    The eSIM security model builds on the proven 3GPP AKA (Authentication and Key Agreement) framework while adding eUICC-specific protections. Key security considerations include:

    ISD-R (Issuer Security Domain – Root): The root security domain on the eUICC, managed by the eUICC manufacturer (EUM), responsible for creating and managing ISD-Ps (Issuer Security Domain – Profiles). The ISD-R private key never leaves the eUICC secure element, ensuring that only authorized entities can manage profiles.

    Profile Interlock and Isolation: Each operator profile operates within its own ISD-P, providing cryptographic isolation between profiles. One operator’s profile cannot access another’s credentials or network parameters. This is critical for scenarios where the CPE may switch between competing operators.

    CI (Certificate Issuer) Trust Chain: GSMA’s Certificate Issuer root of trust ensures that only authenticated SM-DP+ servers can communicate with the eUICC for profile operations. Buyers should confirm that the eUICC vendor participates in the GSMA CI program and supports the latest ECC (Elliptic Curve Cryptography) key algorithms in addition to legacy RSA.

    Integration with 5G CPE Platform Architecture

    From a system integration perspective, the eSIM/Multi-IMSI subsystem must interface with several CPE platform components:

    • Modem Baseband: The modem must support eUICC ISO 7816 interface or SPI-based eUICC connections, with modem firmware capable of hot-swapping IMSI/applet sessions without requiring a full modem reset—a non-trivial requirement that varies significantly between modem vendors
    • Device Management Client: Integration with TR-369 USP or LwM2M device management agents to enable remote profile management operations through standardized APIs, including profile enable/disable, profile list query, and profile download initiation
    • Local Management UI/API: A web GUI or mobile app interface for end-users or field technicians to initiate profile downloads (e.g., scan a QR code), view active profile information, and manage basic eSIM settings

    Procurement Checklist for eSIM/Multi-IMSI 5G CPE

    When evaluating 5G CPE solutions with eSIM and Multi-IMSI capabilities, technical buyers should verify the following specifications:

    • eUICC compliance: GSMA SGP.02 and/or SGP.22 certified, with SAS-UP accreditation
    • Number of simultaneously stored operator profiles: minimum 3 profiles for Multi-IMSI use cases; 5+ preferred for global deployments
    • Profile switching time: target under 30 seconds for seamless failover; modem vendors’ support for hot-swap without full baseband re-initialization should be confirmed
    • RSP platform interoperability: verified against major SM-DP+ providers (IDEMIA, G+D, Thales, Kigen, Valid) used by target operators
    • Fallback physical SIM slot: dual-SIM architecture with one eSIM and one physical SIM slot provides maximum deployment flexibility during eSIM ecosystem transition periods
    • Remote management API compliance: TR-369 USP or equivalent for operator-managed profile operations
    • Security certification: CC EAL4+ or higher for eUICC secure element; GSMA SAS-SM for the RSP infrastructure

    The transition to eSIM and Multi-IMSI architectures in 5G CPE represents a foundational shift in how connectivity is provisioned, managed, and monetized. For operators and enterprises deploying FWA at scale, selecting the right SIM architecture today will determine deployment agility, operational cost structure, and vendor flexibility for years to come.

  • Wi-Fi 7 Integrated 5G CPE Gains Momentum as Operators Target Multi-Gigabit Home Broadband Experience in H2 2026

    Wi-Fi 7 Integrated 5G CPE Gains Momentum as Operators Target Multi-Gigabit Home Broadband Experience in H2 2026

    The convergence of 5G Fixed Wireless Access and Wi-Fi 7 is reshaping the home broadband landscape as operators worldwide prepare device roadmaps targeting multi-gigabit throughput and ultra-low latency for premium residential and SOHO segments. With Wi-Fi 7 (IEEE 802.11be) chipsets reaching volume production maturity in Q2 2026, 5G CPE vendors are racing to integrate the new standard into their flagship FWA gateways, promising a step-change in in-home wireless performance that matches the multi-gigabit WAN capabilities of 5G-Advanced networks.

    Wi-Fi 7 Meets 5G: The Technical Synergy

    Wi-Fi 7 introduces several transformative features that align directly with 5G FWA use cases. Multi-Link Operation (MLO) enables simultaneous aggregation across 2.4 GHz, 5 GHz, and 6 GHz bands, delivering aggregate throughput exceeding 30 Gbps while reducing latency to sub-2 ms under optimal conditions. When paired with a 5G CPE capable of 4CC Carrier Aggregation delivering 4–6 Gbps on the WAN side, the combined system eliminates the traditional bottleneck where Wi-Fi 6 routers struggled to distribute gigabit-plus WAN bandwidth across multiple client devices.

    “The industry is moving from ‘good enough’ Wi-Fi to ‘no compromise’ Wi-Fi,” explains Dr. Lin Wei, Senior Director of Wireless Product Strategy at Honlly Telecom. “Operators investing in 5G FWA with peak rates above 2 Gbps need Wi-Fi 7 CPE to monetize that capacity inside the home. Otherwise the last 30 feet becomes the bottleneck.”

    Key Wi-Fi 7 features driving CPE design decisions include: 320 MHz channel bandwidth support on the 6 GHz band, doubling the maximum channel width from Wi-Fi 6E’s 160 MHz; 4096-QAM modulation, increasing spectral efficiency by approximately 20% over Wi-Fi 6’s 1024-QAM; and Multi-Resource Unit (MRU) allocation, which significantly improves spectrum utilization in dense multi-client environments typical of smart homes with 50+ connected devices.

    Operator Deployment Roadmaps and Silicon Ecosystem

    The silicon ecosystem has matured rapidly. Qualcomm’s Networking Pro 1620 and 1220 platforms, Broadcom’s BCM6765/BCM4775 series, and MediaTek’s Filogic 880/880 Pro are all in volume production, with reference designs optimized for 5G CPE integration. These platforms natively support the Wi-Fi 7 feature set including MLO, 4K-QAM, and preamble puncturing, while maintaining backward compatibility with Wi-Fi 6/6E and earlier client devices—a critical requirement for mass-market deployments where legacy device support is non-negotiable.

    Several Tier-1 operators have launched or announced Wi-Fi 7 5G CPE products in H1 2026. KT Corporation in South Korea deployed Wi-Fi 7 integrated FWA gateways alongside its 5G-Advanced commercial launch in March 2026, targeting 3 Gbps guaranteed home throughput. T-Mobile US announced its “Home Internet Plus” tier with a Wi-Fi 7 capable gateway in April 2026, while European operators including Deutsche Telekom, Vodafone, and Orange have all signaled Wi-Fi 7 CPE requirements in their 2026 H2 procurement RFPs.

    In China, the MIIT’s promotion of “5G + Wi-Fi 7” dual-gigabit home broadband has accelerated CPE innovation. China Mobile’s 2026 FWA terminal procurement specification includes mandatory Wi-Fi 7 support for premium-tier devices, with volume purchases expected to exceed 2 million units in the second half of the year alone.

    Enterprise and SOHO Market Impact

    Beyond residential FWA, Wi-Fi 7 5G CPE is gaining traction in the small-office/home-office (SOHO) and branch-office segments. The combination of 5G WAN connectivity with Wi-Fi 7 LAN capabilities creates a compelling “office-in-a-box” solution: a single device providing multi-gigabit internet access, secure VLAN segmentation for guest and corporate traffic, and deterministic low-latency wireless for video conferencing and cloud collaboration workloads.

    Enterprise features increasingly expected in Wi-Fi 7 5G CPE include: WPA3 Enterprise security with 802.1X authentication; support for up to 16 SSIDs with per-SSID QoS policies; integrated DPI-based application recognition; and cloud-managed provisioning via TR-369 USP. These capabilities position the Wi-Fi 7 CPE as a legitimate branch-office networking platform rather than merely a consumer-grade access point.

    Power Efficiency and Thermal Design Challenges

    One underappreciated challenge in Wi-Fi 7 5G CPE design is power consumption and thermal management. Wi-Fi 7 radios operating at full 320 MHz channel width with 4×4 MIMO can consume 6–8 watts per band, while the 5G modem subsystem adds another 4–6 watts under heavy load. Combined peak power draw of 15–20 watts pushes thermal design limits for passively cooled consumer devices, requiring innovative heat dissipation solutions including vapor chambers, graphite thermal interface materials, and optimized airflow chassis designs.

    Honlly Telecom and other CPE vendors are addressing this through advanced power management schemes that dynamically adjust Wi-Fi 7 channel widths, MIMO configurations, and transmit power based on actual client demand rather than theoretical maximums, achieving 30–40% power savings in typical usage scenarios without perceptible performance degradation.

    Market Outlook: H2 2026 and Beyond

    Industry analysts project that Wi-Fi 7 will account for over 25% of all 5G FWA CPE shipments by Q4 2026, rising to more than 60% by end of 2027. The ASP premium for Wi-Fi 7 over Wi-Fi 6 is expected to narrow from approximately $35–45 today to $15–20 by mid-2027 as silicon volumes scale and competition intensifies among chipset vendors.

    For operators, Wi-Fi 7 5G CPE represents a strategic opportunity to differentiate premium service tiers, reduce churn through superior in-home experience, and capture additional ARPU from multi-gigabit speed tiers. For CPE vendors, it represents both a technology race and a market expansion opportunity—one that will define the competitive landscape of the FWA device market for the next product generation cycle.

  • Global 5G FWA Subscriber Base Tops 230 Million as Operators Prioritize CPE Acquisition for Rural Digital Divide Initiatives in 2026–2028

    Global 5G FWA Subscriber Base Tops 230 Million as Operators Prioritize CPE Acquisition for Rural Digital Divide Initiatives in 2026–2028

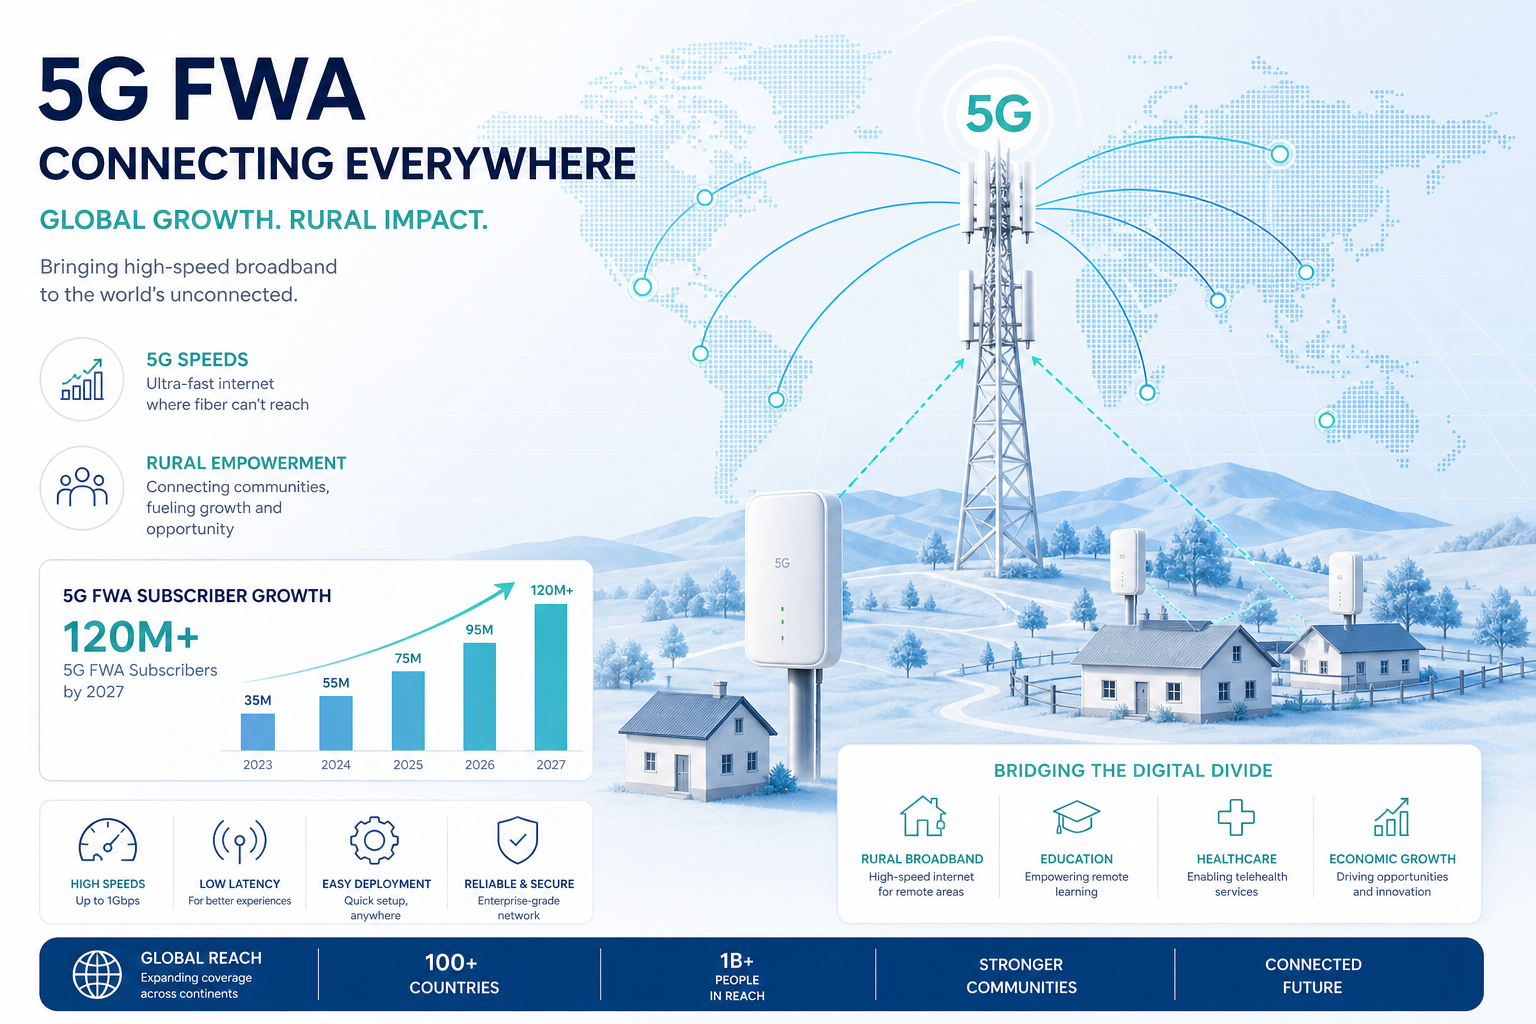
    The global 5G Fixed Wireless Access (FWA) market has crossed a critical inflection point. Industry analysts now estimate the worldwide FWA subscriber base has surpassed 230 million connections, with year-over-year growth exceeding 38% across both developed and emerging markets. This unprecedented expansion is reshaping how operators, ISPs, and government agencies approach last-mile broadband infrastructure — and CPE procurement has become the central strategic variable.

    The Numbers Behind the Surge

    According to the latest quarterly data from the GSA and Ericsson Mobility Report, 5G FWA now accounts for approximately 15% of all fixed broadband subscriptions globally. The growth is no longer concentrated in early-adopter markets like the United States, Japan, and Saudi Arabia. India, Brazil, Indonesia, Nigeria, and the Philippines have emerged as the fastest-growing regions, driven by a combination of limited fiber infrastructure, favorable spectrum allocation policies, and aggressive operator capex toward wireless last-mile solutions.

    Key market indicators include:

    • Operator commitments: Over 140 mobile network operators worldwide now offer commercial 5G FWA services, up from 92 in early 2025.
    • Device ecosystem: The number of commercially available 5G FWA CPE models has grown to over 380, spanning indoor desktop units, outdoor-mounted CPE, and industrial-grade gateways.
    • ARPU stability: Contrary to early concerns, FWA ARPU has remained competitive with fiber in most markets, with average monthly revenue of $28–$42 in developed markets and $8–$15 in price-sensitive emerging economies.
    • Spectrum utilization: Mid-band spectrum (3.5 GHz n78 and 2.6 GHz n41) accounts for 72% of FWA deployments, with mmWave (n257/n258/n261) contributing high-capacity urban overlay in 18% of operator networks.

    Rural Digital Divide: The Policy Catalyst

    Government broadband funding programs have become the single largest demand driver for 5G FWA CPE. The United States’ BEAD (Broadband Equity, Access, and Deployment) program, the European Union’s Connecting Europe Broadband Fund, India’s BharatNet Phase 3, and Brazil’s Norte Conectado initiative collectively represent over USD 45 billion in committed funding through 2028. Each of these programs explicitly includes FWA as an eligible technology pathway for serving unserved and underserved rural premises.

    For CPE vendors, this creates both opportunity and obligation. Operators participating in government-funded programs must meet stringent performance, reliability, and interoperability requirements. Devices must demonstrate sustained throughput above 100 Mbps downlink at cell edge, support IPv6/IPv4 dual-stack, and pass carrier-specific interoperability testing across multiple RAN vendor environments.

    The rural use case also places unique demands on CPE hardware design. Outdoor CPE (ODU) units must withstand extreme temperature ranges (−40°C to +55°C), IP67-rated weatherproofing, and wind loading up to 200 km/h in cyclone-prone regions. Integrated high-gain directional antenna arrays with 11–15 dBi gain are increasingly specified for long-range rural links extending beyond 12 km from the serving cell site.

    CPE Procurement Dynamics: What Operators Are Buying

    The CPE procurement landscape in 2026 reflects a maturing market with clear segmentation. Three distinct device categories dominate operator RFPs:

    1. Entry-Level Indoor CPE (USD 80–150)

    Targeted at price-sensitive mass-market deployments in emerging economies. These units typically support 4×4 MIMO on sub-6 GHz bands, deliver peak throughput of 1.5–2 Gbps, and include basic Wi-Fi 6 (802.11ax) 2×2 AP functionality. The primary design challenge is balancing cost reduction with minimum performance thresholds.

    2. Mid-Range Outdoor CPE (USD 180–350)

    The fastest-growing segment, driven by rural and suburban deployments. These self-install or technician-install outdoor units feature integrated high-gain antennas, support carrier aggregation across up to 8 component carriers, and deliver peak throughput of 3–6 Gbps. Power-over-Ethernet (PoE++) and IP67 rating are standard requirements.

    3. Premium Enterprise/Industrial CPE (USD 400–1,200)

    Designed for enterprise branch connectivity, industrial IoT backhaul, and multi-tenant residential buildings. These gateways support Wi-Fi 7, multi-gigabit Ethernet switching, SD-WAN integration, and advanced security features including hardware-rooted secure boot, IPSec/VXLAN tunneling, and Zero Trust Network Access (ZTNA) compatibility.

    Procurement decision-makers are increasingly weighting total cost of ownership (TCO) over upfront unit price. Factors such as remote management capability (TR-369 USP compliance), mean time between failures (MTBF), firmware update cadence, and vendor responsiveness to security vulnerability disclosures now feature prominently in operator scorecards.

    Supply Chain and Geopolitical Considerations

    The 5G CPE supply chain continues to diversify away from single-source dependencies. The US FCC’s Secure and Trusted Communications Networks Act, the EU’s 5G Cybersecurity Toolbox, and similar frameworks in India, Australia, and Japan have driven operators to mandate multi-source component strategies. CPE vendors with manufacturing facilities in Vietnam, India, Malaysia, and Mexico have gained competitive advantage as operators seek to reduce geopolitical concentration risk in their device supply chains.

    Chipset diversification is also accelerating, with MediaTek’s T830 and T900 platforms, Qualcomm’s Snapdragon X75 and X80 modems, and UNISOC’s Ivy 510 series now competing across multiple price-performance tiers. This broadening silicon ecosystem has reduced platform lock-in risks for CPE OEMs and enabled faster time-to-market for new device designs.

    Market Outlook: 2026–2028

    Looking ahead, several trends will shape the next phase of 5G FWA CPE market evolution:

    • 5G-Advanced (3GPP Release 18/19) integration: AI/ML-based beam management, enhanced carrier aggregation (up to 16 CC), and multi-TRP support will drive a new generation of CPE silicon arriving in late 2026.
    • Satellite-Direct-to-CPE convergence: 3GPP Release 19 NTN standards will enable hybrid terrestrial-satellite CPE capable of seamless failover to LEO satellite broadband, particularly valuable for truly remote deployments.
    • AI-native CPE management: On-device machine learning for interference detection, traffic classification, and predictive fault detection will become standard features in mid-range and premium CPE segments.
    • Sustainability mandates: Operators in the EU and Japan are beginning to require CPE vendors to disclose product carbon footprints and implement recyclable packaging and device take-back programs.

    For CPE manufacturers and telecom procurement professionals, the message is clear: the 5G FWA market is entering its high-growth phase, and device strategy — encompassing performance, cost, supply chain resilience, and lifecycle management — will determine which vendors capture share in the next wave of global broadband expansion.

    Frequently Asked Questions

    What is the current global 5G FWA subscriber count?

    As of mid-2026, the global 5G FWA subscriber base has surpassed 230 million connections, with sustained year-over-year growth above 38%. The GSA and Ericsson project the base will exceed 350 million by 2028.

    Which regions are driving the fastest FWA growth?

    While the United States, Japan, and Saudi Arabia remain large markets, the fastest growth rates are now observed in India, Brazil, Indonesia, Nigeria, and the Philippines, where limited fiber infrastructure and supportive government policies are accelerating wireless last-mile adoption.

    What CPE specifications do operators prioritize for rural FWA deployments?

    Rural FWA CPE requirements include outdoor-rated (IP67) enclosures, integrated high-gain directional antennas (11–15 dBi), support for extended-range operation beyond 12 km, wide temperature tolerance (−40°C to +55°C), and carrier aggregation across multiple bands for sustained throughput above 100 Mbps at cell edge.

    How are government broadband programs impacting CPE procurement?

    Programs such as the US BEAD initiative, EU Connecting Europe Broadband Fund, India’s BharatNet, and Brazil’s Norte Conectado collectively represent over USD 45 billion in committed funding through 2028, with FWA explicitly included as an eligible technology pathway. These programs impose strict performance and interoperability requirements on CPE vendors.

    What role does supply chain diversification play in operator CPE strategy?

    Operators are increasingly mandating multi-source component strategies and favoring CPE vendors with geographically diversified manufacturing footprints to reduce geopolitical concentration risk. Chipset diversification across MediaTek, Qualcomm, and UNISOC platforms is also accelerating.

    Looking for reliable 5G FWA CPE for your network deployment? Contact Honlly Telecom today to discuss your requirements — from entry-level indoor units to high-gain outdoor CPE and enterprise-grade gateways, we deliver carrier-tested devices engineered for global operator deployments.