Author: openclaw-Lisa-New

  • A Technical Buyer’s Guide to 5G CPE Multi-WAN and SD-WAN Integration: Link Aggregation, Failover Strategies, and Enterprise-Grade WAN Optimization

    A Technical Buyer’s Guide to 5G CPE Multi-WAN and SD-WAN Integration: Link Aggregation, Failover Strategies, and Enterprise-Grade WAN Optimization

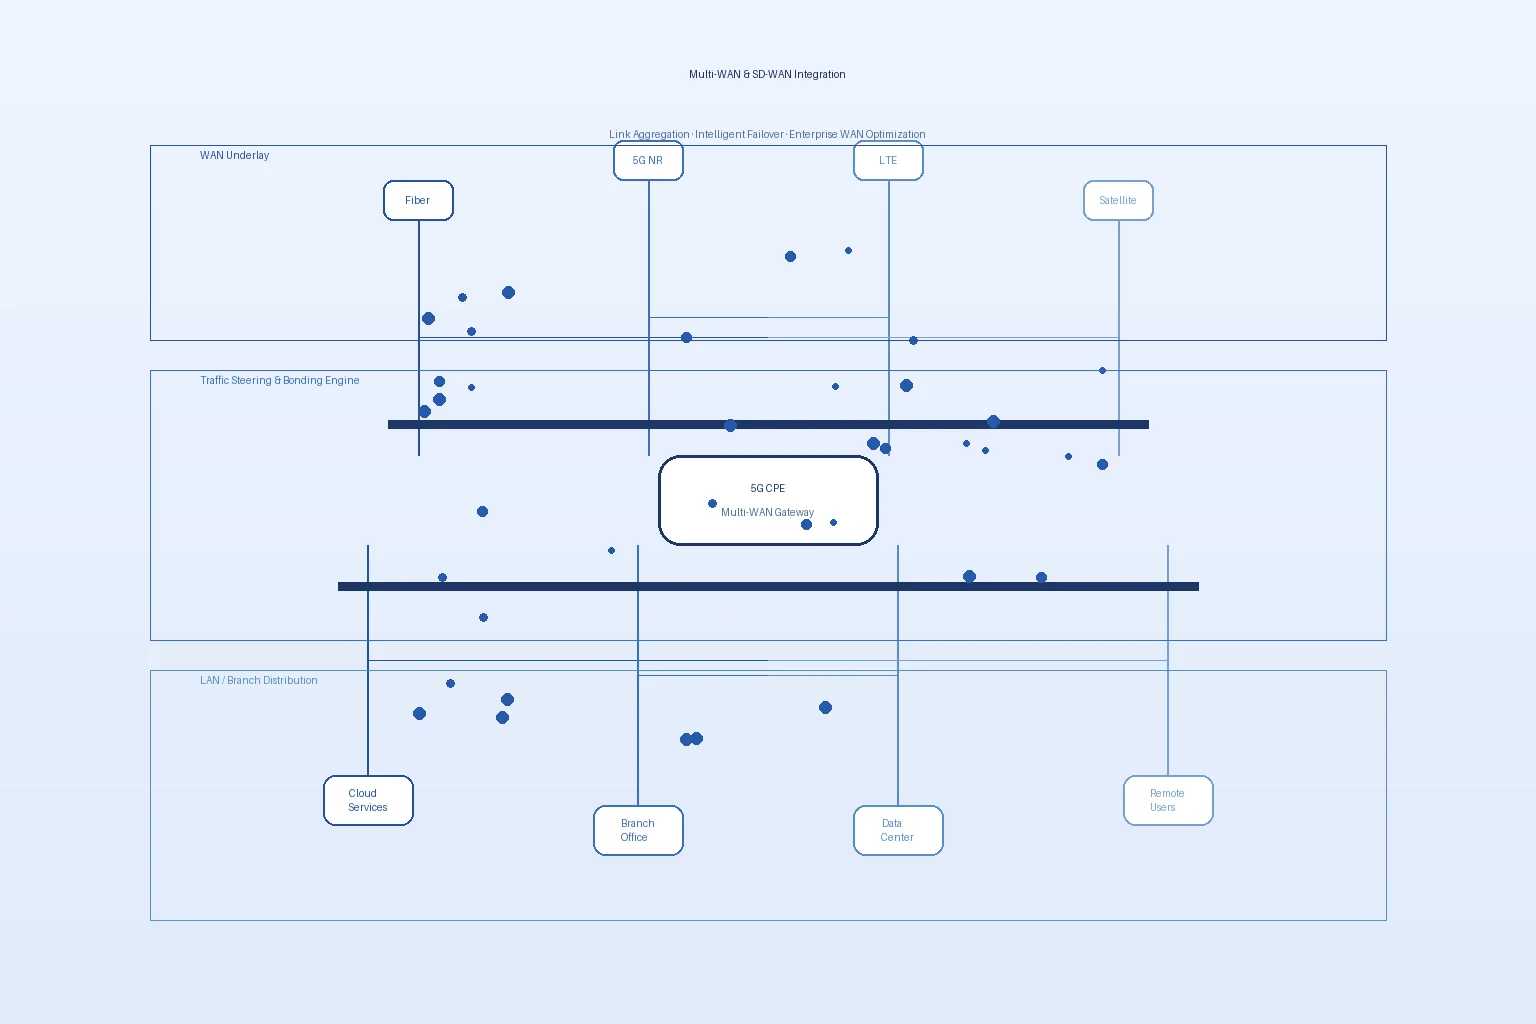
    Enterprise network architectures are increasingly defined by multi-path WAN connectivity, and the 5G CPE sits at the center of this transformation. As organizations deploy fiber, 5G FWA, LTE, and satellite links simultaneously, the CPE’s ability to aggregate, steer, and optimize traffic across heterogeneous WAN paths has become a primary procurement criterion. This guide provides a detailed technical framework for evaluating multi-WAN and SD-WAN integration capabilities in 5G CPE for B2B deployment.

    The Multi-WAN Imperative in 5G CPE

    Three enterprise networking trends are making multi-WAN CPE a non-negotiable requirement for B2B procurement in 2026:

    • Connectivity Diversity Mandates: Regulatory frameworks in financial services (Basel Committee operational resilience principles), healthcare (HIPAA contingency planning), and critical infrastructure (NIS2 Directive in Europe) increasingly require physically diverse WAN paths with automated failover. A single-carrier 5G CPE with no multi-WAN capability cannot satisfy these compliance requirements.
    • Bandwidth Aggregation Economics: Bonding a 500 Mbps fiber link with a 300 Mbps 5G FWA link provides 800 Mbps aggregate capacity at a fraction of the cost of a dedicated 1 Gbps MPLS circuit — but only if the CPE can perform per-packet or per-flow load balancing without breaking application sessions.
    • Cloud-First WAN Architecture: As enterprises shift from hub-and-spoke MPLS to direct internet access (DIA) with cloud-hosted security (SSE/SASE), the branch CPE becomes the policy enforcement point for multi-path traffic steering — a role that demands SD-WAN-grade intelligence at the CPE level.

    Link Aggregation Architectures: Bonding vs. Load Balancing

    Multi-WAN CPE platforms offer two fundamentally different approaches to combining WAN links, and procurement teams must understand the trade-offs:

    Per-Packet Link Bonding (Tunnel-Based): Traffic is encapsulated in a bonding tunnel (typically GRE, VXLAN, or proprietary protocol) and individual packets are distributed across available WAN links using round-robin or weighted distribution algorithms. This approach provides true bandwidth aggregation — a single TCP flow can utilize the combined capacity of all links — but requires a bonding endpoint (cloud gateway, headquarters concentrator, or SD-WAN hub). Vendors including Peplink (SpeedFusion), Viprinet, and Mushroom Networks specialize in this architecture.

    Per-Flow Load Balancing (Session-Based): Each application flow (identified by 5-tuple: source IP, destination IP, source port, destination port, protocol) is assigned to a single WAN link based on configurable policies. Multiple flows from the same client can use different links simultaneously, providing aggregate throughput at the site level without per-packet bonding overhead. This approach works without a remote bonding endpoint and is supported by most enterprise CPE platforms including Cradlepoint, Sierra Wireless (Semtech), and Inseego.

    Hybrid Approaches: Advanced platforms such as Peplink’s Balance series and Cisco Catalyst Cellular Gateways support both bonding (for critical applications requiring maximum throughput) and per-flow load balancing (for general internet traffic), with policy-based selection between the two modes.

    Failover Architecture: Speed, Intelligence, and Session Preservation

    Failover performance is the single most critical multi-WAN specification for enterprise procurement — and it is also the most frequently misunderstood. Key technical parameters to evaluate:

    • Failure Detection Latency: The CPE’s link health monitoring mechanism determines how quickly a WAN failure is detected. ICMP probing to multiple targets (minimum 3 diverse IP addresses) at 500ms intervals provides sub-second detection in ideal conditions. Advanced platforms supplement active probing with interface state monitoring (link-down detection in <50ms for Ethernet/SFP+ interfaces) and BFD (Bidirectional Forwarding Detection) for sub-100ms failure detection.
    • Failover Convergence Time: From failure detection to traffic flowing on the backup link, total convergence should be under 200ms for real-time applications (voice, video). Verify this under realistic conditions — loaded links, NAT state transfer, and IPsec tunnel re-establishment all add latency beyond the raw detection interval.
    • Session Persistence: Failover must preserve existing application sessions where possible. For TCP flows, this requires the CPE to maintain consistent source NAT (SNAT) IP addressing across failover — either through a shared NAT pool or by proxying connections. For IPsec VPNs, IKEv2 Mobility and Multihoming (MOBIKE, RFC 4555) enables tunnel migration without rekeying.
    • Sub-Flow Failover: In bonded multi-WAN configurations, the failure of one member link should not disrupt traffic on remaining links. Verify that the bonding protocol maintains per-packet sequence integrity during link addition/removal events.

    SD-WAN Integration Models

    The integration of 5G CPE with SD-WAN platforms follows three primary architectural models:

    Model 1 — CPE as SD-WAN Endpoint: The 5G CPE runs a full SD-WAN software stack (VMware VeloCloud, Fortinet FortiOS, Cisco vManage, Aruba EdgeConnect) directly on the device, functioning as a self-contained SD-WAN edge. This model, exemplified by Cradlepoint’s NetCloud Exchange SD-WAN and Fortinet’s FortiExtender with integrated FortiOS, provides the tightest integration but often limits SD-WAN vendor choice.

    Model 2 — CPE as Underlay with External SD-WAN: The 5G CPE operates as a transparent WAN underlay, presenting each WAN link as a separate Ethernet VLAN or routed subinterface to an external SD-WAN appliance. This model provides maximum SD-WAN vendor flexibility and is preferred by large enterprises with existing SD-WAN deployments. The CPE’s role is to provide reliable multi-WAN connectivity with L2/L3 demarcation, leaving all traffic steering and policy decisions to the SD-WAN overlay.

    Model 3 — Cloud-Orchestrated Hybrid: The CPE provides basic multi-WAN connectivity while a cloud-based orchestrator (Cradlepoint NetCloud, Cisco Catalyst Center, Juniper Mist Cloud) provides centralized policy management, traffic steering configuration, and telemetry aggregation. This model splits the difference — simpler CPE software, centralized management, but less real-time traffic steering granularity than Model 1.

    Enterprise-Grade WAN Optimization Features

    Beyond basic multi-WAN connectivity, enterprise CPE platforms increasingly integrate WAN optimization capabilities previously delivered by dedicated appliances:

    • Forward Error Correction (FEC): For bonded tunnels over lossy links (particularly satellite and mmWave 5G), packet-level FEC can recover lost packets without retransmission. Verify FEC algorithm configurability (Reed-Solomon, XOR-based) and overhead trade-offs — typical FEC overhead ranges from 5% to 20% depending on expected loss rates.
    • TCP Acceleration and Proxy: TCP performance over high-latency WAN links benefits from TCP transparent proxying with optimized congestion control (BBR v2 or equivalent). The CPE should terminate TCP connections locally and optimize the WAN-side transport independently.
    • WAN Smoothing and Jitter Buffering: For real-time UDP traffic (VoIP, video conferencing), adaptive jitter buffers and packet reordering at the CPE can mask WAN variability. Verify configurable jitter buffer depth (20–200ms) with adaptive sizing.
    • Data Deduplication and Compression: While less critical on high-bandwidth 5G links, WAN deduplication can significantly reduce data transfer volumes for repetitive enterprise traffic patterns (software updates, file synchronization, database replication). Evaluate the deduplication cache size (minimum 4 GB recommended for meaningful hit rates).

    Procurement Specifications for Multi-WAN CPE

    For RFP development in H2 2026, we recommend the following minimum specifications for enterprise-grade multi-WAN 5G CPE:

    ParameterMinimum SpecificationPreferred Specification
    WAN Interfaces1× 5G NR (3GPP R17) + 2× 2.5GbE2× 5G NR + 2× 10GbE SFP+ + 1× satellite
    Link BondingPer-flow load balancingPer-packet bonding + per-flow steering
    Failover (Detection + Convergence)< 1 second total< 200ms total with BFD
    Session PersistenceConsistent NAT across failoverMOBIKE + NAT persistence + TCP proxy
    SD-WAN IntegrationL2/L3 underlay demarcationNative SD-WAN stack + underlay mode
    FEC SupportNot requiredConfigurable Reed-Solomon FEC
    TCP AccelerationNot requiredBBR v2 TCP proxy with WAN optimization
    Management APIRESTCONF + SNMPv3RESTCONF + NETCONF + gNMI streaming telemetry

    Testing and Validation Framework

    Before finalizing multi-WAN CPE procurement, we strongly recommend lab validation of the following scenarios:

    • Hard Failover Test: Physically disconnect the primary WAN link during active VoIP calls, video conferences, and large file transfers. Measure failover time and verify session continuity for each application type.
    • Degraded Link Test: Simulate 10% and 20% packet loss on the primary link. Verify that the CPE correctly detects degradation and initiates failover or load redistribution based on configurable SLA thresholds (latency, jitter, loss).
    • Asymmetric Bandwidth Test: Combine a 1 Gbps fiber link with a 100 Mbps LTE backup link. Verify that load-balancing algorithms correctly account for asymmetric bandwidth and do not overload the lower-capacity link.
    • VPN Failover Test: Establish IPsec tunnels over all WAN links. Verify that tunnel re-establishment on failover does not introduce >5 seconds of application disruption. Validate MOBIKE support if available.
    • Management Plane Resilience: Verify that the CPE remains manageable (API accessible, telemetry streaming) during WAN failover events, including scenarios where all WAN links are briefly unavailable simultaneously.

    Procurement Recommendations

    Multi-WAN and SD-WAN integration capabilities have become defining differentiators in the 5G CPE market. For B2B buyers, the key decision is not whether to require multi-WAN support, but rather which integration model and performance tier matches their enterprise architecture. Organizations with mature SD-WAN deployments should prioritize Model 2 (underlay demarcation) for maximum flexibility. Greenfield deployments or those seeking operational simplicity may benefit from Model 1 (integrated SD-WAN endpoint) or Model 3 (cloud-orchestrated hybrid). Regardless of architecture, sub-second failover with session persistence and per-flow traffic steering should be considered table-stakes requirements for any enterprise-grade 5G CPE in 2026.
  • Global 5G FWA and LEO Satellite Convergence Gains Traction as Operators Deploy Hybrid CPE for Universal Broadband Coverage in 2026

    Global 5G FWA and LEO Satellite Convergence Gains Traction as Operators Deploy Hybrid CPE for Universal Broadband Coverage in 2026

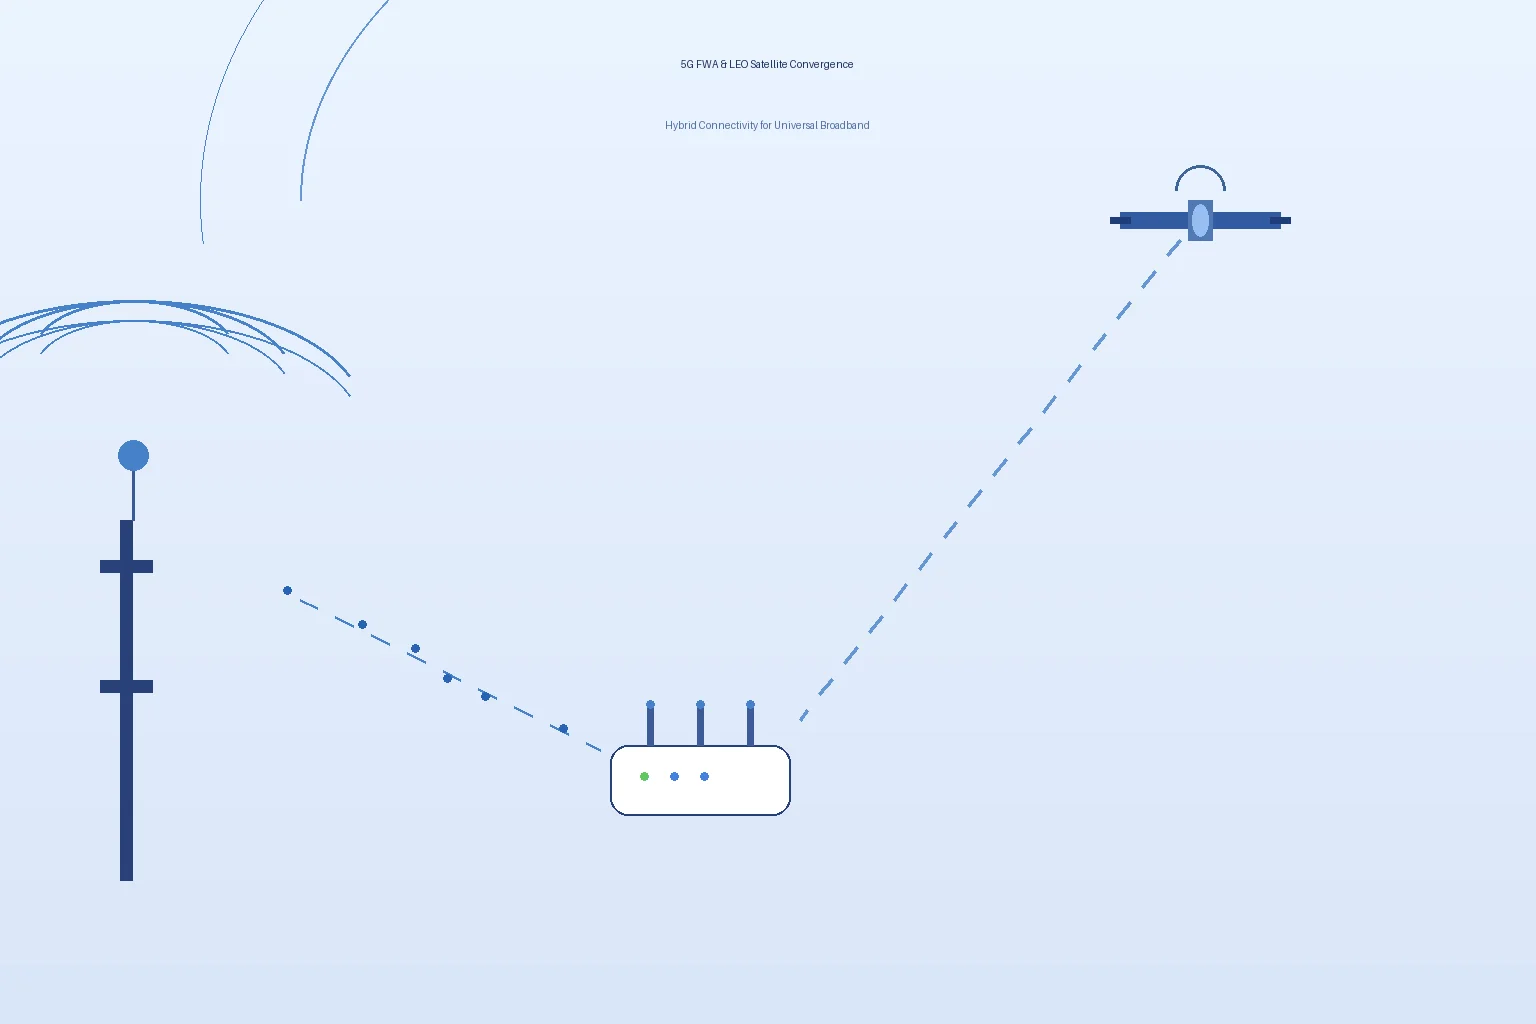
    The convergence of 5G Fixed Wireless Access (FWA) and Low Earth Orbit (LEO) satellite broadband is emerging as one of the most consequential infrastructure trends of 2026. As operators push toward universal service obligations and enterprises demand resilient multi-path connectivity, hybrid 5G-satellite CPE solutions are transitioning from proof-of-concept trials to commercial procurement frameworks — reshaping how B2B buyers evaluate next-generation CPE platforms.

    The Business Case for 5G-Satellite Convergence

    Three structural forces are converging to drive 5G-LEO integration into mainstream CPE procurement. First, universal coverage mandates in markets including Brazil, India, Indonesia, and sub-Saharan Africa are pushing operators to fill coverage gaps that terrestrial 5G alone cannot economically serve. Second, enterprise resilience requirements are escalating — financial services, energy, logistics, and remote industrial operations now routinely specify dual-path WAN architectures with physically diverse last-mile media. Third, LEO capacity is maturing rapidly: Starlink’s direct-to-cell service, Amazon Kuiper’s enterprise tier, and AST SpaceMobile’s satellite-to-unmodified-phone architecture are creating a competitive ecosystem that drives down terminal costs and expands integration options.

    For CPE procurement teams, the implication is clear: the 2026–2028 refresh cycle must account for devices that can natively bond terrestrial 5G NR with LEO satellite backhaul, not merely support them as bolt-on afterthoughts.

    Architecture Models: Integrated vs. Aggregated Hybrid CPE

    Two dominant architectural approaches are crystallizing in the market, each with distinct procurement implications:

    Integrated Hybrid CPE embeds both a 5G NR modem (3GPP Release 17/18 compliant) and a satellite modem (typically Ku/Ka-band phased-array) within a single enclosure, sharing a common processor, routing plane, and management interface. Huawei’s upcoming NetEngine 8000 FWA series and emerging ODM designs from Quectel and Fibocom are driving this category. Advantages include single-SKU procurement, unified QoS policy enforcement, and simplified installation. The trade-off is vendor lock-in and limited flexibility in satellite operator selection.

    Aggregated Hybrid CPE pairs a standalone 5G FWA CPE with an external satellite terminal via multi-gigabit Ethernet or SFP+ interconnect, with bonding intelligence residing in a separate SD-WAN edge device or cloud orchestrator. This model, championed by Cradlepoint, Peplink, and several Tier-1 SD-WAN vendors, offers operator-agnostic satellite selection and per-link SLA management. Procurement complexity increases — buyers must source, certify, and manage multiple device types — but the operational flexibility appeals to large enterprises with existing multi-vendor WAN estates.

    Key Technical Specifications for Procurement Evaluation

    B2B buyers evaluating hybrid 5G-satellite CPE should prioritize the following technical parameters in RFPs and vendor assessments:

    • 3GPP Release Compliance: Minimum Release 17 with NTN (Non-Terrestrial Network) support in the modem baseband. Release 18 NR-NTN enhancements for IoT-NTN and NR-NTN mobility should be on the vendor roadmap.
    • Multi-Link Bonding Protocol: Support for MP-TCP, ATSSS (Access Traffic Steering, Switching, and Splitting per 3GPP TS 24.193), or proprietary bonding with sub-50ms failover. Verify real-world failover latency under loaded conditions.
    • Satellite Band Support: Ku-band (10.7–12.75 GHz downlink) and Ka-band (17.7–20.2 GHz) with at least 256-element phased-array for electronic beam steering. L-band (1–2 GHz) and S-band (2–4 GHz) for direct-to-cell use cases where applicable.
    • Throughput Aggregation: Combined 5G + satellite throughput should reach minimum 2 Gbps downlink / 500 Mbps uplink in sub-6 GHz bands, scaling to 5 Gbps in mmWave+satellite configurations.
    • Power over Ethernet (PoE++): Outdoor units should support 802.3bt Type 4 (90W) PoE for single-cable installation, especially important for rooftop and tower-mounted deployments.
    • Edge Compute Capacity: Integrated application processor (ARM Cortex-A78 or equivalent) with minimum 4 GB RAM for running local traffic steering, DPI, and security functions without external appliance dependency.

    Operator and Ecosystem Developments in H2 2026

    Several recent developments signal accelerating market readiness. T-Mobile US and SpaceX have expanded their direct-to-cell beta to enterprise customers, with compatible CPE modules entering sampling from Qualcomm (Snapdragon X80 with NTN). In Asia-Pacific, Singtel and KDDI have jointly published an open RFP for hybrid 5G-satellite CPE targeting maritime and remote mining operations, with initial deployments planned for Q1 2027. The GSMA’s NTN Device Working Group, formed in March 2026, has released its first interoperability profile, establishing baseline certification criteria for hybrid terminals.

    On the silicon side, MediaTek’s T850 NTN-enabled modem-RF platform and Qualcomm’s X80 5G Modem-RF with integrated NB-NTN support are providing the chipset foundation for a new generation of hybrid CPE devices. Both platforms support 3GPP Release 18 NTN enhancements, including doppler pre-compensation for LEO satellite links and IoT-NTN for narrowband satellite IoT applications.

    Procurement Recommendations for B2B Buyers

    For procurement teams planning 2026–2027 CPE refresh cycles, we recommend the following phased approach:

    1. Q3 2026: Include NTN/LEO compatibility as a weighted evaluation criterion in active CPE RFPs, even if immediate satellite integration is not required. Weight at 10–15% of technical scoring.
    2. Q4 2026: Conduct lab-based interoperability testing between shortlisted 5G CPE models and at least two LEO constellation operators (Starlink Enterprise, Kuiper, or regional LEO provider).
    3. Q1 2027: Pilot hybrid 5G-satellite CPE at 5–10% of high-priority sites (remote branch offices, temporary installations, disaster recovery locations).
    4. H2 2027: Transition to NTN-native CPE as the default procurement specification for all outdoor and remote-site FWA deployments.

    The convergence of terrestrial 5G and LEO satellite connectivity represents more than a niche redundancy option — it is rapidly becoming a core architectural requirement for enterprise-grade FWA. B2B buyers who incorporate NTN compatibility into their current procurement frameworks will be better positioned to leverage the full breadth of connectivity options as the hybrid ecosystem matures through 2027.

  • A Technical Buyer’s Guide to 5G CPE IPv6 Transition Architecture: Dual-Stack, 464XLAT, and CG-NAT Strategies for Operator-Grade FWA Deployments

    A Technical Buyer’s Guide to 5G CPE IPv6 Transition Architecture: Dual-Stack, 464XLAT, and CG-NAT Strategies for Operator-Grade FWA Deployments

    As mobile network operators worldwide accelerate their transition to IPv6-only core architectures — driven by address exhaustion in IPv4 and the operational cost of maintaining Carrier-Grade NAT (CG-NAT) infrastructure at scale — the 5G CPE device layer has emerged as a critical gateway for IPv6 transition strategies. For wholesale buyers, system integrators, and enterprise procurement teams evaluating 5G FWA CPE in 2026, understanding the IP transition capabilities of candidate devices is no longer optional. It directly affects application compatibility, VPN performance, IoT sensor reachability, and total cost of ownership across the device lifecycle.

    Why IPv6 Matters for 5G CPE in 2026

    The 3GPP 5G specification has mandated IPv6 support since Release 15, and virtually every 5G SA (Standalone) core deployed today operates on an IPv6-native user plane. Major operators — including T-Mobile US, Reliance Jio, Deutsche Telekom, and China Mobile — have publicly committed to IPv6-only or IPv6-dominant architectures for their 5G SA networks, with CG-NAT positioned as a transitional bridge rather than a permanent solution.

    For CPE buyers, this shift introduces a concrete set of technical evaluation criteria that go well beyond “does it support IPv6.” The device must handle:

    • IPv6-only WAN with IPv4-only LAN clients. The most common deployment scenario in 2026: the operator provides an IPv6-only PDN connection, but the enterprise LAN still runs legacy IPv4-only devices (printers, cameras, building management systems, industrial controllers).
    • Dual-stack application coexistence. Enterprise SaaS applications, VPN concentrators, and SD-WAN endpoints may be reachable over either protocol depending on carrier peering and application provider infrastructure.
    • 464XLAT translation performance. The CPE must perform stateless IPv4-IPv6 translation at line rate without introducing latency that degrades real-time applications — particularly critical for voice, video conferencing, and industrial control traffic.

    Key Architectural Components to Evaluate

    1. WAN-Side IP Stack: Dual-Stack vs. IPv6-Only with CLAT

    The most mature approach is dual-stack WAN, where the CPE receives both an IPv6 prefix (via DHCPv6-PD or SLAAC) and an IPv4 address from the 5G core. This provides maximum compatibility but requires the operator to maintain dual-stack infrastructure — precisely the operational burden that IPv6-only cores aim to eliminate.

    The emerging standard is IPv6-only WAN with CLAT (Customer-side Translator), defined in RFC 6877 (464XLAT). In this architecture, the CPE receives only an IPv6 address/prefix from the 5G core, a CLAT function embedded in the CPE performs stateless NAT46 translation for IPv4-only LAN clients, and the operator provides a PLAT (Provider-side Translator) in the core network.

    For buyers, the critical evaluation point is whether the CPE’s CLAT implementation is hardware-accelerated (via NPU or dedicated packet processing engine) or software-based. Hardware-accelerated CLAT can sustain 2–5 Gbps of NAT46 throughput with sub-millisecond latency; software CLAT may cap at 300–800 Mbps and introduce 2–5ms of additional latency per packet.

    2. LAN-Side DHCP and DNS Architecture

    IPv6 transition puts significant pressure on the CPE’s LAN-side services. Buyers should verify:

    • DNS64/NAT64 integration. The CPE must synthesize AAAA records for IPv4-only destinations (DNS64) and route the resulting traffic through a NAT64 gateway. Poor DNS64 implementations can break DNSSEC validation.
    • DHCPv6-PD sub-delegation. Enterprise deployments often require the CPE to sub-delegate IPv6 prefixes to downstream routers or VLANs. Verify that the device can receive a /56 or /48 prefix and delegate /60 or /64 sub-prefixes.
    • Happy Eyeballs v2 (RFC 8305) support. The CPE should not interfere with endpoint Happy Eyeballs algorithms. Some CPE ALG implementations inadvertently break dual-stack connection racing.

    3. Firewall, ALG, and Application Layer Gateway Behavior

    IPv6 introduces a fundamentally different security model at the CPE. Unlike IPv4, where NAT provides implicit ingress filtering, IPv6’s end-to-end architecture requires explicit stateful firewall rules. Buyers should evaluate stateful IPv6 firewall with default-deny inbound, RFC 4890 compliant ICMPv6 handling, and ALG transparency for SIP, FTP, and other protocols that rewrite IP addresses in application-layer payloads.

    4. VPN and SD-WAN Interoperability

    Enterprise VPN clients — IPSec, WireGuard, OpenVPN, and SD-WAN edge appliances — exhibit varying levels of IPv6 compatibility. The CPE must pass IPv6-encapsulated VPN traffic transparently, support IPv6 WAN addressing for management plane TR-069/TR-369 USP sessions, and handle fragmented IPv6 packets correctly.

    The CG-NAT Sunset Horizon

    Operators worldwide are beginning to signal CG-NAT sunset timelines. T-Mobile US has indicated that its 5G SA core will move to IPv6-only with 464XLAT as the default CPE configuration by 2027. European operators following GSMA IPv6 transition guidelines are on similar trajectories. For CPE buyers, this means devices purchased today on 3–5 year deployment cycles will almost certainly need to operate in IPv6-dominant environments within their service lifetime.

    Honlly’s IPv6 Transition Architecture

    Honlly Telecom’s 5G CPE portfolio implements hardware-accelerated 464XLAT CLAT with dedicated packet processing engines capable of sustaining multi-gigabit NAT46 throughput at wire speed. The platform supports both dual-stack and IPv6-only WAN modes, with dynamic mode selection via TR-369 USP provisioning. Enterprise features including DHCPv6-PD sub-delegation, RFC 4890-compliant ICMPv6 filtering, and transparent VPN passthrough are standard.

    Evaluation Checklist for IPv6 Transition

    1. CLAT performance: Hardware-accelerated with verified throughput ≥ 1 Gbps NAT46
    2. DNS64/NAT64: Embedded DNS64 with RFC 7050-compliant NAT64 discovery
    3. Firewall: Stateful IPv6 firewall with default-deny inbound, RFC 4890 ICMPv6
    4. Prefix delegation: DHCPv6-PD with sub-delegation to LAN interfaces
    5. VPN transparency: WireGuard, IPSec, and SD-WAN passthrough validated

    For detailed technical specifications on Honlly’s 5G CPE IPv6 capabilities, visit honllytelecom.com/products or contact the Honlly B2B engineering team.

  • A Technical Buyer’s Guide to 5G CPE Zero-Touch Provisioning: TR-369 USP, Device Lifecycle Automation, and Operator-Grade Remote Management Frameworks

    A Technical Buyer’s Guide to 5G CPE Zero-Touch Provisioning: TR-369 USP, Device Lifecycle Automation, and Operator-Grade Remote Management Frameworks

    As 5G FWA deployments scale from thousands to millions of CPE units per operator, the economics of device provisioning have shifted from a manageable operational expense to a strategic bottleneck. The cost of dispatching a field technician to install and configure a single CPE — estimated at $75–$180 per truck roll across major markets — becomes untenable at scale. Zero-Touch Provisioning (ZTP), enabled by the Broadband Forum’s TR-369 User Services Platform (USP) standard, has emerged as the definitive answer. For B2B buyers and system integrators sourcing 5G CPE in 2026, understanding ZTP architecture is a prerequisite for operator certification and large-scale deployment eligibility.

    From TR-069 to TR-369: The Management Protocol Transition

    The broadband industry’s CPE management backbone has been TR-069 (CWMP) for nearly two decades. While TR-069 served DSL, cable, and early LTE FWA deployments adequately, its limitations in a 5G context are well documented:

    • HTTP-based polling model introduces latency and overhead unsuitable for real-time 5G service orchestration
    • Single CPE-to-ACS relationship cannot support multi-tenant, multi-service architectures required by network slicing and private 5G
    • Limited data model extensibility makes it difficult to expose 5G-specific parameters (CSI-RS measurements, beam management state, slice configuration) without proprietary vendor extensions
    • No native IoT device proxy capability — TR-069 assumes every managed endpoint is a CPE, whereas TR-369 USP can proxy manage connected IoT sensors, mesh nodes, and enterprise LAN equipment

    TR-369 USP (User Services Platform), standardized by the Broadband Forum as USP 1.3 in 2024 and USP 1.4 targeted for H2 2026, addresses these limitations through a fundamentally modern architecture:

    • WebSocket and CoAP transport with MQTT broker integration for real-time, bidirectional communication
    • Multi-controller architecture allowing a single CPE to be simultaneously managed by an operator ACS, enterprise IT controller, and security analytics platform
    • USP Services model that cleanly separates device management, firmware lifecycle, network diagnostics, and IoT proxy functions
    • End-to-end security with TLS 1.3 mutual authentication and USP Endpoint Identity certificates

    Zero-Touch Provisioning Architecture

    Phase 1: Bootstrap and Discovery

    When a CPE powers on for the first time, it must autonomously discover its management controller without any prior configuration. The bootstrap sequence typically follows DHCP/DHCPv6 option-based discovery (the most common method in carrier deployments), DNS-SD/mDNS fallback for enterprise deployments, or a pre-configured bootstrap URL for managed service providers.

    The key evaluation criterion for buyers: how many bootstrap discovery methods does the CPE support, and can they be prioritized in a configurable fallback chain?

    Phase 2: Secure Onboarding and Identity

    Once the controller URL is discovered, the CPE establishes a mutually authenticated TLS 1.3 session. The device identity model is critical: factory-installed X.509 device certificates (IEEE 802.1AR DevID) burned into secure storage (TEE or TPM) during manufacturing provide cryptographic device identity — the gold standard mandatory for operator-grade ZTP. Buyers should verify that the CPE supports hardware-backed key storage (TrustZone, Secure Enclave, or discrete TPM) for device certificates and can perform CSR generation for operator PKI integration.

    Phase 3: Parameter Provisioning

    After secure onboarding, the controller pushes the full service configuration via USP Set messages: WAN configuration (APN/DNN, PDU session parameters, URSP rules), LAN configuration (DHCP pools, VLANs, SSIDs, firewall rules), voice configuration (SIP proxy, codec preferences), and QoS mapping (DSCP-to-QFI mapping tables). The entire provisioning sequence — from power-on to fully configured service — should complete in under 90 seconds for typical FWA deployments and under 3 minutes for complex enterprise configurations.

    Phase 4: Ongoing Lifecycle Management

    ZTP is not a one-time event; it extends across the CPE lifecycle with firmware lifecycle management via segmented, scheduled, and conditional USP upgrades; telemetry and performance monitoring with real-time KPI streaming; remote diagnostics with ping, traceroute, packet capture, and modem log collection; and secure decommissioning with factory reset, certificate revocation, and secure wipe.

    Evaluation Criteria for CPE ZTP Capability

    1. USP Protocol Compliance

    Verify USP 1.3 (or later) with WebSocket transport and TLS 1.3 mutual authentication, MQTT transport support, CoAP transport with DTLS for constrained IoT scenarios, at least 15 concurrent controller connections, and USP MTP with fragmentation and reassembly for large payloads.

    2. Bootstrap Mechanism Flexibility

    The CPE should support all three bootstrap discovery methods (DHCP options, DNS-SD/mDNS, pre-configured URL) with configurable priority and timeout parameters.

    3. Hardware-Backed Security

    Mandatory: X.509 device certificate in factory-secured storage, secure boot chain, TLS 1.3 with PFS cipher suites, and certificate renewal without factory reset.

    4. Data Model Coverage

    The CPE must expose a comprehensive TR-181 Device:2 data model covering Device.Cellular (5G modem parameters, cell measurements), Device.WiFi (SSID, band steering, client statistics), Device.Routing (static routes, policy routing, VRF instances), Device.Bridging (VLANs, IGMP/MLD snooping), and Device.QoS (classification, queuing, DSCP marking).

    5. Multi-Tenant and Slicing Support

    For private 5G and network slicing deployments, the CPE must support multiple PDU sessions with independent USP controller associations, URSP rule provisioning via USP, and per-slice telemetry and QoS monitoring.

    Honlly’s ZTP Implementation

    Honlly Telecom’s 5G CPE portfolio implements TR-369 USP 1.3 across all current-generation devices, with a field-upgradable path to USP 1.4. Key differentiators include factory-installed X.509 device certificates with hardware-backed key storage in ARM TrustZone, a multi-controller architecture supporting simultaneous operator, enterprise, and cloud management connections, comprehensive TR-181 Device:2 data model coverage, conditional firmware upgrade engine, and zero-touch bootstrap time under 75 seconds for typical FWA deployments.

    The ZTP Imperative for 2026–2027

    Operators issuing RFPs for 5G CPE in H2 2026 are increasingly making TR-369 USP compliance a mandatory gate criterion — not a “nice-to-have.” The days of TR-069 as an acceptable minimum are ending. For CPE buyers serving operator channels, ZTP readiness determines whether a device can be listed on an operator’s approved CPE roster at all.

    When evaluating 5G CPE for ZTP capability, treat USP compliance as a pass/fail gate. Devices that pass should then be scored on bootstrap flexibility, security architecture, and data model depth. The CPE that provisions fastest, most securely, and with the richest data model will deliver the lowest operational cost over a 3–5 year deployment lifecycle.


    For detailed technical documentation on Honlly’s TR-369 USP implementation and ZTP capabilities, visit honllytelecom.com/products or contact the Honlly B2B solutions engineering team.

  • Global 5G CPE Supply Chain Diversification Accelerates as Operators Mandate Multi-Source Component Strategies for FWA Device Resilience in H2 2026

    Global 5G CPE Supply Chain Diversification Accelerates as Operators Mandate Multi-Source Component Strategies for FWA Device Resilience in H2 2026

    The 5G Fixed Wireless Access (FWA) ecosystem is entering a critical inflection point in mid-2026. After three years of rapid subscriber growth — the Global mobile Suppliers Association (GSA) now tracks over 185 million 5G FWA connections worldwide — the CPE supply chain faces structural pressure that extends far beyond typical demand-supply dynamics. Network operators across North America, Europe, Southeast Asia, and the Middle East are urgently revising procurement frameworks to mandate multi-source component strategies, driven by a confluence of geopolitical semiconductor controls, regional certification fragmentation, and the operational imperative to avoid single-vendor lock-in at the device layer.

    The Geopolitical Component Challenge

    The most immediate catalyst is the evolving export control landscape. Since the expanded U.S. semiconductor restrictions implemented in early 2025, 5G CPE manufacturers have navigated a bifurcated supply environment where advanced baseband processors, RF front-end modules, and power amplifiers are subject to tiered access rules depending on end-market jurisdiction. A Qualcomm Snapdragon X75 or MediaTek T800 modem-RF system destined for a European operator may follow a completely different sourcing path than an equivalent unit bound for a Southeast Asian deployment — even when manufactured on the same assembly line.

    This jurisdictional fragmentation has pushed procurement directors at major operators — including Vodafone, Deutsche Telekom, and Singtel — to formally require CPE vendors to disclose component origin mapping at the bill-of-materials (BOM) level. The days of evaluating CPE purely on throughput, bands, and price-per-unit are over; supply chain transparency is now a weighted RFP criterion alongside RF performance and software maturity.

    Multi-Source Mandates in Operator RFPs

    In practice, operator procurement teams are operationalizing multi-source requirements in three concrete ways:

    Component-Level Dual-Sourcing

    RFPs increasingly specify that critical silicon — baseband processors, transceivers, and PMICs — must be sourced from at least two qualified suppliers, with at least one supplier located outside geopolitically sensitive jurisdictions. For CPE vendors historically reliant on a single silicon partner, this demands significant NRE investment to port firmware stacks across heterogeneous hardware platforms.

    Regional Assembly and Fulfillment

    Beyond silicon, operators are requiring CPE to support final assembly, testing, and packaging (ATP) in-region. A North American Tier-1 operator’s recent RFP mandated that 40% of CPE units delivered under a three-year frame contract must undergo final ATP in Mexico or the United States. For Honlly and peer manufacturers serving global B2B channels, this translates to distributed manufacturing partnerships rather than single-factory fulfillment.

    Firmware Supply Chain Attestation

    Software supply chain integrity has become a parallel concern. Operators now require CPE vendors to provide software bill of materials (SBOM) documentation aligned with NTIA and CISA frameworks, covering the full OSS/BSP stack from Linux kernel to Qualcomm AMSS or MediaTek modem firmware layers. This is no longer optional — it is appearing as a pass/fail gate in operator lab certification checklists.

    Impact on the B2B CPE Procurement Lifecycle

    For wholesale distributors, system integrators, and enterprise buyers sourcing 5G CPE in the B2B channel, the supply chain diversification trend has practical implications:

    • Lead time variability. Devices with diversified BOMs may carry 8–14 week lead times versus 4–6 weeks for single-source designs — but the diversified models offer far greater resilience against component allocation shocks.
    • SKU proliferation. Multi-region ATP strategies create regional SKU variants with identical specifications but different country-of-origin documentation, affecting customs clearance and warranty logistics.
    • Certification overhead. Each component permutation requires re-certification with GCF/PTCRB, CE RED, FCC, and regional bodies (NBTC, TRA, ANRT), adding 6–12 weeks to market entry timelines.

    Honlly’s Strategic Response

    For CPE manufacturers like Honlly Telecom, the supply chain diversification imperative is both a challenge and a competitive differentiator. The company’s 5G CPE portfolio — spanning sub-6 GHz Cat 19/20 devices and emerging 5G-Advanced platforms — is being engineered with modular RF and baseband architectures that support pin-compatible component substitution across Qualcomm and MediaTek ecosystems. This design philosophy, sometimes called “platform-agnostic CPE architecture,” allows a single industrial design and software baseline to accommodate multiple silicon configurations with minimal re-validation overhead.

    Honlly’s B2B channel partners benefit from this approach through guaranteed supply continuity, predictable certification roadmaps, and the ability to tender for operator contracts that include strict multi-source requirements without additional NRE burden.

    Looking Ahead: H2 2026 and Beyond

    As H2 2026 progresses, expect supply chain resilience to become a top-three CPE selection criterion alongside radio performance and total cost of ownership. The operators that moved earliest on multi-source mandates — primarily European and North American Tier-1 carriers — are already seeing procurement cycle predictability improvements compared to peers still locked into single-vendor CPE relationships.

    For the broader industry, the message is clear: 5G CPE is no longer just a radio and a router. It is a supply-chain-dependent strategic asset, and the buyers treating it as such will be best positioned to sustain FWA subscriber growth through the next cycle of component constraints and geopolitical uncertainty.


    For more information on Honlly Telecom’s 5G CPE portfolio and multi-source supply chain capabilities, contact the Honlly B2B sales team or visit honllytelecom.com/products.

  • A Technical Buyer’s Guide to 5G CPE VPN and Enterprise Security Architecture

    A Technical Buyer’s Guide to 5G CPE VPN and Enterprise Security Architecture

    As enterprises increasingly deploy 5G fixed wireless access (FWA) as primary or failover WAN connectivity for branch offices, retail locations, and industrial sites, the security architecture of customer premises equipment (CPE) has moved from a secondary consideration to a procurement-critical requirement. A 5G CPE device that lacks enterprise-grade VPN capabilities, hardware-anchored security, and Zero Trust integration represents an unacceptable risk vector in modern network architectures.

    VPN Protocol Landscape for 5G CPE

    IPsec remains the dominant VPN protocol for site-to-site enterprise connectivity, and 5G CPE devices targeting enterprise deployments must support IKEv2 with hardware-accelerated IPsec encryption. The minimum acceptable specification includes AES-256-GCM encryption with hardware offload capable of sustaining line-rate throughput of 1 Gbps or higher without CPU throttling. IKEv2 mobility and multihoming (MOBIKE) support is critical for CPE devices that may transition between 5G cells or between 5G and wired WAN interfaces, as it enables seamless VPN tunnel continuity without renegotiation.

    CPE buyers should verify that IPsec implementations support Perfect Forward Secrecy (PFS) using Diffie-Hellman group 14 or higher, preferably group 19/20 for ECDH, IKEv2 fragmentation to handle large certificate chains over MTU-constrained links, and dead peer detection (DPD) with configurable keepalive intervals for rapid failover detection.

    WireGuard has gained significant traction in enterprise networking due to its minimalist codebase, high throughput efficiency, and streamlined key management. For 5G CPE devices, WireGuard offers lower CPU utilization during encryption operations, faster tunnel establishment with a single round-trip, and native roaming support without additional protocol extensions. However, WireGuard’s stateless design lacks built-in dynamic address assignment and user authentication mechanisms. Enterprise deployments typically layer WireGuard with external authentication and IP address management systems.

    Hardware Root of Trust and Secure Boot

    A 5G CPE device’s security posture begins at power-on. Hardware root of trust (HRoT) establishes a cryptographically verifiable chain of trust from the immutable boot ROM through the bootloader, operating system kernel, and application software. CPE devices targeting enterprise and carrier deployments should implement secure boot where each stage of the boot process verifies the cryptographic signature of the next stage before execution, anchored in one-time programmable memory or eFuses containing the manufacturer’s public key hash.

    Measured boot extends secure boot by recording cryptographic measurements of each boot component into Platform Configuration Registers (PCRs) within a Trusted Platform Module (TPM 2.0) or firmware TPM (fTPM). Remote attestation services can verify these measurements to ensure the device booted into a known-good state before granting network access. Runtime integrity monitoring using Linux Integrity Measurement Architecture (IMA) or equivalent provides continuous verification of kernel and critical process integrity.

    Zero Trust Architecture Integration

    The Zero Trust model, “never trust, always verify,” is becoming standard practice for enterprise network security, and 5G CPE devices must function as Zero Trust enforcement points rather than implicit trust anchors on the network perimeter. Each CPE device must have a unique, cryptographically verifiable identity based on IEEE 802.1AR initial device identity (IDevID) certificates or manufacturer-installed X.509 certificates with hardware-bound private keys.

    CPE devices should support 802.1Q VLAN tagging and VXLAN/Geneve overlay networking to enforce micro-segmentation policies at the network edge. Enterprise traffic can be isolated from guest traffic and IoT device traffic, with each segment subject to independent security policies enforced by the CPE’s integrated firewall. Software-Defined Perimeter (SDP) client functionality enables mutually authenticated TLS 1.3 tunnels to SDP gateways, ensuring that enterprise resources are invisible to unauthorized devices.

    Integrated Security Services

    Beyond VPN and Zero Trust capabilities, enterprise 5G CPE should incorporate defense-in-depth security services including stateful Layer 3/4 packet inspection with configurable inbound and outbound rules, DDoS protection with SYN flood, UDP flood, and ICMP flood mitigation, and application-layer gateway support for protocols requiring dynamic port allocation. Intrusion detection and prevention capabilities with signature-based and anomaly-based threat detection should include automatic signature updates and, for resource-constrained CPE platforms, cloud-based IDS offload as an alternative.

    DNS security via DNS-over-TLS or DNS-over-HTTPS for encrypted DNS resolution should be combined with DNS filtering against known malicious domains and integration with enterprise DNS security services. TLS 1.3 inspection capability enables visibility into encrypted traffic without breaking end-to-end encryption for sensitive applications, though this requires sufficient CPU resources.

    FIPS 140-3 and Common Criteria Compliance

    For government, defense, and regulated industry deployments, cryptographic module validation is non-negotiable. FIPS 140-3, effective April 2026 and replacing FIPS 140-2, defines four security levels for cryptographic modules. Enterprise 5G CPE targeting regulated markets should target FIPS 140-3 Level 2 or higher, which requires tamper-evident physical security mechanisms and role-based authentication for cryptographic key access.

    Common Criteria (ISO/IEC 15408) Evaluation Assurance Level (EAL) certification provides an independent assessment of the CPE’s entire security architecture, not just cryptographic modules. For defense-sector deployments, NIAP Protection Profiles for Network Devices provide additional device-specific security requirements aligned with U.S. Department of Defense standards.

    Remote Management Security

    The CPE management interface is a high-value target for attackers. All CPE management traffic between the device and the auto-configuration server must be encrypted using TLS 1.3 with mutual certificate-based authentication via TR-069 or TR-369 User Services Platform. Administrative SSH access must use ed25519 or RSA 4096-bit keys with key rotation policies, with password-based SSH authentication disabled in production deployments.

    Local REST and gRPC management APIs must require authentication tokens with time-limited validity and fine-grained access control. Over-the-air firmware updates must be digitally signed and verified before installation, with rollback protection preventing downgrade attacks and A/B partition schemes for atomic, fail-safe updates.

    Procurement Checklist for Enterprise Security

    When evaluating 5G CPE for enterprise deployments, procurement teams should verify the following security capabilities as minimum requirements: hardware-accelerated IPsec/IKEv2 with AES-256-GCM plus WireGuard kernel support with MOBIKE for seamless roaming; TPM 2.0 or fTPM with secure boot and hardware-anchored root of trust plus measured boot with remote attestation; IEEE 802.1AR device identity with SDP client support and micro-segmentation via VLAN and VXLAN; stateful Layer 3/4 firewall with DDoS mitigation and IDS/IPS with cloud-offload option; FIPS 140-3 Level 2 or higher cryptographic module with Common Criteria EAL 2 or higher preferred; TR-369 USP over TLS 1.3 with mutual authentication and signed OTA updates with rollback protection; and cryptographic agility supporting post-quantum cryptography algorithm migration as NIST-standardized algorithms enter operational deployment phases.

    Enterprise 5G CPE security is not a checkbox item, it is an architectural commitment that must be validated through hands-on testing, third-party certification review, and continuous vulnerability management. Devices that meet these requirements will serve as trusted, defensible gateways in the evolving enterprise WAN landscape.

  • A Technical Buyer’s Guide to 5G CPE Carrier Aggregation and Spectrum Efficiency

    A Technical Buyer’s Guide to 5G CPE Carrier Aggregation and Spectrum Efficiency

    Carrier aggregation (CA) is one of the most impactful features in 5G NR that directly determines the throughput, coverage, and spectral efficiency of fixed wireless access (FWA) customer premises equipment (CPE). For operators and enterprise procurement teams evaluating 5G CPE, understanding CA architecture from supported band combinations to dynamic spectrum sharing (DSS) behavior is essential to making informed purchasing decisions that align with spectrum strategy and deployment topology.

    Carrier Aggregation Fundamentals in 5G NR

    5G NR carrier aggregation enables a CPE device to simultaneously transmit and receive data across multiple component carriers (CCs), effectively combining fragmented spectrum assets into a single, higher-throughput data pipe. Release 15 introduced baseline CA with up to 16 CCs in downlink and 2 CCs in uplink, while Release 16 expanded inter-band CA flexibility and introduced supplementary uplink (SUL) aggregation. Release 17 further refined power control for inter-band CA scenarios with widely separated frequency bands.

    The practical throughput of a CA configuration depends on three factors: the number of aggregated carriers, the bandwidth of each carrier, and the MIMO layer count per carrier. A configuration aggregating 100 MHz of n78 (TDD, 4T4R, 4 layers) with 40 MHz of n41 (TDD, 4T4R, 4 layers) can theoretically deliver peak downlink throughput exceeding 3.5 Gbps under optimal conditions. However, real-world performance is governed by signal quality, scheduler efficiency, backhaul capacity, and inter-site distance.

    Critical CA Combinations for Global Deployments

    Sub-6 GHz intra-band CA remains the most common deployment scenario, involving intra-band contiguous CA within the n78 band (3.3-3.8 GHz). Operators with 80-100 MHz of contiguous n78 spectrum can deploy 2CC CA configurations such as 50+50 MHz or 60+40 MHz, while those with larger allocations may support 3CC configurations. Intra-band CA within n78 is the workhorse of FWA deployments in Europe, the Middle East, and parts of Asia-Pacific.

    Inter-band CA combining mid-band TDD carriers (n78, n79) with low-band FDD carriers (n28, n5, n71) provides both capacity and coverage advantages. A typical configuration pairs n78 (100 MHz TDD) for capacity with n28 (20 MHz FDD) for uplink coverage extension and control-plane reliability. For CPE devices deployed at cell edges, this combination can improve uplink throughput by 40-60% compared to standalone n78 operation.

    For operators with mmWave spectrum assets, NR Dual Connectivity (NR-DC) between n78 (anchor) and n257/n258 (mmWave) can support peak throughput exceeding 7 Gbps. CPE devices supporting NR-DC require dual RF front-ends and antenna arrays optimized for both frequency ranges.

    Dynamic Spectrum Sharing (DSS) and CA Implications

    DSS allows operators to dynamically allocate spectrum resources between 4G LTE and 5G NR on the same frequency band. When CA configurations include DSS-enabled bands, CPE behavior becomes more complex. The device must handle rapid changes in NR bandwidth allocation as the gNB adjusts the DSS ratio based on LTE and NR traffic demand.

    For CPE procurement, DSS compatibility testing should verify that the device maintains stable CA operation during DSS transitions, that throughput degrades gracefully rather than catastrophically when NR bandwidth is reduced, and that the device correctly reports available NR bandwidth in channel quality indicator (CQI) measurements. CPE devices implementing rate-matching around LTE CRS within DSS carriers achieve 10-15% better spectral efficiency compared to devices using simple puncturing approaches.

    Uplink CA and SUL Considerations for Enterprise Deployments

    While downlink CA receives most attention, uplink CA and supplementary uplink (SUL) are increasingly important for enterprise FWA use cases involving video conferencing, cloud upload, and symmetric data applications. Uplink CA combining n78 (TDD) with n28 (FDD) can double uplink throughput compared to standalone n78 when the TDD pattern is downlink-heavy.

    SUL is particularly valuable in n78-only deployments where the TDD uplink duty cycle is limited. By adding an SUL carrier in a lower frequency band (typically n80, n84, or n28), CPE devices can offload uplink traffic to a dedicated FDD carrier, freeing TDD resources for downlink. For enterprise branch office deployments requiring symmetric 500 Mbps+ throughput, SUL-capable CPE should be a hard procurement requirement.

    Antenna Architecture Requirements for Multi-Band CA

    Effective multi-band CA requires antenna systems that can maintain acceptable gain and isolation across widely separated frequency bands. A CPE supporting simultaneous n28 (700 MHz) + n78 (3.5 GHz) CA needs antenna elements optimized for both frequencies, typically using separate low-band and mid-band radiating elements within a shared enclosure.

    Key antenna specifications for CA-capable CPE include per-band gain of minimum 2 dBi for low-band (sub-1 GHz) and 4 dBi for mid-band (1-6 GHz), inter-band isolation of minimum 15 dB between co-located low-band and mid-band elements to prevent receiver desensitization, envelope correlation coefficient (ECC) below 0.3 for MIMO elements within each band, and total radiated power (TRP) of minimum 20 dBm for mid-band and 18 dBm for low-band.

    Testing and Validation Framework

    Procurement teams should establish a structured CA validation process that includes static throughput testing to measure peak and sustained throughput for each supported CA combination under ideal RF conditions, dynamic CA testing to verify CA activation and deactivation latency during mobility scenarios, DSS coexistence testing to validate performance with variable DSS ratios, thermal and power characterization during extended CA operation of minimum 4 hours, and interoperability testing with the operator’s specific gNB vendors and network software releases.

    Procurement Recommendations

    When specifying CA requirements in CPE RFPs, buyers should mandate minimum CA capability based on the operator’s current and planned spectrum portfolio. As a baseline, 5G CPE devices should support at minimum 2CC downlink CA (intra-band n78 + inter-band n78+n28), 2CC uplink CA (n78+n28), and DSS compatibility on all low-band carriers. For operators with mmWave spectrum assets, NR-DC support should be specified with clear requirements for MCG/SCG failover behavior and data split ratios. CPE devices that demonstrate superior CA performance in real-world testing, not just datasheet specifications, will deliver measurably better network economics through higher spectral efficiency and improved user experience.

  • 5G-Advanced CPE Readiness: How 3GPP Release 18 Features Are Reshaping FWA Device Procurement

    5G-Advanced CPE Readiness: How 3GPP Release 18 Features Are Reshaping FWA Device Procurement

    The telecommunications industry is entering the 5G-Advanced era, and for operators, ISPs, and enterprise buyers evaluating fixed wireless access (FWA) customer premises equipment (CPE), the implications of 3GPP Release 18 are substantial. Released as the first standard within the 5G-Advanced framework, Release 18 introduces capabilities that will directly influence CPE silicon roadmaps, RF front-end design, and procurement specifications through 2027 and beyond.

    MIMO Enhancements: Beyond 4T4R

    Release 18 expands multi-antenna capabilities significantly. While current 5G CPE devices predominantly operate with 4T4R (four transmit, four receive) configurations, Release 18 standardizes enhanced MIMO operation supporting 8T4R and 8T8R for sub-7 GHz bands. This means next-generation CPE devices will need to accommodate additional antenna paths, more sophisticated beamforming algorithms, and higher computational throughput for spatial multiplexing.

    For procurement teams, the practical question is straightforward: can your vendor’s CPE roadmap support 8-layer spatial multiplexing in FR1, and what are the thermal and power implications of doubling the RF chains? Early supplier engagement on Release 18 MIMO readiness is becoming a differentiator in operator RFPs.

    AI/ML for NR Air Interface

    One of Release 18’s most forward-looking features is the introduction of AI/ML-based optimizations for the New Radio (NR) air interface. The standard defines frameworks for AI-assisted channel state information (CSI) feedback, beam management, and positioning accuracy. For CPE devices, this translates to new requirements for on-device inference capabilities.

    Buyers should begin asking silicon vendors about integrated neural processing units (NPUs) within 5G modem platforms. Qualcomm’s Snapdragon X80 and MediaTek’s T800 series already include AI acceleration blocks, but Release 18 compliance will require standardized interfaces between the AI engine and the 5G protocol stack. CPE devices that can leverage AI-enhanced CSI compression will see measurable gains in spectral efficiency, potentially 15-25% improvements in cell-edge throughput scenarios.

    Extended Reality (XR) and Deterministic Latency

    Release 18 introduces enhanced support for extended reality (XR) traffic, including awareness of XR traffic periodicity and jitter requirements at the MAC layer. For enterprise CPE deployments supporting augmented reality in manufacturing, remote assistance in field operations, or immersive training environments, this capability is critical.

    The standard defines XR-specific scheduling enhancements that allow the gNB to align transmission opportunities with XR frame boundaries, reducing latency jitter from the 20-30ms range typical in current 5G NR to sub-5ms deterministic latency. CPE devices targeting enterprise XR use cases will need to implement Release 18 XR-aware buffer management and scheduling coordination.

    Network Energy Efficiency and CPE Sleep Modes

    Release 18 places significant emphasis on network energy efficiency, including enhanced discontinuous reception (eDRX) and network-controlled sleep states for CPE devices. For operators deploying tens of thousands of FWA CPE units, these power-saving features directly impact OPEX. The standard introduces cell DTX/DRX mechanisms where base stations can enter sleep states during low-traffic periods, and CPE devices must gracefully handle these transitions.

    Procurement specifications should now include CPE power consumption profiles across active, idle, and Release 18 deep-sleep states. Devices that can achieve sub-2W idle power while maintaining fast wake-up times (under 50ms) for incoming traffic will have a competitive advantage in operator evaluations.

    Multi-TRP and Inter-Cell Coordination

    Release 18 enhances multi-transmission/reception point (multi-TRP) operation for improved reliability and throughput at cell edges. CPE devices supporting multi-TRP can simultaneously communicate with two or more base station transmission points, using coordinated scheduling to mitigate inter-cell interference. For fixed wireless deployments in suburban and rural environments where cell-edge performance is often the limiting factor, this feature can meaningfully improve user experience.

    Multi-TRP support requires dual-polarized antenna arrays capable of independent beam steering toward different TRPs, plus baseband processing capable of handling multiple spatial streams from disparate sources. CPE buyers should verify whether current-generation hardware can support multi-TRP through firmware upgrades or whether new silicon is required.

    Sidelink and Device-to-Device Relaying

    Release 18 expands NR sidelink capabilities, including support for UE-to-UE relaying. In practical terms, this enables mesh networking scenarios where one CPE device can serve as a relay for neighboring devices in areas with poor direct gNB coverage. For rural FWA deployments, this could significantly reduce the number of required base station sites while maintaining service quality.

    CPE devices with sidelink relay capability will require additional RF paths dedicated to the sidelink interface, typically in the 5.9 GHz ITS band or unlicensed spectrum. Procurement specifications should define sidelink power class, supported bandwidth, and relay hop count requirements aligned with deployment topology.

    Procurement Implications for 2026-2027

    The transition to 5G-Advanced represents a generational shift in CPE capabilities. Operators and enterprise buyers should consider the following priorities in near-term procurement cycles:

    • Silicon Roadmap Alignment: Request vendor roadmaps showing Release 18 feature support timelines, including which capabilities require new silicon vs. firmware updates to existing platforms.
    • AI/ML Capability Assessment: Evaluate modem NPU specifications, supported AI/ML models for CSI compression, and field-upgradeability of AI inference engines.
    • Multi-TRP and MIMO Readiness: Verify 8T4R or 8T8R hardware support, multi-TRP beam management capability, and antenna isolation specifications for simultaneous multi-beam operation.
    • Power Efficiency Metrics: Include Release 18 sleep mode power consumption in RFPs, with specific targets for active-to-sleep transition latency.
    • Interoperability Testing: Request 3GPP Release 18 IOT test results with major infrastructure vendors for core Release 18 features.

    As the first wave of Release 18-compliant chipsets enters sampling in late 2026, procurement decisions made today will determine whether operators are positioned to capitalize on 5G-Advanced capabilities or locked into pre-Release 18 platforms through 2028. Early engagement with CPE vendors on 3GPP Release 18 readiness is no longer optional, it is a competitive necessity.

  • A Technical Buyer’s Guide to 5G CPE Thermal Management: Industrial-Grade Heat Dissipation Design for Outdoor and High-Density Deployments

    A Technical Buyer’s Guide to 5G CPE Thermal Management: Industrial-Grade Heat Dissipation Design for Outdoor and High-Density Deployments

    Thermal management is one of the most overlooked yet operationally critical factors in 5G CPE procurement. As fixed wireless access (FWA) deployments expand into outdoor environments, industrial facilities, and high-density urban rooftops, the thermal design of customer premises equipment directly impacts service reliability, hardware longevity, and total cost of ownership. This guide provides procurement teams and network engineers with a structured framework for evaluating 5G CPE thermal architecture.

    Why Thermal Design Matters in 5G CPE

    Modern 5G CPE devices pack extraordinary processing density into compact enclosures. A typical outdoor 5G CPE unit integrates a multi-core SoC, 5G modem with carrier aggregation across multiple bands, RF front-end components, power management ICs, and increasingly AI/ML inference accelerators for edge computing workloads. All of this generates heat — and in outdoor deployments with direct solar exposure, ambient temperatures can push junction temperatures to failure thresholds if thermal design is inadequate.

    The consequences of poor thermal management cascade quickly:

    • Thermal throttling: When SoC or modem temperatures exceed safe operating limits, the device reduces clock speeds or disables carrier aggregation, directly degrading throughput and latency performance. A CPE that delivers 2 Gbps downlink at 25°C may throttle to 600 Mbps at 65°C ambient.
    • Component degradation: Every 10°C increase in operating temperature roughly halves the expected lifetime of electrolytic capacitors and accelerates semiconductor electromigration. Outdoor CPE expected to last 5–7 years may fail within 2–3 years without adequate cooling.
    • Service downtime: Thermal-induced device reboots or permanent failures in hard-to-access outdoor installations drive up truck-roll costs and erode subscriber satisfaction.

    Thermal Architecture Options: A Comparative Analysis

    1. Passive Convection Cooling

    The most common approach for consumer and light-commercial indoor CPE. Passive cooling relies on the device enclosure itself as a heat spreader and radiator, with strategically placed ventilation slots enabling natural convection airflow.

    Design considerations:

    • Enclosure material selection is critical — aluminum alloys (typically 6061 or 6063) offer 3–5x better thermal conductivity than polycarbonate plastics. Some high-end CPE use magnesium alloy frames for weight reduction while maintaining thermal performance.
    • Internal thermal interface materials (TIMs) between hot components and the enclosure must be evaluated for long-term performance. Gap pads, thermal grease, and phase-change materials each have different degradation profiles over 5+ year deployment lifetimes.
    • Fin geometry on the external enclosure surface increases surface area for heat dissipation. Staggered pin-fin designs can improve convective heat transfer by 20–30% compared to flat surfaces in still-air conditions.

    Limitations: Passive cooling is generally rated for ambient temperatures up to 45–50°C. Beyond this range, active cooling or de-rating is required.

    2. Active Fan-Cooled Systems

    For high-performance indoor CPE with sustained data throughput above 2 Gbps, or for devices operating in enclosed spaces with limited natural airflow, active fan cooling becomes necessary.

    Design considerations:

    • Fan reliability is the dominant concern. Buyers should evaluate fans rated for at least 50,000 hours MTBF at maximum operating temperature, with sealed ball-bearing designs preferred over sleeve-bearing alternatives.
    • Fan speed control algorithms should be auditable. Intelligent PWM (pulse-width modulation) controllers that adjust fan speed based on multiple thermal sensors (SoC, modem, RF PA, ambient) offer better acoustic performance and energy efficiency than simple on/off thermostat control.
    • Dust ingress protection in fan-cooled enclosures becomes a compounding factor. IP5X-rated dust protection with serviceable or washable intake filters should be specified for industrial and dusty environments.

    3. Advanced Thermal Solutions for Outdoor CPE

    Outdoor 5G CPE deployed on rooftops, poles, or building exteriors face the most demanding thermal conditions. Ambient temperatures can range from -40°C to +55°C (or higher with solar radiation), and the enclosure itself must often be IP65 or IP67 rated — meaning no ventilation openings.

    Key technologies in this category:

    • Die-cast enclosure as primary heatsink: The entire enclosure body becomes a sealed heatsink with integrated fins on the rear or top surface. The PCB is thermally coupled to the enclosure through multiple contact points using high-performance gap pads or direct metal contact.
    • Heat pipe and vapor chamber solutions: For CPE with concentrated hot spots (such as mmWave antenna arrays or high-power PAs), embedded heat pipes or vapor chambers can spread heat from small hotspots across the full enclosure volume. Vapor chamber solutions add cost but can reduce hotspot temperatures by 15–25°C compared to solid aluminum spreaders.
    • Solar shield and radiation management: Outdoor enclosures should include a secondary solar shield or radome that reflects solar radiation while maintaining an air gap for convective cooling of the primary enclosure. Multi-layer coatings with high solar reflectance (SR > 0.85) and high thermal emittance (TE > 0.80) are cost-effective thermal management additions.

    Evaluation Checklist for Procurement Teams

    When evaluating 5G CPE thermal designs, procurement and engineering teams should verify the following:

    1. Operating temperature range specification: The vendor should provide both the rated ambient operating range and the maximum internal component junction temperatures under worst-case load and ambient conditions. A rated range of -30°C to +55°C is the minimum baseline for outdoor CPE.
    2. Thermal throttling behavior: Request detailed characterization of how throughput, carrier aggregation configuration, and Tx power scale with temperature. The device should not experience sudden performance cliffs but should implement graceful degradation with clear alerting via the management interface.
    3. Accelerated life testing (ALT) data: Vendors should provide ALT results conducted at 85°C/85% RH for a minimum of 1,000 hours, with pre- and post-test RF performance characterization.
    4. IP rating verification: For outdoor CPE, verify that the IP rating (typically IP65 or IP67) has been certified by an independent test laboratory, not self-declared. The IP rating applies to the complete assembly including all cable glands and connector interfaces.
    5. Thermal telemetry and SNMP MIB support: The CPE should expose internal temperature sensors (at minimum: SoC junction, modem, and ambient) via the management plane, with configurable alarm thresholds and SNMP trap generation for thermal events.
    6. Solar load testing: For outdoor CPE, request solar load test results (typically conducted at 1,120 W/m² irradiance per IEC 60068-2-5) demonstrating stable operation without throttling.

    Conclusion

    Thermal management is not a cosmetic consideration in 5G CPE procurement — it is a fundamental determinant of field reliability, sustained performance, and total cost of ownership. As FWA networks expand into harsher environments and device power densities continue to increase, the ability to evaluate thermal architecture with engineering rigor will separate successful large-scale deployments from those plagued by premature failures and unpredictable performance degradation.

    Procurement teams that incorporate the thermal evaluation criteria outlined in this guide into their RFQ and vendor qualification processes will be better positioned to select CPE that delivers consistent, reliable connectivity across the full range of real-world operating conditions.