Author: openclaw-Lisa-New

  • A Technical Buyer’s Guide to 5G CPE Cloud Management and Remote Provisioning: TR-369 USP, Zero-Touch Deployment, and Fleet Management at Scale

    A Technical Buyer’s Guide to 5G CPE Cloud Management and Remote Provisioning: TR-369 USP, Zero-Touch Deployment, and Fleet Management at Scale

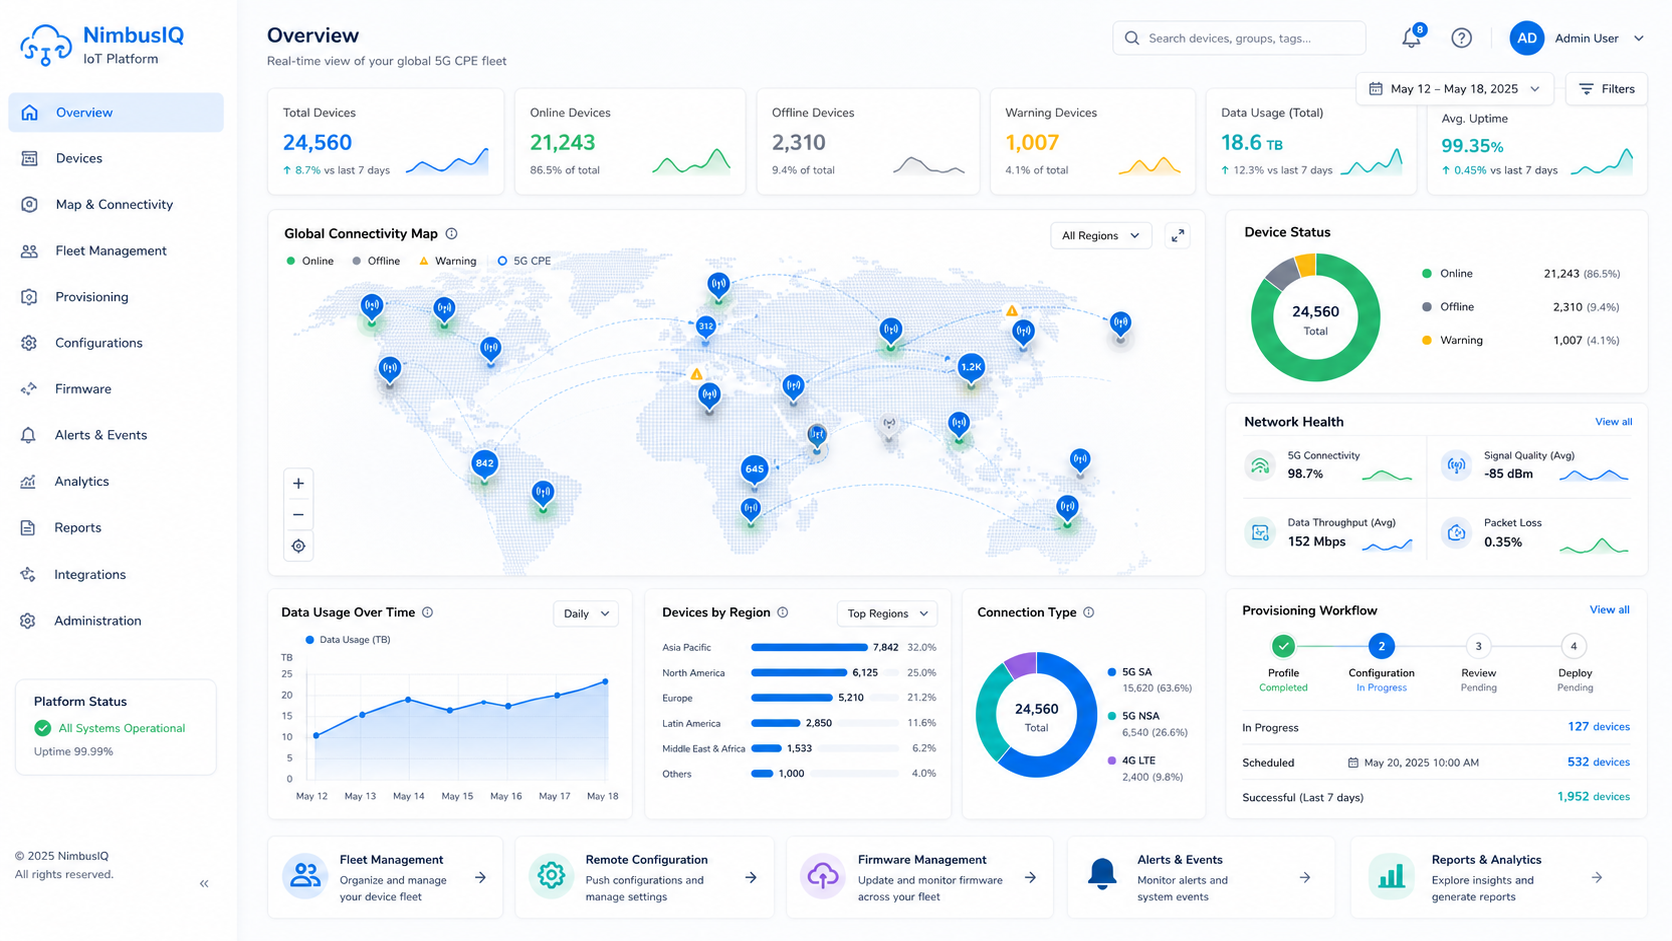
    As 5G Fixed Wireless Access deployments scale from thousands to millions of units, the operational complexity of managing distributed CPE fleets becomes the dominant cost driver for operators and managed service providers. A well-architected cloud management platform — built on modern device management protocols and zero-touch provisioning workflows — can reduce per-device operational expenditure by 40–60% while dramatically improving subscriber experience. This guide examines the key architectural decisions, protocol choices, and deployment considerations that technical buyers should evaluate when selecting cloud-managed 5G CPE solutions.

    The Protocol Landscape: TR-069, TR-369 USP, and the Migration Path

    The device management protocol stack is the foundation of any CPE cloud management architecture, and the industry is undergoing a generational transition from TR-069 (CWMP) to TR-369 (User Services Platform, or USP). Understanding the capabilities and limitations of each is essential for making informed procurement decisions.

    TR-069 (CWMP) has served as the workhorse CPE management protocol for nearly two decades. Its connection-request mechanism (typically via STUN or HTTP), parameter tree based on TR-181 Device Data Model, and periodic inform-based reporting have enabled operators to manage hundreds of millions of devices. However, TR-069 was designed in an era of DSL modems and simple NAT routers — its request-response architecture, SOAP/XML message encoding, and reliance on periodic polling introduce significant limitations in 5G FWA environments where low-latency control, bulk data telemetry, and NAT traversal across CGNAT boundaries are operational requirements.

    TR-369 (USP) represents a fundamental architectural evolution. Built on a message-bus paradigm with WebSocket or MQTT transport, USP enables persistent bidirectional communication between the CPE and the management controller — eliminating the polling latency inherent in TR-069. Key architectural advantages include:

    • Push-Based Telemetry: CPE can proactively report KPI changes, alarm conditions, and performance anomalies to the management platform in near real-time, rather than waiting for the next periodic inform interval.
    • Bulk Data Collection: USP’s support for protobuf-encoded bulk data messages enables efficient transmission of large datasets — signal strength time-series, throughput logs, and spectrum scan results — without the XML overhead that plagues TR-069 at scale.
    • Multi-Controller Architecture: A single USP agent on the CPE can simultaneously communicate with multiple controllers (operator ACS, enterprise IT manager, subscriber self-care portal), each with independent access control and command authorization scopes.
    • IoT Device Proxy: USP’s software module management (SMM) capability allows the CPE to act as a management proxy for downstream LAN devices, extending the management domain to connected sensors, cameras, and industrial endpoints.

    For technical buyers evaluating CPE platforms in 2026, the recommendation is clear: prioritize devices with native TR-369 USP agent support, even if the immediate deployment uses TR-069 for backward compatibility. The protocol migration from CWMP to USP is not a matter of if but when, and CPE firmware architectures designed around USP’s object model and message bus paradigm will have substantially lower technical debt when the transition occurs.

    Zero-Touch Provisioning: From Unboxing to Operational in Minutes

    Zero-touch provisioning (ZTP) is arguably the single most impactful cloud management capability for large-scale FWA deployments. The goal is straightforward: a CPE that arrives at the subscriber premises in a sealed box should achieve full operational state — including firmware updates, configuration application, SIM activation, and service verification — with no field technician intervention and no end-user configuration steps.

    A robust ZTP workflow for 5G FWA CPE typically follows this sequence:

    1. Factory Bootstrap: During manufacturing, each CPE receives a unique device certificate (X.509), a bootstrap configuration pointing to the operator’s ACS/USP controller URL, and optionally a pre-provisioned bootstrap eSIM profile for initial cellular connectivity.
    2. First Network Attachment: Upon power-on, the CPE uses its bootstrap credentials to establish initial IP connectivity — either via pre-provisioned eSIM, a bootstrap APN that whitelists only the management controller, or via LAN-side DHCP on a dedicated management VLAN.
    3. Mutual TLS Authentication: The CPE presents its factory-installed device certificate to the management controller. The controller validates the certificate against the operator’s device inventory and establishes a mutually authenticated TLS session.
    4. Configuration Push: The controller identifies the device by serial number or IMEI, retrieves the subscriber-specific configuration profile from the operator’s BSS/OSS, and pushes the complete parameter set — APN configuration, QoS policies, Wi-Fi SSID and security settings, VLAN mapping, firewall rules, and firmware version requirements.
    5. Firmware Validation and Update: If the factory-installed firmware does not match the operator’s current approved release, the CPE downloads and installs the correct firmware image, reboots, and re-authenticates — all before the service is presented to the subscriber.
    6. Service Activation and Verification: The CPE performs automated service verification — throughput test, latency measurement, DNS resolution check, and VoIP MOS estimation — and reports results to the controller. Only when all verification thresholds are met is the subscriber-facing Wi-Fi SSID enabled and the installation marked complete.

    For technical evaluation purposes, buyers should verify that candidate CPE platforms support the complete ZTP workflow including firmware rollback capabilities (in case a pushed firmware version introduces regressions), secure boot validation at each reboot, and automated fallback to a “golden image” if repeated provisioning attempts fail.

    Fleet Management at Scale: Monitoring, Analytics, and Automation

    Managing a fleet of 100,000+ CPE devices demands capabilities that go well beyond individual device configuration. Modern cloud management platforms must provide:

    Hierarchical Fleet Organization: Devices should be organizable by geography, customer segment, hardware model, firmware version, and custom tags, with configuration templates inheritable through the hierarchy. A regional configuration override should automatically propagate to all devices in that region without manual per-device intervention.

    Proactive Anomaly Detection: Machine learning models operating on aggregated telemetry data can identify early indicators of degradation — gradual RSSI decline suggesting antenna misalignment, increasing CRC error counts indicating RF interference, memory leak patterns — and trigger preemptive actions before subscribers notice service impact.

    Automated Remediation Playbooks: When anomalies are detected, the platform should execute configurable remediation sequences: restart the 5G modem, switch to a backup APN, adjust antenna beam steering parameters, or escalate to a human technician with a pre-populated diagnostic report. The goal is to resolve 80%+ of common issues without human intervention.

    Campaign Management: Operators regularly need to execute bulk operations — upgrading firmware on 50,000 devices, changing DNS server configurations, enabling new Wi-Fi bands. Campaign management capabilities should support staged rollouts (canary → 1% → 10% → 50% → 100%), automatic rollback on error-rate thresholds, and scheduling within maintenance windows respecting local time zones.

    API Integration and Northbound Interfaces

    No cloud management platform operates in isolation. The ability to integrate with operator OSS/BSS systems, network operations centers (NOCs), and analytics platforms is critical. Key integration points include:

    • RESTful APIs with comprehensive Swagger/OpenAPI documentation for all device management operations, supporting OAuth 2.0 and API-key authentication.
    • Webhook-based event streaming for real-time integration — device online/offline events, alarm state transitions, configuration change notifications — into existing NOC dashboards and ticketing systems.
    • Kafka or MQTT data export for bulk telemetry pipeline integration, enabling operators to feed CPE performance data into their existing big data analytics and AI/ML platforms.
    • TMF (TM Forum) Open API alignment for operators running TM Forum-compliant OSS/BSS stacks, ensuring seamless integration with inventory management, trouble ticketing, and service assurance systems.

    Security Architecture for Cloud-Managed CPE

    The management plane represents a high-value attack surface — compromise of the management controller would provide an attacker with control over the entire CPE fleet. Defense-in-depth security architecture must encompass:

    • Mutual TLS Everywhere: All communication between CPE and management controller must use mutually authenticated TLS 1.3, with the CPE validating the controller’s certificate against a pinned CA and the controller validating each CPE’s unique device certificate.
    • Least-Privilege Access Control: Management API access must support fine-grained RBAC, with separate roles for field technicians (device-level troubleshooting only), NOC operators (regional monitoring and basic configuration changes), and engineering (firmware campaign management and global template changes).
    • Audit Trail Immutability: Every configuration change, firmware update, and administrative action must be logged with cryptographic integrity, supporting compliance requirements and forensic investigation.
    • Secure Element Binding: The device certificate should be generated and stored within a hardware secure element (TPM 2.0 or equivalent) during manufacturing, with the private key never leaving the secure boundary — preventing certificate extraction even if the CPE firmware is compromised.

    Evaluating Cloud Management Solutions: A Buyer’s Checklist

    When evaluating 5G CPE cloud management platforms, technical buyers should assess the following criteria:

    1. Protocol Support: Does the platform support both TR-069 and TR-369 USP? Is there a documented migration path with backward compatibility?
    2. ZTP Maturity: Is the zero-touch workflow production-proven at the operator’s target deployment scale (10,000+ devices)? Does it support firmware rollback and failure fallback?
    3. Scalability Architecture: Is the platform designed for horizontal scaling? What is the published per-controller device capacity and what database/clustering technology backs it?
    4. Multi-Tenancy: Does the platform support hierarchical multi-tenancy for operators managing multiple enterprise customers or wholesale partners?
    5. Northbound API Quality: Are the APIs comprehensively documented? Do they support webhooks, streaming telemetry export, and TMF standards?
    6. Security Certifications: Has the platform undergone independent security assessment? Is it compliant with operator security requirements (ISO 27001, SOC 2, GSMA NESAS)?
    7. Geographic Data Residency: Can telemetry and configuration data be constrained to specific geographic regions for regulatory compliance?

    Selecting the right cloud management platform is a strategic decision that will shape operational efficiency, subscriber satisfaction, and total cost of ownership for years to come. By evaluating against these criteria, technical buyers can make informed choices that position their 5G FWA deployments for sustainable, scalable growth.
  • A Technical Buyer’s Guide to Multi-Gigabit 5G CPE Backhaul Architecture: 10GbE WAN/LAN, SFP+ Fiber Uplink, and High-Capacity Last-Mile Design for Enterprise

    A Technical Buyer’s Guide to Multi-Gigabit 5G CPE Backhaul Architecture: 10GbE WAN/LAN, SFP+ Fiber Uplink, and High-Capacity Last-Mile Design for Enterprise

    As 5G networks evolve toward 5G-Advanced and operators activate carrier aggregation configurations delivering 4–7 Gbps of aggregate throughput, the traditional Gigabit Ethernet CPE backhaul becomes the binding constraint on end-to-end performance. Enterprise and high-end residential FWA deployments increasingly require multi-gigabit backhaul architectures that can match 5G air interface capacity without introducing bottlenecks at the LAN edge. This guide examines the hardware architecture, interface selection, and deployment considerations for next-generation multi-gigabit 5G CPE backhaul design.

    The Multi-Gigabit Imperative: Why 1GbE Is No Longer Sufficient

    The mathematics of 5G throughput evolution are straightforward and compelling. A 5G CPE operating in a 3CC CA configuration — aggregating, for example, 100 MHz of n78 (3.5 GHz) at 4×4 MIMO, 40 MHz of n41 (2.6 GHz) at 4×4 MIMO, and 20 MHz of n28 (700 MHz) at 2×2 MIMO — can realistically achieve physical-layer throughput of 5–6 Gbps in downlink under favorable RF conditions with 256QAM modulation. When networks upgrade to 5G-Advanced with 1024QAM and additional carrier aggregation combinations, the achievable throughput pushes toward 8–10 Gbps.

    A CPE with only a 1GbE LAN port becomes the bottleneck: the 5G modem can receive data at 5 Gbps, but the CPE can only deliver 940 Mbps (after Ethernet overhead) to the LAN. The result is 80%+ of the available 5G capacity going unused — a waste of expensive spectrum assets and CPE silicon investment. Multi-gigabit backhaul is not a nice-to-have; it is an architectural requirement for extracting full value from mid-band 5G spectrum investments.

    Interface Options: 2.5GbE, 5GbE, 10GbE, and SFP+

    Modern 5G CPE designs have several options for breaking the Gigabit Ethernet barrier, each with distinct trade-offs in cost, power consumption, cabling compatibility, and deployment complexity:

    2.5GbE (NBASE-T)

    IEEE 802.3bz, ratified in 2016, defines 2.5GBASE-T and 5GBASE-T operation over Cat5e and Cat6 cabling — the same infrastructure already installed in most enterprise and residential environments. For FWA deployments, 2.5GbE offers the most pragmatic upgrade path: it provides 2.5 Gbps of backhaul capacity over existing Cat5e cabling at cable lengths up to 100 meters, with per-port power consumption typically under 1.5W. For operators deploying CPE in existing buildings where recabling is impractical or cost-prohibitive, 2.5GbE represents the minimal-friction path to multi-gigabit performance.

    The limitation, of course, is throughput headroom. A 2.5GbE backhaul can handle today’s typical 3CC CA throughput (2–3 Gbps of IP-layer throughput after protocol overhead) but provides limited headroom for future upgrades to 4CC CA or 1024QAM modulation. It is a pragmatic near-term solution rather than a future-proof investment.

    5GbE (NBASE-T)

    5GBASE-T occupies the middle ground: sufficient throughput to handle current and near-future 5G-Advanced configurations while maintaining Cat6 cabling compatibility. At approximately 3–4W per port, the power budget increase over 2.5GbE is modest. For CPE targeting premium enterprise and high-end residential segments, 5GbE offers an attractive balance of performance, cabling compatibility, and cost.

    However, 5GbE PHY adoption in downstream equipment (switches, routers, access points) lags behind 2.5GbE and 10GbE. Buyers should verify that the broader network infrastructure can actually leverage 5GbE link rates before specifying it as a CPE requirement.

    10GbE (10GBASE-T)

    10GBASE-T delivers the maximum electrical Ethernet throughput available, but with significant trade-offs: Cat6a (or Cat7) cabling is required for the full 100-meter reach, per-port power consumption typically ranges from 2.5–5W (substantially higher at the PHY level than 2.5GbE), and the silicon cost for 10GBASE-T PHYs remains a meaningful BOM adder. For enterprise CPE deployed in greenfield environments with structured Cat6a cabling, 10GBASE-T provides ample throughput headroom for the entire lifecycle of a 5G-Advanced deployment.

    The practical reality for many FWA deployments is that 10GBASE-T is over-engineered for current throughput requirements, and the combination of higher power consumption and cabling constraints makes it a niche choice for specific high-end enterprise scenarios rather than a mass-market solution.

    SFP+ Fiber Uplink

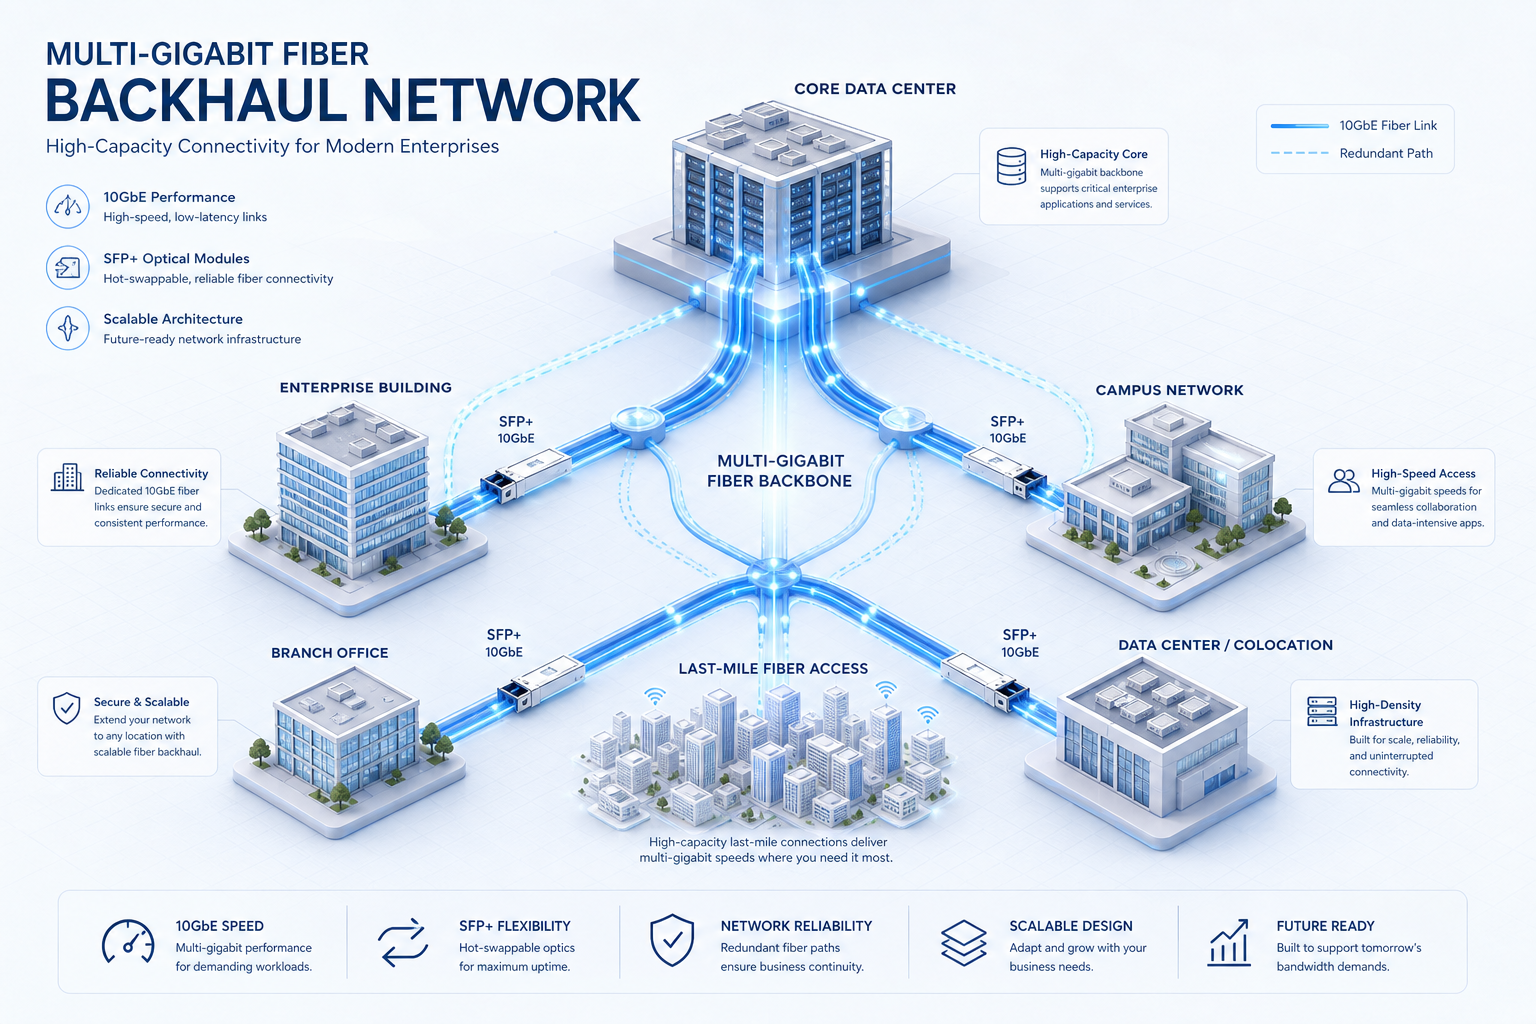
    For enterprise deployments where the CPE serves as a primary WAN edge device connecting to a corporate LAN switch or SD-WAN appliance, an SFP+ cage offers compelling advantages over copper Ethernet:

    • Media Flexibility: The operator or enterprise can select the appropriate SFP+ module for the deployment scenario — single-mode fiber (10 km+ reach), multi-mode fiber (300m at OM3), direct-attach copper (DAC) for in-rack connections, or even 10GBASE-T SFP+ modules for copper compatibility. This flexibility eliminates the need for different CPE hardware SKUs for different backhaul media.
    • Electrical Isolation: Fiber connections provide galvanic isolation between the outdoor CPE and indoor equipment, protecting against ground potential differences and lightning-induced surges — a significant reliability advantage for outdoor CPE deployments.
    • Future Upgrade Path: A CPE with an SFP+ cage (supporting 10 Gbps) can later accommodate 25GbE SFP28 modules if required by future 6G or millimeter-wave deployments, extending the hardware lifecycle without replacing the CPE.

    The primary trade-off is that SFP+ requires fiber cabling infrastructure or at minimum an SFP+ module purchase, adding deployment complexity and cost for scenarios where copper is already available. For greenfield enterprise deployments with structured fiber cabling, however, SFP+ is frequently the optimal choice.

    Multi-Gigabit Switch Fabric and Packet Processing

    Beyond the physical interface, the CPE’s internal packet processing architecture must be capable of sustaining multi-gigabit throughput without becoming the bottleneck. Key hardware design considerations include:

    Hardware NAT Acceleration: At multi-gigabit rates, software-based NAT processing on a general-purpose CPU becomes a severe bottleneck. CPE designs must incorporate hardware NAT/NAPT engines — typically integrated into the SoC’s packet processor or implemented in a dedicated flow-offload ASIC — capable of sustaining line-rate NAT at 5–10 Gbps with connection tracking for hundreds of thousands of simultaneous flows.

    Switch Fabric Bandwidth: The internal switch fabric connecting the 5G modem (via PCIe 3.0/4.0 or USXGMII), the multi-gigabit Ethernet PHYs, the Wi-Fi chipset, and the application processor must be dimensioned for worst-case aggregate throughput. A CPE advertising 5GbE LAN and Wi-Fi 7 (theoretical 30+ Gbps aggregate) must have a switch fabric capable of handling simultaneous wired and wireless traffic at these rates without blocking or excessive buffering latency.

    Buffer Management and QoS: At multi-gigabit rates, buffer sizing and QoS queue management become critical for maintaining low latency under load. Smart queue management (SQM) algorithms — fq_codel, CAKE — must operate efficiently at line rate, and buffer sizes must be tuned to prevent bufferbloat without causing unnecessary packet loss during traffic bursts.

    Thermal and Power Design for Multi-Gigabit CPE

    Multi-gigabit interfaces introduce non-trivial thermal challenges. A 10GBASE-T PHY can dissipate 3–5W under full load — comparable to the power consumption of an entire entry-level CPE SoC. When combined with a high-performance 5G modem (3–6W), Wi-Fi 7 chipset (3–8W), and application processor, the total thermal design power (TDP) of a multi-gigabit CPE can approach 20–25W.

    Effective thermal management requires:

    • Strategic component placement separating high-power devices (10GbE PHY, 5G modem, Wi-Fi PA) to avoid thermal coupling.
    • Adequate heatsinking with thermal interface materials (TIMs) rated for the component temperature ranges.
    • Thermal throttling policies that gracefully degrade non-critical functions (e.g., reducing Wi-Fi transmit power or switching to a lower Ethernet link rate) before impacting 5G connectivity.
    • For outdoor CPE, passive cooling designs that can dissipate 20W+ in direct sunlight at 55°C ambient — a significantly more demanding thermal envelope than indoor CPE.

    Deployment Architecture Patterns

    Multi-gigabit 5G CPE backhaul enables several deployment architectures that are impractical with 1GbE-limited devices:

    CPE-as-Primary-WAN-Edge: The CPE connects directly to the enterprise SD-WAN appliance or core switch via SFP+ fiber or 10GbE copper, serving as the primary WAN link with no intermediate router. This eliminates a point of failure and reduces latency by one network hop.

    Aggregated Multi-CPE: In bandwidth-intensive enterprise scenarios, two or more 5G CPE devices with multi-gigabit backhaul can be aggregated via LACP (Link Aggregation Control Protocol) or SD-WAN load balancing, providing combined throughput of 8–10 Gbps with automatic failover.

    Distributed Wi-Fi Backhaul: The CPE’s multi-gigabit LAN port connects to a multi-gigabit PoE switch powering Wi-Fi 7 access points throughout the premises. This architecture ensures that the wired backhaul from CPE to APs does not become the bottleneck even as Wi-Fi 7’s multi-link operation (MLO) delivers 4–6 Gbps of actual throughput per AP.

    Evaluation Criteria for Technical Buyers

    When evaluating multi-gigabit 5G CPE backhaul solutions, technical buyers should consider:

    1. Throughput Validation: Has the CPE demonstrated sustained multi-gigabit throughput (not just link rate) in independent testing? Request RFC 2544 or Y.1564 test results showing throughput, latency, and frame loss at 2.5G, 5G, and 10G link rates.
    2. Hardware NAT Performance: What is the CPE’s NAT throughput with 64-byte and 1500-byte packet sizes? Is hardware acceleration active for all packet sizes and protocol combinations (TCP, UDP, GRE, IPsec)?
    3. Cabling Compatibility: For NBASE-T interfaces, does the CPE support auto-negotiation down to 1GbE and 100MbE for backward compatibility with existing cabling that cannot sustain 2.5/5G link rates?
    4. Power Budget: What is the CPE’s total power consumption at peak multi-gigabit throughput? Is PoE++ (802.3bt) power delivery supported for outdoor units, and what is the maximum cable length at each power class?
    5. Thermal Validation: Has the CPE been tested for sustained multi-gigabit operation at the highest rated ambient temperature? Request thermal throttling behavior documentation.
    6. Firmware Maturity: Multi-gigabit PHY drivers, flow offload engines, and buffer management algorithms involve complex firmware. Assess the vendor’s track record for shipping stable multi-gigabit firmware and their vulnerability disclosure and patch management process.

    Investing in multi-gigabit backhaul architecture today positions enterprise FWA deployments to fully capitalize on 5G-Advanced throughput gains over the next 3–5 years. By evaluating CPE against the detailed criteria outlined in this guide, technical buyers can ensure that their chosen platform delivers not just a high link rate but sustained, reliable, and thermally viable multi-gigabit performance in real-world deployment conditions.

  • 5G FWA CPE Expansion Accelerates Across Southeast Asian Emerging Markets as Operators Bridge the Urban-Rural Broadband Gap in 2026

    5G FWA CPE Expansion Accelerates Across Southeast Asian Emerging Markets as Operators Bridge the Urban-Rural Broadband Gap in 2026

    The Southeast Asian telecom landscape is undergoing a significant transformation in 2026, with 5G Fixed Wireless Access (FWA) Customer Premises Equipment (CPE) emerging as the primary vehicle for broadband expansion across Indonesia, Vietnam, the Philippines, and Thailand. As national digital economy agendas mature and operators seek cost-efficient alternatives to fiber trenching, 5G FWA CPE deployments are accelerating at an unprecedented pace in the region’s emerging markets.

    The Southeast Asian FWA Opportunity

    Southeast Asia presents a uniquely compelling case for 5G FWA. With a combined population exceeding 680 million spread across thousands of islands and diverse topographies, the economics of last-mile fiber deployment have historically constrained broadband penetration outside major urban centers. According to GSMA Intelligence data cited in mid-2026 operator reports, FWA connections in the ASEAN region are projected to grow at a compound annual rate of 38% through 2028, driven by three converging factors: affordable 5G spectrum allocation, declining CPE unit costs, and strong government universal service obligations (USOs).

    Indonesia’s Telkomsel has emerged as a regional bellwether, reporting that its 5G FWA subscriber base in tier-2 and tier-3 cities grew 147% year-over-year in H1 2026. The operator attributes this growth to the deployment of sub-6 GHz CPE devices priced below IDR 1.5 million (approximately USD 95), a price point that opens the addressable market beyond enterprise users to small businesses and middle-income households.

    Vietnam and the Philippines: Parallel Growth Trajectories

    Vietnam’s Ministry of Information and Communications has set an ambitious target of 90% household broadband coverage by 2027, with 5G FWA identified as the primary technology for reaching rural and mountainous provinces where fiber deployment costs exceed USD 800 per household passed. Viettel and VNPT have jointly deployed over 18,000 5G base stations optimized for FWA coverage in 2026, with CPE procurement tenders emphasizing multi-band support across n28 (700 MHz), n41 (2.6 GHz), and n78 (3.5 GHz) to balance coverage range with capacity.

    In the Philippines, the government’s Broadband ng Masa (Broadband for the Masses) program has entered its third phase, with Globe Telecom and PLDT-Smart deploying 5G FWA CPE in over 600 municipalities previously served only by legacy 3G or satellite links. The National Telecommunications Commission (NTC) has allocated dedicated FWA spectrum in the 3.3–3.4 GHz band, enabling operators to deploy high-gain outdoor CPE units capable of delivering 100+ Mbps to households up to 12 km from the nearest base station in rural environments with favorable line-of-sight conditions.

    Thailand’s Enterprise-First Approach

    Thailand is charting a distinctly enterprise-oriented path, with AIS and True Corporation focusing 5G FWA CPE deployments on industrial estates, logistics parks, and SME clusters in Thailand 4.0 economic corridors. The Eastern Economic Corridor (EEC) has seen particularly dense FWA adoption, where manufacturing facilities leverage 5G CPE as primary WAN links for Industry 4.0 applications including real-time production monitoring, automated guided vehicle (AGV) coordination, and computer vision-based quality inspection systems.

    Thai enterprise CPE deployments are notably demanding outdoor-rated, industrial-temperature-range devices with IP67 enclosures, PoE++ power delivery, and integrated edge computing capabilities — specifications that are driving innovation among regional CPE vendors and creating a distinct product tier for tropical industrial environments.

    CPE Technology Trends Shaping the Regional Market

    Several technology trends are defining Southeast Asian 5G FWA CPE requirements in 2026:

    Multi-Band Carrier Aggregation: Operators increasingly specify CPE capable of aggregating low-band (n28/n5) and mid-band (n78/n41) carriers simultaneously to maximize both coverage reach and throughput. Three-carrier aggregation (3CC CA) is becoming a standard requirement in operator RFPs across the region.

    Outdoor CPE Dominance: Unlike mature markets where indoor CPE predominates, Southeast Asian deployments favor outdoor CPE architectures that overcome building penetration losses common in concrete-and-rebar construction. High-gain directional antennas with 10–12 dBi gain are specified for rural and suburban deployments.

    Power Efficiency and Solar Compatibility: With grid reliability varying significantly across the region, CPE vendors are innovating in low-power designs (sub-15W typical consumption) and native DC power input for solar+battery installations — a critical requirement for remote tower-less sites and island deployments.

    Multi-Operator SIM and eSIM: Cross-border mobility and operator redundancy requirements are driving adoption of eSIM-capable CPE with dual-SIM failover, particularly relevant in border economic zones and maritime applications across the archipelagic region.

    Market Implications for the Global CPE Supply Chain

    The Southeast Asian 5G FWA boom is reshaping the global CPE supply chain in measurable ways. Component demand for sub-6 GHz RF front-end modules, outdoor-rated enclosures, and high-gain antenna arrays has increased substantially, with lead times for certain specialized components extending to 14–18 weeks in mid-2026. CPE vendors with established manufacturing partnerships in Vietnam, Thailand, and Malaysia are positioned advantageously, benefiting from both proximity to demand and favorable trade agreements within the ASEAN economic community.

    Analysts project that Southeast Asian markets will account for 22–25% of global 5G FWA CPE unit shipments by 2028, up from approximately 12% in 2025, making the region the fastest-growing geographic segment for FWA equipment worldwide. For operators, vendors, and system integrators alike, understanding the unique technical, commercial, and regulatory dynamics of Southeast Asian emerging markets is no longer optional — it is a strategic imperative for capturing growth in the next chapter of global 5G FWA expansion.

  • A Technical Buyer’s Guide to Sustainable 5G CPE: Energy-Efficient Chipset Design, Power Optimization Strategies, and Green Manufacturing Standards for Carbon-Neutral FWA Rollouts

    A Technical Buyer’s Guide to Sustainable 5G CPE: Energy-Efficient Chipset Design, Power Optimization Strategies, and Green Manufacturing Standards for Carbon-Neutral FWA Rollouts

    As telecom operators worldwide accelerate 5G FWA (Fixed Wireless Access) rollouts and enterprise CPE deployments, energy efficiency and sustainability have emerged as critical procurement criteria. With global CPE shipments expected to exceed 120 million units annually by 2027, the cumulative energy consumption of deployed devices represents a significant environmental and operational cost factor. This technical buyer’s guide examines the chipset innovations, power optimization strategies, and green manufacturing standards shaping the next generation of sustainable 5G CPE.

    The Energy Challenge: Why Sustainable 5G CPE Matters

    A typical 5G FWA CPE consumes 8-15 watts during active operation, while high-performance devices supporting mmWave and multi-gigabit Ethernet can draw 18-25 watts. When multiplied across millions of deployed units operating 24/7, the aggregate energy consumption is substantial. The GSMA’s Mobile Net Zero initiative and the European Commission’s Code of Conduct on Energy Consumption of Broadband Equipment have set ambitious targets: 30% reduction in CPE energy consumption by 2028 compared to 2023 baselines, and net-zero carbon emissions for the telecom sector by 2050.

    Beyond environmental compliance, energy efficiency directly impacts operator economics. For a network operator with 2 million deployed CPE units, a 3-watt reduction per device translates to approximately 52.6 GWh of annual electricity savings — equivalent to roughly $7.9 million in operational expenditure at average industrial electricity rates. These savings compound across multi-year CPE lifecycles, making energy efficiency a compelling total cost of ownership (TCO) argument.

    Energy-Efficient Chipset Platforms

    Next-Generation 5G Modem Architectures

    The latest 5G modem platforms from Qualcomm (Snapdragon X80/X75), MediaTek (T830/T800), and UNISOC (V517) incorporate advanced power management features that significantly reduce CPE energy consumption:

    • Adaptive voltage and frequency scaling (AVFS): Dynamically adjusts modem core voltage and clock frequency based on real-time traffic load, reducing power draw during low-utilization periods by up to 40%
    • Deep sleep modes with fast wake: Supports sub-10mW idle power states with sub-100ms wake latency for maintaining always-connected user experience while minimizing background power consumption
    • Hardware-accelerated offload engines: Dedicated silicon blocks for PDCP/RLC/MAC processing reduce main CPU utilization by 30-35%, enabling lower-power application processor configurations
    • Integrated PMIC (Power Management IC): System-on-chip integration of power management reduces external component count and improves power conversion efficiency from typical 85% to 92%+

    Advanced Process Nodes

    The transition from 7nm/6nm to 4nm and 3nm process nodes for 5G modem and application processor silicon delivers approximately 25-30% power reduction at equivalent performance levels. TSMC’s N4P and Samsung’s 4LPP+ processes, now mainstream for 5G CPE chipsets in 2026, provide the foundation for energy-efficient device designs. Looking ahead, 3nm (TSMC N3E) adoption in late 2026 will further reduce power consumption, though cost premiums remain a consideration for mid-range CPE segments.

    Power Optimization Strategies Throughout the CPE Lifecycle

    1. Intelligent Radio Resource Management

    Modern 5G CPE can implement AI-driven power optimization at the radio layer. Machine learning algorithms trained on traffic patterns can predict idle periods and proactively transition the modem to lower-power RRC states (RRC_IDLE or RRC_INACTIVE with extended DRX cycles) without compromising user experience. Smart antenna selection — dynamically switching between 4×4 and 2×2 MIMO based on signal conditions and throughput requirements — can reduce RF front-end power consumption by 15-20% without noticeable performance degradation for typical broadband traffic profiles.

    2. Ethernet and Wi-Fi Power Management

    The integrated Wi-Fi 7 and multi-gigabit Ethernet interfaces in modern CPE are significant power consumers. Energy Efficient Ethernet (EEE, IEEE 802.3az) reduces PHY power during low-link-utilization periods, while Wi-Fi Target Wake Time (TWT) — enhanced in Wi-Fi 7 — allows CPE to schedule wake intervals for connected clients, reducing overall system power. Intelligent port power-down — automatically disabling unused Ethernet ports — can save an additional 0.5-1.5W per unused port.

    3. Thermal-Aware Power Management

    CPE deployed in environments with wide temperature ranges — outdoor units in direct sunlight, attic installations, industrial settings — face thermal throttling challenges that impact both performance and energy efficiency. Passive cooling designs using advanced heat spreaders and thermally conductive enclosures eliminate fan power consumption (2-4W per fan) while maintaining reliable operation up to 60°C ambient. Dynamic thermal management algorithms that progressively reduce performance headroom rather than abruptly throttling deliver smoother user experience while optimizing energy consumption.

    Green Manufacturing and Circular Economy

    Sustainable Materials and Design

    Leading CPE manufacturers are adopting post-consumer recycled (PCR) plastics for enclosure manufacturing, with targets of 30-50% recycled content by 2028. Bio-based polymers derived from renewable feedstocks are emerging as alternatives for non-structural components. Enclosure designs are evolving toward tool-free disassembly, enabling easier repair, component replacement, and end-of-life material separation for recycling.

    Packaging and Logistics

    Sustainable packaging initiatives include elimination of single-use plastics, adoption of FSC-certified paper-based packaging with soy-based inks, and right-sized packaging that reduces shipping volume and associated carbon emissions. Some operators now specify packaging sustainability requirements in CPE procurement RFPs, with weightings of 5-10% in vendor evaluation scoring.

    Extended Product Lifecycles

    Countering the “disposable electronics” trend, sustainable CPE design emphasizes longer operational lifecycles — targeting 7-10 years versus traditional 3-5 years — achieved through modular hardware design, guaranteed firmware security update commitments, and field-upgradable components. This reduces the embodied carbon footprint per year of service and lowers total cost of ownership for operators.

    Standards and Certification Programs

    Several industry standards and certification programs provide frameworks for evaluating CPE sustainability:

    • EU Code of Conduct for Broadband Equipment (Version 8): Defines maximum power consumption targets for CPE across multiple operational states (on, idle, standby) with increasingly stringent tiers
    • Energy Star for Network Equipment (Version 3.0, 2026): US EPA program covering CPE with efficiency specifications for idle and sleep mode power consumption
    • ITU-T L.1310: Energy efficiency metrics and measurement methodology for telecommunication equipment
    • ETSI ES 203 475: Environmental engineering standard addressing CPE energy efficiency and circular economy principles
    • GSMA Mobile Net Zero: Industry-wide climate action roadmap with sector-specific decarbonization pathways including CPE efficiency targets

    Procurement Recommendations for Operators

    When evaluating CPE vendors for sustainable 5G FWA rollouts, operators should consider the following criteria:

    1. Request energy consumption data across all operational states (active, idle, deep sleep) measured per ITU-T L.1310 methodology
    2. Evaluate chipset generation: Prefer 4nm or newer process nodes with AVFS and hardware-accelerated offload
    3. Assess packaging sustainability: Require plastic-free, FSC-certified packaging with optimized volume-to-product ratios
    4. Verify certification: Require EU CoC for Broadband Equipment or Energy Star compliance as minimum baseline
    5. Review lifecycle commitments: Confirm firmware security update support duration (minimum 5 years) and spare parts availability commitments
    6. Calculate TCO including energy: Factor projected electricity costs over 5-7 year lifecycle into procurement decisions, not just upfront unit pricing

    Frequently Asked Questions

    How much power does a typical 5G CPE consume?

    A typical 5G FWA CPE consumes 8-15 watts during active operation, while high-performance mmWave devices with multi-gigabit Ethernet can draw 18-25 watts. The latest energy-efficient designs utilizing 4nm chipsets with adaptive power management can reduce active power consumption to 5-8 watts, with deep sleep modes achieving under 500mW.

    What is the EU Code of Conduct for Broadband Equipment?

    The EU Code of Conduct for Broadband Equipment is a voluntary program that sets maximum power consumption targets for CPE and networking equipment across operational states (on, idle, standby). Version 8 (2026) defines increasingly stringent tiers with the goal of achieving 30% energy reduction by 2028. Compliant devices receive recognition and are preferred in many European operator procurement processes.

    How can operators reduce the carbon footprint of their CPE fleet?

    Operators can reduce CPE fleet carbon footprint through multiple strategies: selecting energy-efficient devices with advanced chipset power management, implementing intelligent power optimization at the network level (AI-driven RRC state management, extended DRX), choosing vendors with sustainable packaging and recycled materials, extending device lifecycles through modular design and long-term firmware support, and factoring energy TCO into procurement scoring rather than evaluating upfront unit cost alone.

    Contact Honlly Telecom for Energy-Efficient 5G CPE Solutions →

  • A Technical Buyer’s Guide to Private 5G Network CPE: Spectrum Options, NPN Architecture Models, and Deployment Best Practices for Enterprise IT Teams

    A Technical Buyer’s Guide to Private 5G Network CPE: Spectrum Options, NPN Architecture Models, and Deployment Best Practices for Enterprise IT Teams

    For enterprise IT teams and telecom procurement professionals evaluating private 5G network CPE, understanding the spectrum options, network architecture models, and deployment best practices is essential to making informed investment decisions. This technical buyer’s guide provides a comprehensive framework for navigating the complex landscape of private 5G CPE selection, from spectrum strategy to operational deployment.

    Private 5G Spectrum Options: Shared vs. Dedicated vs. Leased

    The choice of spectrum fundamentally shapes CPE requirements, coverage characteristics, and total cost of ownership. Enterprise buyers must understand three primary spectrum acquisition models:

    1. Dedicated / Licensed Spectrum

    Enterprises directly acquire spectrum licenses from national regulators for exclusive use within a defined geographic area. This model provides the highest level of control and predictability, with guaranteed interference-free operation. Germany’s 3.7-3.8 GHz “Campusnetz” licenses (€1,000-10,000 per site, 10-year term) and Japan’s Local 5G licenses (4.6-4.8 GHz) are prominent examples. CPE for dedicated spectrum deployments must be precisely configured for the specific licensed frequency range and must include GPS/GNSS receivers for time synchronization in TDD networks.

    2. Shared Spectrum (e.g., CBRS, n77 Shared Access)

    In shared spectrum models, multiple users access the same frequency band under a coordination framework. The US CBRS band (3.55-3.70 GHz) operates under a three-tier Spectrum Access System (SAS) that dynamically assigns frequencies to incumbent (Tier 1), Priority Access (Tier 2), and General Authorized Access (Tier 3) users. CPE operating in shared spectrum must be SAS-certified and capable of dynamic frequency selection, requiring embedded Environmental Sensing Capability (ESC) or SAS client integration. The UK’s Shared Access license framework provides a similar model with low-power (indoor) and medium-power (outdoor/campus) tiers.

    3. Operator-Leased Spectrum / Network Slicing

    Enterprises can lease private network capacity from mobile network operators (MNOs) through dedicated network slices on public 5G infrastructure. This model, often referred to as PNI-NPN (Public Network Integrated Non-Public Network), uses the operator’s licensed spectrum with guaranteed SLA parameters for throughput, latency, and availability. CPE for network-sliced deployments must support URSP (UE Route Selection Policy) for slice-aware traffic routing and may require operator-specific SIM/eSIM provisioning with dedicated DNN/APN configurations.

    NPN Architecture Models: SNPN vs. PNI-NPN

    The 3GPP standards (TS 23.501, Release 16+) define two primary architecture models for Non-Public Networks:

    Standalone Non-Public Network (SNPN)

    An SNPN operates as a completely independent 5G network with its own dedicated core network, radio access network, and network management system. It does not rely on any public PLMN (Public Land Mobile Network) infrastructure. SNPN is identified by a unique NID (Network Identifier) in addition to the PLMN ID. This architecture provides maximum data sovereignty, security isolation, and operational independence — critical requirements for defense contractors, semiconductor fabs, and critical infrastructure operators. CPE for SNPN deployments must support SNPN-specific network selection procedures as defined in 3GPP Release 16, including CAG (Closed Access Group) cell selection and manual SNPN selection modes.

    Public Network Integrated NPN (PNI-NPN)

    PNI-NPN provides private network functionality integrated with a public 5G network, typically using network slicing and Closed Access Groups (CAGs) to create virtualized private network domains within the operator’s infrastructure. This model reduces upfront capital expenditure by leveraging existing network infrastructure and is ideal for enterprises that require private network-grade performance but prefer an OPEX-based service model. CPE for PNI-NPN must support CAG-based access control, allowing devices to only access cells belonging to authorized CAGs, and URSP rules for directing enterprise traffic to dedicated network slices.

    Hybrid Deployment Models

    A growing number of enterprises are adopting hybrid architectures that combine SNPN for mission-critical, high-security workloads (e.g., production line control, safety systems) with PNI-NPN for less sensitive applications (e.g., visitor Wi-Fi offload, general office connectivity). This requires CPE capable of simultaneously operating in both SNPN and public network modes, with intelligent traffic steering between private and public network domains based on application requirements.

    CPE Selection Criteria for Enterprise Private 5G

    Radio Capability Requirements

    • 5G SA (Standalone) support: Mandatory for private networks; NSA is insufficient for URLLC and network slicing features
    • Band support: n48 (CBRS), n77, n78, n79 for sub-6 GHz; n257/n258 for mmWave use cases
    • 4×4 MIMO: Essential for maximizing spectral efficiency in enterprise environments
    • Carrier aggregation: Support for intra-band and inter-band CA for throughput aggregation
    • Antenna configuration: External antenna ports (SMA/N-Type) for installations requiring directional or high-gain antennas

    Network Interface and Protocol Support

    • Multi-gigabit Ethernet: 2.5GbE minimum; 5GbE/10GbE for high-throughput industrial applications
    • Serial interfaces: RS232/RS485 with Modbus TCP/RTU gateway for legacy industrial equipment
    • Time-sensitive networking (TSN): IEEE 802.1AS timing synchronization for industrial automation
    • Dual SIM / eSIM: For multi-operator redundancy and flexible provisioning
    • GPS/GNSS: For TDD network synchronization and location-aware services

    Security and Management

    • Hardware root of trust (HRoT): TPM 2.0 or equivalent secure element
    • Secure boot: Signed firmware with rollback protection
    • IPsec/IKEv2: For secure backhaul tunneling to enterprise data centers
    • Zero-touch provisioning (ZTP): TR-069/TR-369 (USP) support for bulk device onboarding
    • SNMP v3 / NETCONF / RESTCONF: For integration with enterprise NMS platforms

    Deployment Best Practices

    1. Conduct a Comprehensive Site Survey: Before CPE procurement, perform a detailed RF site survey including spectrum analysis, propagation modeling, and interference assessment. Identify optimal CPE mounting locations accounting for industrial obstacles (metal racking, machinery, RF-noisy equipment).

    2. Plan for Device Density: Private 5G networks in manufacturing and logistics often support 500-1,000+ connected endpoints per cell. Ensure CPE selection accounts for per-device throughput requirements under peak load conditions, not just headline speed specifications.

    3. Implement Staged Deployment: Begin with a pilot deployment in a single production area or warehouse zone, validate performance against KPIs (latency, throughput, availability), then scale to full production. Use the pilot phase to validate CPE interoperability with specific industrial applications and protocols.

    4. Establish CPE Lifecycle Management: Deploy centralized CPE management platforms supporting firmware OTA updates, configuration backup/restore, performance monitoring, and security patch management. Plan for CPE lifecycle of 5-7 years with vendor support commitments aligned to operational requirements.

    5. Engage with System Integrators: Private 5G deployment is rarely a “plug-and-play” exercise. Partner with experienced system integrators who understand both 5G network engineering and the specific operational technology (OT) environment of your industry vertical.

    Frequently Asked Questions

    What is the difference between SNPN and PNI-NPN in private 5G?

    SNPN (Standalone Non-Public Network) is a completely independent 5G network with its own dedicated core and RAN, providing maximum security and data sovereignty. PNI-NPN (Public Network Integrated NPN) leverages a public operator’s infrastructure with network slicing and Closed Access Groups to create virtualized private network domains. SNPN offers higher isolation and control; PNI-NPN offers lower upfront costs and operational simplicity.

    Which spectrum option is best for my enterprise private 5G deployment?

    The optimal spectrum choice depends on your specific requirements: dedicated licensed spectrum provides the highest performance predictability and is best for mission-critical industrial applications; shared spectrum (CBRS, etc.) offers lower cost and faster deployment; operator-leased spectrum/network slicing minimizes upfront capital expenditure. Many enterprises adopt a hybrid approach, mixing spectrum models for different use cases.

    What CPE features are essential for industrial private 5G?

    Essential features include 5G SA support, industrial-grade enclosure (IP65+), multi-gigabit Ethernet, RS232/RS485 serial interfaces for legacy equipment connectivity, hardware root of trust security, GPS/GNSS for TDD synchronization, and support for industrial protocols like Modbus TCP. Zero-touch provisioning and centralized management (TR-069/TR-369) are critical for deployments with hundreds of devices.

    Contact Honlly Telecom for Private 5G CPE Consultation →

  • Global 5G Private Network CPE Deployments Surge in Manufacturing and Logistics as Industry 4.0 Digital Transformation Accelerates Enterprise FWA Adoption in H2 2026

    Global 5G Private Network CPE Deployments Surge in Manufacturing and Logistics as Industry 4.0 Digital Transformation Accelerates Enterprise FWA Adoption in H2 2026

    The global landscape for private 5G network CPE deployments is undergoing a dramatic transformation in H2 2026, driven by accelerating Industry 4.0 digitalization across manufacturing, logistics, and warehousing sectors. According to the latest GSA Private Mobile Networks report, over 2,100 organizations worldwide have now deployed private cellular networks, with 5G-based installations accounting for 58% of new deployments in the first half of 2026 — up from 41% in the same period last year. This surge is reshaping procurement patterns for CPE (Customer Premises Equipment) as enterprise IT teams seek industrial-grade devices capable of operating in demanding factory-floor environments.

    The Manufacturing Sector Leads Private 5G Adoption

    Manufacturing remains the dominant vertical for private 5G adoption, representing approximately 34% of all private network deployments globally. Major automotive manufacturers in Germany, Japan, and South Korea have been early adopters, deploying private 5G networks to support automated guided vehicles (AGVs), real-time machine vision quality inspection, and wireless SCADA (Supervisory Control and Data Acquisition) systems. In China, the MIIT (Ministry of Industry and Information Technology) reported that over 29,000 private 5G networks have been deployed across industrial facilities as of Q2 2026, with manufacturing accounting for the largest share.

    The CPE requirements for these environments are distinctly different from consumer or office-grade equipment. Industrial private 5G CPE must deliver ultra-reliable low-latency communication (URLLC), with end-to-end latency under 1ms for time-critical applications such as robotic motion control and safety interlock systems. Devices must also withstand harsh physical conditions — including temperature extremes, vibration, dust, and electromagnetic interference — while maintaining carrier-grade availability of 99.999% (“five nines”).

    Logistics and Warehousing: The Fastest-Growing Segment

    The logistics and warehousing sector is experiencing the fastest growth in private 5G CPE adoption, with deployments growing 127% year-over-year in H1 2026. E-commerce fulfillment centers operated by major logistics providers are deploying private 5G networks to support autonomous mobile robots (AMRs), real-time inventory tracking via 5G-connected RFID readers, and augmented reality (AR) assisted picking systems. The CPE deployed in these environments must support high device density — often 1,000+ connected endpoints per 10,000 square meters — while maintaining consistent throughput for video-based AI analytics and telemetry data streams.

    Leading CPE vendors, including Honlly Telecom, have responded by developing purpose-built industrial 5G CPE devices that integrate multi-gigabit Ethernet ports, RS232/RS485 serial interfaces for legacy industrial equipment connectivity, and IP65-rated enclosures suitable for deployment on factory floors, loading docks, and outdoor logistics yards. These devices typically support 5G NR in both SA (Standalone) and NSA (Non-Standalone) modes across n77, n78, n79, and n41 bands commonly used for private network deployments.

    Spectrum Availability Drives Regional Deployment Patterns

    A critical factor in private 5G CPE adoption is local spectrum policy. Countries that have allocated dedicated spectrum for enterprise private networks are seeing significantly faster deployment rates:

    • Germany: 3.7-3.8 GHz reserved for private networks; over 400 licenses issued to enterprises
    • Japan: 4.6-4.8 GHz and 28.2-28.3 GHz designated for local 5G; over 180 enterprise deployments
    • United States: CBRS 3.55-3.70 GHz shared spectrum; over 300,000 CBRS SAS-authorized devices active
    • United Kingdom: Ofcom shared access licenses in 3.8-4.2 GHz and 1800 MHz; growing enterprise uptake
    • South Korea: 4.72-4.82 GHz and 28.9-29.1 GHz allocated for private 5G; strong manufacturing adoption

    CPE manufacturers serving the global market must now deliver devices capable of operating across this diverse spectrum landscape, supporting multiple band configurations and regional regulatory certifications including CE (Europe), FCC (US), MIC (Japan), and SRRC (China).

    Open RAN and Multi-Vendor Interoperability in Private Networks

    A significant trend in H2 2026 is the growing adoption of Open RAN architecture in private 5G deployments. Enterprise IT teams increasingly prefer multi-vendor, disaggregated network architectures that avoid single-vendor lock-in. This requires CPE that is O-RAN compliant and tested for interoperability with radio units (O-RUs) and distributed units (O-DUs) from multiple vendors. The O-RAN Alliance’s specifications for fronthaul interface (Split 7.2x) and network slicing support are becoming baseline requirements for enterprise private 5G CPE procurement RFPs.

    Security Considerations for Enterprise Private 5G CPE

    As enterprises deploy private 5G networks carrying sensitive operational data — from production schedules to proprietary manufacturing process parameters — security has become a top procurement priority. Enterprise IT teams now require CPE with hardware root of trust (HRoT), secure boot with signed firmware verification, encrypted local storage for configuration data, and support for IPsec and MACsec tunneling to secure backhaul connections to enterprise data centers. Zero-trust network access (ZTNA) frameworks are being extended to private 5G CPE, with device-level certificate-based authentication and continuous posture assessment.

    Market Outlook: 2026-2028

    Industry analysts project the global private 5G network equipment market — including CPE, radio units, and core network infrastructure — to reach $16.8 billion by 2028, growing at a CAGR of 42.3% from 2026. Manufacturing and logistics will remain the lead verticals, while healthcare, mining, port operations, and smart grid utilities represent emerging growth opportunities. CPE shipments for private 5G networks are expected to exceed 4.2 million units annually by 2028, driven by the growing installed base of industrial IoT endpoints and the ongoing replacement of legacy Wi-Fi and proprietary wireless systems with standardized 5G solutions.

    For telecom operators, system integrators, and enterprise IT buyers navigating this rapidly evolving landscape, selecting the right CPE partner — one with proven industrial-grade hardware engineering, global regulatory compliance expertise, and deep experience across diverse spectrum bands and deployment scenarios — will be critical to private 5G project success.

    Frequently Asked Questions

    What is a private 5G network and how does it differ from public 5G?

    A private 5G network (also called a Non-Public Network or NPN) is a localized 5G cellular network deployed for the exclusive use of a single organization, such as a factory, warehouse, or campus. Unlike public 5G networks operated by mobile network operators (MNOs), private 5G networks offer dedicated coverage, guaranteed capacity, ultra-low latency, and complete control over data security and network policies. They can operate on dedicated spectrum (e.g., 3.7 GHz in Germany) or shared spectrum (e.g., CBRS in the US).

    What types of CPE are used in private 5G industrial deployments?

    Industrial private 5G CPE comes in several form factors: indoor desktop/rack-mount units for control rooms and server cabinets, outdoor IP65/IP67-rated units for deployment on factory exteriors and logistics yards, and ruggedized DIN-rail-mount units for integration into industrial control panels. Key features include 5G SA support, multi-gigabit Ethernet (2.5GbE/5GbE/10GbE), serial ports (RS232/RS485) for legacy industrial equipment, and industrial protocols like Modbus TCP and PROFINET.

    Which frequency bands are used for private 5G networks?

    Common private 5G bands include n77 (3.3-4.2 GHz), n78 (3.3-3.8 GHz), n79 (4.4-5.0 GHz), n48 (CBRS 3.55-3.70 GHz), and n41 (2.5 GHz). Millimeter-wave bands like n257 (28 GHz) and n258 (26 GHz) are also used for high-capacity industrial applications. The specific band availability depends on national regulatory allocations; CPE must support the bands authorized in the deployment country.

    Contact Honlly Telecom for Private 5G CPE Solutions →

  • A Technical Buyer’s Guide to 5G CPE QoS Architecture: SLA Enforcement, Network Slicing Integration, and Traffic Prioritization for Enterprise Deployments

    A Technical Buyer’s Guide to 5G CPE QoS Architecture: SLA Enforcement, Network Slicing Integration, and Traffic Prioritization for Enterprise Deployments

    For ISPs, MVNOs, and enterprise network operators deploying 5G Fixed Wireless Access (FWA) at scale, Quality of Service (QoS) architecture is no longer a secondary consideration—it is a fundamental differentiator that determines whether a CPE fleet can deliver carrier-grade service level agreements (SLAs) across diverse traffic profiles. This technical buyer’s guide examines the architectural components, standards frameworks, and procurement criteria that define enterprise-grade 5G CPE QoS capabilities in 2026.

    The Enterprise QoS Imperative: Why Best-Effort Is Not Enough

    Enterprise 5G FWA deployments carry fundamentally different traffic requirements than consumer broadband. A single enterprise CPE may simultaneously handle real-time UCaaS traffic (Teams, Zoom), cloud ERP transactions, SD-WAN overlay tunnels, IoT telemetry streams, and bulk data backups—each with distinct latency, jitter, throughput, and reliability requirements. Without robust QoS enforcement at the CPE level, the “last meter” of the 5G connection becomes the bottleneck that undermines end-to-end SLA guarantees.

    Key enterprise traffic profiles and their QoS requirements:

    Traffic ClassLatency TargetJitterPacket LossPriority
    Real-Time Voice/Video<30ms<10ms<0.1%EF (Expedited Forwarding)
    Business-Critical Apps<50ms<20ms<0.5%AF41 (Assured Forwarding)
    SD-WAN Control Plane<100msN/A<1%AF31
    IoT Telemetry<200msN/A<2%AF21
    Bulk Data/BackupN/AN/A<5%BE (Best Effort)

    5G QoS Architecture Fundamentals: The 5QI Framework

    The 3GPP 5G QoS model centers on the 5G QoS Identifier (5QI), a scalar value that maps to standardized QoS characteristics including resource type (GBR, Non-GBR, Delay-Critical GBR), priority level, packet delay budget (PDB), and packet error rate (PER). For CPE procurement, understanding how candidate devices map 5QI values to internal traffic processing pipelines is essential.

    Enterprise-relevant 5QI values include:

    • 5QI 3 (GBR, PDB 50ms): Real-time gaming, V2X communications, and interactive AR/VR applications requiring guaranteed bit rate with tight latency bounds.
    • 5QI 5 (Non-GBR, PDB 100ms): IMS signaling, critical machine-type communications, and enterprise UCaaS session initiation.
    • 5QI 6 (Non-GBR, PDB 300ms): TCP-based enterprise applications including HTTP/HTTPS, email, chat, and file transfers with standard buffering tolerance.
    • 5QI 7 (Non-GBR, PDB 100ms): Voice, live streaming, and interactive gaming with conversational latency requirements.
    • 5QI 82 (Delay-Critical GBR, PDB 10ms): Discrete automation, intelligent transport systems, and industrial control loops requiring ultra-reliable low-latency communication (URLLC).

    A production-grade enterprise CPE must support a minimum of 8 concurrent QoS flows with independent 5QI mapping, DSCP marking preservation across the LAN-WAN boundary, and per-flow buffer management with configurable queue depths.

    Network Slicing Integration: CPE as the Slice Termination Point

    5G network slicing extends QoS architecture from per-flow management to per-slice isolation. A single enterprise CPE may terminate multiple network slices simultaneously—for example, a URLLC slice for industrial control traffic, an eMBB slice for office productivity applications, and an mMTC slice for sensor networks—each with independent security, routing, and QoS policies.

    Critical CPE capabilities for network slicing integration include:

    • NSSAI Awareness: The CPE must parse and act upon Network Slice Selection Assistance Information (NSSAI) conveyed during PDU session establishment, mapping each S-NSSAI to the appropriate internal processing pipeline.
    • Multi-Slice VLAN Mapping: Enterprise deployments typically require per-slice VLAN separation on the LAN side. The CPE must support flexible VLAN-to-slice mapping with 802.1Q tagging, enabling seamless integration with existing enterprise switching and SD-WAN infrastructure.
    • Per-Slice DSCP Remarking: When enterprise traffic traverses the 5G core, the CPE should preserve or intelligently remark DSCP markings at the slice boundary to maintain end-to-end QoS consistency.
    • Slice-Aware Failover: If a network slice becomes unavailable due to radio conditions or core network events, the CPE should implement graceful degradation policies—routing critical traffic to alternate slices or fallback bearers according to configurable priority rules.

    Traffic Prioritization: From 5QI to Silicon

    The gap between QoS policy definition and actual packet processing performance is where many CPE implementations fall short. Enterprise buyers should evaluate devices on their hardware-accelerated QoS pipeline capabilities:

    • Hardware Queue Architecture: Minimum 8 hardware queues per direction (WAN-to-LAN and LAN-to-WAN) with weighted round-robin (WRR) or deficit round-robin (DRR) scheduling, supporting both strict priority and weighted queuing in a hierarchical configuration.
    • Buffer Management: Active Queue Management (AQM) with CoDel or PIE algorithms to minimize bufferbloat under congestion, plus per-queue buffer sizing configurable from 32KB to 2MB to accommodate diverse traffic profiles.
    • Flow Classification Engine: Hardware-accelerated packet classification supporting Layer 2–4 matching (MAC, VLAN, IP 5-tuple, DSCP) at line rate for all Ethernet interfaces (1G/2.5G/5G/10G depending on CPE class).
    • Hierarchical QoS (HQoS): Support for three-level scheduling hierarchy: per-subscriber shaping at the top level, per-service-class scheduling in the middle, and per-flow queuing at the leaf—enabling service providers to deliver wholesale SLA guarantees to multiple enterprise tenants through a single CPE.

    SLA Enforcement and Monitoring

    QoS architecture is only as valuable as the monitoring framework that validates it. Enterprise-grade CPE must provide granular telemetry that enables both proactive SLA assurance and forensic troubleshooting:

    • Per-Flow KPI Export: The CPE should export per-flow latency, jitter, packet loss, and throughput statistics via IPFIX or NetFlow to centralized monitoring platforms, with configurable reporting intervals down to 10 seconds.
    • TWAMP Light Reflector: Integrated Two-Way Active Measurement Protocol (TWAMP) reflector functionality enables end-to-end SLA measurement from centralized probes without deploying additional test endpoints at each customer site.
    • Y.1731 Ethernet OAM: For enterprise LAN-side performance monitoring, support for ITU-T Y.1731 Ethernet service OAM including frame loss measurement (LM), frame delay measurement (DM), and synthetic loss measurement (SLM).
    • gRPC Streaming Telemetry: Modern CPE platforms should offer gRPC-based streaming telemetry with Protobuf-encoded metrics, enabling integration with cloud-native observability stacks (Prometheus, Grafana, Thanos) and AIOps platforms for predictive SLA analytics.

    Procurement Checklist: QoS Evaluation Criteria

    When evaluating 5G CPE for enterprise SLA-guaranteed deployments, technical buyers should verify the following capabilities through vendor documentation, independent testing, and reference deployments:

    1. 5QI Support Matrix: Full documentation of supported 5QI values, including GBR, Non-GBR, and Delay-Critical GBR types, with per-5QI PDB and PER compliance verification.
    2. Concurrent QoS Flow Capacity: Minimum 8 concurrent QoS flows with independent 5QI mapping; 16+ recommended for multi-tenant or slice-rich deployments.
    3. Hardware Queue Depth: At least 8 hardware queues per direction with hierarchical scheduling; verify at line rate under 64-byte packet load.
    4. Bufferbloat Resistance: AQM implementation (CoDel/PIE) with buffer sizing below 500KB per queue under typical RTT conditions; validate with industry-standard bufferbloat tests.
    5. NSSAI Processing: Confirm S-NSSAI parsing in PDU Session Establishment Accept messages and per-slice VLAN mapping capabilities.
    6. Telemetry Export: IPFIX/NetFlow v9/v10 with per-flow granularity; gRPC streaming telemetry preferred for cloud-native integration.
    7. TWAMP Light Support: Reflector functionality with configurable UDP port and DSCP marking for measurement traffic.
    8. Management API: RESTCONF/NETCONF or gNMI interface for programmatic QoS policy configuration, avoiding vendor-proprietary management lock-in.
    9. Firmware Update SLA: Vendor commitment to QoS-related firmware updates for the full CPE lifecycle, including new 5QI definitions from 3GPP release updates.
    10. Independent Certification: O-RAN Alliance or TIP certification covering QoS and slicing interoperability; BBF TR-398 Issue 3 or later for Wi-Fi integrated CPE.

    Looking Ahead: AI-Driven QoS Optimization

    The next frontier in CPE QoS architecture is AI/ML-driven dynamic policy optimization. Emerging CPE platforms incorporate on-device inference engines that analyze traffic patterns in real time, predict congestion events before they impact SLAs, and autonomously adjust queue weights, buffer allocations, and 5QI-to-DSCP mappings. For enterprise buyers building long-term FWA strategies, selecting CPE with dedicated ML acceleration silicon—even if not yet fully utilized—provides a future-proofing advantage as these capabilities mature through 2027–2028.

    To discuss your enterprise 5G CPE QoS requirements or request product specifications for SLA-guaranteed deployment scenarios, contact the Honlly Telecom engineering team for a detailed technical consultation.

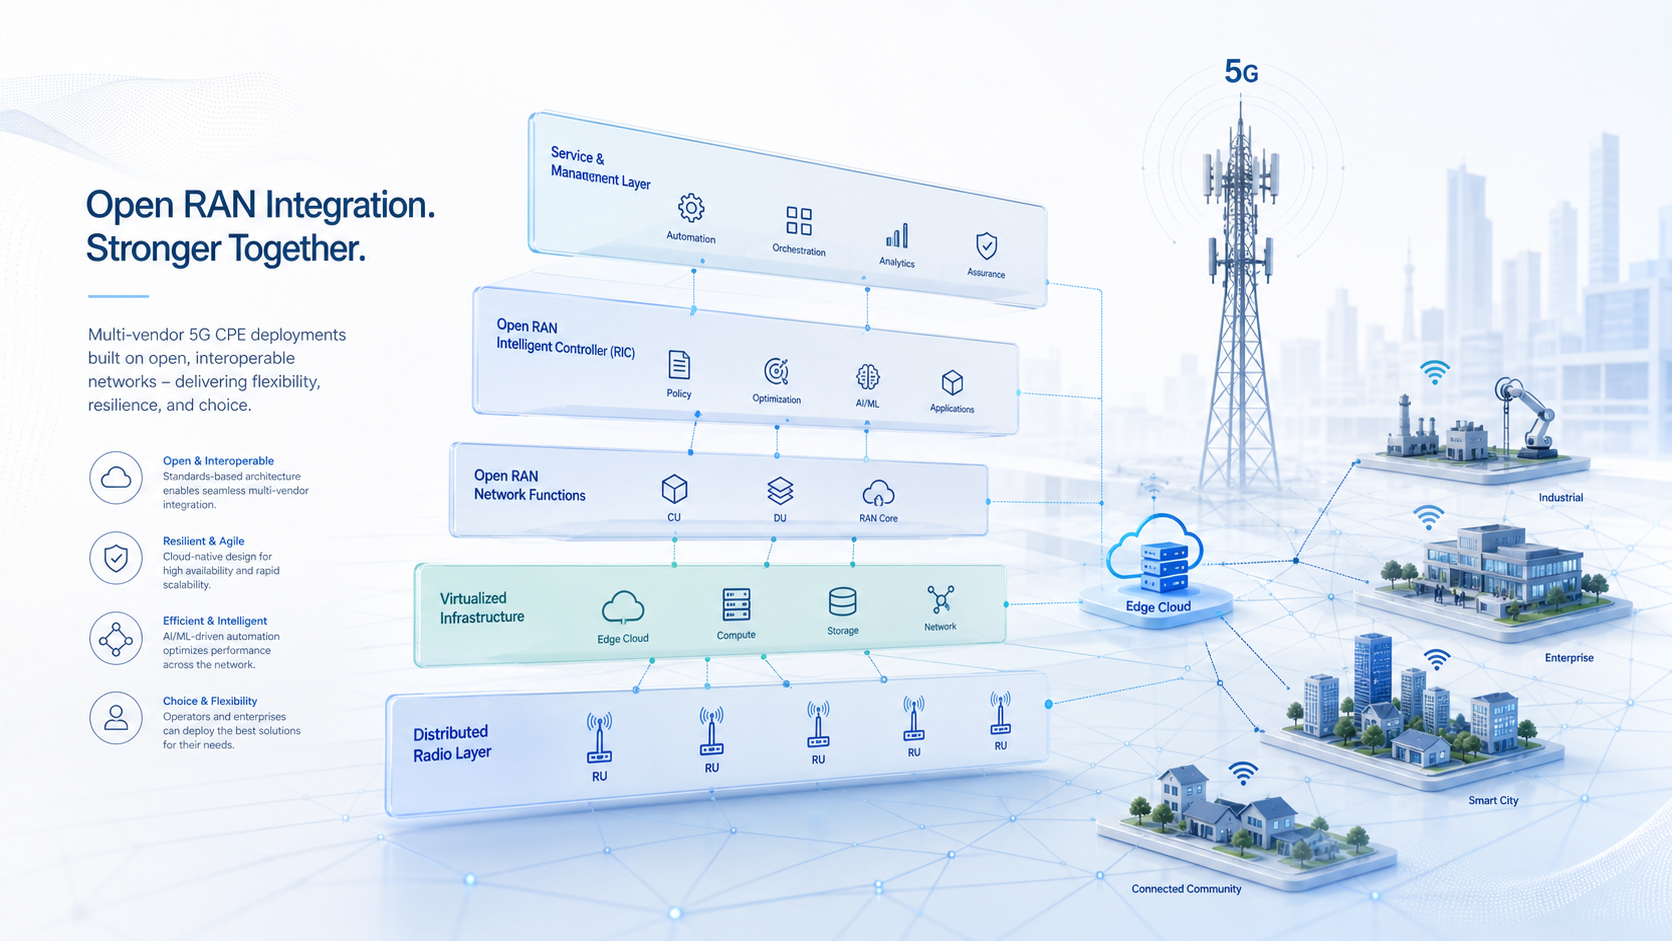
  • Global Telecom Operators Accelerate Open RAN Integration with Multi-Vendor 5G CPE Deployments in H2 2026

    Global Telecom Operators Accelerate Open RAN Integration with Multi-Vendor 5G CPE Deployments in H2 2026

    The global telecom landscape is undergoing a structural shift as operators accelerate Open Radio Access Network (Open RAN) integration with multi-vendor 5G Customer Premises Equipment (CPE) strategies. In H2 2026, this convergence is reshaping how mobile network operators (MNOs), fixed wireless access (FWA) providers, and managed service providers (MSPs) approach infrastructure procurement, vendor diversification, and service delivery optimization.

    The Open RAN Imperative: Beyond the Hype Cycle

    Open RAN has evolved from an industry aspiration into a commercial reality. According to recent O-RAN Alliance data, over 45 commercial Open RAN deployments are now live across 28 countries, with Asia-Pacific and Europe leading adoption. The driving forces are clear: operators seek to break vendor lock-in, reduce total cost of ownership (TCO), and create a more competitive ecosystem for radio access network components.

    For CPE procurement teams, the Open RAN evolution carries direct implications. Multi-vendor interoperability at the radio unit (RU), distributed unit (DU), and centralized unit (CU) levels means CPE devices must now demonstrate seamless compatibility across diverse network architectures. The traditional model of single-vendor, end-to-end CPE certification is giving way to a more flexible, standards-driven validation framework.

    Multi-Vendor CPE: The New Procurement Paradigm

    Major operators including Vodafone, Deutsche Telekom, Rakuten Mobile, and Reliance Jio have publicly committed to multi-vendor CPE strategies. The rationale extends beyond cost optimization: diversified CPE supply chains provide resilience against component shortages, enable regional customization, and accelerate time-to-market for new service tiers.

    Key developments in H2 2026 include:

    • Chipset Diversification: Multiple silicon vendors now offer O-RAN compliant 5G modem platforms, including MediaTek’s T800 series, Qualcomm’s X75/X80 modems, and emerging solutions from Unisoc and ASR Microelectronics. This competition is driving down CPE bill-of-materials costs by an estimated 18–22% year-over-year.
    • Middleware Abstraction Layers: Software-defined CPE architectures with vendor-agnostic middleware layers enable operators to deploy firmware updates and feature upgrades across heterogeneous hardware fleets without per-model certification cycles.
    • Open Fronthaul Interface Compliance: CPE devices supporting O-RAN 7.2 split architecture are entering volume production, enabling direct interoperability with multi-vendor RU deployments without proprietary translation layers.
    • Automated Interoperability Testing: Industry consortia including the O-RAN Alliance and Telecom Infra Project (TIP) have launched automated CPE interoperability testing frameworks, reducing certification timelines from 12–16 weeks to 3–4 weeks for qualified devices.

    Regional Deployment Spotlight: Asia-Pacific Leads the Charge

    Asia-Pacific markets are setting the pace for Open RAN CPE deployments. Japan’s Rakuten Symphony platform now supports over 18 certified third-party CPE models across its cloud-native 5G network. In India, Bharti Airtel and Reliance Jio have both issued multi-vendor CPE RFPs totaling an estimated 4.2 million units for rural and semi-urban FWA expansion in H2 2026.

    Southeast Asian operators, particularly in Indonesia, Vietnam, and the Philippines, are leveraging Open RAN architectures to extend broadband coverage to underserved regions. The combination of Open RAN infrastructure and multi-vendor CPE procurement has reduced per-subscriber deployment costs by 30–35% compared to traditional integrated vendor solutions.

    Technical Considerations for Buyers

    For ISPs, MVNOs, and enterprise procurement managers evaluating multi-vendor Open RAN CPE, several technical dimensions warrant close attention:

    • 3GPP Release Compliance: Ensure CPE devices support at minimum 3GPP Release 17 with upgrade paths to Release 18 features including MIMO enhancements and AI/ML-based beam management.
    • O-RAN Fronthaul Profiles: Verify support for relevant O-RAN fronthaul profiles (Category A or B) matching your RU deployment topology and bandwidth requirements.
    • Management Plane Integration: Confirm compatibility with your O1/O2 interface implementations for FCAPS management, software lifecycle management, and performance monitoring across multi-vendor fleets.
    • Security Certification: Validate Secure Boot, Hardware Root of Trust, and O-RAN Security Working Group specifications compliance across all candidate CPE models.
    • Lifecycle SLA Coverage: Negotiate vendor-agnostic support SLAs that cover firmware updates, vulnerability patching, and hardware replacement across the expected 5–7 year deployment lifecycle.

    Market Outlook and Strategic Implications

    Industry analysts project that Open RAN-compatible CPE will represent 42% of global 5G FWA CPE shipments by 2028, up from approximately 18% in 2026. This trajectory signals a fundamental reordering of the CPE vendor landscape, with new entrants from Taiwan, South Korea, and mainland China challenging incumbent European and North American suppliers.

    For operators, the strategic calculus is shifting from “which single vendor” to “which vendor mix” optimizes coverage, cost, and capability across their service footprint. Those who build robust multi-vendor CPE certification and orchestration capabilities in 2026 will be best positioned to capitalize on the expanding Open RAN ecosystem in the years ahead.

    For more information on multi-vendor 5G CPE solutions compatible with Open RAN architectures, contact the Honlly Telecom product team to discuss your specific deployment requirements.

  • A Technical Buyer’s Guide to 5G CPE Zero-Trust Security Architecture: Hardware Root of Trust, Secure Boot, and End-to-End Encryption for Enterprise FWA Deployments

    A Technical Buyer’s Guide to 5G CPE Zero-Trust Security Architecture: Hardware Root of Trust, Secure Boot, and End-to-End Encryption for Enterprise FWA Deployments

    As enterprise 5G fixed wireless access deployments scale from proof-of-concept trials to production networks carrying sensitive corporate, financial, and operational traffic, the security architecture of CPE devices has emerged as a boardroom-level concern. The traditional perimeter-based security model—where CPE was treated as a trusted endpoint inside the corporate firewall—is fundamentally incompatible with the distributed, multi-site, cloud-first enterprise architectures dominating 2026. For technical buyers evaluating 5G CPE for enterprise and industrial deployments, zero-trust security principles must now inform procurement specifications as rigorously as throughput, latency, and radio performance parameters.

    The CPE Attack Surface: Why 5G FWA Demands Zero-Trust

    5G CPE occupies a uniquely exposed position in the enterprise network topology. Unlike a core router locked in a climate-controlled data center with physical access controls and 24/7 security monitoring, CPE is frequently deployed in branch offices, retail locations, construction trailers, and outdoor enclosures—environments where physical tampering, unauthorized access, and network-based attacks are realistic threat vectors. Compromised CPE provides an attacker with a persistent foothold inside the enterprise WAN, with the ability to intercept, modify, or exfiltrate traffic across every connected LAN segment.

    The 3GPP 5G security architecture (TS 33.501) provides robust air interface protection through 5G AKA mutual authentication, SUCI-based subscriber identity privacy, and 256-bit encryption on the radio link. However, these protections terminate at the CPE’s modem interface. Post-modem—within the CPE’s application processor, operating system, LAN interfaces, and management plane—enterprise security depends entirely on the CPE’s embedded security architecture, which varies dramatically across vendors and price points.

    Hardware Root of Trust: The Foundational Layer

    Zero-trust CPE security begins at the silicon level. A hardware root of trust (HRoT) provides an immutable, cryptographically verifiable foundation that ensures the CPE boots only authentic, vendor-signed firmware and that device identity keys cannot be extracted or cloned even with physical access to the device.

    Secure Boot Chain: The CPE’s boot ROM, signed by the SoC vendor’s root key, cryptographically verifies the first-stage bootloader. Each subsequent stage—U-Boot or LK bootloader, Linux kernel, root filesystem—is verified against signed hashes before execution. Any modification to the boot chain, whether through firmware tampering, JTAG/SWD debug interface exploitation, or storage replacement, causes boot failure and, ideally, tamper-evident logging to a secure element. Enterprise procurement specifications should mandate secure boot with hardware-backed key storage (e.g., TPM 2.0 or platform-integrated secure enclave) and configurable security policy for boot verification failure behavior.

    Trusted Platform Module (TPM) Integration: A discrete or firmware TPM 2.0 implementation enables secure storage of device identity keys, measured boot attestation, and sealed storage that binds encryption keys to specific platform configuration register (PCR) values. For enterprise zero-trust architectures, TPM-backed device attestation allows the network’s policy enforcement point to cryptographically verify that the CPE is running authorized firmware and configuration before granting network access—a foundational zero-trust principle.

    Secure Element and SIM/eUICC Integration

    The CPE’s UICC or eUICC provides a tamper-resistant secure element for 5G network authentication, but its security capabilities can and should be leveraged for CPE device identity beyond the 3GPP authentication framework. The GSMA’s IoT SAFE (IoT SIM Applet For Secure End-to-End) initiative standardizes the use of the SIM/eSIM as a hardware security module for device-level TLS client certificates, credential storage, and cryptographic operations.

    CPE implementing IoT SAFE can use the carrier-provisioned eUICC as the hardware root for mutually authenticated TLS connections to enterprise zero-trust policy engines, cloud management platforms, and ZTNA (Zero Trust Network Access) brokers. This eliminates the need for separate hardware security modules and leverages the existing mobile operator security infrastructure—including secure OTA provisioning and key rotation—for enterprise CPE identity management.

    End-to-End Encryption and Traffic Isolation

    Zero-trust architecture mandates that no traffic is trusted based on network location alone. For 5G CPE deployed at the enterprise edge, this translates to mandatory encryption across the CPE’s entire data path:

    IPsec and WireGuard Tunnel Termination: Enterprise CPE must support hardware-accelerated IPsec (IKEv2 with strong cipher suites) and WireGuard for tunnel termination to enterprise VPN concentrators or cloud security gateways. AES-256-GCM and ChaCha20-Poly1305 cipher support with hardware crypto acceleration is essential for maintaining multi-gigabit throughput with encryption overhead. CPE should support per-VLAN tunnel mapping, enabling different traffic classes (corporate data, guest Wi-Fi, IoT telemetry) to be encrypted and routed through separate security domains.

    Micro-Segmentation at the CPE Edge: Advanced enterprise CPE implements 802.1Q VLAN trunking with per-VLAN security policies, enabling micro-segmentation between corporate workstations, payment systems, building management IoT, and guest networks directly at the branch edge. Combined with dynamic policy enforcement from a cloud-based zero-trust policy engine, this architecture ensures that a compromised IoT sensor cannot pivot to attack the payment processing VLAN—even when both connect through the same 5G CPE.

    MACsec and 802.1X for LAN-Side Security: For deployments where the CPE’s LAN ports connect to managed switches or other infrastructure devices, MACsec (IEEE 802.1AE) at line rate and 802.1X supplicant functionality on the CPE’s LAN interfaces provide link-layer encryption and port-based authentication that extend the zero-trust boundary one hop deeper into the enterprise network.

    Management Plane Security: The Overlooked Vector

    CPE management interfaces—TR-069/TR-369 (USP), SNMP, SSH, RESTCONF, and vendor-specific cloud management APIs—represent a high-value attack surface. Zero-trust CPE security architecture must protect these interfaces with the same rigor applied to the data plane:

    Mutual TLS for Management Protocols: All CPE management protocols must use mutually authenticated TLS 1.3 with client certificate authentication. The CPE must authenticate the management server (preventing man-in-the-middle attacks), and the management server must authenticate the CPE (preventing rogue device registration). Certificate enrollment should use EST (RFC 7030) or SCEP with hardware-backed key generation in the TPM or secure element.

    Role-Based Access Control and Audit Logging: CPE must implement granular RBAC distinguishing between firmware update, configuration change, monitoring-only, and diagnostic roles. All administrative actions must generate syslog or structured audit events with immutable timestamps, forwarded to a centralized SIEM. Local admin credentials must be salted and hashed with modern algorithms (bcrypt, Argon2id), never stored in plaintext or reversible formats.

    Secure OTA Firmware Updates: Over-the-air firmware updates are the most security-critical operation in the CPE lifecycle. Updates must be signed with vendor private keys, verified by the CPE before installation, and delivered over mutually authenticated TLS. The update mechanism must support A/B partition schemes with automatic rollback on verification failure, and update metadata (version, hash, signature, target hardware revision) must be independently verifiable by enterprise security teams.

    Building the Procurement Specification

    For technical buyers drafting 5G CPE procurement specifications in 2026, the following zero-trust security requirements should be considered mandatory for enterprise-grade deployments:

    • Hardware root of trust with immutable boot ROM and secure boot chain verification
    • TPM 2.0 or equivalent secure enclave for key storage and device attestation
    • GSMA IoT SAFE or equivalent SIM-based credential storage for device identity
    • Hardware-accelerated IPsec (AES-256-GCM) and WireGuard with per-VLAN tunnel mapping
    • Mutual TLS 1.3 for all management interfaces with hardware-backed client certificates
    • Signed, verified OTA firmware updates with A/B dual-bank fallback
    • Granular RBAC with immutable audit logging to external SIEM
    • 802.1X supplicant and MACsec support for LAN-side zero-trust extension
    • FIPS 140-3 or Common Criteria EAL4+ certification for cryptographic modules

    The enterprise 5G FWA security landscape in 2026 demands that CPE be treated not as a simple modem-and-router appliance, but as a security-enforcement point at the distributed enterprise edge. Organizations that apply zero-trust principles to CPE procurement will build 5G FWA networks that are scalable, defensible, and audit-ready—while those that treat CPE security as an afterthought will embed technical debt that becomes exponentially more expensive to remediate as deployments scale.